<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" ><generator uri="https://jekyllrb.com/" version="3.10.0">Jekyll</generator><link href="https://royce-fu.com/feed.xml" rel="self" type="application/atom+xml" /><link href="https://royce-fu.com/" rel="alternate" type="text/html" /><updated>2026-10-02T20:03:04+00:00</updated><id>https://royce-fu.com/feed.xml</id><title type="html">Royce Fu’s AI and Cloud Insights</title><subtitle>Use cases of AI, Cloud, Development and and Technologies AI Operations and Security, Cloud Infrastructure, Development, Platform Engineering, Oracle Database, Exadata, Platform Engineering, Observability and Management</subtitle><author><name>Royce Fu</name></author><entry><title type="html">Beyond the Fusion Metrics: Monitoring Oracle Fusion Business APIs</title><link href="https://royce-fu.com/blog/beyond-the-fusion-metrics-monitoring-oracle-fusion-business-apis/" rel="alternate" type="text/html" title="Beyond the Fusion Metrics: Monitoring Oracle Fusion Business APIs" /><published>2026-10-01T00:00:00+00:00</published><updated>2026-10-01T00:00:00+00:00</updated><id>https://royce-fu.com/blog/beyond-the-fusion-metrics-monitoring-oracle-fusion-business-apis</id><content type="html" xml:base="https://royce-fu.com/blog/beyond-the-fusion-metrics-monitoring-oracle-fusion-business-apis/"><![CDATA[<h1 id="beyond-the-fusion-metrics-monitoring-oracle-fusion-business-apis">Beyond the Fusion Metrics: Monitoring Oracle Fusion Business APIs</h1>

<p><em>A customer-inspired performance-monitoring pattern with OCI Application Performance Monitoring</em></p>

<p>This new monitoring paradigm grew out of a customer request to test the Oracle Fusion REST APIs that their business integrations depend on, with synthetic monitoring as the next step. It offers a way to check API availability and expected responses even when integration traffic is quiet.</p>

<p>That request points to a useful design shift for Fusion monitoring: <strong>organize checks around business API capabilities</strong>. An item lookup, an inventory query, or a work-order request gives availability a meaning that an integration team can act on. Each check combines an authenticated request, a small set of known test records, and explicit response assertions.</p>

<p>The customer request supplied the starting point, but the pattern applies more broadly. Fusion customers can choose the API capabilities on which their own processes depend, then check those capabilities from the locations and at the frequency that matter to them. In a broader Fusion observability approach, these outside-in API checks belong in the <strong>Performance pillar</strong>: they measure whether a selected business API responds correctly and how long the synthetic operation takes. <a href="https://www.ateam-oracle.com/real-user-monitoring-for-oracle-fusion-saas-cloud-apps-using-oci-apm-browser-agent">Real User Monitoring for Oracle Fusion SaaS Cloud Apps</a> examines the complementary experience of people using the Fusion interface, while <a href="https://www.ateam-oracle.com/fusion-apps-observability-by-collecting-ess-logs-using-oci-logging-analytics-rest-api-ingestion">ESS log collection</a> and <a href="https://www.ateam-oracle.com/gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai-part-3">ESS, audit, and security dashboards</a> show other operational and security signals. This pillar framing describes how to organize the monitoring design; it is not an OCI product category.</p>

<p>This post extends Fusion monitoring beyond native metrics by asking whether a selected, authenticated business API returns the expected data within an acceptable time from a chosen vantage point. Using OCI Application Performance Monitoring (APM) Availability Monitoring, we show how to create Scripted REST checks, configure where and when they run, and visualize availability, execution time, and failure trends. Items, inventories, work centers, and work orders illustrate scoped GET checks; a read-only batch shows how to test POST without changing business records. Together, these examples give Fusion teams a pattern they can adapt to their own critical integrations while keeping customer-specific workflows and records private.</p>

<h2 id="reference-architecture-fusion-business-apis-and-apm-availability-monitoring">Reference architecture: Fusion business APIs and APM Availability Monitoring</h2>

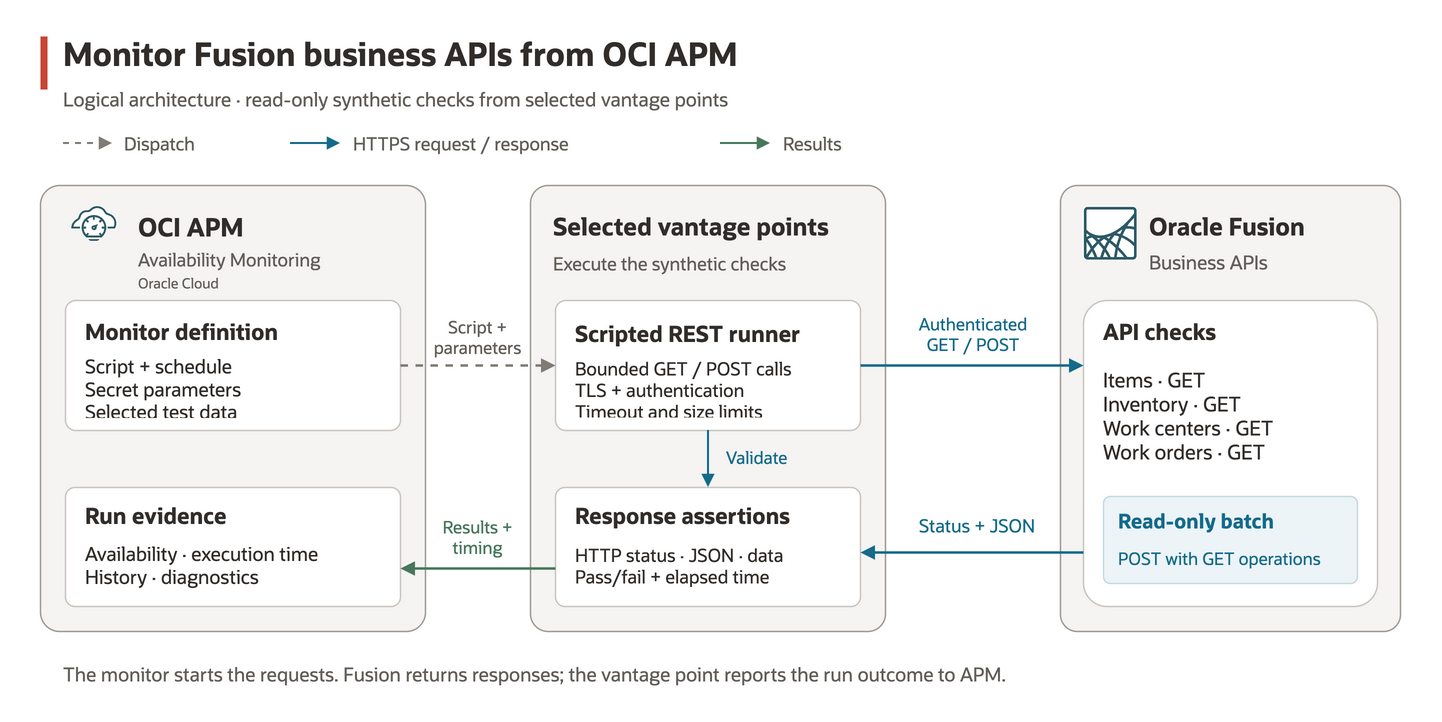
<p>In OCI APM, these synthetic checks are configured under <strong>Availability Monitoring</strong>. APM schedules the monitor, a selected execution location sends requests to Fusion, and the results return to APM for analysis. Requests originate at the vantage point; this outside-in design needs no monitoring agent inside Fusion. The architecture connects each business API capability to a repeatable availability check. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/use-synthetic-monitoring.html">Use Availability Monitoring</a></p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/architecture.png" alt="OCI APM Availability Monitoring dispatches a configured Scripted REST monitor to a vantage point, which calls Fusion business APIs, validates responses, and returns results to APM." /></p>

<p><em>Figure 1. Reference architecture for Fusion Business API endpoint monitoring via OCI APM.</em></p>

<p>The components have distinct responsibilities:</p>

<table>
  <thead>
    <tr>
      <th>Component</th>
      <th>Role in this design</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong>APM domain and Availability Monitoring</strong></td>
      <td>Organize scripts and monitors, schedule executions, and expose run history and metrics.</td>
    </tr>
    <tr>
      <td><strong>Scripted REST script</strong></td>
      <td>Define the HTTP requests, authentication headers, response assertions, and optional timing markers in JavaScript.</td>
    </tr>
    <tr>
      <td><strong>Monitor</strong></td>
      <td>Associate a script with parameter values, execution locations, frequency, timeout, and availability settings. One script can be reused with different monitor configurations.</td>
    </tr>
    <tr>
      <td><strong>Vantage point</strong></td>
      <td>Run the script, call Fusion over HTTPS, evaluate the responses, and report the outcome.</td>
    </tr>
    <tr>
      <td><strong>Fusion business APIs</strong></td>
      <td>Serve the authenticated requests using the monitoring account’s access and selected test records.</td>
    </tr>
    <tr>
      <td><strong>Metrics, history, and dashboards</strong></td>
      <td>Show availability and timing trends, locate failed executions, and connect observations to a monitor and location.</td>
    </tr>
  </tbody>
</table>

<p>For a scripted monitor, the <strong>script defines what to test</strong>; the <strong>monitor defines how and where it runs</strong>. For example, an items script contains the lookup and assertions, while a monitor named <code class="language-plaintext highlighter-rouge">fusion_items</code> supplies the pod, test values, schedule, and locations.</p>

<h3 id="choose-the-monitor-type-for-the-test">Choose the monitor type for the test</h3>

<p>Availability Monitoring provides several monitor types, each suited to a different kind of test:</p>

<table>
  <thead>
    <tr>
      <th>Monitor type</th>
      <th>What it tests</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong>Browser</strong></td>
      <td>Loads one web page in a browser to measure page performance and check its response.</td>
    </tr>
    <tr>
      <td><strong>Scripted Browser</strong></td>
      <td>Runs a recorded browser workflow, such as signing in and navigating through a user transaction.</td>
    </tr>
    <tr>
      <td><strong>REST</strong></td>
      <td>Sends a single GET or POST request with configured authentication and response validation.</td>
    </tr>
    <tr>
      <td><strong>Scripted REST</strong></td>
      <td>Runs JavaScript-defined API requests, sequencing, and custom response assertions.</td>
    </tr>
    <tr>
      <td><strong>Network</strong></td>
      <td>Checks host reachability and network performance using TCP or ICMP probes.</td>
    </tr>
    <tr>
      <td><strong>DNS</strong></td>
      <td>Tests DNS resolution, delegation, or DNSSEC validation.</td>
    </tr>
    <tr>
      <td><strong>SQL</strong></td>
      <td>Executes a SELECT query against a reachable supported database and measures its performance.</td>
    </tr>
    <tr>
      <td><strong>FTP</strong></td>
      <td>Tests file listing, upload, or download over FTP, FTPS, or SFTP.</td>
    </tr>
  </tbody>
</table>

<p>Oracle’s <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-monitor.html">monitor type and configuration documentation</a> describes the settings for each type. SQL monitoring requires an accessible database; a Fusion REST endpoint does not provide that database connection.</p>

<p>We use <strong>Scripted REST</strong> because this API testing use case needs queries built from test values, validation of returned JSON and batch parts, and timing around named operations. JavaScript gives the check control over those requests and assertions. The REST monitor also supports POST; the reason for choosing Scripted REST here is the programmable test logic. Browser monitors suit checks of the Fusion user interface.</p>

<h3 id="what-is-a-vantage-point">What is a vantage point?</h3>

<p>A vantage point is where APM runs a monitor and sends its requests. Oracle provides public locations in OCI data centers and in external data centers; the locations labeled <strong>External</strong> are part of that public offering. You can also run monitors from locations you operate in your tenancy or on a VM in another network. <a href="https://www.oracle.com/manageability/application-performance-monitoring/">Oracle APM vantage-point overview</a></p>

<table>
  <thead>
    <tr>
      <th>Vantage point</th>
      <th>Where the check runs</th>
      <th>When it helps</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong>Public, OCI location</strong></td>
      <td>An Oracle-managed location in an OCI data center.</td>
      <td>Check a publicly reachable Fusion API from a selected OCI region. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/synthetic-monitoring.html">Availability Monitoring setup</a></td>
    </tr>
    <tr>
      <td><strong>Public, External location</strong></td>
      <td>An Oracle-managed location in an external data center.</td>
      <td>See how the same public API responds from a location outside OCI. <a href="https://www.oracle.com/manageability/application-performance-monitoring/">Oracle APM overview</a></td>
    </tr>
    <tr>
      <td><strong>Dedicated</strong></td>
      <td>A location set up inside your OCI tenancy and network.</td>
      <td>Run checks through your chosen VCN path, including access to private endpoints when that network is configured to reach them. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/use-dedicated-vantage-points.html">Dedicated vantage points</a></td>
    </tr>
    <tr>
      <td><strong>On-premise</strong></td>
      <td>An Availability Monitoring worker deployed on a VM in a network you operate.</td>
      <td>Test a private endpoint from that network; use a non-browser worker for a Scripted REST check. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/use-onpremise-vantage-points.html">On-premise vantage points</a>, <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/download-synthetic-worker.html">worker types</a></td>
    </tr>
  </tbody>
</table>

<p>This exercise uses selected public vantage points for a reachable Fusion pod. Choose additional locations based on the network path the integration uses; each location contributes its own execution result.</p>

<p>At each selected vantage point, the script builds the request, authenticates with the monitoring account, and checks the returned data. A failed assertion fails that execution. Comparing the same check across locations helps distinguish a widespread problem from one concentrated along a particular access path.</p>

<h3 id="create-a-script-for-an-api-check">Create a script for an API check</h3>

<p>Open <strong>Observability &amp; Management → Application Performance Monitoring → Availability Monitoring → Scripts</strong>, select the compartment and APM domain, and choose <strong>Create Script</strong>. Upload a JavaScript <code class="language-plaintext highlighter-rouge">.js</code> file. After saving the script, create a <strong>Scripted REST</strong> monitor that references it. Oracle documents <code class="language-plaintext highlighter-rouge">postman-request</code> for HTTP calls and ORAP placeholders for parameters, including secret values. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-script.html">Create an APM script</a></p>

<p>This compact items example shows the pattern. Set <code class="language-plaintext highlighter-rouge">BASE_URL</code> to the HTTPS origin, <code class="language-plaintext highlighter-rouge">BASIC_AUTH_B64</code> to Base64 of the UTF-8 string <code class="language-plaintext highlighter-rouge">username:password</code> with <strong>Value is secret</strong> enabled, and <code class="language-plaintext highlighter-rouge">ITEM_QUERY</code> to an organization-and-item-scoped query, such as <code class="language-plaintext highlighter-rouge">OrganizationCode='DEMO_ORG' AND ItemNumber='DEMO_ITEM'</code>, using your own test values. Base64 is reversible encoding, so treat that authentication value as a credential. The query is supplied through <code class="language-plaintext highlighter-rouge">qs</code> so the request library URL-encodes it.</p>

<div class="language-javascript highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="kd">const</span> <span class="nx">request</span> <span class="o">=</span> <span class="nx">require</span><span class="p">(</span><span class="dl">"</span><span class="s2">postman-request</span><span class="dl">"</span><span class="p">);</span>
<span class="kd">const</span> <span class="nx">baseUrl</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">&lt;ORAP&gt;&lt;ON&gt;BASE_URL&lt;/ON&gt;&lt;OV&gt;SET_IN_APM&lt;/OV&gt;&lt;OS&gt;false&lt;/OS&gt;&lt;/ORAP&gt;</span><span class="dl">"</span><span class="p">;</span>
<span class="kd">const</span> <span class="nx">basicAuth</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">&lt;ORAP&gt;&lt;ON&gt;BASIC_AUTH_B64&lt;/ON&gt;&lt;OV&gt;SET_IN_APM&lt;/OV&gt;&lt;OS&gt;true&lt;/OS&gt;&lt;/ORAP&gt;</span><span class="dl">"</span><span class="p">;</span>
<span class="kd">const</span> <span class="nx">itemQuery</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">&lt;ORAP&gt;&lt;ON&gt;ITEM_QUERY&lt;/ON&gt;&lt;OV&gt;SET_IN_APM&lt;/OV&gt;&lt;OS&gt;true&lt;/OS&gt;&lt;/ORAP&gt;</span><span class="dl">"</span><span class="p">;</span>

<span class="k">if</span> <span class="p">([</span><span class="nx">baseUrl</span><span class="p">,</span> <span class="nx">basicAuth</span><span class="p">,</span> <span class="nx">itemQuery</span><span class="p">].</span><span class="nx">some</span><span class="p">(</span><span class="nx">v</span> <span class="o">=&gt;</span> <span class="o">!</span><span class="nx">v</span> <span class="o">||</span> <span class="sr">/SET_IN_APM|&lt;ORAP&gt;/</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nx">v</span><span class="p">)))</span> <span class="p">{</span>
  <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">CONFIG: set the script parameters</span><span class="dl">"</span><span class="p">);</span>
<span class="p">}</span>
<span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="sr">/^https:</span><span class="se">\/\/[</span><span class="sr">a-z0-9.-</span><span class="se">]</span><span class="sr">+$/i</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nx">baseUrl</span><span class="p">))</span> <span class="p">{</span>
  <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">CONFIG: BASE_URL must be an HTTPS origin without a trailing slash</span><span class="dl">"</span><span class="p">);</span>
<span class="p">}</span>

<span class="nx">oraSynCustomMarker</span><span class="p">(</span><span class="dl">"</span><span class="s2">item_lookup</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">startTime</span><span class="dl">"</span><span class="p">);</span>
<span class="nx">request</span><span class="p">({</span>
  <span class="na">method</span><span class="p">:</span> <span class="dl">"</span><span class="s2">GET</span><span class="dl">"</span><span class="p">,</span>
  <span class="na">url</span><span class="p">:</span> <span class="nx">baseUrl</span> <span class="o">+</span> <span class="dl">"</span><span class="s2">/fscmRestApi/resources/11.13.18.05/itemsV2</span><span class="dl">"</span><span class="p">,</span>
  <span class="na">qs</span><span class="p">:</span> <span class="p">{</span> <span class="na">q</span><span class="p">:</span> <span class="nx">itemQuery</span><span class="p">,</span> <span class="na">fields</span><span class="p">:</span> <span class="dl">"</span><span class="s2">ItemNumber,ItemId</span><span class="dl">"</span><span class="p">,</span> <span class="na">onlyData</span><span class="p">:</span> <span class="kc">true</span><span class="p">,</span> <span class="na">limit</span><span class="p">:</span> <span class="mi">1</span> <span class="p">},</span>
  <span class="na">headers</span><span class="p">:</span> <span class="p">{</span>
    <span class="na">Authorization</span><span class="p">:</span> <span class="dl">"</span><span class="s2">Basic </span><span class="dl">"</span> <span class="o">+</span> <span class="nx">basicAuth</span><span class="p">,</span>
    <span class="na">Accept</span><span class="p">:</span> <span class="dl">"</span><span class="s2">application/json</span><span class="dl">"</span><span class="p">,</span>
    <span class="dl">"</span><span class="s2">REST-Framework-Version</span><span class="dl">"</span><span class="p">:</span> <span class="dl">"</span><span class="s2">4</span><span class="dl">"</span>
  <span class="p">},</span>
  <span class="na">strictSSL</span><span class="p">:</span> <span class="kc">true</span><span class="p">,</span> <span class="na">followRedirect</span><span class="p">:</span> <span class="kc">false</span><span class="p">,</span> <span class="na">followAllRedirects</span><span class="p">:</span> <span class="kc">false</span><span class="p">,</span>
  <span class="na">timeout</span><span class="p">:</span> <span class="mi">20000</span>
<span class="p">},</span> <span class="p">(</span><span class="nx">error</span><span class="p">,</span> <span class="nx">response</span><span class="p">,</span> <span class="nx">body</span><span class="p">)</span> <span class="o">=&gt;</span> <span class="p">{</span>
  <span class="k">if</span> <span class="p">(</span><span class="nx">error</span><span class="p">)</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">REQUEST: item_lookup</span><span class="dl">"</span><span class="p">);</span>
  <span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">response</span> <span class="o">||</span> <span class="nx">response</span><span class="p">.</span><span class="nx">statusCode</span> <span class="o">!==</span> <span class="mi">200</span><span class="p">)</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">HTTP: item_lookup</span><span class="dl">"</span><span class="p">);</span>
  <span class="kd">let</span> <span class="nx">data</span><span class="p">;</span>
  <span class="k">try</span> <span class="p">{</span> <span class="nx">data</span> <span class="o">=</span> <span class="nx">JSON</span><span class="p">.</span><span class="nx">parse</span><span class="p">(</span><span class="nx">body</span><span class="p">);</span> <span class="p">}</span>
  <span class="k">catch</span> <span class="p">(</span><span class="nx">_</span><span class="p">)</span> <span class="p">{</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">JSON: item_lookup</span><span class="dl">"</span><span class="p">);</span> <span class="p">}</span>
  <span class="kd">const</span> <span class="nx">item</span> <span class="o">=</span> <span class="nx">data</span> <span class="o">&amp;&amp;</span> <span class="nb">Array</span><span class="p">.</span><span class="nx">isArray</span><span class="p">(</span><span class="nx">data</span><span class="p">.</span><span class="nx">items</span><span class="p">)</span> <span class="o">&amp;&amp;</span> <span class="nx">data</span><span class="p">.</span><span class="nx">items</span><span class="p">[</span><span class="mi">0</span><span class="p">];</span>
  <span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">item</span> <span class="o">||</span> <span class="nx">item</span><span class="p">.</span><span class="nx">ItemNumber</span> <span class="o">==</span> <span class="kc">null</span> <span class="o">||</span> <span class="nx">item</span><span class="p">.</span><span class="nx">ItemId</span> <span class="o">==</span> <span class="kc">null</span><span class="p">)</span> <span class="p">{</span>
    <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">ASSERT: item_lookup expected item fields</span><span class="dl">"</span><span class="p">);</span>
  <span class="p">}</span>
  <span class="nx">oraSynCustomMarker</span><span class="p">(</span><span class="dl">"</span><span class="s2">item_lookup</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">endTime</span><span class="dl">"</span><span class="p">);</span>
  <span class="nx">console</span><span class="p">.</span><span class="nx">log</span><span class="p">(</span><span class="dl">"</span><span class="s2">PASS: item_lookup</span><span class="dl">"</span><span class="p">);</span>
<span class="p">});</span>
</code></pre></div></div>

<p><em>This is an illustrative single-request check, verified locally with mocked responses; it has not been executed as a hosted monitor. It checks status, JSON, and item-field presence. The fuller scripts add stricter input validation, response-size and pagination controls, and sanitized diagnostic detail.</em></p>

<p>The paired literal markers measure the successful <code class="language-plaintext highlighter-rouge">item_lookup</code> step, including response validation. Failed checks throw a short diagnostic without printing credentials or returned records. The example uses a direct <code class="language-plaintext highlighter-rouge">ITEM_QUERY</code> parameter for readability; the fuller monitors build their queries from the fixture supplied in <code class="language-plaintext highlighter-rouge">FIXTURE_B64</code>.</p>

<h3 id="what-data-does-apm-collect">What data does APM collect?</h3>

<p>APM publishes availability and monitor execution-time metrics, with dimensions that include the monitor and vantage point. These support comparisons across locations and over time. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring-metrics.html">APM metric definitions</a></p>

<p>The scripts add context through named timing markers and sanitized output:</p>

<ul>
  <li><strong>Availability:</strong> whether the execution satisfied the configured checks. A failure can reflect connectivity, authentication, response validation, or a fixture that needs attention.</li>
  <li><strong>Execution time:</strong> how long the complete monitor took, plus custom durations around named script steps. A GET step can include pagination and validation; the batch marker measures the complete batch check.</li>
  <li><strong>Response evidence:</strong> whether the expected HTTP status, JSON structure, selected fields, and applicable identity checks passed. Success output includes bounded row and request counts.</li>
  <li><strong>Failure context:</strong> the operation that failed and a diagnostic such as a missing parameter, an HTTP error, or a transport error. Credentials and response bodies are excluded from the script’s own logs.</li>
</ul>

<p>These signals help direct investigation. A missing fixture value calls for a configuration check. An HTTP 401 calls for investigation of authentication and access. Slower results concentrated at one vantage point suggest comparing that location’s access path with the others before attributing the delay to Fusion.</p>

<p>Custom assertions may appear under APM’s <strong>Unknown Error</strong> category, so inspect the script error message as well. A completed timing marker may also be absent when the execution fails early.</p>

<h2 id="monitor-the-business-contexts">Monitor the business contexts</h2>

<p>For an integration, availability includes being able to authenticate, access the intended resource, and receive a usable response. A successful HTTP connection is one part of that contract. The script also needs to check the response against a defined expectation.</p>

<p>A <strong>fixture</strong> supplies that context: a known item and organization, an existing work center, or a work order selected for testing. The script uses those values to make a focused request and evaluate the result. Small page limits and a request timeout keep each execution bounded.</p>

<table>
  <thead>
    <tr>
      <th>Business capability</th>
      <th>Illustrative request</th>
      <th>What the check examines</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Items</td>
      <td>GET <code class="language-plaintext highlighter-rouge">/itemsV2</code></td>
      <td>An organization-and-item-scoped lookup returns records with the expected item fields.</td>
    </tr>
    <tr>
      <td>Inventories</td>
      <td>GET <code class="language-plaintext highlighter-rouge">/subinventories</code></td>
      <td>An organization-scoped query returns inventory reference records with expected fields such as the subinventory name.</td>
    </tr>
    <tr>
      <td>Work centers</td>
      <td>GET <code class="language-plaintext highlighter-rouge">/workCenters</code></td>
      <td>A query for a known active work center returns the intended center.</td>
    </tr>
    <tr>
      <td>Work orders</td>
      <td>GET <code class="language-plaintext highlighter-rouge">/workOrders</code></td>
      <td>A query for an existing work order returns a nonempty response with the selected fields.</td>
    </tr>
    <tr>
      <td>Read-only batch</td>
      <td>POST to the REST API root</td>
      <td>One batch request returns the expected item and work-order read results.</td>
    </tr>
  </tbody>
</table>

<p>These resource paths sit below <code class="language-plaintext highlighter-rouge">/fscmRestApi/resources/11.13.18.05</code>. They are representative checks, rather than complete request definitions; each needs an appropriate query and fixture for the target pod.</p>

<p>The assertions determine what a green result means. In this implementation, the GET checks generally validate HTTP status, JSON content, nonempty collections, and selected field presence; they do not all compare every returned value with the fixture. The batch check additionally verifies the requested record identities. Inventory quantities and completion of a business process are outside these checks.</p>

<h2 id="exercise-post-with-a-read-only-batch">Exercise POST with a read-only batch</h2>

<p>POST is useful here because Oracle’s batch interface accepts an envelope containing multiple operations, including reads. Our example posts to <code class="language-plaintext highlighter-rouge">/fscmRestApi/resources/11.13.18.05/</code> with the media type <code class="language-plaintext highlighter-rouge">application/vnd.oracle.adf.batch+json</code>. Both enclosed operations use <code class="language-plaintext highlighter-rouge">get</code>. <a href="https://docs.oracle.com/en/cloud/saas/supply-chain-and-manufacturing/26b/fasrp/Batch_Actions.html">Oracle batch actions</a></p>

<p>The abbreviated body below illustrates the idea. The paths contain explanatory placeholders; the actual script constructs and URL-encodes queries from private fixture values.</p>

<div class="language-json highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="p">{</span><span class="w">
  </span><span class="nl">"parts"</span><span class="p">:</span><span class="w"> </span><span class="p">[</span><span class="w">
    </span><span class="p">{</span><span class="w">
      </span><span class="nl">"id"</span><span class="p">:</span><span class="w"> </span><span class="s2">"item_lookup"</span><span class="p">,</span><span class="w">
      </span><span class="nl">"path"</span><span class="p">:</span><span class="w"> </span><span class="s2">"/itemsV2?&lt;scoped item query&gt;"</span><span class="p">,</span><span class="w">
      </span><span class="nl">"operation"</span><span class="p">:</span><span class="w"> </span><span class="s2">"get"</span><span class="w">
    </span><span class="p">},</span><span class="w">
    </span><span class="p">{</span><span class="w">
      </span><span class="nl">"id"</span><span class="p">:</span><span class="w"> </span><span class="s2">"work_order"</span><span class="p">,</span><span class="w">
      </span><span class="nl">"path"</span><span class="p">:</span><span class="w"> </span><span class="s2">"/workOrders?&lt;known work-order query&gt;"</span><span class="p">,</span><span class="w">
      </span><span class="nl">"operation"</span><span class="p">:</span><span class="w"> </span><span class="s2">"get"</span><span class="w">
    </span><span class="p">}</span><span class="w">
  </span><span class="p">]</span><span class="w">
</span><span class="p">}</span><span class="w">
</span></code></pre></div></div>

<p>A <strong>Scripted REST</strong> monitor can send that batch request with JavaScript. The example below takes <code class="language-plaintext highlighter-rouge">BASE_URL</code> as the HTTPS origin, <code class="language-plaintext highlighter-rouge">BASIC_AUTH_B64</code> as the secret Base64 value of <code class="language-plaintext highlighter-rouge">username:password</code>, and <code class="language-plaintext highlighter-rouge">FIXTURE_B64</code> as a secret Base64-encoded JSON object containing <code class="language-plaintext highlighter-rouge">organization_code</code>, <code class="language-plaintext highlighter-rouge">item_number</code>, and <code class="language-plaintext highlighter-rouge">work_order_id</code>. Supply existing test records when setting the monitor parameters. The script fixes both batch operations to <code class="language-plaintext highlighter-rouge">get</code> and URL-encodes their scoped queries.</p>

<div class="language-javascript highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="kd">const</span> <span class="nx">request</span> <span class="o">=</span> <span class="nx">require</span><span class="p">(</span><span class="dl">"</span><span class="s2">postman-request</span><span class="dl">"</span><span class="p">);</span>
<span class="kd">const</span> <span class="nx">baseUrl</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">&lt;ORAP&gt;&lt;ON&gt;BASE_URL&lt;/ON&gt;&lt;OV&gt;SET_IN_APM&lt;/OV&gt;&lt;OS&gt;false&lt;/OS&gt;&lt;/ORAP&gt;</span><span class="dl">"</span><span class="p">;</span>
<span class="kd">const</span> <span class="nx">basicAuth</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">&lt;ORAP&gt;&lt;ON&gt;BASIC_AUTH_B64&lt;/ON&gt;&lt;OV&gt;SET_IN_APM&lt;/OV&gt;&lt;OS&gt;true&lt;/OS&gt;&lt;/ORAP&gt;</span><span class="dl">"</span><span class="p">;</span>
<span class="kd">const</span> <span class="nx">fixtureB64</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">&lt;ORAP&gt;&lt;ON&gt;FIXTURE_B64&lt;/ON&gt;&lt;OV&gt;SET_IN_APM&lt;/OV&gt;&lt;OS&gt;true&lt;/OS&gt;&lt;/ORAP&gt;</span><span class="dl">"</span><span class="p">;</span>
<span class="kd">const</span> <span class="nx">apiPath</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">/fscmRestApi/resources/11.13.18.05</span><span class="dl">"</span><span class="p">;</span>
<span class="kd">const</span> <span class="nx">mediaType</span> <span class="o">=</span> <span class="dl">"</span><span class="s2">application/vnd.oracle.adf.batch+json</span><span class="dl">"</span><span class="p">;</span>

<span class="k">if</span> <span class="p">([</span><span class="nx">baseUrl</span><span class="p">,</span> <span class="nx">basicAuth</span><span class="p">,</span> <span class="nx">fixtureB64</span><span class="p">].</span><span class="nx">some</span><span class="p">(</span><span class="nx">v</span> <span class="o">=&gt;</span> <span class="o">!</span><span class="nx">v</span> <span class="o">||</span> <span class="sr">/SET_IN_APM|&lt;ORAP&gt;/</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nx">v</span><span class="p">))</span> <span class="o">||</span>
    <span class="o">!</span><span class="sr">/^https:</span><span class="se">\/\/[</span><span class="sr">a-z0-9.-</span><span class="se">]</span><span class="sr">+$/i</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nx">baseUrl</span><span class="p">))</span> <span class="p">{</span>
  <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">CONFIG: set valid script parameters</span><span class="dl">"</span><span class="p">);</span>
<span class="p">}</span>
<span class="kd">let</span> <span class="nx">fixture</span><span class="p">;</span>
<span class="k">try</span> <span class="p">{</span> <span class="nx">fixture</span> <span class="o">=</span> <span class="nx">JSON</span><span class="p">.</span><span class="nx">parse</span><span class="p">(</span><span class="nx">Buffer</span><span class="p">.</span><span class="k">from</span><span class="p">(</span><span class="nx">fixtureB64</span><span class="p">,</span> <span class="dl">"</span><span class="s2">base64</span><span class="dl">"</span><span class="p">).</span><span class="nx">toString</span><span class="p">(</span><span class="dl">"</span><span class="s2">utf8</span><span class="dl">"</span><span class="p">));</span> <span class="p">}</span>
<span class="k">catch</span> <span class="p">(</span><span class="nx">_</span><span class="p">)</span> <span class="p">{</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">CONFIG: FIXTURE_B64</span><span class="dl">"</span><span class="p">);</span> <span class="p">}</span>
<span class="kd">function</span> <span class="nx">safeText</span><span class="p">(</span><span class="nx">value</span><span class="p">)</span> <span class="p">{</span>
  <span class="k">return</span> <span class="k">typeof</span> <span class="nx">value</span> <span class="o">===</span> <span class="dl">"</span><span class="s2">string</span><span class="dl">"</span> <span class="o">&amp;&amp;</span> <span class="o">!!</span><span class="nx">value</span><span class="p">.</span><span class="nx">trim</span><span class="p">()</span> <span class="o">&amp;&amp;</span> <span class="nx">value</span><span class="p">.</span><span class="nx">length</span> <span class="o">&lt;=</span> <span class="mi">128</span> <span class="o">&amp;&amp;</span>
    <span class="o">!</span><span class="sr">/</span><span class="se">[\x</span><span class="sr">00-</span><span class="se">\x</span><span class="sr">1f</span><span class="se">\x</span><span class="sr">7f</span><span class="se">]</span><span class="sr">/</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nx">value</span><span class="p">);</span>
<span class="p">}</span>
<span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">fixture</span> <span class="o">||</span> <span class="k">typeof</span> <span class="nx">fixture</span><span class="p">.</span><span class="nx">organization_code</span> <span class="o">!==</span> <span class="dl">"</span><span class="s2">string</span><span class="dl">"</span> <span class="o">||</span>
    <span class="k">typeof</span> <span class="nx">fixture</span><span class="p">.</span><span class="nx">item_number</span> <span class="o">!==</span> <span class="dl">"</span><span class="s2">string</span><span class="dl">"</span> <span class="o">||</span>
    <span class="o">!</span><span class="sr">/^</span><span class="se">[</span><span class="sr">1-9</span><span class="se">][</span><span class="sr">0-9</span><span class="se">]{0,17}</span><span class="sr">$/</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nb">String</span><span class="p">(</span><span class="nx">fixture</span><span class="p">.</span><span class="nx">work_order_id</span><span class="p">))</span> <span class="o">||</span>
    <span class="o">!</span><span class="nx">safeText</span><span class="p">(</span><span class="nx">fixture</span><span class="p">.</span><span class="nx">organization_code</span><span class="p">)</span> <span class="o">||</span> <span class="o">!</span><span class="nx">safeText</span><span class="p">(</span><span class="nx">fixture</span><span class="p">.</span><span class="nx">item_number</span><span class="p">))</span> <span class="p">{</span>
  <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">CONFIG: expected item, organization, and work order</span><span class="dl">"</span><span class="p">);</span>
<span class="p">}</span>
<span class="kd">function</span> <span class="nx">quoted</span><span class="p">(</span><span class="nx">value</span><span class="p">)</span> <span class="p">{</span> <span class="k">return</span> <span class="dl">"</span><span class="s2">'</span><span class="dl">"</span> <span class="o">+</span> <span class="nx">value</span><span class="p">.</span><span class="nx">replace</span><span class="p">(</span><span class="sr">/'/g</span><span class="p">,</span> <span class="dl">"</span><span class="s2">''</span><span class="dl">"</span><span class="p">)</span> <span class="o">+</span> <span class="dl">"</span><span class="s2">'</span><span class="dl">"</span><span class="p">;</span> <span class="p">}</span>
<span class="kd">function</span> <span class="nx">path</span><span class="p">(</span><span class="nx">resource</span><span class="p">,</span> <span class="nx">query</span><span class="p">,</span> <span class="nx">fields</span><span class="p">)</span> <span class="p">{</span>
  <span class="k">return</span> <span class="dl">"</span><span class="s2">/</span><span class="dl">"</span> <span class="o">+</span> <span class="nx">resource</span> <span class="o">+</span> <span class="dl">"</span><span class="s2">?q=</span><span class="dl">"</span> <span class="o">+</span> <span class="nb">encodeURIComponent</span><span class="p">(</span><span class="nx">query</span><span class="p">)</span> <span class="o">+</span>
    <span class="dl">"</span><span class="s2">&amp;fields=</span><span class="dl">"</span> <span class="o">+</span> <span class="nb">encodeURIComponent</span><span class="p">(</span><span class="nx">fields</span><span class="p">)</span> <span class="o">+</span> <span class="dl">"</span><span class="s2">&amp;limit=1&amp;onlyData=true</span><span class="dl">"</span><span class="p">;</span>
<span class="p">}</span>
<span class="kd">const</span> <span class="nx">parts</span> <span class="o">=</span> <span class="p">[</span>
  <span class="p">{</span> <span class="na">id</span><span class="p">:</span> <span class="dl">"</span><span class="s2">item_lookup</span><span class="dl">"</span><span class="p">,</span> <span class="na">operation</span><span class="p">:</span> <span class="dl">"</span><span class="s2">get</span><span class="dl">"</span><span class="p">,</span>
    <span class="na">path</span><span class="p">:</span> <span class="nx">path</span><span class="p">(</span><span class="dl">"</span><span class="s2">itemsV2</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">OrganizationCode=</span><span class="dl">"</span> <span class="o">+</span> <span class="nx">quoted</span><span class="p">(</span><span class="nx">fixture</span><span class="p">.</span><span class="nx">organization_code</span><span class="p">)</span> <span class="o">+</span>
      <span class="dl">"</span><span class="s2"> AND ItemNumber=</span><span class="dl">"</span> <span class="o">+</span> <span class="nx">quoted</span><span class="p">(</span><span class="nx">fixture</span><span class="p">.</span><span class="nx">item_number</span><span class="p">),</span> <span class="dl">"</span><span class="s2">ItemId,ItemNumber,OrganizationCode</span><span class="dl">"</span><span class="p">)</span> <span class="p">},</span>
  <span class="p">{</span> <span class="na">id</span><span class="p">:</span> <span class="dl">"</span><span class="s2">work_order</span><span class="dl">"</span><span class="p">,</span> <span class="na">operation</span><span class="p">:</span> <span class="dl">"</span><span class="s2">get</span><span class="dl">"</span><span class="p">,</span>
    <span class="na">path</span><span class="p">:</span> <span class="nx">path</span><span class="p">(</span><span class="dl">"</span><span class="s2">workOrders</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">WorkOrderId=</span><span class="dl">"</span> <span class="o">+</span> <span class="nx">fixture</span><span class="p">.</span><span class="nx">work_order_id</span><span class="p">,</span>
      <span class="dl">"</span><span class="s2">WorkOrderId,WorkOrderNumber</span><span class="dl">"</span><span class="p">)</span> <span class="p">}</span>
<span class="p">];</span>

<span class="nx">oraSynCustomMarker</span><span class="p">(</span><span class="dl">"</span><span class="s2">batch_readonly</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">startTime</span><span class="dl">"</span><span class="p">);</span>
<span class="nx">request</span><span class="p">({</span>
  <span class="na">method</span><span class="p">:</span> <span class="dl">"</span><span class="s2">POST</span><span class="dl">"</span><span class="p">,</span> <span class="na">url</span><span class="p">:</span> <span class="nx">baseUrl</span> <span class="o">+</span> <span class="nx">apiPath</span> <span class="o">+</span> <span class="dl">"</span><span class="s2">/</span><span class="dl">"</span><span class="p">,</span>
  <span class="na">body</span><span class="p">:</span> <span class="nx">JSON</span><span class="p">.</span><span class="nx">stringify</span><span class="p">({</span> <span class="nx">parts</span> <span class="p">}),</span>
  <span class="na">headers</span><span class="p">:</span> <span class="p">{</span> <span class="na">Authorization</span><span class="p">:</span> <span class="dl">"</span><span class="s2">Basic </span><span class="dl">"</span> <span class="o">+</span> <span class="nx">basicAuth</span><span class="p">,</span> <span class="na">Accept</span><span class="p">:</span> <span class="nx">mediaType</span><span class="p">,</span>
    <span class="dl">"</span><span class="s2">Content-Type</span><span class="dl">"</span><span class="p">:</span> <span class="nx">mediaType</span><span class="p">,</span> <span class="dl">"</span><span class="s2">REST-Framework-Version</span><span class="dl">"</span><span class="p">:</span> <span class="dl">"</span><span class="s2">4</span><span class="dl">"</span> <span class="p">},</span>
  <span class="na">strictSSL</span><span class="p">:</span> <span class="kc">true</span><span class="p">,</span> <span class="na">followRedirect</span><span class="p">:</span> <span class="kc">false</span><span class="p">,</span> <span class="na">followAllRedirects</span><span class="p">:</span> <span class="kc">false</span><span class="p">,</span>
  <span class="na">timeout</span><span class="p">:</span> <span class="mi">20000</span>
<span class="p">},</span> <span class="p">(</span><span class="nx">error</span><span class="p">,</span> <span class="nx">response</span><span class="p">,</span> <span class="nx">body</span><span class="p">)</span> <span class="o">=&gt;</span> <span class="p">{</span>
  <span class="k">if</span> <span class="p">(</span><span class="nx">error</span><span class="p">)</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">REQUEST: batch_readonly</span><span class="dl">"</span><span class="p">);</span>
  <span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">response</span> <span class="o">||</span> <span class="nx">response</span><span class="p">.</span><span class="nx">statusCode</span> <span class="o">!==</span> <span class="mi">200</span><span class="p">)</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">HTTP: batch_readonly</span><span class="dl">"</span><span class="p">);</span>
  <span class="kd">const</span> <span class="nx">contentType</span> <span class="o">=</span> <span class="nx">response</span><span class="p">.</span><span class="nx">headers</span> <span class="o">&amp;&amp;</span> <span class="nx">response</span><span class="p">.</span><span class="nx">headers</span><span class="p">[</span><span class="dl">"</span><span class="s2">content-type</span><span class="dl">"</span><span class="p">];</span>
  <span class="k">if</span> <span class="p">(</span><span class="k">typeof</span> <span class="nx">contentType</span> <span class="o">!==</span> <span class="dl">"</span><span class="s2">string</span><span class="dl">"</span> <span class="o">||</span>
      <span class="o">!</span><span class="sr">/^application</span><span class="se">\/</span><span class="sr">vnd</span><span class="se">\.</span><span class="sr">oracle</span><span class="se">\.</span><span class="sr">adf</span><span class="se">\.</span><span class="sr">batch</span><span class="se">\+</span><span class="sr">json</span><span class="se">(?:\s</span><span class="sr">*;.*</span><span class="se">)?</span><span class="sr">$/i</span><span class="p">.</span><span class="nx">test</span><span class="p">(</span><span class="nx">contentType</span><span class="p">))</span> <span class="p">{</span>
    <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">CONTENT_TYPE: batch_readonly</span><span class="dl">"</span><span class="p">);</span>
  <span class="p">}</span>
  <span class="k">if</span> <span class="p">((</span><span class="k">typeof</span> <span class="nx">body</span> <span class="o">!==</span> <span class="dl">"</span><span class="s2">string</span><span class="dl">"</span> <span class="o">&amp;&amp;</span> <span class="o">!</span><span class="nx">Buffer</span><span class="p">.</span><span class="nx">isBuffer</span><span class="p">(</span><span class="nx">body</span><span class="p">))</span> <span class="o">||</span>
      <span class="nx">Buffer</span><span class="p">.</span><span class="nx">byteLength</span><span class="p">(</span><span class="nx">body</span><span class="p">)</span> <span class="o">&gt;</span> <span class="mi">2</span> <span class="o">*</span> <span class="mi">1024</span> <span class="o">*</span> <span class="mi">1024</span><span class="p">)</span> <span class="p">{</span>
    <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">BODY: batch_readonly</span><span class="dl">"</span><span class="p">);</span>
  <span class="p">}</span>
  <span class="kd">let</span> <span class="nx">result</span><span class="p">;</span>
  <span class="k">try</span> <span class="p">{</span> <span class="nx">result</span> <span class="o">=</span> <span class="nx">JSON</span><span class="p">.</span><span class="nx">parse</span><span class="p">(</span><span class="nx">body</span><span class="p">.</span><span class="nx">toString</span><span class="p">(</span><span class="dl">"</span><span class="s2">utf8</span><span class="dl">"</span><span class="p">));</span> <span class="p">}</span>
  <span class="k">catch</span> <span class="p">(</span><span class="nx">_</span><span class="p">)</span> <span class="p">{</span> <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">JSON: batch_readonly</span><span class="dl">"</span><span class="p">);</span> <span class="p">}</span>
  <span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">result</span> <span class="o">||</span> <span class="o">!</span><span class="nb">Array</span><span class="p">.</span><span class="nx">isArray</span><span class="p">(</span><span class="nx">result</span><span class="p">.</span><span class="nx">parts</span><span class="p">)</span> <span class="o">||</span> <span class="nx">result</span><span class="p">.</span><span class="nx">parts</span><span class="p">.</span><span class="nx">length</span> <span class="o">!==</span> <span class="mi">2</span><span class="p">)</span> <span class="p">{</span>
    <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">BATCH: expected two parts</span><span class="dl">"</span><span class="p">);</span>
  <span class="p">}</span>
  <span class="kd">const</span> <span class="nx">byId</span> <span class="o">=</span> <span class="nb">Object</span><span class="p">.</span><span class="nx">create</span><span class="p">(</span><span class="kc">null</span><span class="p">);</span>
  <span class="k">for</span> <span class="p">(</span><span class="kd">const</span> <span class="nx">part</span> <span class="k">of</span> <span class="nx">result</span><span class="p">.</span><span class="nx">parts</span><span class="p">)</span> <span class="p">{</span>
    <span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">part</span> <span class="o">||</span> <span class="o">!</span><span class="p">[</span><span class="dl">"</span><span class="s2">item_lookup</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">work_order</span><span class="dl">"</span><span class="p">].</span><span class="nx">includes</span><span class="p">(</span><span class="nx">part</span><span class="p">.</span><span class="nx">id</span><span class="p">)</span> <span class="o">||</span>
        <span class="nx">byId</span><span class="p">[</span><span class="nx">part</span><span class="p">.</span><span class="nx">id</span><span class="p">]</span> <span class="o">||</span> <span class="nx">part</span><span class="p">.</span><span class="nx">operation</span> <span class="o">!==</span> <span class="dl">"</span><span class="s2">get</span><span class="dl">"</span> <span class="o">||</span> <span class="o">!</span><span class="nx">part</span><span class="p">.</span><span class="nx">payload</span> <span class="o">||</span>
        <span class="o">!</span><span class="nb">Array</span><span class="p">.</span><span class="nx">isArray</span><span class="p">(</span><span class="nx">part</span><span class="p">.</span><span class="nx">payload</span><span class="p">.</span><span class="nx">items</span><span class="p">)</span> <span class="o">||</span> <span class="nx">part</span><span class="p">.</span><span class="nx">payload</span><span class="p">.</span><span class="nx">items</span><span class="p">.</span><span class="nx">length</span> <span class="o">!==</span> <span class="mi">1</span><span class="p">)</span> <span class="p">{</span>
      <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">BATCH: missing or invalid read part</span><span class="dl">"</span><span class="p">);</span>
    <span class="p">}</span>
    <span class="nx">byId</span><span class="p">[</span><span class="nx">part</span><span class="p">.</span><span class="nx">id</span><span class="p">]</span> <span class="o">=</span> <span class="nx">part</span><span class="p">.</span><span class="nx">payload</span><span class="p">.</span><span class="nx">items</span><span class="p">[</span><span class="mi">0</span><span class="p">];</span>
  <span class="p">}</span>
  <span class="kd">const</span> <span class="nx">item</span> <span class="o">=</span> <span class="nx">byId</span><span class="p">.</span><span class="nx">item_lookup</span><span class="p">;</span>
  <span class="kd">const</span> <span class="nx">order</span> <span class="o">=</span> <span class="nx">byId</span><span class="p">.</span><span class="nx">work_order</span><span class="p">;</span>
  <span class="k">if</span> <span class="p">(</span><span class="o">!</span><span class="nx">item</span> <span class="o">||</span> <span class="nx">item</span><span class="p">.</span><span class="nx">ItemId</span> <span class="o">==</span> <span class="kc">null</span> <span class="o">||</span> <span class="nx">item</span><span class="p">.</span><span class="nx">ItemNumber</span> <span class="o">!==</span> <span class="nx">fixture</span><span class="p">.</span><span class="nx">item_number</span> <span class="o">||</span>
      <span class="nx">item</span><span class="p">.</span><span class="nx">OrganizationCode</span> <span class="o">!==</span> <span class="nx">fixture</span><span class="p">.</span><span class="nx">organization_code</span> <span class="o">||</span> <span class="o">!</span><span class="nx">order</span> <span class="o">||</span>
      <span class="nb">String</span><span class="p">(</span><span class="nx">order</span><span class="p">.</span><span class="nx">WorkOrderId</span><span class="p">)</span> <span class="o">!==</span> <span class="nb">String</span><span class="p">(</span><span class="nx">fixture</span><span class="p">.</span><span class="nx">work_order_id</span><span class="p">)</span> <span class="o">||</span>
      <span class="o">!</span><span class="nx">order</span><span class="p">.</span><span class="nx">WorkOrderNumber</span><span class="p">)</span> <span class="p">{</span>
    <span class="k">throw</span> <span class="k">new</span> <span class="nb">Error</span><span class="p">(</span><span class="dl">"</span><span class="s2">ASSERT: batch_readonly identities</span><span class="dl">"</span><span class="p">);</span>
  <span class="p">}</span>
  <span class="nx">oraSynCustomMarker</span><span class="p">(</span><span class="dl">"</span><span class="s2">batch_readonly</span><span class="dl">"</span><span class="p">,</span> <span class="dl">"</span><span class="s2">endTime</span><span class="dl">"</span><span class="p">);</span>
  <span class="nx">console</span><span class="p">.</span><span class="nx">log</span><span class="p">(</span><span class="dl">"</span><span class="s2">PASS: batch_readonly parts=2</span><span class="dl">"</span><span class="p">);</span>
<span class="p">});</span>
</code></pre></div></div>

<p><em>This compact example was verified locally with mocked responses; this exact excerpt has not been run as a hosted monitor. The fuller batch script adds stricter input, returned-path, pagination, and response-size handling. The monitoring account and fixture remain private.</em></p>

<p>The monitor validates the outer response and both returned parts, including their identities. HTTP 200 alone is insufficient: a missing, duplicate, erroneous, or mismatched part fails the check. The implementation fixes the two read operations in code rather than accepting arbitrary batch actions through parameters.</p>

<p>This exercises POST transport, authentication, batch processing, and result validation without creating or updating business records. It provides a useful additional monitoring pattern alongside the individual GET checks. Testing a business write would require its own transaction assertions and repeatable data lifecycle.</p>

<h2 id="monitor-fusion-api-endpoints-in-apm">Monitor Fusion API endpoints in APM</h2>

<p>Start with an APM domain, a monitoring account that can access the selected Fusion records, and a vantage point that can reach the pod. Prepare one stable fixture and confirm the request locally before scheduling it.</p>

<h3 id="1-upload-and-configure-the-script">1. Upload and configure the script</h3>

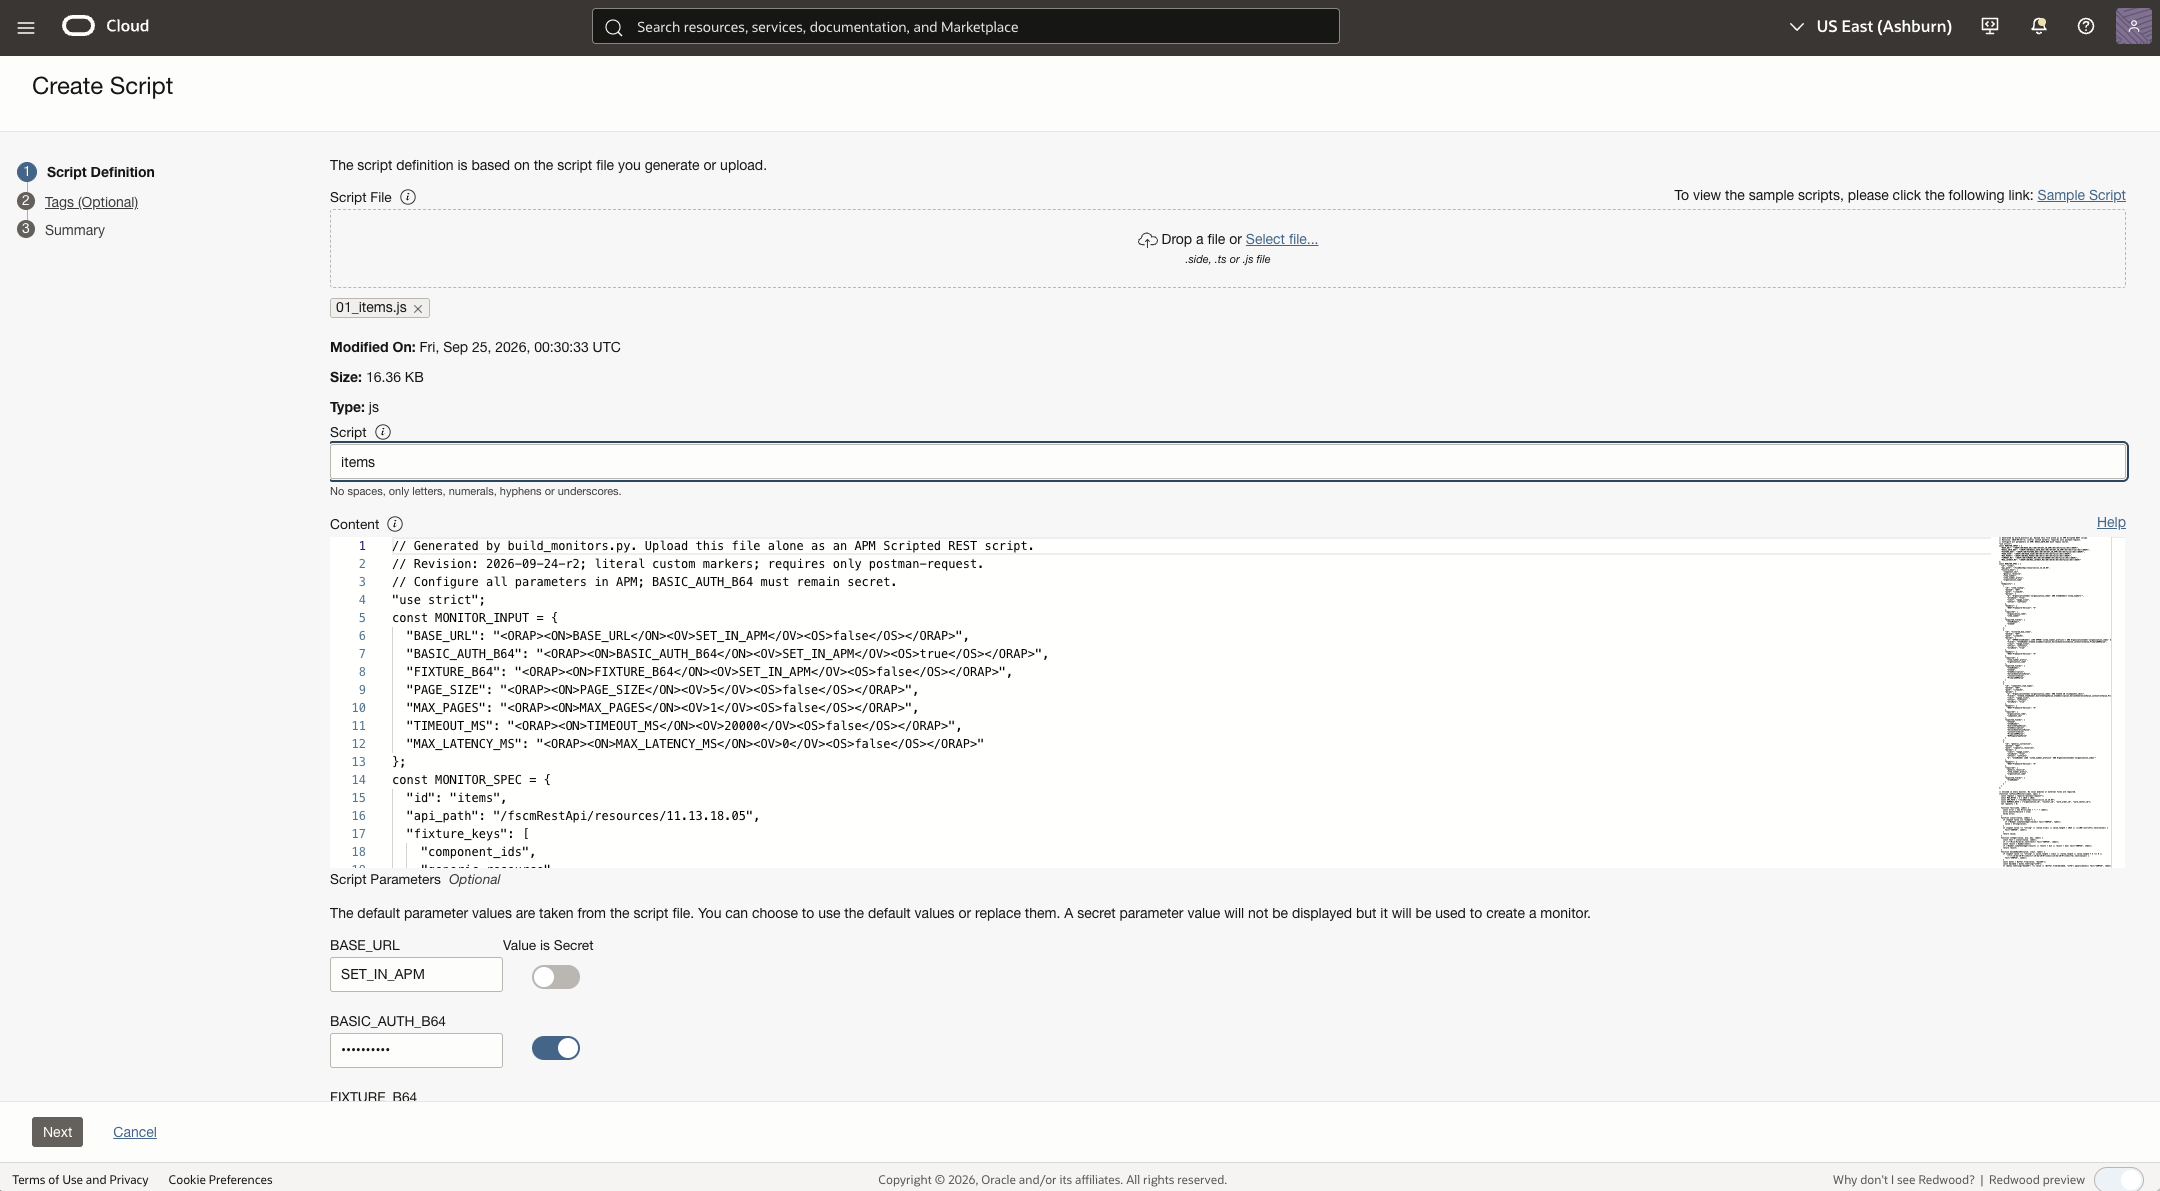
<p>In <strong>Observability &amp; Management → Application Performance Monitoring → Availability Monitoring</strong>, select the compartment and APM domain, open <strong>Scripts</strong>, and choose <strong>Create Script</strong>. On <strong>Script Definition</strong>, upload one <code class="language-plaintext highlighter-rouge">.js</code> file for the capability you want to check. For example, the items script contains its HTTP request and assertions; the read-only batch script contains its POST and two fixed GET parts. Confirm that the uploaded content is the intended version before continuing. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-script.html">Create an APM script</a></p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-script-upload.png" alt="Create Script page with the items JavaScript file uploaded and its content displayed." /></p>

<p><em>Figure 2. Uploading the full items Scripted REST file.</em></p>

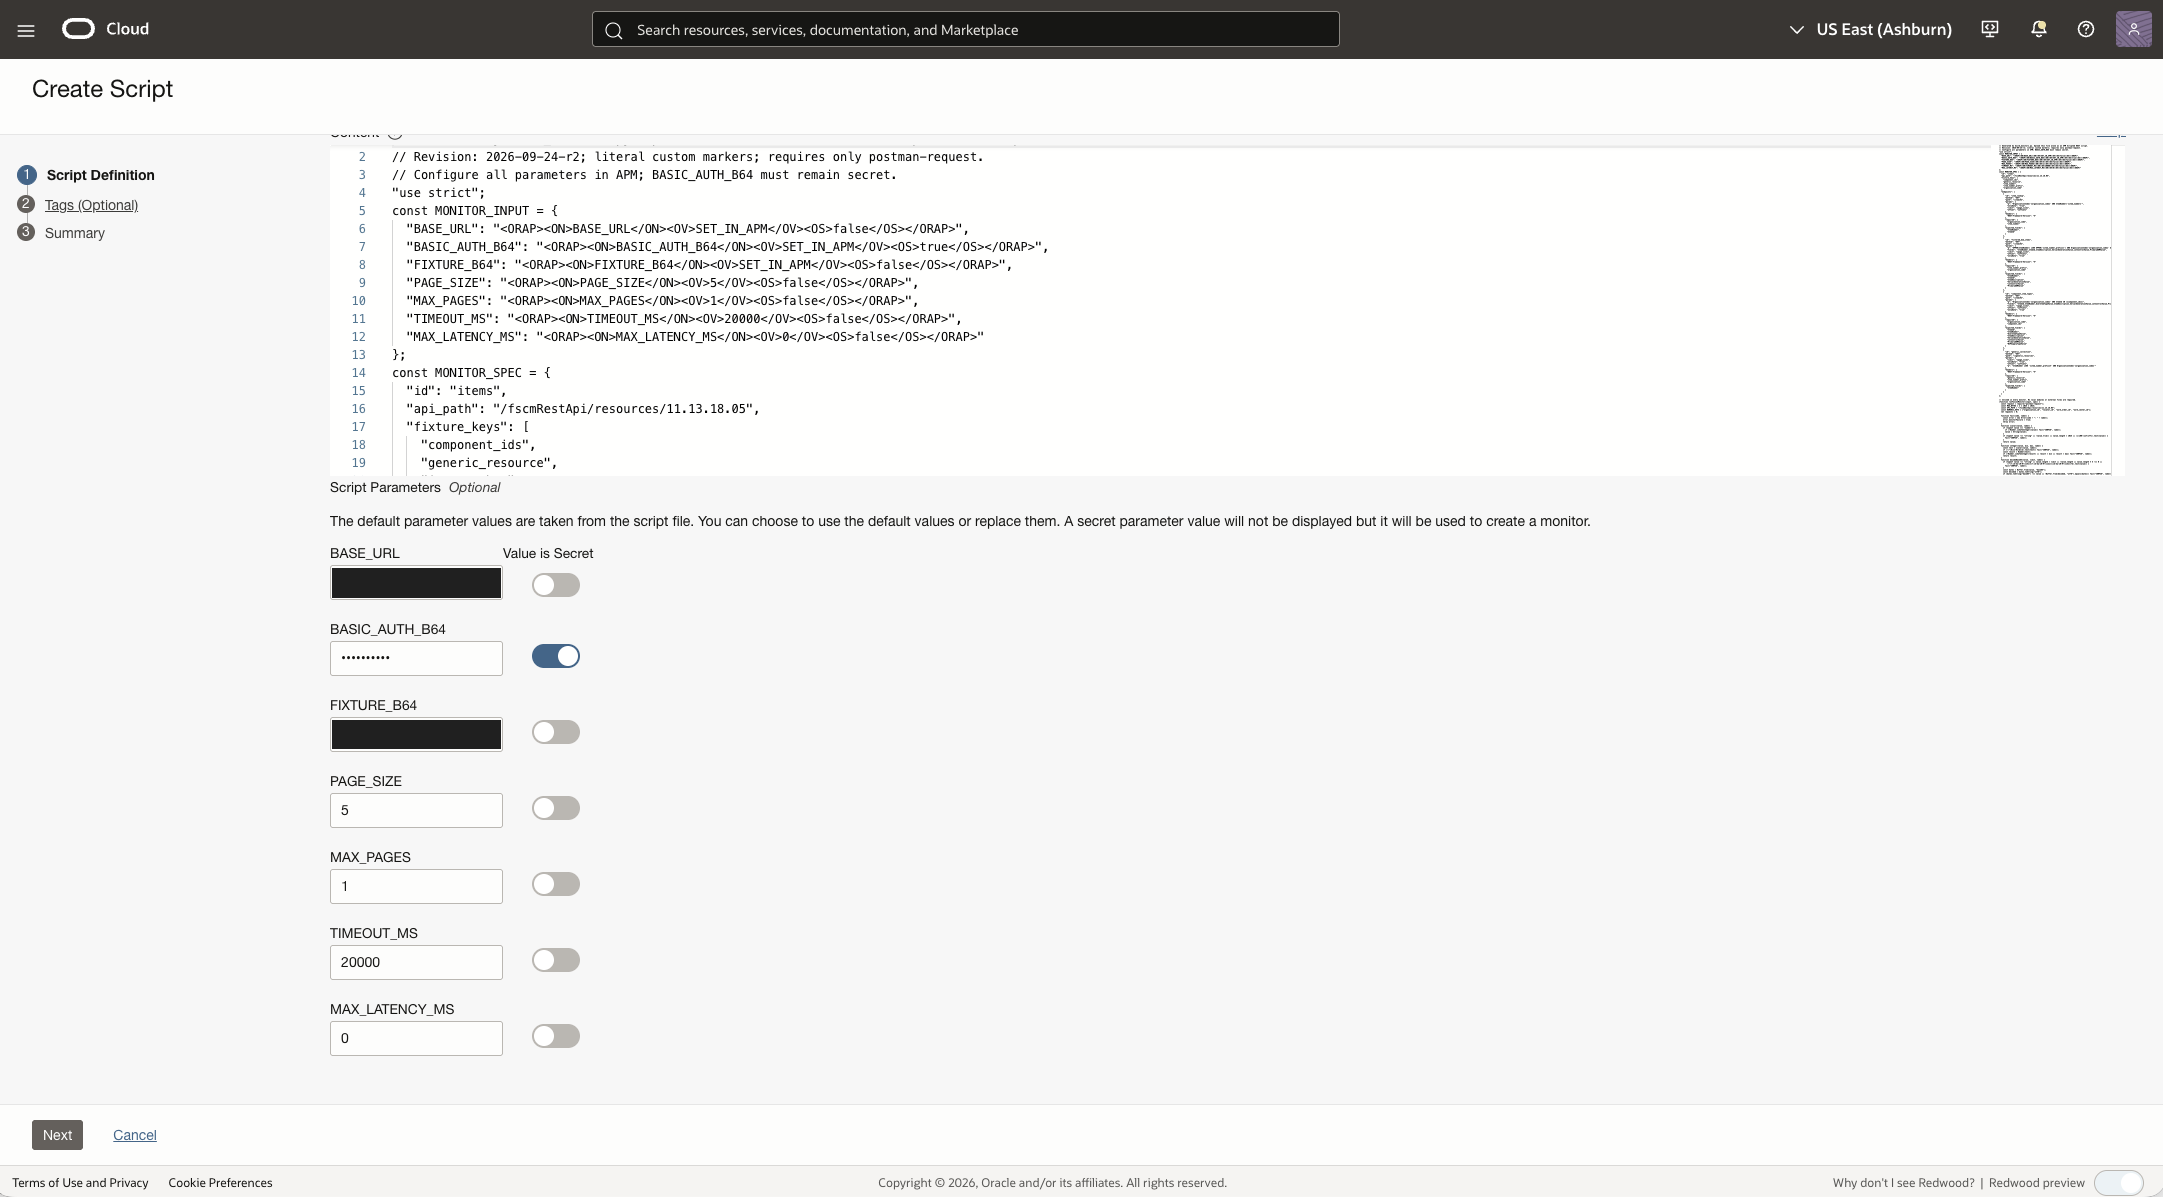
<p>The script’s ORAP placeholders appear as <strong>Script Parameters</strong> below the content. Set <code class="language-plaintext highlighter-rouge">BASE_URL</code> to the Fusion HTTPS origin without a trailing slash. Set <code class="language-plaintext highlighter-rouge">BASIC_AUTH_B64</code> to the Base64 value of <code class="language-plaintext highlighter-rouge">username:password</code> and turn on <strong>Value is secret</strong>. Set <code class="language-plaintext highlighter-rouge">FIXTURE_B64</code> to Base64-encoded JSON containing the selected test identifiers and mark it secret when those identifiers are private. The earlier capture below has the fixture’s secret toggle off; enable it for private identifiers before saving. Base64 is reversible encoding, so neither value is safe to publish. Keep the script’s request-size, page-count, and timeout settings bounded.</p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-script-parameters.png" alt="Create Script parameters with the authentication parameter marked secret and environment-specific values redacted." /></p>

<p><em>Figure 3. Configuring script parameters and secret values.</em></p>

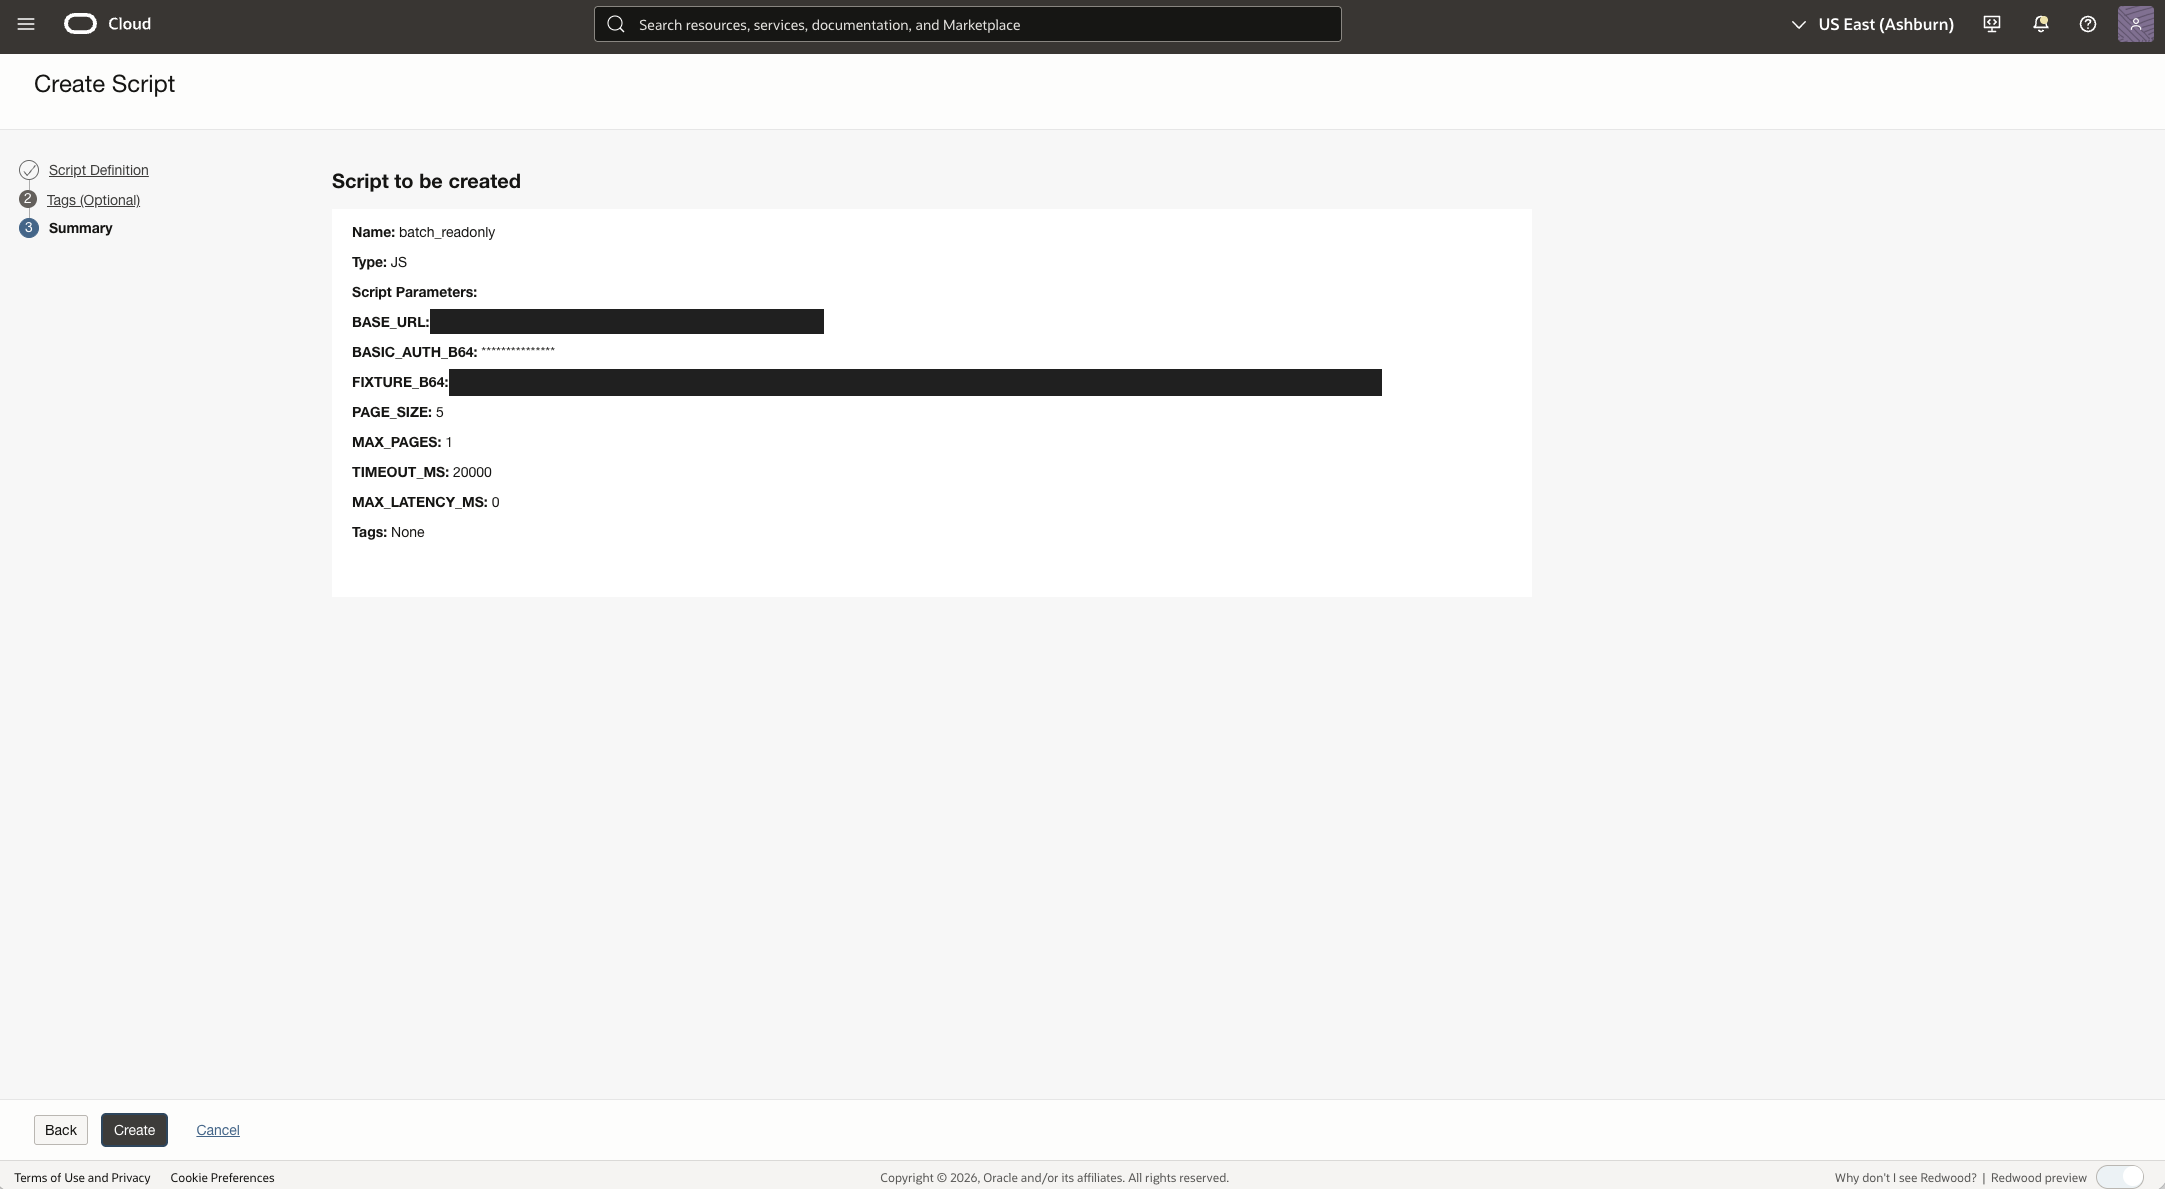
<p>Choose <strong>Next</strong>, add tags if needed, and check the <strong>Summary</strong> page before selecting <strong>Create</strong>. Verify the script name and parameter names; a summary only confirms what will be saved, not that the API request has succeeded. The capture below shows the equivalent summary for the read-only batch script.</p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-script-summary.png" alt="Create Script summary for the read-only batch JavaScript file with environment-specific values redacted." /></p>

<p><em>Figure 4. Reviewing the read-only batch script summary.</em></p>

<h3 id="2-create-and-configure-the-monitor">2. Create and configure the monitor</h3>

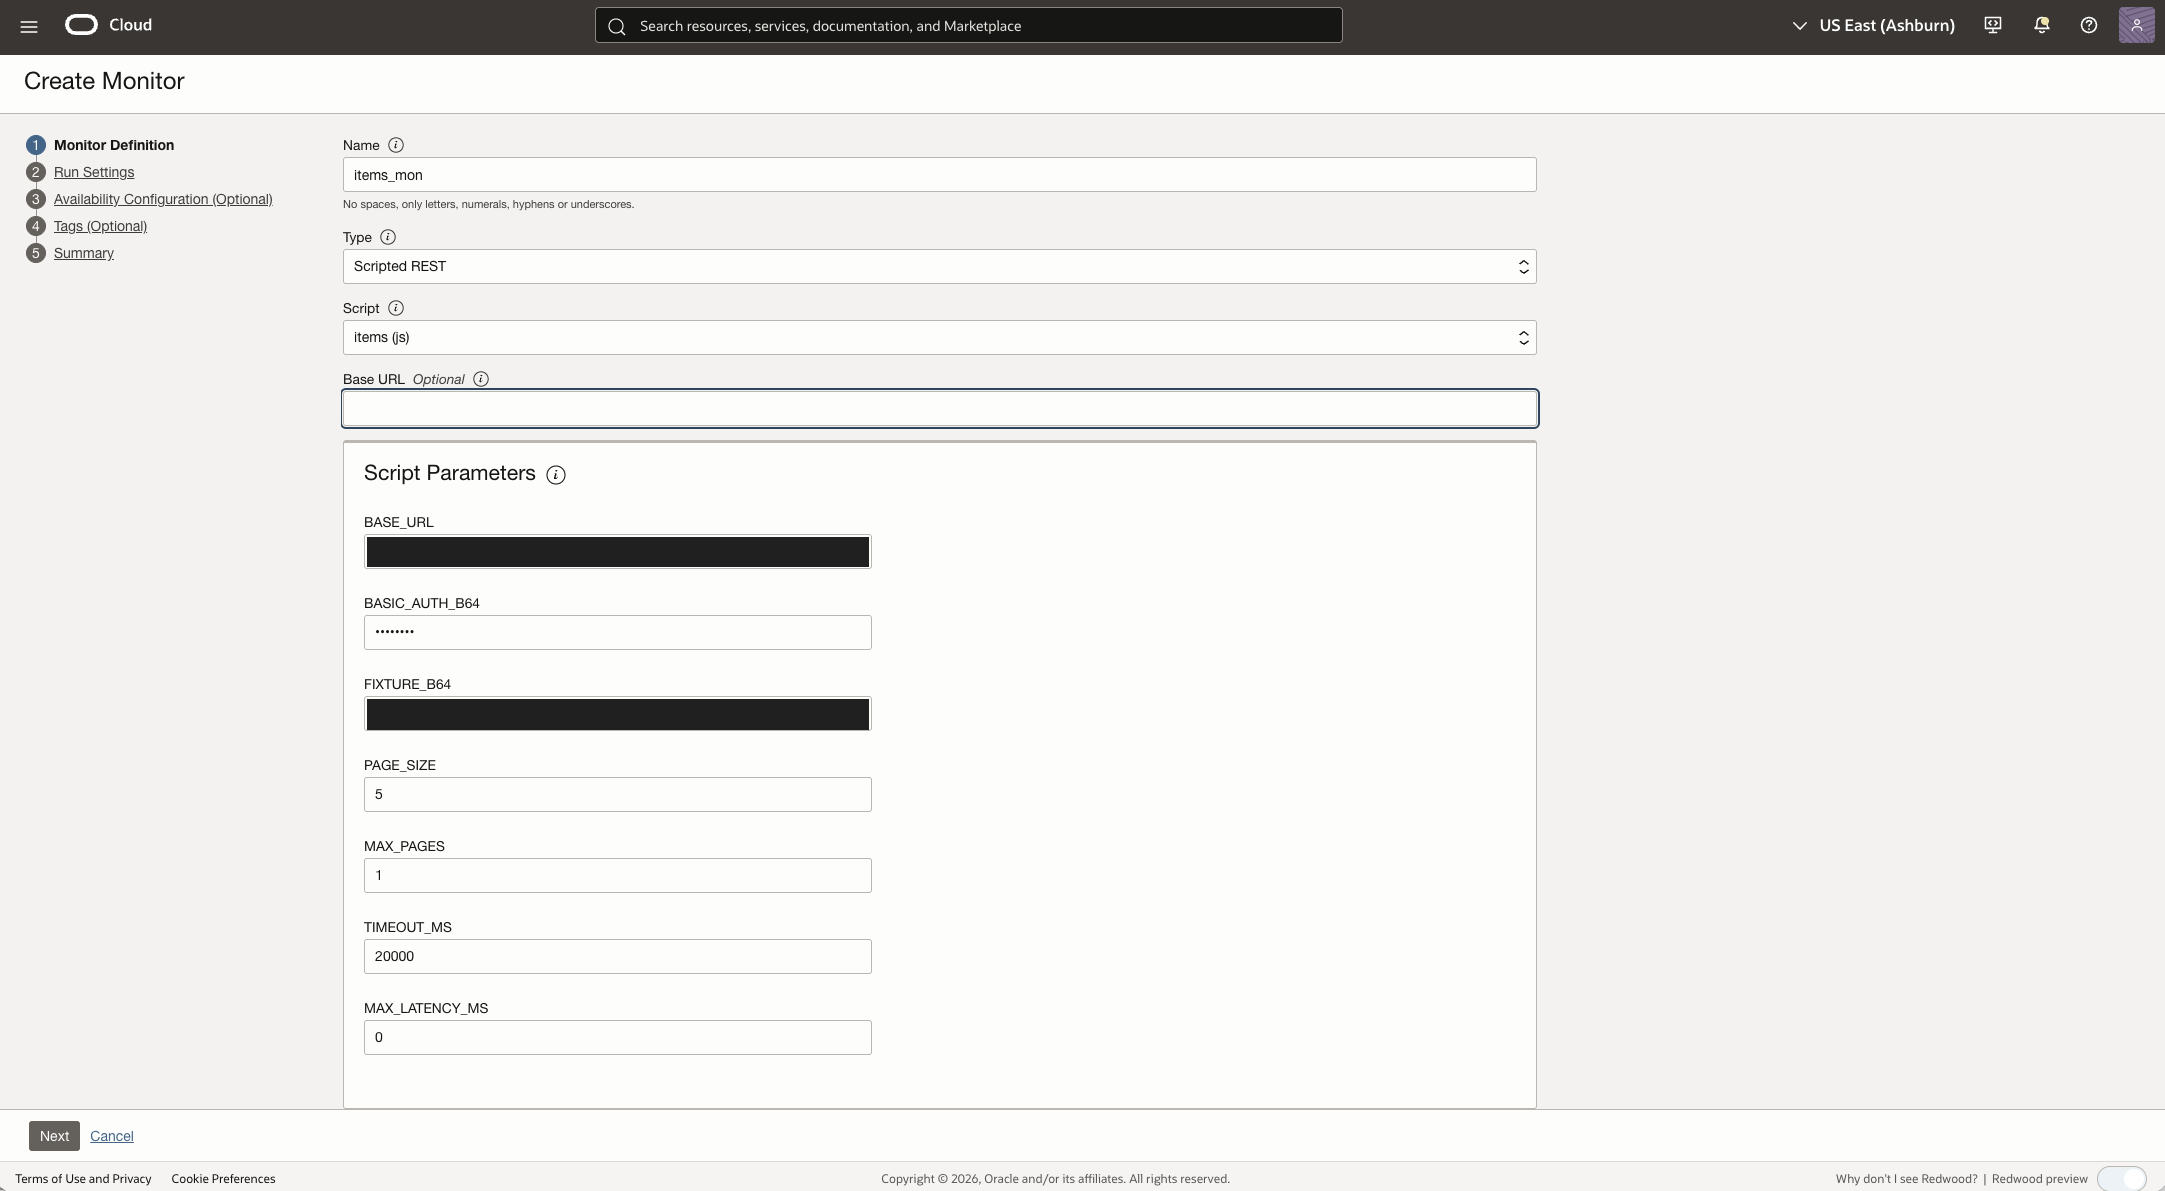
<p>From the saved script’s page, choose <strong>Create Monitor</strong>, or open <strong>Monitors → Create Monitor</strong> in the same APM domain. Enter a distinctive name, select <strong>Scripted REST</strong>, and choose the saved <code class="language-plaintext highlighter-rouge">.js</code> script. The script parameters are available on <strong>Monitor Definition</strong>; verify their values for this environment and keep <code class="language-plaintext highlighter-rouge">BASIC_AUTH_B64</code> secret.</p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-monitor-definition.png" alt="Historical Scripted REST monitor definition showing an empty monitor-level Base URL and separate script parameters. Environment-specific values are redacted." /></p>

<p><em>Figure 5. Historical monitor definition with an empty monitor-level Base URL.</em></p>

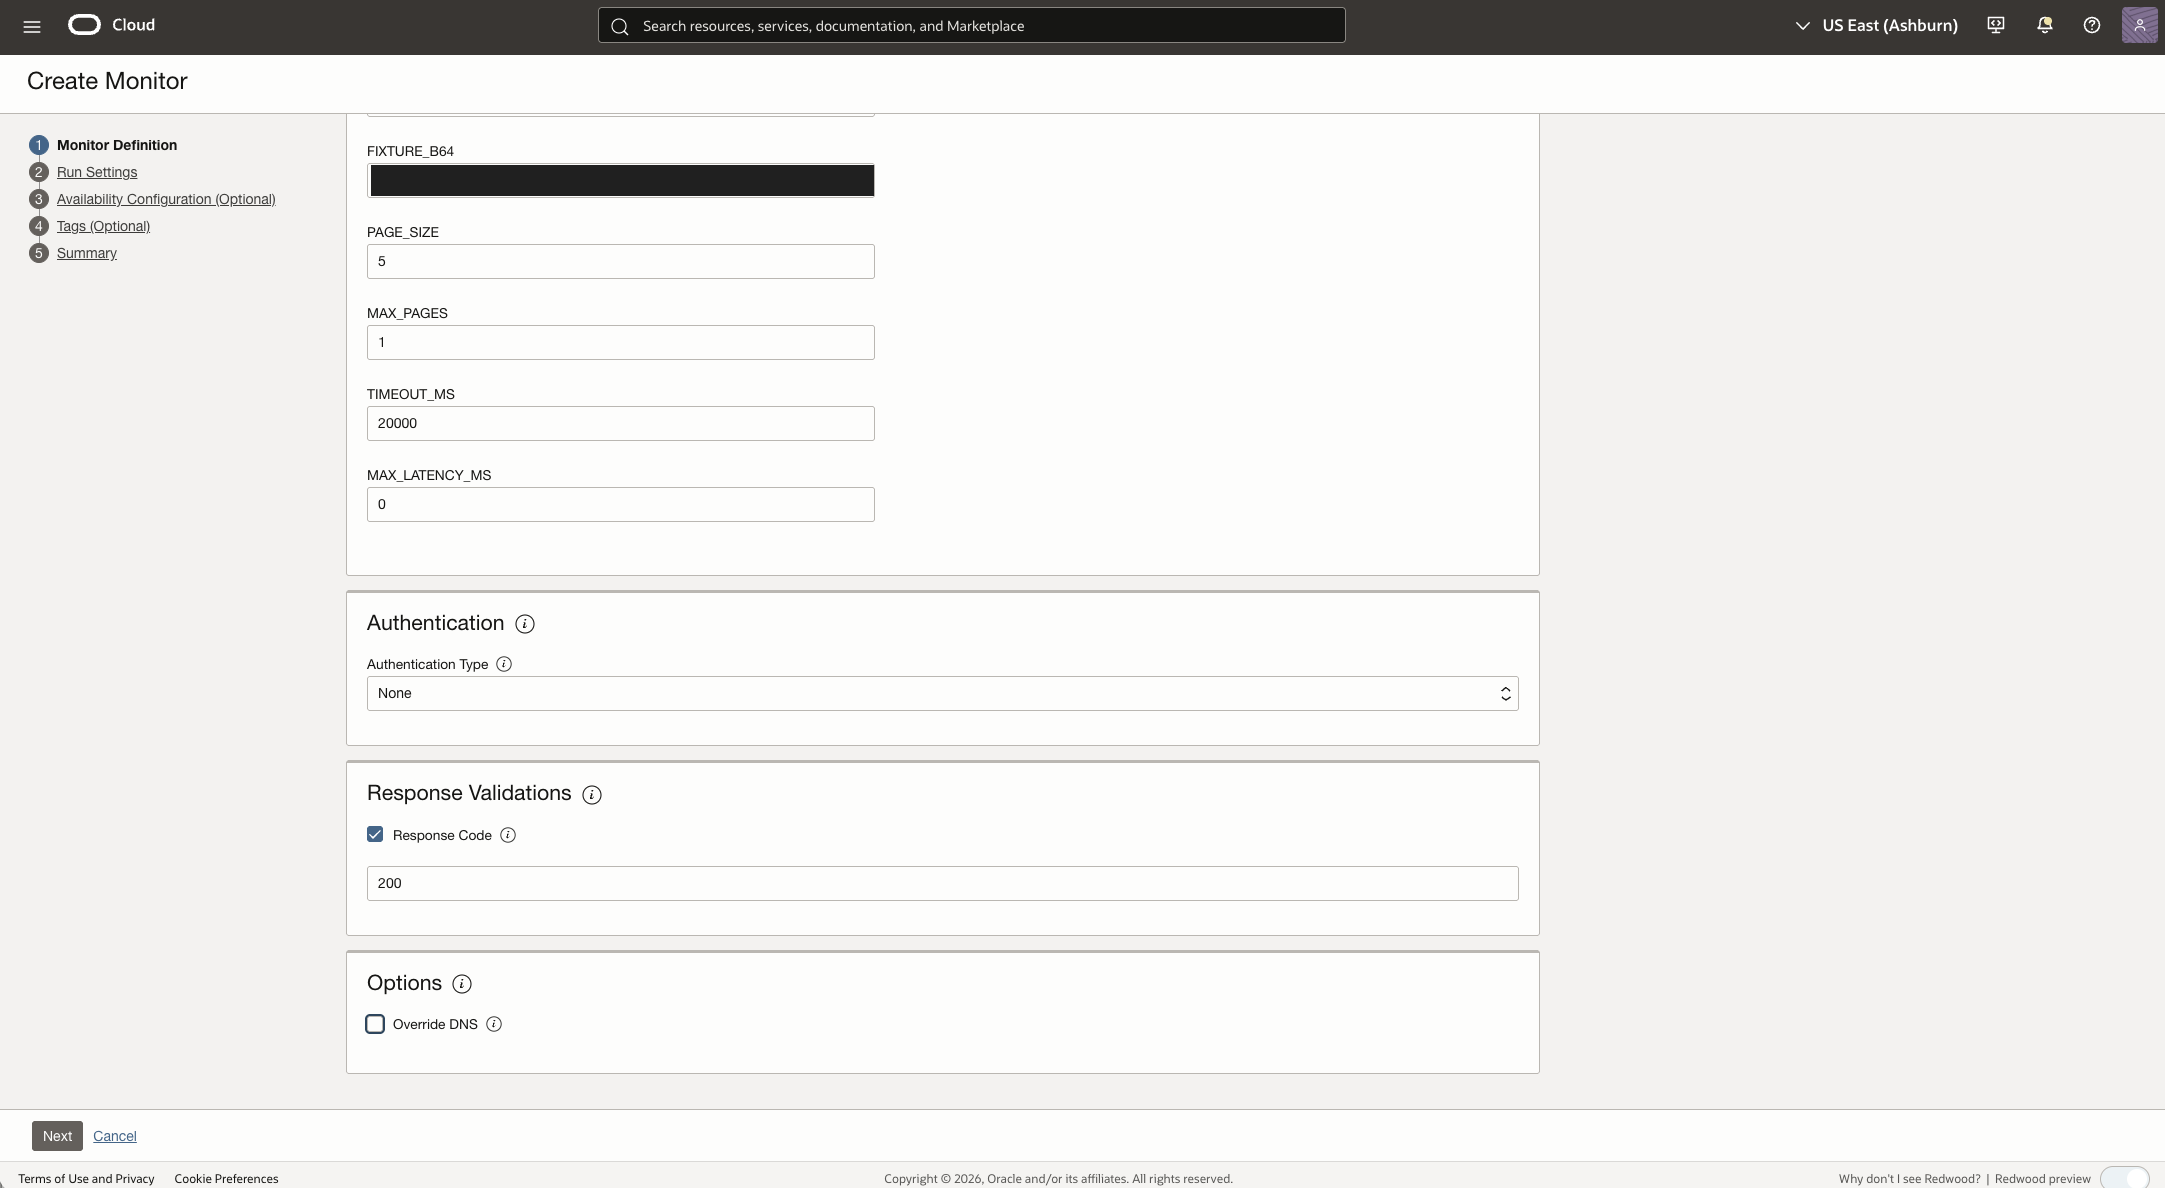
<p>Enter the Fusion HTTPS origin, without a trailing slash, in <strong>both</strong> places: the monitor-level <strong>Base URL</strong> field and the script parameter <code class="language-plaintext highlighter-rouge">BASE_URL</code>. The monitor form in this setup requires its own Base URL even though the script builds complete request URLs from its parameter. Oracle’s documentation labels the monitor-level field optional, so check the behavior of the APM form you use; the earlier empty-field capture above is no longer the configuration to follow here. Scroll down to <strong>Authentication</strong> and leave its type at <strong>None</strong>: this script supplies the Basic Authorization header itself. Under <strong>Response Validations</strong>, select response code <code class="language-plaintext highlighter-rouge">200</code>; the JavaScript also checks the status and the returned data. Leave <strong>Override DNS</strong> off unless the network design specifically requires it. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-monitor.html">Oracle monitor configuration</a></p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-monitor-validation.png" alt="Lower portion of Monitor Definition showing Authentication None, response code 200, and Override DNS unchecked." /></p>

<p><em>Figure 6. Configuring authentication, response validation, and DNS options.</em></p>

<h3 id="3-set-the-execution-locations-and-cadence">3. Set the execution locations and cadence</h3>

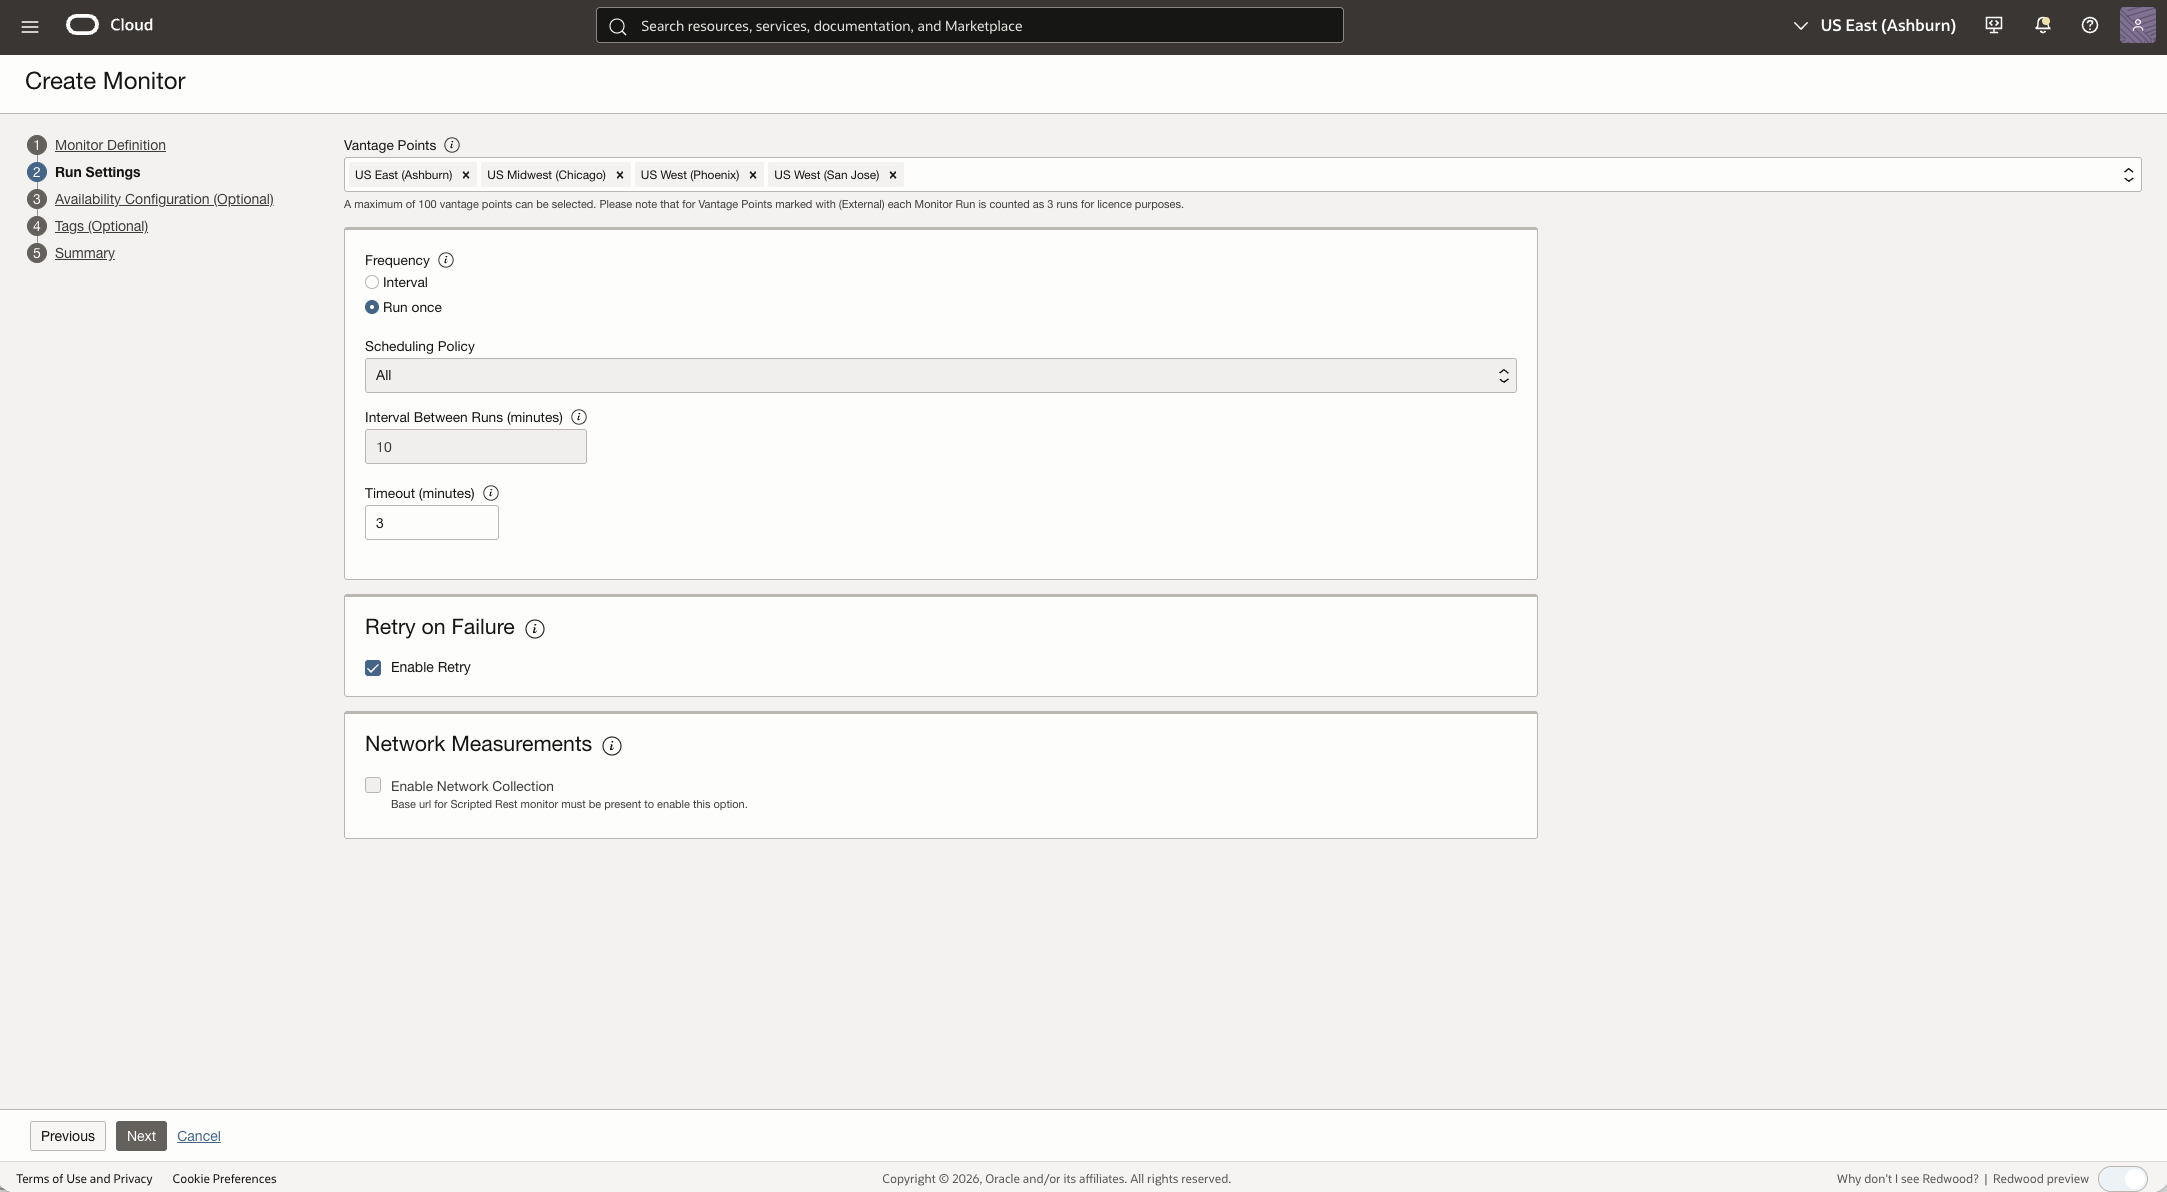
<p>On <strong>Run Settings</strong>, select the vantage points that represent the integration’s access path. For an initial diagnostic, choose one location and <strong>Run once</strong>; once that execution succeeds, expand to the intended locations and select <strong>Interval</strong> for continuous monitoring. Set the monitor timeout long enough for the script to finish; the captured setup used three minutes, while each request in the example has its own 20-second timeout. Disable <strong>Enable Retry</strong> for the first diagnostic so its result is easier to interpret, then decide whether retries fit the operational policy. Figure 7 captures a later choice of four public vantage points, <strong>Run once</strong>, and retry enabled.</p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-run-settings.png" alt="APM run settings showing selected vantage points and Network Collection unchecked." /></p>

<p><em>Figure 7. Selecting vantage points and run settings.</em></p>

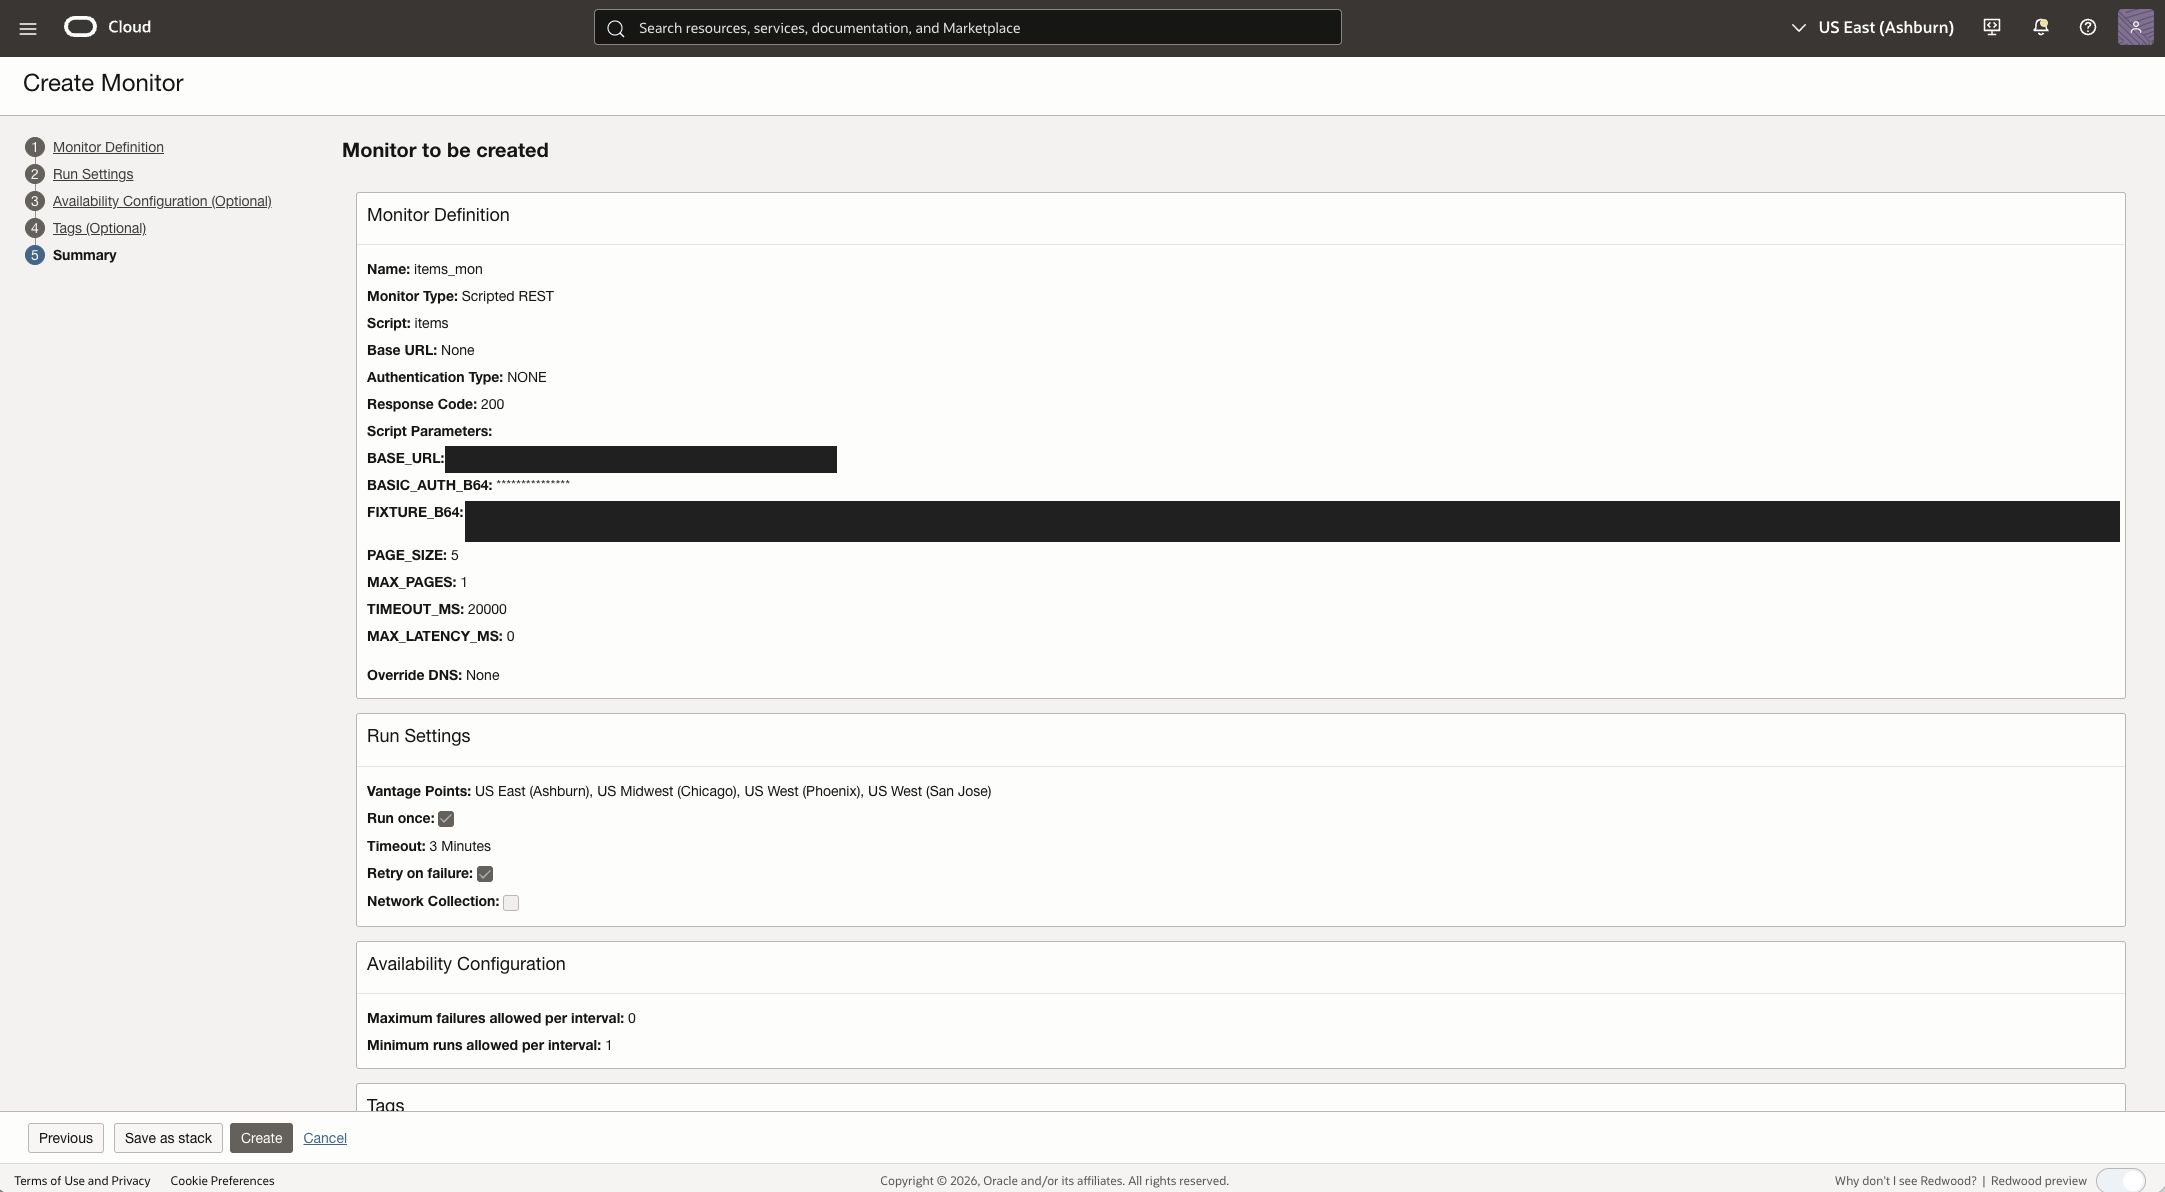
<p>For the current setup, leave <strong>Enable Network Collection</strong> unchecked even though both Base URL fields are populated. The image above shows the same unchecked option in the earlier configuration with an empty monitor-level Base URL. Network Collection is a separate measurement option; leaving it unchecked here does not imply a general incompatibility with Fusion. Oracle documents that the option is shown for Scripted REST when a monitor-level Base URL is specified. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-monitor.html">Run settings and Network Collection</a></p>

<h3 id="4-define-availability-and-review-the-summary">4. Define availability and review the summary</h3>

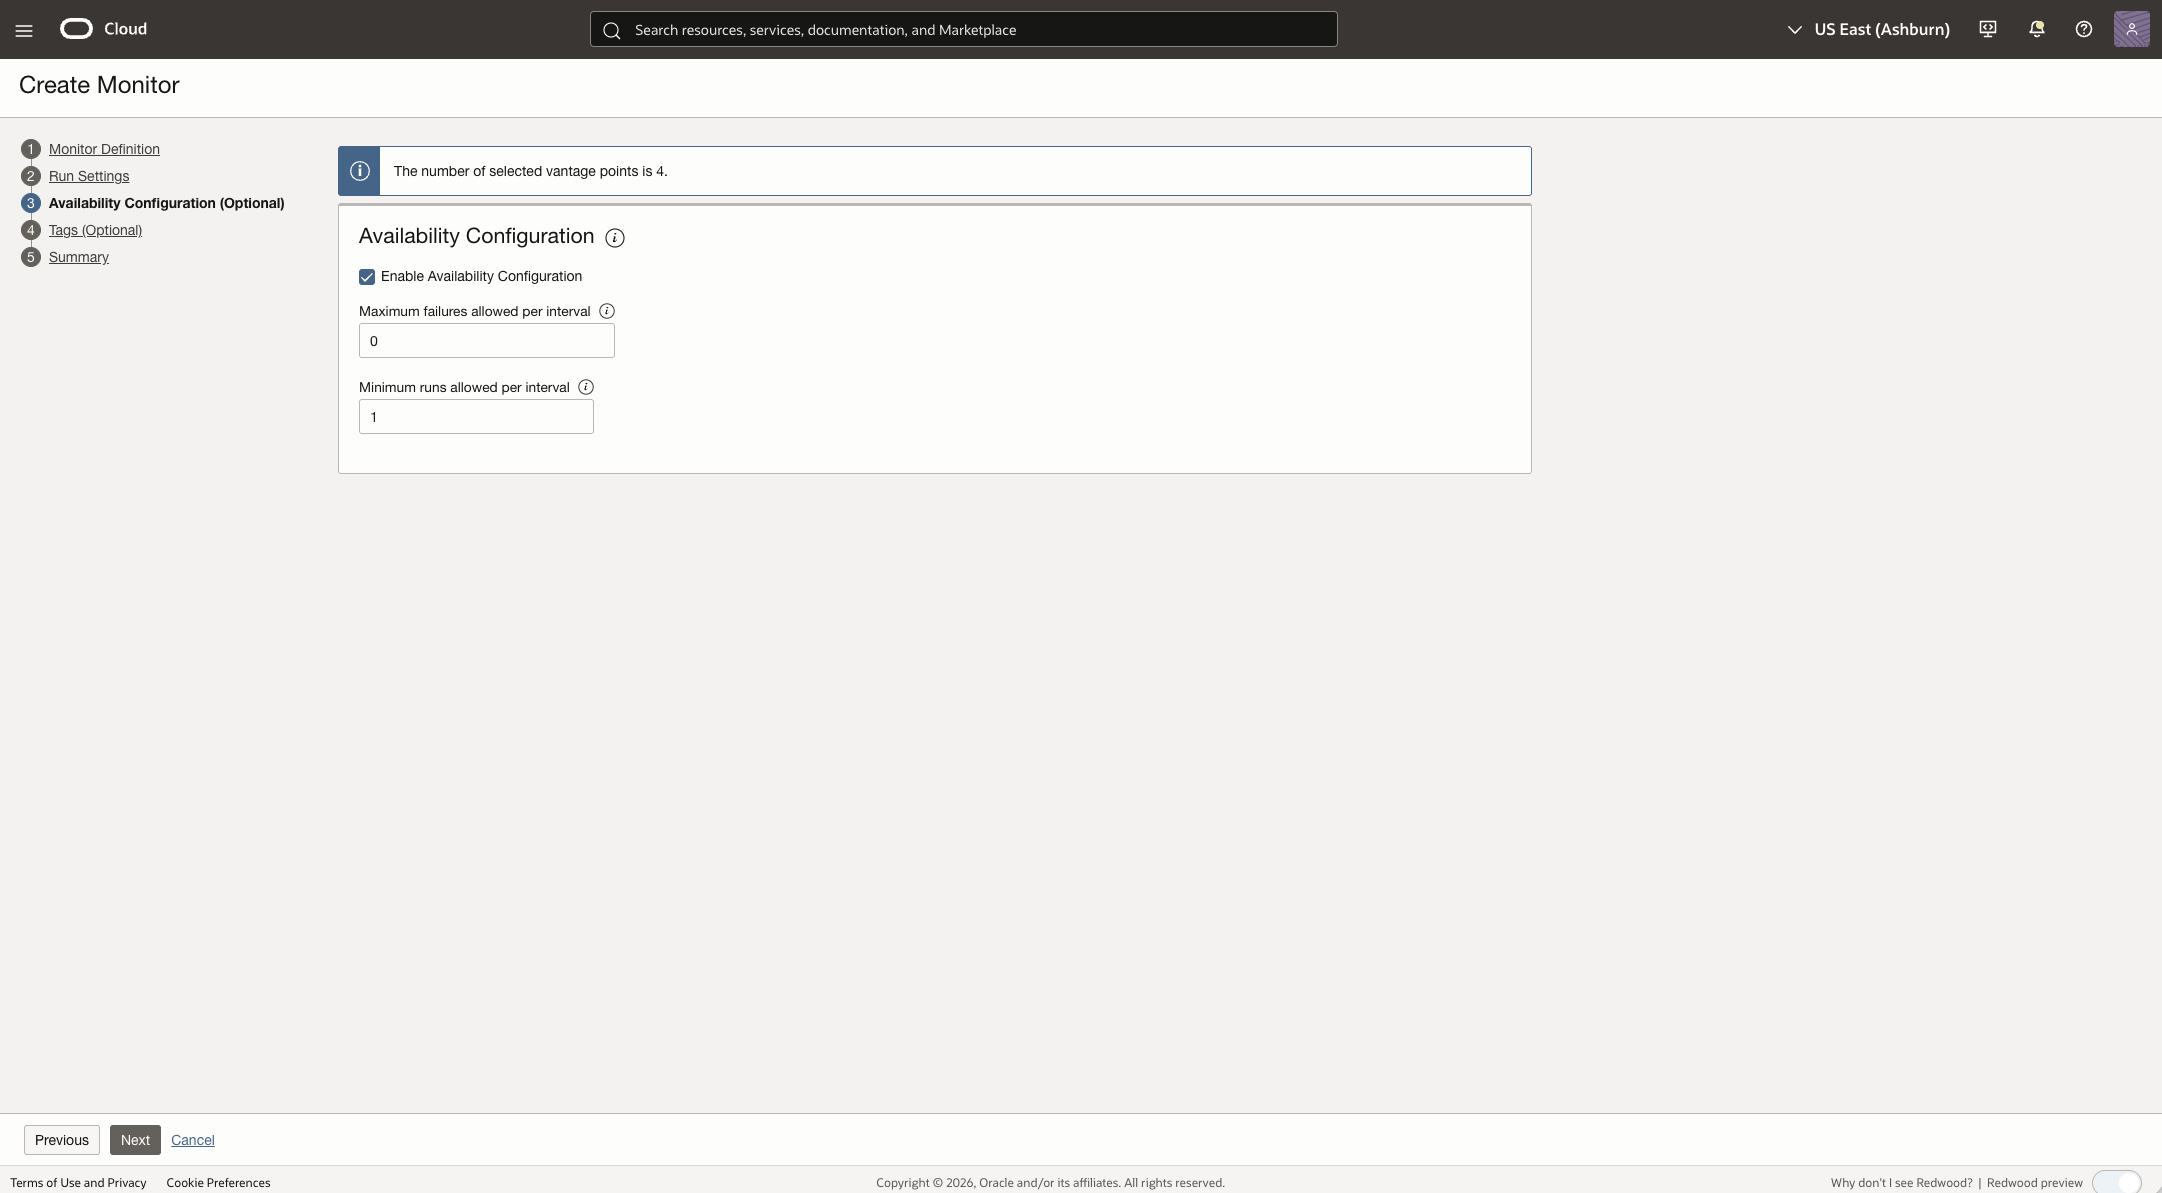
<p>On <strong>Availability Configuration (Optional)</strong>, enable the calculation if you want the dashboard’s availability widget to classify each interval. The captured example allows <strong>0 maximum failures</strong> and requires <strong>1 minimum run</strong> per interval. With those thresholds, any failed run makes an interval with enough runs unavailable; too few runs makes it unknown and excludes it from the availability calculation. Choose thresholds appropriate for the final schedule and number of vantage points. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-monitor.html">Availability configuration</a></p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-availability-configuration.png" alt="Availability Configuration page enabled with zero failures allowed and one minimum run per interval." /></p>

<p><em>Figure 8. Setting availability thresholds for monitor runs.</em></p>

<p>Choose <strong>Next</strong>, add optional tags, and inspect <strong>Summary</strong>. Confirm that the monitor-level Base URL and the script parameter <code class="language-plaintext highlighter-rouge">BASE_URL</code> both show the intended Fusion origin. Also review the script name, authentication type, response validation, vantage points, cadence, retry, Network Collection, and availability thresholds before clicking <strong>Create</strong>. The summary screenshot is a historical configuration review, not proof of a completed run or an example of the new Base URL setting.</p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-monitor-summary.png" alt="Historical Create Monitor summary showing the selected items script and an empty monitor-level Base URL; the current setup should show the Fusion origin in that field." /></p>

<p><em>Figure 9. Reviewing the historical monitor summary before creation.</em></p>

<p>Inspect the newest execution in <strong>History</strong> before choosing a recurring interval. Verify the timestamp, vantage point, assertions, and duration. Then add the other selected capabilities, each with its own fixture, and expand the locations according to the integration’s access requirements.</p>

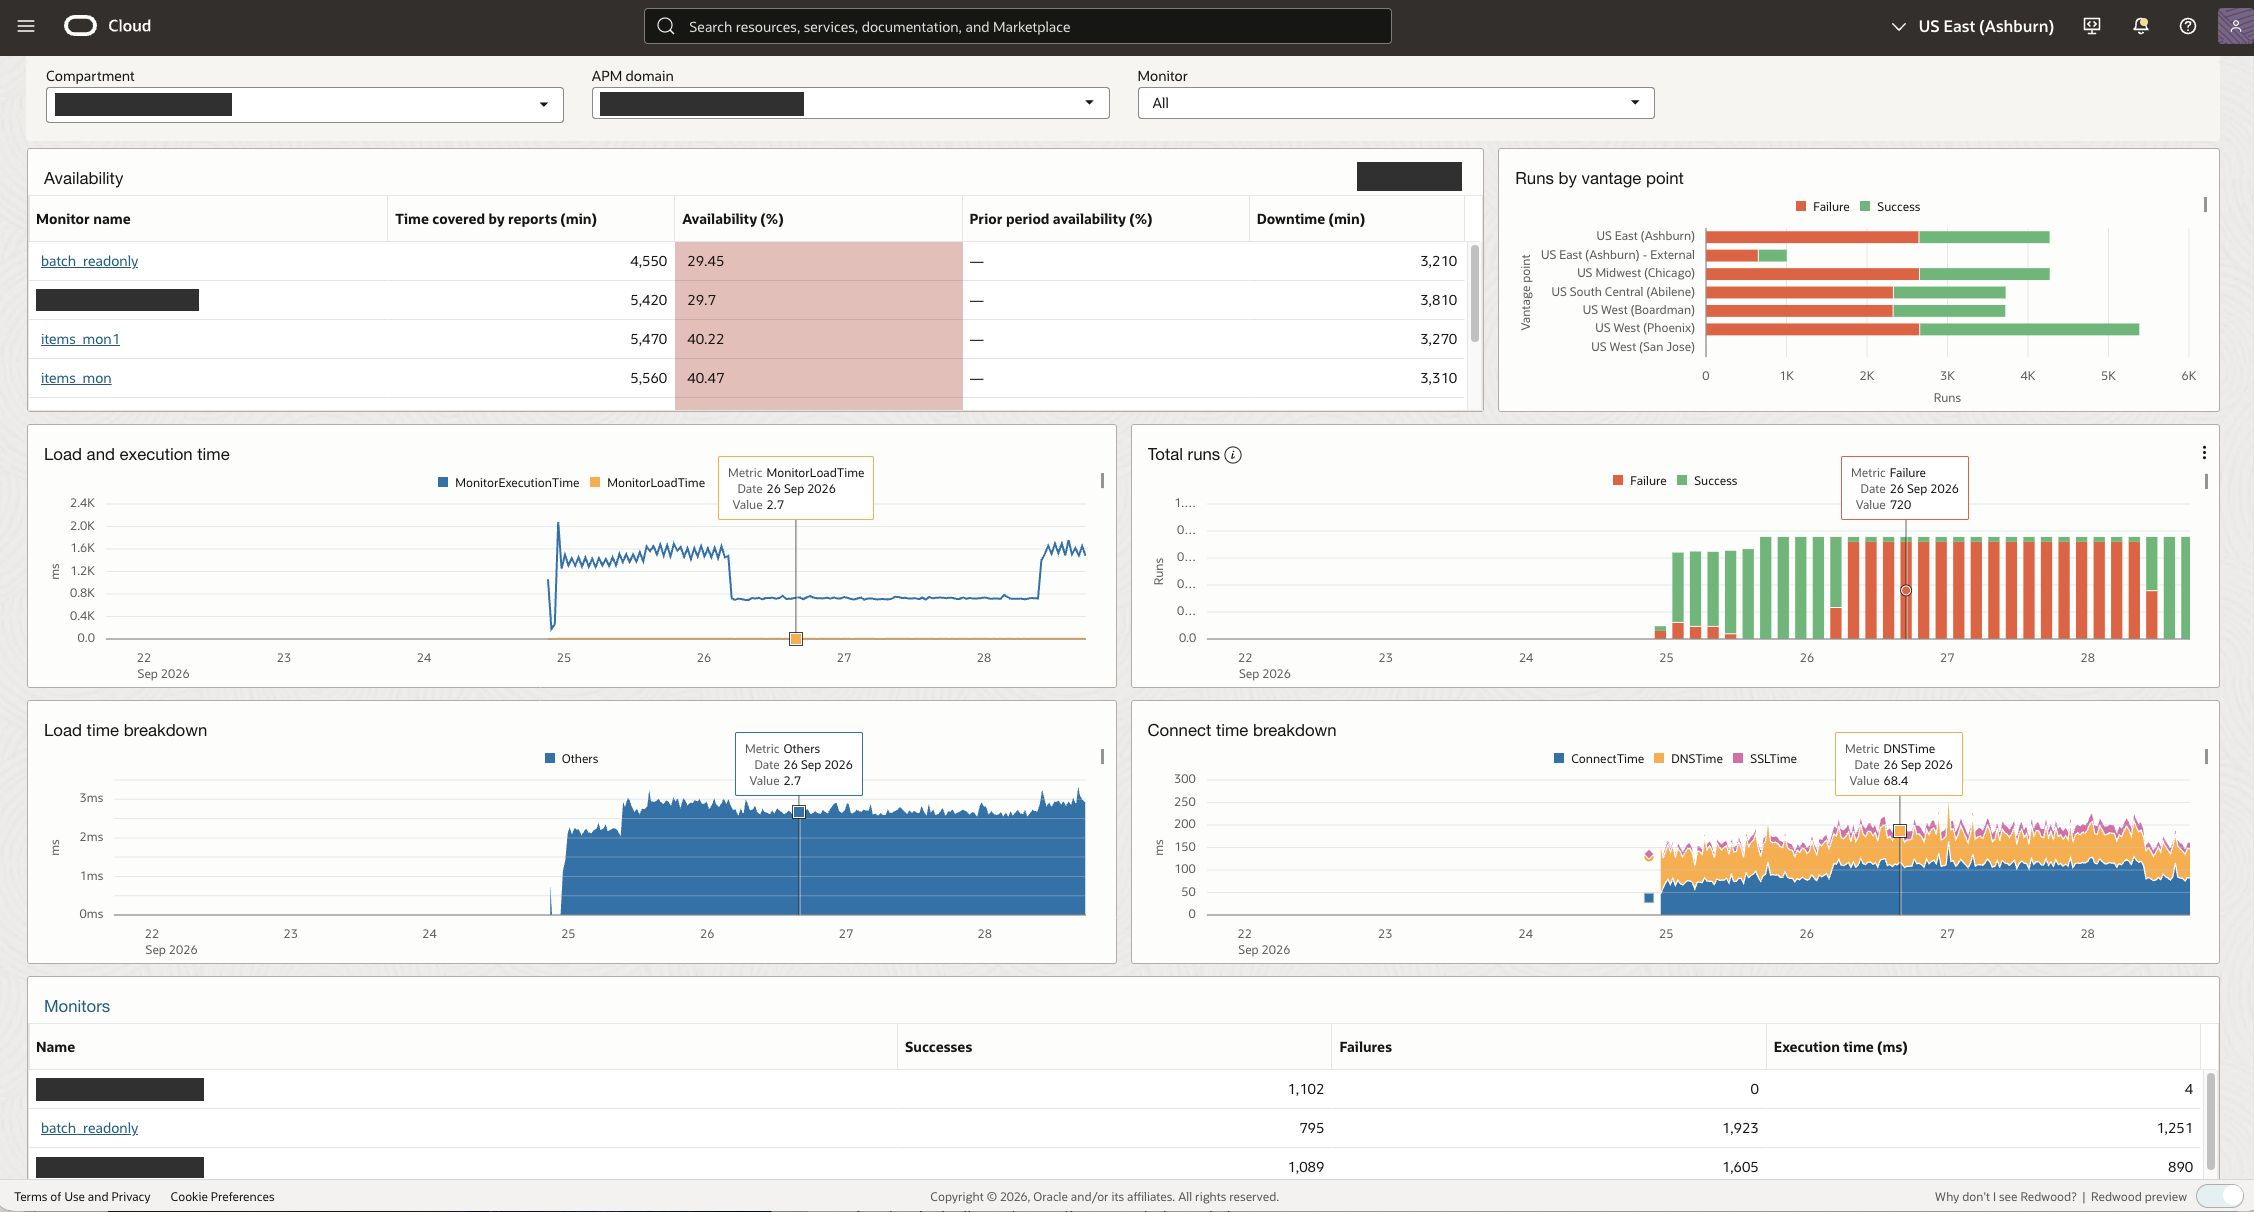
<p>Development evidence included a successful hosted items check and local validation of the other selected GET patterns. The exact read-only batch script passed locally against Fusion. The later dashboard screenshots also show recorded successes and failures for the hosted batch monitor. Those aggregate counters do not identify the executed script revision or establish which response assertions passed; use individual run output to confirm that baseline.</p>

<h2 id="create-monitoring-widgets-using-apm-monitor-kpis">Create monitoring widgets using APM monitor KPIs</h2>

<p>Each Availability Monitoring execution produces signals that can answer three operational questions: <strong>Is the Fusion endpoint available? How long does the scripted check take? Are failures recurring or concentrated at one vantage point?</strong> Build widgets around those questions so the dashboard shows the health of the business API checks, not merely a collection of charts. The supplied test dashboard includes historical series beyond the five examples in this article; its successes and failures are not a production SLA.</p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-dashboard-overview.png" alt="APM dashboard with monitor availability, runs by vantage point, execution time, and successful and failed runs. Environment details and unrelated monitor labels are redacted." /></p>

<p><em>Figure 10. Viewing availability and run results in the APM dashboard.</em></p>

<p>Start with a small KPI set, then choose a widget that makes each signal easy to interpret. The metrics below come from the <code class="language-plaintext highlighter-rouge">oracle_apm_synthetics</code> namespace. They measure synthetic monitor runs and requests, not the volume or end-to-end success of the customer’s integration traffic. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring-metrics.html">APM metric definitions</a></p>

<table>
  <thead>
    <tr>
      <th>Monitoring question</th>
      <th>Metric</th>
      <th>Suggested widget and interpretation</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong>Availability:</strong> Are the selected API checks passing?</td>
      <td><code class="language-plaintext highlighter-rouge">Availability</code></td>
      <td>Show a trend or current value by <code class="language-plaintext highlighter-rouge">MonitorName</code>; <code class="language-plaintext highlighter-rouge">1</code> means a successful run and <code class="language-plaintext highlighter-rouge">0</code> a failed run. Mean × 100 gives the success percentage for the selected runs and period.</td>
    </tr>
    <tr>
      <td><strong>Performance:</strong> Is the complete check getting slower?</td>
      <td><code class="language-plaintext highlighter-rouge">MonitorExecutionTime</code></td>
      <td>Plot a line by monitor and, when useful, vantage point. The metric measures the whole monitor execution in milliseconds.</td>
    </tr>
    <tr>
      <td><strong>Performance detail:</strong> Which scripted step changed?</td>
      <td><code class="language-plaintext highlighter-rouge">CustomMetric</code></td>
      <td>Plot a named <code class="language-plaintext highlighter-rouge">CustomMarker</code>, such as <code class="language-plaintext highlighter-rouge">item_lookup</code> or <code class="language-plaintext highlighter-rouge">batch_readonly</code>, beside overall execution time. A marker may be absent when a run fails before its end marker.</td>
    </tr>
    <tr>
      <td><strong>Reliability:</strong> How often do runs fail?</td>
      <td><code class="language-plaintext highlighter-rouge">Failure</code></td>
      <td>Sum failures per time bucket and compare them with successful runs or the availability trend. <code class="language-plaintext highlighter-rouge">Failure</code> is <code class="language-plaintext highlighter-rouge">1</code> for a failed run, <code class="language-plaintext highlighter-rouge">0</code> otherwise.</td>
    </tr>
    <tr>
      <td><strong>Failure diagnosis:</strong> Did requests return HTTP errors or no response?</td>
      <td><code class="language-plaintext highlighter-rouge">HTTP4xxFailureCount</code>, <code class="language-plaintext highlighter-rouge">HTTP5xxFailureCount</code>, <code class="language-plaintext highlighter-rouge">TotalRequestFailures</code></td>
      <td>Use separate count charts so an HTTP response error is not confused with a request that received no response.</td>
    </tr>
    <tr>
      <td><strong>Synthetic activity:</strong> Were checks actually sent?</td>
      <td><code class="language-plaintext highlighter-rouge">RequestCount</code></td>
      <td>Show the count of requests generated by these monitors; this is not business integration traffic.</td>
    </tr>
  </tbody>
</table>

<p>For count metrics, sum within a time bucket. For execution times, start with a mean and keep the native millisecond unit clear; compare failure counts before treating a sudden shorter run as an improvement. Choose a bucket that fits the monitor’s schedule. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring-metrics.html">APM metric names, units, and dimensions</a></p>

<p><strong>Create the widgets.</strong> A Metric line chart is one way to show execution time or availability over time; use a table or count chart when it communicates outcomes more clearly. The following steps use the APM dashboard editor:</p>

<ol>
  <li>Open <strong>Observability &amp; Management → Application Performance Monitoring → Dashboards</strong>. Create a dashboard or open a custom dashboard and choose <strong>Actions → Edit</strong>. To customize an Oracle-defined dashboard, duplicate it first. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/customize-oracle-defined-dashboard.html">APM dashboard customization</a></li>
  <li>On the <strong>Widgets</strong> tab, choose a visualization for one KPI. For example, search for <strong>Metric line chart</strong> and add it to the canvas for execution time.</li>
  <li>Open <strong>Edit widgets</strong>, select that widget, and use the pencil icons beside <strong>Configured widget inputs</strong>. Set <strong>Namespace</strong> to <code class="language-plaintext highlighter-rouge">oracle_apm_synthetics</code> and <strong>Metric name</strong> to <code class="language-plaintext highlighter-rouge">MonitorExecutionTime</code>; verify that the data compartment contains the intended APM domain.</li>
  <li>Label it <strong>Fusion monitor execution time</strong>, select a time range, and choose <strong>Save changes</strong>. Add separate widgets for availability and failure counts using the metrics in the table. Confirm that each series represents the intended monitor and location. <a href="https://docs.oracle.com/en-us/iaas/management-dashboard/doc/create-custom-dashboard.html">Widget input configuration</a></li>
</ol>

<p>An APM domain filter elsewhere on a dashboard does not automatically scope every generic metric widget. Check its input links. When you need explicit domain filtering and separate vantage-point series that the widget’s exposed inputs do not provide, use <strong>Widgets → + → Create query-based widget…</strong>, select <strong>Monitoring</strong> as the data source and <code class="language-plaintext highlighter-rouge">oracle_apm_synthetics</code> as the namespace, then enter a query such as:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>MonitorExecutionTime[10m]{ResourceId="&lt;APM_DOMAIN_OCID&gt;",MonitorName="fusion_items"}.groupBy(MonitorName,VantagePoint).mean()
</code></pre></div></div>

<p>Replace the placeholders with your domain and monitor. This illustrative query uses a ten-minute aggregation interval and a mean for each monitor/location pair; the dashboard time range is a separate choice. Click <strong>Run</strong>, select a <strong>Line chart</strong> visualization, save the widget, and save the dashboard. <a href="https://docs.oracle.com/en-us/iaas/management-dashboard/doc/create-query-based-widget-using-metrics.html">Query-based metric widgets</a>, <a href="https://docs.oracle.com/en-us/iaas/Content/Monitoring/Reference/mql.htm">Monitoring query syntax</a></p>

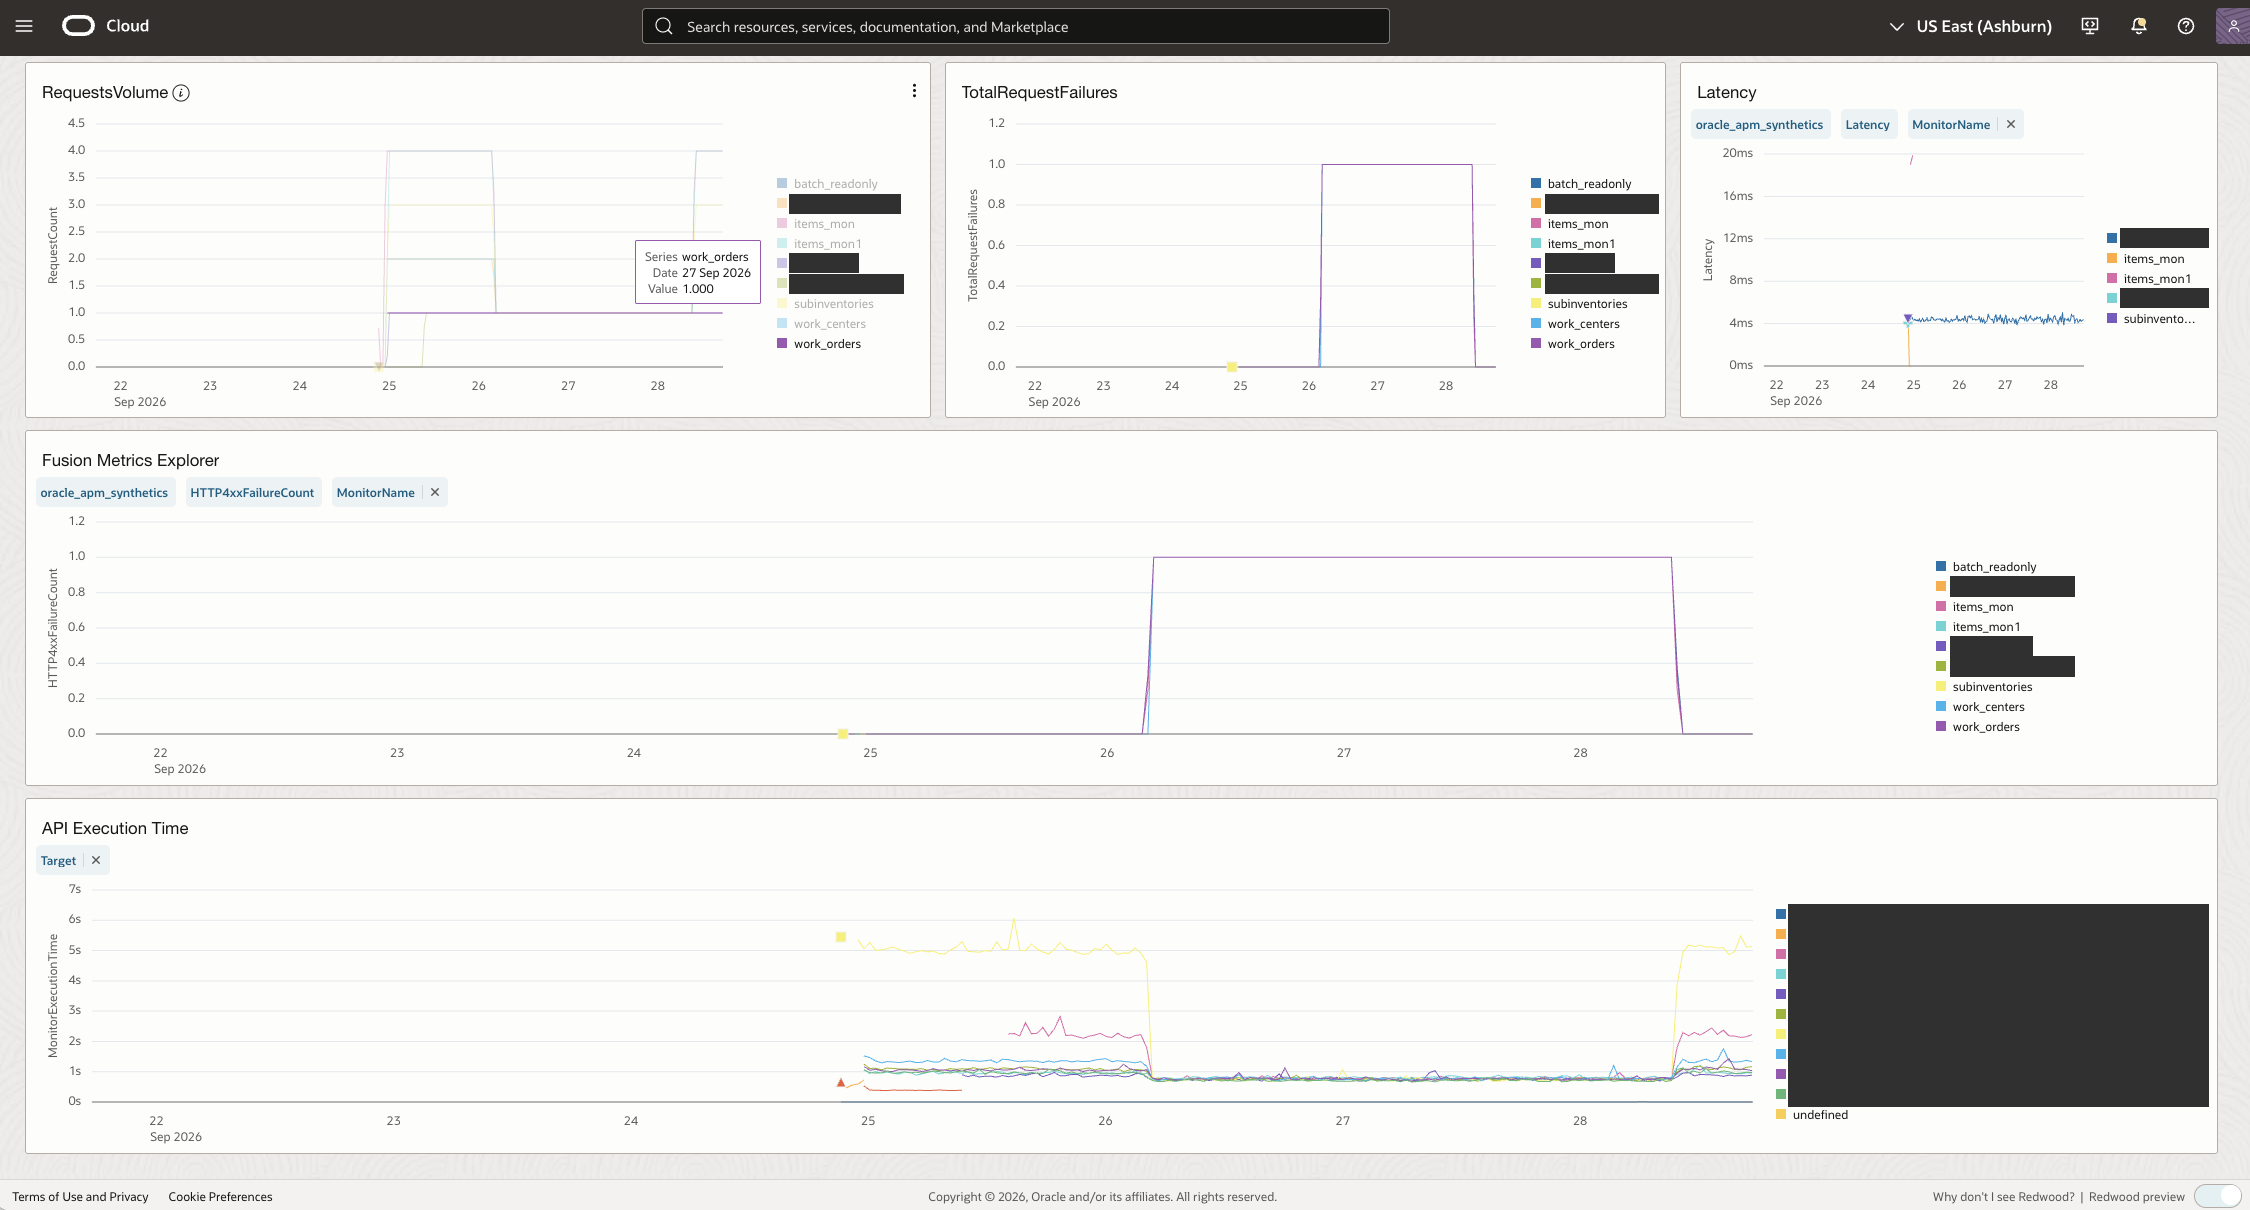
<p>Use <code class="language-plaintext highlighter-rouge">MonitorName</code> for a capability overview and <code class="language-plaintext highlighter-rouge">VantagePoint</code> to compare locations. <code class="language-plaintext highlighter-rouge">ResourceId</code> identifies the APM domain; <code class="language-plaintext highlighter-rouge">MonitorId</code> identifies an individual monitor. Prefer monitor names in public chart legends because <code class="language-plaintext highlighter-rouge">Target</code> can expose pod URLs. In Figure 11, <code class="language-plaintext highlighter-rouge">MonitorExecutionTime</code> measures the complete monitor run; the separate <code class="language-plaintext highlighter-rouge">Latency</code> metric measures network packet round-trip time, not the duration of a Fusion API operation. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring-metrics.html">APM metric dimensions</a></p>

<p><img src="/images/posts/2026-10-01-fusion-business-api-monitoring/blog-post-fusion-api-apm-dashboard-metric-charts.png" alt="Custom dashboard charts showing synthetic request counts, request failures, HTTP errors, and monitor execution time. Target URLs and unrelated monitor labels are redacted." /></p>

<p><em>Figure 11. Charting synthetic requests, failures, and monitor execution time.</em></p>

<p>Use <code class="language-plaintext highlighter-rouge">RequestCount</code> to understand synthetic request activity, not the customer’s integration traffic volume. A shorter execution time can also accompany a request that fails early, so compare timings with success and failure signals. Gaps are missing observations, not evidence of zero latency or perfect availability. Select the same monitor and time window in <strong>History</strong> to investigate a change. <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring-metrics.html">APM synthetic metric definitions</a></p>

<h2 id="conclusion-make-fusion-api-health-visible">Conclusion: make Fusion API health visible</h2>

<p>This customer-inspired pattern turns an integration requirement into a repeatable check at the Fusion SaaS API boundary. A Scripted REST monitor asks a specific business question—can this account retrieve the expected item, inventory reference, work center, or work order?—from a chosen vantage point. A read-only batch adds coverage of POST transport without changing business records. The resulting availability, execution-time, and failure signals remain useful even when customer integration traffic is quiet.</p>

<p>The broader value for Fusion customers is a shared view of <strong>which capability is affected, when it changed, and from where the failure was observed</strong>. A dashboard can reveal a trend; the individual monitor run provides the request and assertion context needed to investigate it. As a Performance-pillar signal, this outside-in view complements <a href="https://www.ateam-oracle.com/real-user-monitoring-for-oracle-fusion-saas-cloud-apps-using-oci-apm-browser-agent">real user experience monitoring</a>, <a href="https://www.ateam-oracle.com/fusion-apps-observability-by-collecting-ess-logs-using-oci-logging-analytics-rest-api-ingestion">ESS process logs</a>, integration logs, and security/audit analysis. A passing synthetic read does not prove that every business transaction or customer integration succeeded.</p>

<p>The five examples are a starting template, not a prescribed customer workload. Start with a few critical endpoints and stable, owned test records. Assign an owner to each fixture and monitor, validate the script from the intended vantage points, then schedule and review the checks as the integration evolves. That makes API availability an operational signal tied to business capabilities rather than an isolated pod status.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://www.oracle.com/manageability/application-performance-monitoring/">Oracle APM overview: public locations in OCI and external data centers</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/synthetic-monitoring.html">Set Up Availability Monitoring: public and private vantage-point options</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/use-dedicated-vantage-points.html">Use Dedicated Vantage Points</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/use-onpremise-vantage-points.html">Use On-premise Vantage Points</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/download-synthetic-worker.html">Download a Worker: monitor types supported by each on-premise worker</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring-metrics.html">APM Availability Monitoring metrics and dimensions</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/management-dashboard/doc/create-query-based-widget-using-metrics.html">Create a query-based widget using metrics</a></li>
</ul>

<p>Related Fusion observability posts by Royce Fu and coauthors:</p>

<ul>
  <li><a href="https://www.ateam-oracle.com/real-user-monitoring-for-oracle-fusion-saas-cloud-apps-using-oci-apm-browser-agent">Real User Monitoring for Oracle Fusion SaaS Cloud Apps using OCI APM Browser Agent</a> — browser-side user experience and performance.</li>
  <li><a href="https://www.ateam-oracle.com/fusion-apps-observability-by-collecting-ess-logs-using-oci-logging-analytics-rest-api-ingestion">Fusion Apps Observability by Collecting Enterprise Scheduler ESS Logs Using OCI Logging Analytics REST API Ingestion</a> — scheduled-process logs and operational visibility.</li>
  <li><a href="https://www.ateam-oracle.com/gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai-part-3">Gaining Insights from Fusion ESS, Audit and Security Dashboards with AI Augmentation Using LoganAI – Part 3</a> — ESS, audit, and security analysis.</li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="Observability and Monitoring" /><category term="Oracle Fusion SaaS Cloud Apps" /><category term="Oracle Cloud Infrastructure" /><category term="Performance Monitoring" /><category term="Application Performance Monitoring" /><summary type="html"><![CDATA[Beyond the Fusion Metrics: Monitoring Oracle Fusion Business APIs]]></summary></entry><entry><title type="html">OCI Log Analytics for Oracle Database@AWS Fleet Log Management</title><link href="https://royce-fu.com/blog/oci-log-analytics-oracle-database-at-aws-exadbd-log-management/" rel="alternate" type="text/html" title="OCI Log Analytics for Oracle Database@AWS Fleet Log Management" /><published>2026-09-11T00:00:00+00:00</published><updated>2026-09-18T14:47:30+00:00</updated><id>https://royce-fu.com/blog/oci-log-analytics-oracle-database-at-aws-exadbd-log-management</id><content type="html" xml:base="https://royce-fu.com/blog/oci-log-analytics-oracle-database-at-aws-exadbd-log-management/"><![CDATA[<p>Oracle Exadata Database Service delivers proven Oracle Database capabilities on purpose-built, optimized Oracle Exadata infrastructure in the public cloud and on Cloud@Customer. Built-in cloud automation, elastic resource scaling, security, and fast performance for all Oracle Database workloads help you simplify management and reduce costs. It is a crucial component for enterprises seeking to optimize their database performance and efficiency. <a href="https://www.oracle.com/engineered-systems/exadata/database-service/">Exadata Database Service</a></p>

<p>Given the complexity of managing an Exadata system, observability and monitoring are essential to achieving operational readiness. Comprehensive observability enables administrators to gain deep insights into system performance, detect anomalies, and address potential issues before they escalate into significant problems. To achieve comprehensive observability and management of Exadata systems, we recommend utilizing OCI Observability and Management (O&amp;M) services such as Management Agent Cloud Service, Database Management Service, Ops Insights, and Logging Analytics. These services enable the collection and ingestion of Exadata system metrics and log data across various environments, including OCI, Cloud@Customer, and on-premises deployments.</p>

<p>This article focuses on OCI Log Analytics for Oracle Database@AWS Exadata Database Service on Dedicated Infrastructure (ExaDB-D). The same ZIP-based Management Agent and log-collection model also applies to <a href="https://docs.oracle.com/en-us/iaas/exadata/doc/ecc-exadata-cloud-at-customer-overview.html">Exadata Database Service on Cloud@Customer</a> (ExaC@C). The walkthrough covers Management Agent installation, database and Grid Infrastructure (GI) log access, entity and source associations, Log Explorer verification, dashboards, and investigation queries. It builds on <a href="https://www.ateam-oracle.com/maximize-visibillity-collecting-and-analyzing-logs-for-multiple-oracle-databases-using-oci-logging-analytics">Maximizing Visibility: Collecting and Analyzing Logs from Oracle Databases using OCI Logging Analytics</a>.</p>

<h2 id="oracles-multicloud-database-monitoring-strategy">Oracle’s multicloud database monitoring strategy</h2>

<p>Oracle’s multicloud database monitoring strategy combines three complementary OCI Observability and Management services. <strong>Database Management</strong> provides fleet monitoring, database and infrastructure metrics, performance management, and administration. <strong>Ops Insights</strong> adds capacity planning, SQL insights, machine-learning-driven diagnostics, and fleet-level trends. <strong>Log Analytics</strong> centralizes logs from cloud and on-premises environments and applies Oracle-aware parsing, interactive analytics, dashboards, and AI-assisted investigation. Together, these services let operations teams move from a fleet symptom to database performance, capacity, and log evidence without treating any single signal as the complete answer. <a href="https://docs.oracle.com/en-us/iaas/Content/database-at-aws-exadata-awsmn/awsmn-monitor-oci.html">OCI monitoring for Oracle Database@AWS</a>, <a href="https://www.oracle.com/manageability/database-management/">Database Management</a>, <a href="https://www.oracle.com/manageability/operations-insights/">Ops Insights</a></p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oracle-multicloud-database-monitoring-strategy.png" alt="Oracle database management strategy across public cloud, hybrid cloud, and multicloud environments." class="align-center" /></p>

<p><em>Figure 1. Oracle’s database management strategy combines Database Management, Ops Insights, and Log Analytics across public-cloud, hybrid-cloud, and multicloud database deployments.</em></p>

<h2 id="why-database-and-gi-logs-become-difficult-to-use-across-a-fleet">Why database and GI logs become difficult to use across a fleet</h2>

<p>Oracle Database@AWS publishes useful performance and infrastructure metrics to Amazon CloudWatch under the <code class="language-plaintext highlighter-rouge">AWS/ODB</code> namespace. The service view can expose CPU utilization, load, memory, ASM disk-group utilization, node status, allocated OCPUs, file-system utilization, active sessions, and I/O performance, depending on the resource and enabled monitoring. These metrics help operators recognize resource pressure and availability changes across Exadata VM clusters. <a href="https://docs.oracle.com/en-us/iaas/Content/database-at-aws-exadata-awsmn/awsmn-monitor-cloudwatch.html">Oracle Database@AWS CloudWatch monitoring</a>, <a href="https://docs.aws.amazon.com/odb/latest/UserGuide/monitoring-overview.html">AWS monitoring overview</a></p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oracle-database-at-aws-cloudwatch-monitoring-redacted.png" alt="Oracle Database@AWS CloudWatch metrics for an Exadata VM cluster." class="align-center" /></p>

<p><em>Figure 2. CloudWatch provides useful VM-cluster and database metrics. The VM-cluster name and database-node OCIDs were redacted for publication.</em></p>

<p>The CloudWatch Logs view captured for this walkthrough primarily exposes the <code class="language-plaintext highlighter-rouge">/aws/events/odba_events</code> log group. The example below records a <code class="language-plaintext highlighter-rouge">FetchProtectedDatabaseConfiguration</code> operation as an audit-style service event. AWS documents Oracle Database@AWS events as structured messages about resource lifecycle changes, including Exadata infrastructure, VM cluster, CDB, and PDB events. CloudTrail separately records Oracle Database@AWS control-plane API calls. These streams are valuable for tracking provisioning, configuration changes, and administrative activity, but they are different from the diagnostic files generated inside the database servers. <a href="https://docs.aws.amazon.com/odb/latest/UserGuide/monitoring-events.html">Oracle Database@AWS events</a>, <a href="https://docs.aws.amazon.com/odb/latest/UserGuide/logging-using-cloudtrail.html">Oracle Database@AWS CloudTrail logging</a></p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/cloudwatch-odba-events-redacted.png" alt="Oracle Database@AWS service event in the CloudWatch odba_events log group." class="align-center" /></p>

<p><em>Figure 3. An audit-style Oracle Database@AWS service event in <code class="language-plaintext highlighter-rouge">/aws/events/odba_events</code>. Account identifiers, ARNs, OCIDs, event identifiers, the IP address, and other environment-specific values were redacted for publication.</em></p>

<p>Database alert logs, listener logs, ASM logs, and Clusterware logs are produced on the Exadata database VMs. Without centralized collection, a DBA investigating an <code class="language-plaintext highlighter-rouge">ORA-07445</code>, <code class="language-plaintext highlighter-rouge">ORA-00600</code>, listener failure, or Clusterware event must connect to the relevant database nodes, traverse the database and Grid Infrastructure diagnostic directory structures, identify the correct instance and time range, and then correlate records across nodes. That process becomes slower and less consistent as the number of VM clusters grows.</p>

<p>Exadata diagnostics are also distributed across components and VM-local directories. A RAC database has instance-specific diagnostics; listeners, ASM, and Clusterware have their own files and ownership. Troubleshooting therefore requires both access to the right files and enough context to know which component produced each record.</p>

<p>As the fleet grows, several practical issues accumulate. Nodes can have different database homes and ADR paths. File access differs between the database owner, GI owner, and collection account. Rotation can remove incident evidence before someone retrieves it. A newly added VM can be missing a source association even though the rest of the cluster is collecting successfully.</p>

<p>Use a small collection inventory to turn those issues into explicit configuration:</p>

<table>
  <thead>
    <tr>
      <th>Diagnostic area</th>
      <th>Initial operational question</th>
      <th>Collection priority</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Database alert</td>
      <td>Which instance reported an ORA error, restart, or other significant event?</td>
      <td>Baseline</td>
    </tr>
    <tr>
      <td>Listener</td>
      <td>What connection-related messages occurred during the incident?</td>
      <td>Baseline</td>
    </tr>
    <tr>
      <td>Clusterware</td>
      <td>Did resource, membership, or service events coincide with the symptoms?</td>
      <td>Baseline alert coverage</td>
    </tr>
    <tr>
      <td>ASM</td>
      <td>What storage-management events were visible to the guest cluster?</td>
      <td>Baseline alert coverage</td>
    </tr>
    <tr>
      <td>Database/GI traces and incident dumps</td>
      <td>What deeper evidence is needed for this diagnosis?</td>
      <td>Targeted collection</td>
    </tr>
    <tr>
      <td>Audit records</td>
      <td>Which auditable actions require investigation or retention?</td>
      <td>Separate security use case</td>
    </tr>
  </tbody>
</table>

<p>This article collects from <strong>customer-accessible Exadata database VMs</strong> in Oracle Database@AWS and ExaC@C. Oracle-managed physical hosts and Exadata storage cells have different operating responsibilities. The presence of an Exadata parser in a catalog does not provide customer access to the infrastructure that produces those logs. <a href="https://docs.oracle.com/en-us/iaas/exadatacloud/doc/ecs-security-guide.html">ExaDB-D responsibility model</a>, <a href="https://docs.oracle.com/en/engineered-systems/exadata-cloud-at-customer/eccid/all_diagrams.html">ExaC@C architecture</a></p>

<h2 id="the-value-of-oci-log-analytics-for-multicloud-databases">The value of OCI Log Analytics for multicloud databases</h2>

<p>The cloud-native operating model is to deploy an OCI Management Agent with the Log Analytics plug-in on every Exadata database VM whose local logs must be monitored. Each agent reads the authorized database and GI files and sends their records to OCI Log Analytics, where the operations team can search, parse, correlate, visualize, and report on them as a fleet. This removes the need to begin every investigation by signing in to each node and manually searching separate diagnostic trees.</p>

<p>For a fleet of ExaDB-D or ExaC@C VM clusters, a useful log service must do more than retain files. Operators need to search the same error across instances, distinguish recurring messages from new patterns, and follow an incident from a database symptom into its listener, GI, and guest-host evidence.</p>

<p>OCI Log Analytics provides log collection, parsing, enrichment, search, and visualization in one service. Its catalog includes more than 250 prebuilt parsers across Oracle and other technologies. That lets a database operations team begin with Oracle-defined content and extend it when a diagnostic format needs custom handling. <a href="https://www.oracle.com/manageability/log-analytics/">OCI Log Analytics capabilities</a>, <a href="https://docs.oracle.com/en-us/iaas/Content/database-at-aws-exadata-awsmn/awsmn-monitor-oci.html">OCI Log Analytics for Oracle Database@AWS</a></p>

<p>The operational value is a common place to answer concrete questions:</p>

<ul>
  <li><strong>Scope:</strong> Is an error isolated to an instance, repeated on both RAC nodes, or appearing across several VM clusters?</li>
  <li><strong>Sequence:</strong> Did a listener failure follow a database event, or did both coincide with a GI event?</li>
  <li><strong>Change:</strong> Which message patterns appeared during the incident that were absent in the earlier comparison window?</li>
  <li><strong>Evidence:</strong> Which exact records support the working explanation and the handoff to the next operations team?</li>
</ul>

<h2 id="build-the-operating-model-around-oci-log-analytics">Build the operating model around OCI Log Analytics</h2>

<h3 id="collect-at-the-vm-investigate-across-the-fleet">Collect at the VM, investigate across the fleet</h3>

<p>Deploy a standalone Management Agent with the Log Analytics plug-in on each guest VM whose local logs you need. Represent the emitting components with Log Analytics entities, associate their sources, and send records to the intended log group. This preserves the instance and node context needed for fleet analysis. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/continuous-log-collection-form-your-hosts.html">Continuous collection workflow</a></p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/collection-architecture.png" alt="Proposed OCI Log Analytics collection architecture for Oracle Database@AWS ExaDB-D guest VM clusters." class="align-center" /></p>

<p><em>Figure 4. Proposed collection architecture. Each VM contributes its accessible logs to OCI Log Analytics. The regional connectivity path must be validated for the target deployment.</em></p>

<p>Keep three configuration concepts distinct. A <strong>source</strong> defines how records are collected and processed; a <strong>parser</strong> extracts fields; an <strong>entity</strong> identifies the component that generated them. A <strong>log group</strong> is the destination for collected records, governed through OCI IAM and compartments. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/logging-analytics-terms-concepts.html">Log Analytics concepts</a></p>

<p>Create a naming convention such as <code class="language-plaintext highlighter-rouge">aws-prod-cluster01-vm01-db01</code> for an instance entity and record its relationship to the host and VM cluster. Maintain an expected inventory of VMs, instances, and source associations. Where operators need queryable AWS account or cluster dimensions, configure and verify the relevant enrichment; OCI resource tags should not be assumed to appear automatically as fields on every log record.</p>

<h3 id="establish-the-aws-to-oci-collection-path">Establish the AWS-to-OCI collection path</h3>

<p>AWS documents that an ODB network corresponds to a VCN in the linked OCI tenancy. Oracle’s Database@AWS security prerequisites illustrate a Service Gateway route to OCI Vault, while the OCI service matrix lists Management Agent, LogAnalytics, Monitoring, and Monitoring Ingestion as supported through Service Gateway. These are the basis for the <strong>proposed</strong> private service path in Figure 4. They do not replace an end-to-end check of Log Analytics collection from the target guest VM. <a href="https://docs.aws.amazon.com/odb/latest/UserGuide/configuring.html">AWS ODB networking</a>, <a href="https://docs.oracle.com/en-us/iaas/Content/database-at-aws-exadata-awssc/awssc-security-prerequisites.html">Oracle Database@AWS network prerequisites</a>, <a href="https://www.oracle.com/cloud/networking/private-service-access/service-gateway-and-psa-supported-services/">Service Gateway support matrix</a></p>

<p>Before installing, have the network owner verify the linked OCI region, existing gateway and route configuration, DNS resolution, and permitted HTTPS egress. Relevant endpoint patterns include:</p>

<table>
  <thead>
    <tr>
      <th>Purpose</th>
      <th>HTTPS destination</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Management Agent service</td>
      <td><code class="language-plaintext highlighter-rouge">management-agent.&lt;region&gt;.oci.oraclecloud.com</code></td>
    </tr>
    <tr>
      <td>Log records and collection warnings</td>
      <td><code class="language-plaintext highlighter-rouge">loganalytics.&lt;region&gt;.oci.oraclecloud.com</code></td>
    </tr>
    <tr>
      <td>Collection metrics</td>
      <td><code class="language-plaintext highlighter-rouge">telemetry-ingestion.&lt;region&gt;.oraclecloud.com</code></td>
    </tr>
  </tbody>
</table>

<p>Use the full current prerequisites for the deployment; this table is not an exhaustive allowlist. Validate TLS with certificate verification enabled. A successful connection test establishes reachability, while agent registration and a newly ingested record establish that the collection workflow works. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/troubleshoot-management-agents.html">Agent connectivity diagnostics</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/install-management-agents.html">Log Analytics agent endpoints</a></p>

<h3 id="turn-records-into-explanations-and-repeatable-investigations">Turn records into explanations and repeatable investigations</h3>

<p>Log Explorer supports interactive investigation as well as saved queries. Cluster analysis groups recurring message patterns; Link provides ways to analyze related records. Use these capabilities to narrow an incident before reading the underlying messages in detail. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/perform-advanced-analytics-link.html">Advanced analytics</a></p>

<p>LoganAI adds generated explanations, summaries, and context-aware follow-up questions for selected logs and visualizations. For example, an operator can ask for a summary of database errors in a time window, then investigate the suggested next question against GI and host evidence. This assists RCA; the operator still verifies the conclusion against the records. Enabling LoganAI requires the documented Generative AI region, IAM, and service prerequisites. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/use-loganai.html">LoganAI</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/prerequisites-using-loganai.html">Enablement prerequisites</a></p>

<p>For a broader application-to-database view, OCI Log Analytics also accepts OpenTelemetry logs through the documented <code class="language-plaintext highlighter-rouge">UploadOtlpLogs</code> API using OTLP JSON. This is an optional ingestion path for application context; it is separate from the guest-VM file collection configured here. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/upload-opentelemetry-logs.html">OpenTelemetry log ingestion</a></p>

<h2 id="install-the-management-agent-and-configure-exadb-d-and-exacc-log-collection">Install the Management Agent and configure ExaDB-D and ExaC@C log collection</h2>

<p>The procedure below follows Oracle’s public Exadata ZIP installation guidance, which explicitly prohibits RPM installation on Exadata and specifies <code class="language-plaintext highlighter-rouge">/u02</code> for Exadata Cloud in OCI and Cloud@Customer. It applies directly to ExaDB-D in OCI and ExaC@C; this article uses an Oracle Database@AWS ExaDB-D guest VM as the worked example. Before applying the AWS adaptation, confirm the applicable image and lifecycle requirements in <strong>MOS 3015115.1, OCI: Observability &amp; Management Support For Exadata Cloud</strong>, with Oracle Support when needed. The public guide does not explicitly name AWS in its <code class="language-plaintext highlighter-rouge">/u02</code> statement, and connectivity differs among AWS, OCI, and the customer data center. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/install-management-agent-chapter.html">Exadata installation guidance</a></p>

<h3 id="step-1-establish-the-oci-destination-and-permissions">Step 1: Establish the OCI destination and permissions</h3>

<p>Enable Log Analytics in the chosen OCI region and create the destination log group. Record the region, agent compartment, log-group compartment, and log-group OCID. Keep human administration separate from the identity used by the running collectors.</p>

<p>For example, delegate agent administration to an OCI group, substituting your identity-domain and compartment names:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Allow group &lt;domain&gt;/LogAnalyticsAdmins to manage management-agents in compartment &lt;agent_compartment&gt;
Allow group &lt;domain&gt;/LogAnalyticsAdmins to manage management-agent-install-keys in compartment &lt;agent_compartment&gt;
Allow group &lt;domain&gt;/LogAnalyticsAdmins to read metrics in compartment &lt;agent_compartment&gt;
</code></pre></div></div>

<p>These statements cover agent administration. For Log Analytics configuration, use an existing authorized role or add the following service permissions, applying resource access to each compartment containing entities or log groups:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Allow group &lt;domain&gt;/LogAnalyticsAdmins to use loganalytics-features-family in tenancy
Allow group &lt;domain&gt;/LogAnalyticsAdmins to use loganalytics-resources-family in compartment &lt;log_configuration_compartment&gt;
Allow group &lt;domain&gt;/LogAnalyticsAdmins to manage management-dashboard-family in compartment &lt;dashboard_compartment&gt;
Allow group &lt;domain&gt;/LogAnalyticsAdmins to read compartments in tenancy
Allow service loganalytics to read loganalytics-features-family in tenancy
</code></pre></div></div>

<p>Initial service enablement requires the documented administrator access; the onboarding workflow may have already created the service policy. Features-family permissions are tenancy-wide, while resource-family permissions can be compartment-scoped. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/enable-access-logging-analytics-its-resources.html">Log Analytics access setup</a></p>

<p>Have an authorized IAM administrator create the policies and a dynamic group for collectors in the agent compartment:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>ALL {resource.type='managementagent', resource.compartment.id='&lt;agent_compartment_ocid&gt;'}
</code></pre></div></div>

<p>Grant this group permission to upload logs, emit collection metrics, and read tenancy user information. Oracle’s policy templates support selecting the destination compartments for the first two grants; <code class="language-plaintext highlighter-rouge">READ USERS</code> is tenancy-scoped:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Allow dynamic-group &lt;domain&gt;/LogAnalyticsAgents to {LOG_ANALYTICS_LOG_GROUP_UPLOAD_LOGS} in compartment &lt;log_group_compartment&gt;
Allow dynamic-group &lt;domain&gt;/LogAnalyticsAgents to use metrics in compartment &lt;collection_metrics_compartment&gt;
Allow dynamic-group &lt;domain&gt;/LogAnalyticsAgents to read users in tenancy
</code></pre></div></div>

<p>Match the dynamic group’s compartment to the install key’s compartment. Select the metrics compartment actually used by your collector configuration. IAM authorizes the agent’s OCI operations; filesystem permissions separately determine which local logs it can read. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/allow-continuous-log-collection-using-management-agents.html">Continuous-collection IAM policies</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/oracle-defined-policy-templates-common-use-cases.html">compartment-scoped templates</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/security-monitoring-solution.html">automatic-ingestion policy example</a></p>

<h3 id="step-2-verify-host-prerequisites">Step 2: Verify host prerequisites</h3>

<p>Complete the network validation in Section 3 before continuing on each VM.</p>

<p>Confirm sudo access, time synchronization, adequate free space on <code class="language-plaintext highlighter-rouge">/u02</code>, and that the host has <code class="language-plaintext highlighter-rouge">unzip</code>. The observed <code class="language-plaintext highlighter-rouge">260729.1846</code> installer checks <code class="language-plaintext highlighter-rouge">JAVA_HOME</code> first and then <code class="language-plaintext highlighter-rouge">/usr/bin/java</code>; on the validated guest it found Java <code class="language-plaintext highlighter-rouge">1.8.0_491</code>. Before installation, verify that root can read and execute the supported Java runtime. Set <code class="language-plaintext highlighter-rouge">JAVA_HOME</code> only when the required Java is not available through the default path, then verify it from the root shell. Follow the prerequisites for the exact agent release. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/install-management-agent-chapter.html">Management Agent installation</a></p>

<p>The examples use the host’s <code class="language-plaintext highlighter-rouge">unzip</code> utility. Confirm it is available before the installation window.</p>

<h3 id="step-3-prepare-the-zip-installation">Step 3: Prepare the ZIP installation</h3>

<p>Download the <strong>Linux ZIP</strong> and its published SHA-256 checksum from Management Agent administration. Create a time-limited install key for the planned node count and download its response-file template. Transfer these through your approved administration channel.</p>

<p>For a new installation, confirm that <code class="language-plaintext highlighter-rouge">/opt/oracle</code> already exists, then create the external-volume target and the symbolic link exactly as the documented ZIP procedure specifies:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo mkdir</span> <span class="nt">-p</span> /u02/app/oracle/mgmt_agent
<span class="nb">sudo ln</span> <span class="nt">-s</span> /u02/app/oracle/mgmt_agent /opt/oracle/mgmt_agent
</code></pre></div></div>

<p>Do not run these commands over an existing agent directory or symlink; inspect an existing deployment before changing it. The installer creates and owns the default <code class="language-plaintext highlighter-rouge">mgmt_agent</code> operating-system user. Do not pre-create a group, user, or custom home solely for this procedure. The <code class="language-plaintext highlighter-rouge">/u02</code> requirement applies to the <strong>agent installation directory</strong>, not to the account home. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/install-management-agent-chapter.html">Management Agent installation</a></p>

<h3 id="step-4-extract-configure-and-install">Step 4: Extract, configure, and install</h3>

<p>Use the Exadata layout from the earlier A-Team procedure: create <code class="language-plaintext highlighter-rouge">install_dir</code> below the external <code class="language-plaintext highlighter-rouge">/u02</code> agent path and extract the Linux ZIP there. Because the directory is created with <code class="language-plaintext highlighter-rouge">sudo</code> and is normally owned by root at this point, this example also uses <code class="language-plaintext highlighter-rouge">sudo</code> for extraction. This avoids depending on whether the staging user can write to the new directory.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo mkdir</span> <span class="nt">-p</span> /u02/app/oracle/mgmt_agent/install_dir
<span class="nb">sudo </span>unzip /home/opc/oracle.mgmt_agent.260729.1846.Linux-x86_64.zip <span class="se">\</span>
  <span class="nt">-d</span> /u02/app/oracle/mgmt_agent/install_dir
<span class="nb">cd</span> /u02/app/oracle/mgmt_agent/install_dir/mgmt_agent
</code></pre></div></div>

<p>The observed ZIP creates a nested <code class="language-plaintext highlighter-rouge">mgmt_agent</code> directory containing <code class="language-plaintext highlighter-rouge">installer.sh</code>; running the installer from <code class="language-plaintext highlighter-rouge">install_dir</code> itself returns <code class="language-plaintext highlighter-rouge">No such file or directory</code>. The ZIP filename and <code class="language-plaintext highlighter-rouge">/home/opc</code> source path reflect the observed environment. Before extracting, compare the ZIP’s <code class="language-plaintext highlighter-rouge">sha256sum</code> output with the checksum in Management Agent administration, as Oracle recommends.</p>

<p>Before opening the root shell or running the installer, edit and securely save <code class="language-plaintext highlighter-rouge">mgmt_agent_exadbd.rsp</code>. Use the downloaded install key in the local file, but never capture it in screenshots, tickets, or source control. The following is a screenshot-safe rendering: it retains the observed display name and plug-in options while redacting the sensitive value.</p>

<div class="language-properties highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Do not replace this marker with the actual key in screenshots or published material.
</span><span class="py">ManagementAgentInstallKey</span> <span class="p">=</span> <span class="s">&lt;REDACTED-INSTALL-KEY&gt;</span>
<span class="py">AgentDisplayName</span> <span class="p">=</span> <span class="s">odb-aws-host-vak331</span>

<span class="c">#FreeFormTags = [{"&lt;key1&gt;":"&lt;value1&gt;"}, {"&lt;key2&gt;":"&lt;value2&gt;"}]
#DefinedTags = [{"namespace1":{"&lt;key1&gt;":"&lt;value1&gt;"}}, {"namespace2":{"&lt;key2&gt;":"&lt;value2&gt;"}}]
#CredentialWalletPassword =
#Service.plugin.jm-container.download=true
#Service.plugin.appmgmt.download=true
#Service.plugin.jms.download=true
#Service.plugin.dbaas.download=true
</span><span class="py">Service.plugin.logan.download</span><span class="p">=</span><span class="s">true</span>
<span class="c">#Service.plugin.mds.download=true
#Service.plugin.osmh.download=true
#Service.plugin.opsiHost.download=true
#Service.plugin.jm.download=true
#Service.plugin..startup.jersey.hotpath.1.2f97483d-2052-4ce7-b18e-59a835d599c4.plugin.download=true
</span></code></pre></div></div>

<p>Only <code class="language-plaintext highlighter-rouge">Service.plugin.logan.download=true</code> is enabled in this response file; the remaining shown plug-in options are commented out. Add required defined tags and any approved gateway settings from your environment. Do not paste the key into shell history. The response file contains the installation key, so retain it in the approved protected transfer location and delete or store it securely after successful registration. Oracle requires the response file and every parent directory to be accessible to the <code class="language-plaintext highlighter-rouge">mgmt_agent</code> OS user.</p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/mgmt-agent-exadbd-response-file-redacted.png" alt="Screenshot-safe Management Agent response file for the Oracle Database@AWS ExaDB-D guest VM." class="align-center" /></p>

<p><em>Figure 5. Screenshot-safe rendering of <code class="language-plaintext highlighter-rouge">mgmt_agent_exadbd.rsp</code>; the install key is redacted, while the observed agent display name and response-file options are retained.</em></p>

<p><strong>Important — stage the response file in <code class="language-plaintext highlighter-rouge">/tmp</code> before running <code class="language-plaintext highlighter-rouge">installer.sh</code>.</strong> The installer creates <code class="language-plaintext highlighter-rouge">mgmt_agent</code> and then configures the agent as that user. A response file under <code class="language-plaintext highlighter-rouge">/home/opc</code> may be unreadable because of parent-directory permissions. Copy the completed response file to <code class="language-plaintext highlighter-rouge">/tmp</code>, then grant only the temporary read access required during bootstrap:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo cp</span> /home/opc/mgmt_agent_exadbd.rsp /tmp/mgmt_agent_exadbd.rsp
<span class="nb">sudo chmod </span>0644 /tmp/mgmt_agent_exadbd.rsp
</code></pre></div></div>

<p>The validated troubleshooting session used mode <code class="language-plaintext highlighter-rouge">777</code>, which proved that permissions caused the failure. Do <strong>not</strong> use <code class="language-plaintext highlighter-rouge">777</code> in the published procedure: the response file contains an install key, and mode <code class="language-plaintext highlighter-rouge">777</code> lets every local user read, modify, and execute it. Mode <code class="language-plaintext highlighter-rouge">0644</code> is the minimum practical bootstrap permission before the installer creates <code class="language-plaintext highlighter-rouge">mgmt_agent</code>; remove the file immediately after successful configuration.</p>

<p>After the response file is saved and accessible to the agent user, explicitly change into the nested directory that contains <code class="language-plaintext highlighter-rouge">installer.sh</code>, then open a root shell:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cd</span> /u02/app/oracle/mgmt_agent/install_dir/mgmt_agent
<span class="nb">sudo</span> /bin/bash
</code></pre></div></div>

<p>At the root-shell prompt, start the installation:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">export </span><span class="nv">OPT_ORACLE_SYMLINK</span><span class="o">=</span><span class="nb">true</span>
./installer.sh /tmp/mgmt_agent_exadbd.rsp
</code></pre></div></div>

<h3 id="if-installation-succeeds-but-agent-configuration-fails">If installation succeeds but agent configuration fails</h3>

<p>The observed installation completed the software copy and service creation, then failed configuration because the new <code class="language-plaintext highlighter-rouge">mgmt_agent</code> user could not read <code class="language-plaintext highlighter-rouge">/home/opc/mgmt_agent_exadbd.rsp</code>. This is a partial success: do not reinstall the ZIP. Review the configure log first:</p>

<p>The following host output was captured before the <code class="language-plaintext highlighter-rouge">/tmp</code> correction, when <code class="language-plaintext highlighter-rouge">installer.sh</code> received the response file under <code class="language-plaintext highlighter-rouge">/home/opc</code>. It shows the distinction between successful software installation and failed agent configuration:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Checking pre-requisites
        Checking if any previous agent service exists
        Checking if OS has systemd or initd
        Checking available disk space for agent install
        Checking if /opt/oracle/mgmt_agent directory exists
        Checking if 'mgmt_agent' user exists
        'mgmt_agent' user does not exist. Proceeding to create the user...
        User home directory is valid and writable. Proceeding with user creation...
        Creating user on Linux-based OS...
        Checking Java version
                JAVA_HOME is not set or not readable to root
                Trying default path /usr/bin/java
                Java version: 1.8.0_491 found at /usr/bin/java
        Checking agent version

Executing install
        Unpacking software zip
        Copying files to destination dir (/opt/oracle/mgmt_agent)
        Initializing software from template
        Checking if JavaScript engine is available to use
        Creating mgmt_agent daemon
        Agent Install Logs: /opt/oracle/mgmt_agent/installer-logs/installer.log.0

Agent install successful

/home/opc/mgmt_agent_exadbd.rsp file is either not present or not readable to mgmt_agent user
Please make sure that the directory and parent directories also have the read permissions to make this file readable.

You may execute the following commands to make sure mgmt_agent user can read input.rsp:
cd /tmp
sudo -u mgmt_agent cat &lt;FULL_PATH&gt;/input.rsp

Missing mandatory properties opts
Usage: setup.sh opts=&lt;FULL-PATH&gt;
Please make sure there is no space in between opts=&lt;FULL-PATH&gt;

Executing configure

Prerequisite check failed
Pass opts=&lt;&gt; to application at the startup
Additional details are available in the configure logs at /u02/app/oracle/mgmt_agent/configure-logs

Agent configure failed.
Additional logs can be found at /opt/oracle/mgmt_agent/configure-logs/configure.log.0
</code></pre></div></div>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo tail</span> <span class="nt">-n</span> 200 /opt/oracle/mgmt_agent/configure-logs/configure.log.0
<span class="nb">sudo</span> <span class="nt">-u</span> mgmt_agent <span class="nb">cat</span> /home/opc/mgmt_agent_exadbd.rsp <span class="o">&gt;</span>/dev/null
</code></pre></div></div>

<p>If the second command reports <code class="language-plaintext highlighter-rouge">Permission denied</code>, copy the response file to <code class="language-plaintext highlighter-rouge">/tmp</code>. Because <code class="language-plaintext highlighter-rouge">mgmt_agent</code> now exists, assign the file directly to that user with mode <code class="language-plaintext highlighter-rouge">0600</code>, then verify access without printing the install key:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo cp</span> /home/opc/mgmt_agent_exadbd.rsp /tmp/mgmt_agent_exadbd.rsp
<span class="nb">sudo chown </span>mgmt_agent:mgmt_agent /tmp/mgmt_agent_exadbd.rsp
<span class="nb">sudo chmod </span>0600 /tmp/mgmt_agent_exadbd.rsp
<span class="nb">sudo</span> <span class="nt">-u</span> mgmt_agent <span class="nb">cat</span> /tmp/mgmt_agent_exadbd.rsp <span class="o">&gt;</span>/dev/null
</code></pre></div></div>

<p>Rerun only the configuration step. The <code class="language-plaintext highlighter-rouge">opts=</code> argument is mandatory and must not contain spaces around the equals sign:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo</span> /opt/oracle/mgmt_agent/agent_inst/bin/setup.sh <span class="se">\</span>
  <span class="nv">opts</span><span class="o">=</span>/tmp/mgmt_agent_exadbd.rsp
</code></pre></div></div>

<p>The corrected retry produced the following successful configuration output:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Executing configure
        Parsing input response file
        Validating install key
        Generating communication wallet
        Generating security artifacts
        Registering Management Agent
                Found service plugin(s): [logan]

Starting agent...
Agent started successfully

Starting plugin deployment for: [logan]
Deploying service plugin(s)...Done.
logan : Successfully deployed service plugin

Agent setup completed and the agent is running.
In the future agent can be started by directly running: sudo systemctl start mgmt_agent
Please use OCI CLI or OCI Management Agent console to validate the successful activation of your agent.

Please make sure that you delete /tmp/mgmt_agent_exadbd.rsp or store it in secure location.
</code></pre></div></div>

<p>On the validated guest, this retry completed install-key validation, wallet generation, registration, agent startup, and deployment of the <code class="language-plaintext highlighter-rouge">logan</code> plug-in. If configuration fails again, preserve <code class="language-plaintext highlighter-rouge">/opt/oracle/mgmt_agent/configure-logs/configure.log.0</code> and check the exact reported cause. Common next checks are an expired or exhausted install key, incorrect gateway/proxy parameters, and DNS, TLS, or TCP 443 connectivity to the configured OCI regional endpoint. Correct the response file or connectivity issue, verify readability again as <code class="language-plaintext highlighter-rouge">mgmt_agent</code>, and rerun the same <code class="language-plaintext highlighter-rouge">setup.sh opts=...</code> command. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/install-management-agent-chapter.html">Management Agent setup</a></p>

<p>After setup succeeds and the agent appears active in OCI, remove the temporary response file:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo rm</span> <span class="nt">-f</span> /tmp/mgmt_agent_exadbd.rsp
</code></pre></div></div>

<h3 id="step-5-validate-the-agent-and-plug-in">Step 5: Validate the agent and plug-in</h3>

<p>Check the process and physical location:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>systemctl status mgmt_agent <span class="nt">--no-pager</span>
<span class="nb">readlink</span> <span class="nt">-f</span> /opt/oracle/mgmt_agent
<span class="nb">grep</span> <span class="nt">-F</span> <span class="s1">'packageType=ZIP'</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/security/resource/agent.package
rpm <span class="nt">-qa</span> | <span class="nb">grep</span> <span class="nt">-i</span> mgmt_agent <span class="o">||</span> <span class="nb">true
stat</span> <span class="nt">-c</span> <span class="s1">'%U %n'</span> /opt/oracle/mgmt_agent
<span class="nb">stat</span> <span class="nt">-c</span> <span class="s1">'%U %n'</span> /opt/oracle/mgmt_agent/agent_inst
</code></pre></div></div>

<p><code class="language-plaintext highlighter-rouge">systemctl</code> confirms the service state. <code class="language-plaintext highlighter-rouge">readlink</code> confirms that <code class="language-plaintext highlighter-rouge">/opt/oracle/mgmt_agent</code> resolves to the <code class="language-plaintext highlighter-rouge">/u02</code> installation target; <code class="language-plaintext highlighter-rouge">agent.package</code> must report <code class="language-plaintext highlighter-rouge">packageType=ZIP</code>; the RPM query must produce no Management Agent package; and both ownership checks must report <code class="language-plaintext highlighter-rouge">mgmt_agent</code>.</p>

<p>Next, validate registration and communication in the Management Agent Cloud Service:</p>

<ol>
  <li>In the OCI Console, select the region where the Management Agent resources were created.</li>
  <li>Open <strong>Observability &amp; Management → Management Agent → Agents</strong> and select the agent compartment.</li>
  <li>Search for the node-specific <code class="language-plaintext highlighter-rouge">AgentDisplayName</code>, such as <code class="language-plaintext highlighter-rouge">odb-aws-host-vak331</code> or <code class="language-plaintext highlighter-rouge">odb-aws-host-vak332</code>.</li>
  <li>Confirm that <strong>Availability</strong> is <strong>Active</strong>, <strong>Operating system</strong> is <strong>LINUX</strong>, and <strong>Version</strong> matches the installed ZIP build. Review <strong>Upgrade</strong> for any required update.</li>
  <li>Confirm that <strong>Service plug-ins</strong> lists <strong>Log Analytics</strong>. Open the agent details and verify that the Log Analytics plug-in status is <strong>Running</strong>.</li>
  <li>Repeat the check for every database node and reconcile the console list with the planned VM-cluster inventory. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/management-agents-administration-tasks.html">Management Agent console</a></li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/mgmt-agent-cloud-service-active-agents-redacted.png" alt="Public-safe OCI Management Agent Cloud Service view showing two active Oracle Database@AWS ExaDB-D database-node agents with the Log Analytics plug-in." class="align-center" /></p>

<p><em>Figure 6. Management Agent Cloud Service validation for two ExaDB-D database nodes. Both agents are active on version <code class="language-plaintext highlighter-rouge">260729.1846</code>, show <code class="language-plaintext highlighter-rouge">Up to date</code>, and list the Log Analytics plug-in. The compartment identifier and private DNS suffixes were replaced for publication.</em></p>

<p>An <strong>Active</strong> agent establishes cloud registration and recent Management Agent communication; it does not by itself prove that database or GI logs are being ingested. Associate the intended host, database, and cluster entities and sources, then verify a recent event from each node in Log Explorer. Check collection warnings and metrics, and test rotated or newly created files as well as existing files. For selected log paths, use ACLs that grant directory traversal and file read access, including appropriate default ACLs. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/grant-read-access-logs-agent-user-your-host.html">Log permissions</a></p>

<p>For this Log Analytics-focused article, <code class="language-plaintext highlighter-rouge">Service.plugin.logan.download=true</code> is the only required plug-in. Enable Database Management or Ops Insights only when those services are part of the deployment; they are not prerequisites for collecting database or GI logs in OCI Log Analytics. If the Log Analytics plug-in was not enabled in the response file, it can instead be deployed from the Management Agent page in the OCI Console. <a href="https://www.ateam-oracle.com/maximize-visibillity-collecting-and-analyzing-logs-for-multiple-oracle-databases-using-oci-logging-analytics">Earlier A-Team procedure</a></p>

<h3 id="step-6-install-and-configure-the-agent-on-every-database-node">Step 6: Install and configure the agent on every database node</h3>

<p>After the first database node completes configuration and passes the Step 5 checks, copy the same Management Agent ZIP and a protected copy of the response-file template to every remaining Exadata database node. Install a separate Management Agent locally on each node whose database or GI files must be collected. Do not copy the installed <code class="language-plaintext highlighter-rouge">/u02/app/oracle/mgmt_agent</code> directory from one node to another.</p>

<p>Before reusing the response file, open <strong>Observability &amp; Management → Management Agent → Administration → Install keys</strong>. Confirm that the key is active and that its remaining installations can accommodate all remaining nodes. Create or download a new install key when the existing key is expired, exhausted, or its <strong>Maximum installations</strong> setting does not cover the planned node count. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/management-agents-administration-tasks.html">Install-key administration</a></p>

<p>Use the approved encrypted transfer method for the environment. For example, from the node or staging host that currently holds the two files:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nv">target_dbnode</span><span class="o">=</span>host-vak332
scp /home/opc/oracle.mgmt_agent.260729.1846.Linux-x86_64.zip <span class="se">\</span>
  /home/opc/mgmt_agent_exadbd.rsp <span class="se">\</span>
  opc@<span class="s2">"</span><span class="nv">$target_dbnode</span><span class="s2">"</span>:/home/opc/
ssh opc@<span class="s2">"</span><span class="nv">$target_dbnode</span><span class="s2">"</span> <span class="se">\</span>
  <span class="s1">'chmod 0600 /home/opc/mgmt_agent_exadbd.rsp'</span>
</code></pre></div></div>

<p>Treat the copied response file as a template. On the target node, change <code class="language-plaintext highlighter-rouge">AgentDisplayName</code> to a node-specific value before staging the file in <code class="language-plaintext highlighter-rouge">/tmp</code>. This makes every database node easy to identify in the Management Agent and Log Analytics consoles. For example:</p>

<div class="language-properties highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="py">AgentDisplayName</span> <span class="p">=</span> <span class="s">odb-aws-host-vak332</span>
</code></pre></div></div>

<p>Retain the validated install key and <code class="language-plaintext highlighter-rouge">Service.plugin.logan.download=true</code>, along with any approved tags or gateway settings that apply to that node. Then repeat Steps 2–5 on the target node: complete the preflight checks, create the <code class="language-plaintext highlighter-rouge">/u02</code> target and <code class="language-plaintext highlighter-rouge">/opt/oracle/mgmt_agent</code> symlink, extract the ZIP, stage the response file, run <code class="language-plaintext highlighter-rouge">installer.sh</code>, validate <code class="language-plaintext highlighter-rouge">packageType=ZIP</code>, and confirm that the agent and <code class="language-plaintext highlighter-rouge">logan</code> plug-in are active. Apply the <code class="language-plaintext highlighter-rouge">emd.properties</code> and 2 GB heap baseline below, restart the agent, and validate log collection from that node.</p>

<p>Repeat this sequence for every database node in every VM cluster. Confirm a distinct active agent and current log records for each node in OCI Log Analytics. After a node is registered successfully, delete its temporary response-file copies as described in Step 4. Keep any retained master copy only in the approved secret-management location.</p>

<h3 id="best-practice-establish-an-exadata-management-agent-baseline">Best practice: establish an Exadata Management Agent baseline</h3>

<p>For an ExaDB-D or ExaC@C fleet that collects database and GI logs, start with the following Management Agent properties. Back up <code class="language-plaintext highlighter-rouge">emd.properties</code>, edit the original file, and add the settings in its additional-properties section:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo cp</span> <span class="nt">-p</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/emd.properties <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/emd.properties.pre-exadbd-baseline
<span class="nb">sudo </span>vi /opt/oracle/mgmt_agent/agent_inst/config/emd.properties
</code></pre></div></div>

<div class="language-properties highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="py">loganalytics.enable_large_dir</span><span class="p">=</span><span class="s">true</span>

<span class="c"># Sender properties
</span><span class="py">senderManagerMaxDiskUsedTotal</span><span class="p">=</span><span class="s">1000</span>
<span class="py">_senderManagerPoolSize</span><span class="p">=</span><span class="s">10</span>

<span class="c"># Connection pooling properties
</span><span class="py">clientConnectionPool.SERVICE_INVOKING.defaultMaxConnectionsPerRoute</span><span class="p">=</span><span class="s">50</span>
<span class="py">clientConnectionPool.SERVICE_INVOKING.maxTotalConnections</span><span class="p">=</span><span class="s">100</span>
</code></pre></div></div>

<p>Treat these values as the starting baseline for this Exadata use case. Adjust them according to the number of VM clusters, databases, PDBs, enabled log sources, files created per hour, and observed collection backlog. Validate changes first on a representative VM cluster and monitor agent CPU, memory, disk use, collection latency, and errors before applying them across the fleet. The larger examples in the earlier A-Team sizing table are planning references rather than a universal certified profile.</p>

<p>Oracle defines a large log directory as one containing more than 10,000 files. <code class="language-plaintext highlighter-rouge">loganalytics.enable_large_dir=true</code> allows the agent to monitor such directories, but it can increase heap, disk, inode, and open-file demand. Clean up files that no longer need collection and confirm host capacity before enabling high-volume sources. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/advanced-configuration-options-management-agent.html">Large-directory configuration</a></p>

<p>For this standalone Management Agent deployment, configure a 2 GB maximum Java heap as the Exadata fleet baseline. Oracle documents 512 MB as the out-of-box maximum heap for a standalone Management Agent; 2 GB is the operational baseline used in this article, not the product default. Back up <code class="language-plaintext highlighter-rouge">java.options</code>, confirm the current active <code class="language-plaintext highlighter-rouge">-Xmx</code> entry, and replace it with <code class="language-plaintext highlighter-rouge">-Xmx2048m</code>:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo cp</span> <span class="nt">-p</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/java.options <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/java.options.pre-2gb-heap
<span class="nb">sudo grep</span> <span class="nt">-n</span> <span class="s1">'^-Xmx'</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/java.options
<span class="nb">sudo </span>vi /opt/oracle/mgmt_agent/agent_inst/config/java.options
</code></pre></div></div>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>-Xmx2048m
</code></pre></div></div>

<p>Restart the agent once after both files are updated, then verify the service, heap entry, and Management Agent properties:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>systemctl restart mgmt_agent
<span class="nb">sudo </span>systemctl status mgmt_agent <span class="nt">--no-pager</span>
<span class="nb">sudo grep</span> <span class="nt">-n</span> <span class="s1">'^-Xmx'</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/java.options
<span class="nb">sudo grep</span> <span class="nt">-E</span> <span class="se">\</span>
  <span class="s1">'^(loganalytics\.enable_large_dir|senderManagerMaxDiskUsedTotal|_senderManagerPoolSize|clientConnectionPool\.SERVICE_INVOKING\.(defaultMaxConnectionsPerRoute|maxTotalConnections))='</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/emd.properties
</code></pre></div></div>

<p>The following output from <code class="language-plaintext highlighter-rouge">host-vak331</code> confirms the physical <code class="language-plaintext highlighter-rouge">/u02</code> configuration path and the configured 2 GB heap. The <code class="language-plaintext highlighter-rouge">-XX:+HeapDumpOnOutOfMemoryError</code> option was also present in the installed file:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[root@host-vak331 config]# pwd
/u02/app/oracle/mgmt_agent/agent_inst/config

[root@host-vak331 config]# cat java.options
#encoding=UTF-8

#These java.options contain user supplied extensions to the options set in wrapper.conf.

#If you modify this file, please make sure that you restart the mgmt_agent service.

#Note: Please do not delete this file. Deleting this file will cause agent failures.

#Add each additional parameter on new line

#------------------------------------------------------------------------------------------------
-Dpolyglot.engine.AllowExperimentalOptions=true
-Dpolyglot.js.nashorn-compat=true
-Djdk.tls.client.protocols=TLSv1.3,TLSv1.2
-Djdk.tls.server.protocols=TLSv1.3,TLSv1.2

-Doracle.polaris.fips.approved_only=false
-XX:+HeapDumpOnOutOfMemoryError
-Dio.netty.native.workdir=/u02/app/oracle/mgmt_agent/agent_inst/tmpdir
-Dio.netty.tmpdir=/u02/app/oracle/mgmt_agent/agent_inst/tmpdir

-Dorg.newsclub.net.unix.library.tmpdir=/u02/app/oracle/mgmt_agent/agent_inst/tmpdir

-Dorg.bouncycastle.native.cpu_variant=java
-Xmx2048m
</code></pre></div></div>

<p>The same host showed the requested Log Analytics sender and connection-pool baseline at the end of <code class="language-plaintext highlighter-rouge">emd.properties</code>:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[root@host-vak331 config]# tail -10 emd.properties
################################
loganalytics.enable_large_dir=true

#Sender properties
senderManagerMaxDiskUsedTotal=1000
_senderManagerPoolSize=10

# Connection pooling properties

clientConnectionPool.SERVICE_INVOKING.defaultMaxConnectionsPerRoute=50
clientConnectionPool.SERVICE_INVOKING.maxTotalConnections=100
[root@host-vak331 config]#
</code></pre></div></div>

<p>The file output above validates the saved configuration. After the restart, the following <code class="language-plaintext highlighter-rouge">systemctl</code> output confirmed that the service was enabled and active. It also showed the wrapper and Java process running from the physical <code class="language-plaintext highlighter-rouge">/u02/app/oracle/mgmt_agent</code> installation. Long process arguments were truncated by <code class="language-plaintext highlighter-rouge">systemctl</code> in the captured terminal:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[root@host-vak331 config]# sudo systemctl status mgmt_agent --no-pager
● mgmt_agent.service - mgmt_agent
   Loaded: loaded (/etc/systemd/system/mgmt_agent.service; enabled; vendor preset: disabled)
   Active: active (running) since Thu 2026-09-17 20:08:40 UTC; 3s ago
  Process: 348607 ExecStop=/u02/app/oracle/mgmt_agent/agent_inst/bin/agentcore stop sysd (code=exited, status=0/SUCCESS)
  Process: 350167 ExecStart=/u02/app/oracle/mgmt_agent/agent_inst/bin/agentcore start sysd (code=exited, status=0/SUCCESS)
 Main PID: 350257 (wrapper)
    Tasks: 73 (limit: 319999)
   Memory: 562.9M
   CGroup: /system.slice/mgmt_agent.service
           ├─350257 /u02/app/oracle/mgmt_agent/agent_inst/bin/./wrapper /u02/app/oracle/mgmt_agent/agent_inst/bin/../config/wrapper.conf wrapper.syslog.ident=mgmt_agent wrapper.pidfile=/u02/app/oracle/mgm…
           └─350326 /usr/lib/jvm/jdk-1.8.0_491-oracle-x64/bin/java -Dorg.tanukisoftware.wrapper.WrapperSimpleApp.maxStartMainWait=5 -Djava.security.egd=file:///dev/./urandom -Dpolyglot.engine.AllowExperim…

Sep 17 20:08:28 host-vak331 systemd[1]: Starting mgmt_agent...
Sep 17 20:08:28 host-vak331 agentcore[350167]: Starting mgmt_agent...
Sep 17 20:08:35 host-vak331 agentcore[350167]: Waiting for mgmt_agent.........
Sep 17 20:08:40 host-vak331 agentcore[350167]: .....running: PID:350257
Sep 17 20:08:40 host-vak331 systemd[1]: Started mgmt_agent.
</code></pre></div></div>

<p>Together, the saved-file output and this post-restart service status validate the 2 GB heap and Management Agent property change on <code class="language-plaintext highlighter-rouge">host-vak331</code>. Continue monitoring memory, agent logs, and collection backlog as workload is added.</p>

<h4 id="troubleshoot-the-agent-reports-outofmemoryexception">Troubleshoot: the agent reports <code class="language-plaintext highlighter-rouge">OutOfMemoryException</code></h4>

<p>An agent can run out of heap when its assigned collection load exceeds the configured maximum. Check the active <code class="language-plaintext highlighter-rouge">-Xmx</code> value and recent service messages first:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo grep</span> <span class="nt">-n</span> <span class="s1">'^-Xmx'</span> <span class="se">\</span>
  /opt/oracle/mgmt_agent/agent_inst/config/java.options
<span class="nb">sudo </span>journalctl <span class="nt">-u</span> mgmt_agent <span class="nt">-n</span> 100 <span class="nt">--no-pager</span>
</code></pre></div></div>

<p>If the standalone agent is still using the 512 MB default, apply the 2 GB procedure above, restart the service, and verify that it remains active. If the exception continues at 2 GB, confirm that the VM has sufficient available memory, then review file counts, log-generation rate, enabled sources, collection backlog, and other plug-in workloads before increasing the heap again. Preserve the agent logs and engage Oracle Support when the failure persists with a supported configuration. <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/troubleshoot-management-agents.html">Management Agent <code class="language-plaintext highlighter-rouge">OutOfMemoryException</code> troubleshooting</a></p>

<p>After successful registration, remove the response file and downloaded installation artifacts from their transfer locations, or store them in the approved secret location. Record node, agent OCID, source associations, and verification time before repeating the process. For ExaC@C, retain the ZIP and <code class="language-plaintext highlighter-rouge">/u02</code> approach; adapt connectivity to the customer’s approved OCI egress path or Management Gateway, then apply the same collection checks.</p>

<h3 id="adapt-the-deployment-prerequisites-for-oci-exadb-d-and-exacc">Adapt the deployment prerequisites for OCI ExaDB-D and ExaC@C</h3>

<p>The source/entity configuration and verification steps are reusable across the fleet. Apply each environment’s network and support requirements before reusing the commands:</p>

<table>
  <thead>
    <tr>
      <th>Deployment</th>
      <th>Installation and connectivity adaptation</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Oracle Database@AWS ExaDB-D</td>
      <td>Validate AWS guest-image support for this ZIP procedure and the regional collection path through the linked OCI network.</td>
    </tr>
    <tr>
      <td>ExaDB-D in OCI</td>
      <td>Use the documented Exadata ZIP and <code class="language-plaintext highlighter-rouge">/u02</code> procedure; verify the guest subnet’s route and egress to the required regional services.</td>
    </tr>
    <tr>
      <td>ExaC@C</td>
      <td>Use the documented ZIP and <code class="language-plaintext highlighter-rouge">/u02</code> procedure; arrange connectivity from the customer guest network through the approved egress, proxy, or Management Gateway path. Do not assume the infrastructure management connection provides this path.</td>
    </tr>
  </tbody>
</table>

<p>Use the same per-VM agent, log-access, source-association, and recent-record checks in each deployment. Follow the <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/install-management-agent-chapter.html">current installation guidance</a> and <a href="https://docs.oracle.com/en-us/iaas/management-agents/doc/perform-prerequisites-deploying-management-agents.html">host/network prerequisites</a>.</p>

<h3 id="associate-database-and-gi-logs-with-the-right-entities">Associate database and GI logs with the right entities</h3>

<p>After the agent and plug-in are available, build the collection model for each VM. Use the actual source definitions in your tenancy, including their required entity properties and file patterns. The following Oracle-defined sources provide a useful starting point. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/oracle-defined-sources.html">Source catalog</a></p>

<table>
  <thead>
    <tr>
      <th>Source</th>
      <th>Entity type</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">Database Alert Logs</code></td>
      <td>Oracle Database Instance</td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">Database Listener Alert Logs</code></td>
      <td>Oracle Database Listener</td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">Automatic Storage Management Alert Logs</code></td>
      <td>Automatic Storage Management Instance</td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">Clusterware Ready Services Alert Logs</code></td>
      <td>Oracle Cluster Node</td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">Clusterware Ready Services Daemon Logs</code></td>
      <td>Oracle Cluster Node</td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">Clusterware Disk Monitor Logs</code></td>
      <td>Oracle Cluster Node</td>
    </tr>
  </tbody>
</table>

<p>For database diagnostics, connect through your approved DBA session and discover the active ADR paths:</p>

<div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="k">SELECT</span> <span class="n">name</span><span class="p">,</span> <span class="n">value</span>
<span class="k">FROM</span> <span class="n">v</span><span class="err">$</span><span class="n">diag_info</span>
<span class="k">ORDER</span> <span class="k">BY</span> <span class="n">name</span><span class="p">;</span>
</code></pre></div></div>

<p>Record the ADR home and trace directory for the particular instance. Repeat discovery for other instances instead of copying the first node’s path. Listener diagnostics should be mapped to the appropriate local or SCAN listener entity. Clusterware’s documented ADR home is <code class="language-plaintext highlighter-rouge">&lt;GRID_ORACLE_BASE&gt;/diag/crs/&lt;hostname&gt;/crs</code>, with the text alert in <code class="language-plaintext highlighter-rouge">trace/alert.log</code>; discover the actual Grid base and hostname on the VM. <a href="https://www.ateam-oracle.com/maximize-visibillity-collecting-and-analyzing-logs-for-multiple-oracle-databases-using-oci-logging-analytics">Original database walkthrough</a>, <a href="https://docs.oracle.com/en/database/oracle/oracle-database/19/cwadd/troubleshooting-oracle-clusterware.html">Clusterware diagnostics</a></p>

<h4 id="grant-mgmt_agent-access-to-database-and-listener-logs">Grant <code class="language-plaintext highlighter-rouge">mgmt_agent</code> access to database and listener logs</h4>

<p>The standalone Management Agent runs as <code class="language-plaintext highlighter-rouge">mgmt_agent</code>. That account needs read access to the log files and read/execute access through every directory in each log path. Oracle recommends filesystem ACLs as the first method to grant this access. Review existing ACLs before changing them, verify that the <code class="language-plaintext highlighter-rouge">acl</code> package is present, and add permissions without replacing existing entries. The command is <code class="language-plaintext highlighter-rouge">setfacl</code>; the similar spelling <code class="language-plaintext highlighter-rouge">setfactl</code> is invalid. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/grant-read-access-logs-agent-user-your-host.html">Grant read access to the agent user</a></p>

<p>The following database-alert example uses the observed <code class="language-plaintext highlighter-rouge">/u02/app/oracle/diag/rdbms/oradbrac/ORADBRAC2/trace</code> directory. Replace the database unique name, instance name, and path with the values discovered on the target database node. Open a root login shell:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>su -
</code></pre></div></div>

<p>At the root prompt, grant traversal on the parent directories, grant recursive access to the existing ADR contents, and set a default ACL on the trace directory for future files:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>rpm <span class="nt">-q</span> acl
getfacl <span class="nt">-p</span> /u02/app/oracle/diag
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u02
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u02/app
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u02/app/oracle
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u02/app/oracle/diag
setfacl <span class="nt">-R</span> <span class="nt">-m</span> u:mgmt_agent:rx /u02/app/oracle/diag
setfacl <span class="nt">-d</span> <span class="nt">-m</span> u:mgmt_agent:rx <span class="se">\</span>
  /u02/app/oracle/diag/rdbms/oradbrac/ORADBRAC2/trace
getfacl <span class="nt">-p</span> <span class="se">\</span>
  /u02/app/oracle/diag/rdbms/oradbrac/ORADBRAC2/trace
<span class="nb">exit</span>
</code></pre></div></div>

<p>The following listener example is for <code class="language-plaintext highlighter-rouge">host-vak332</code>. Replace the hostname and retain only the listener directories that exist on the target node:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>su -
</code></pre></div></div>

<p>At the root prompt, run:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>rpm <span class="nt">-q</span> acl
getfacl <span class="nt">-p</span> /u01/app/grid/diag
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u01
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u01/app
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u01/app/grid
setfacl <span class="nt">-m</span> u:mgmt_agent:rx /u01/app/grid/diag
setfacl <span class="nt">-R</span> <span class="nt">-m</span> u:mgmt_agent:rx /u01/app/grid/diag
setfacl <span class="nt">-d</span> <span class="nt">-m</span> u:mgmt_agent:rx <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener/trace
setfacl <span class="nt">-d</span> <span class="nt">-m</span> u:mgmt_agent:rx <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener_scan1/trace
setfacl <span class="nt">-d</span> <span class="nt">-m</span> u:mgmt_agent:rx <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener_scan2/trace
setfacl <span class="nt">-d</span> <span class="nt">-m</span> u:mgmt_agent:rx <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener_scan3/trace
setfacl <span class="nt">-d</span> <span class="nt">-m</span> u:mgmt_agent:rx <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/asmnet1lsnr_asm/trace
getfacl <span class="nt">-p</span> <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener/trace
<span class="nb">exit</span>
</code></pre></div></div>

<p>Validate the effective permissions as the agent account before associating a source. The loop below checks read and traversal access to the example directories without displaying log contents:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="k">for </span>log_dir <span class="k">in</span> <span class="se">\</span>
  /u02/app/oracle/diag/rdbms/oradbrac/ORADBRAC2/trace <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener/trace <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener_scan1/trace <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener_scan2/trace <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/listener_scan3/trace <span class="se">\</span>
  /u01/app/grid/diag/tnslsnr/host-vak332/asmnet1lsnr_asm/trace
<span class="k">do
  </span><span class="nb">sudo</span> <span class="nt">-u</span> mgmt_agent <span class="nb">test</span> <span class="nt">-r</span> <span class="s2">"</span><span class="nv">$log_dir</span><span class="s2">"</span>
  <span class="nb">sudo</span> <span class="nt">-u</span> mgmt_agent <span class="nb">test</span> <span class="nt">-x</span> <span class="s2">"</span><span class="nv">$log_dir</span><span class="s2">"</span>
<span class="k">done</span>
</code></pre></div></div>

<p>After confirming the actual filenames, read one line from a representative database alert log and listener log as <code class="language-plaintext highlighter-rouge">mgmt_agent</code>. Successful output proves file-level read access without relying on root privileges:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nv">database_alert_log</span><span class="o">=</span>/u02/app/oracle/diag/rdbms/oradbrac/ORADBRAC2/trace/alert_ORADBRAC2.log
<span class="nv">listener_log</span><span class="o">=</span>/u01/app/grid/diag/tnslsnr/host-vak332/listener/trace/listener.log
<span class="nb">sudo</span> <span class="nt">-u</span> mgmt_agent <span class="nb">tail</span> <span class="nt">-n</span> 1 <span class="s2">"</span><span class="nv">$database_alert_log</span><span class="s2">"</span>
<span class="nb">sudo</span> <span class="nt">-u</span> mgmt_agent <span class="nb">tail</span> <span class="nt">-n</span> 1 <span class="s2">"</span><span class="nv">$listener_log</span><span class="s2">"</span>
</code></pre></div></div>

<p>Repeat the ACL and validation steps on every database node using that node’s discovered paths. Recheck access after database or Grid homes change and after log rotation. The default ACL helps future files inherit access, while the recursive ACL covers files and directories that already exist.</p>

<h4 id="create-the-oradbrac1-oracle-database-instance-entity">Create the <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> Oracle Database Instance entity</h4>

<p>Create a separate entity for each database instance so that the Oracle-defined alert-log source can resolve the correct paths and use the Management Agent on the node that owns those files. This example creates <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> on <code class="language-plaintext highlighter-rouge">host-vak331</code>; the earlier <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> ACL path is a separate node-specific example.</p>

<ol>
  <li>Open <strong>Observability &amp; Management → Log Analytics → Administration → Entities</strong>, select the entity compartment, and click <strong>Create</strong>.</li>
  <li>Enter <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> for <strong>Name</strong> and select <strong>Oracle Database Instance</strong> for <strong>Entity Type</strong>.</li>
  <li>Select the Management Agent compartment and <code class="language-plaintext highlighter-rouge">odb-aws-host-vak331</code> as the <strong>Management Agent</strong>.</li>
  <li>Enter the values discovered on that database node. The captured configuration uses the following properties:</li>
</ol>

<table>
  <thead>
    <tr>
      <th>Entity property</th>
      <th>Example value</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">DIAGNOSTIC_DEST</code></td>
      <td><code class="language-plaintext highlighter-rouge">/u02/app/oracle/diag</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">adr_home</code></td>
      <td><code class="language-plaintext highlighter-rouge">/u02/app/oracle/diag</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">host_name</code></td>
      <td><code class="language-plaintext highlighter-rouge">host-vak331</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">oracle_home</code></td>
      <td><code class="language-plaintext highlighter-rouge">/u02/app/oracle/product/19.0.0.0/dbhome_2</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">port</code></td>
      <td><code class="language-plaintext highlighter-rouge">1521</code></td>
    </tr>
  </tbody>
</table>

<ol>
  <li>Click <strong>Save Changes</strong>, reopen the entity, and confirm that its type, agent, and properties match the target instance. Oracle-defined file sources use entity properties in their include patterns, so missing or incorrect property values can prevent source association or file matching. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/database-instance-monitoring.html">Create the database entity</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/create-log-source.html">entity properties in source patterns</a></li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oradbrac1-oracle-database-instance-entity-redacted.png" alt="Public-safe OCI Log Analytics Edit Entity view for the ORADBRAC1 Oracle Database Instance and its node-specific Management Agent properties." class="align-center" /></p>

<p><em>Figure 7. Saved <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> entity used for Oracle Database alert-log collection on <code class="language-plaintext highlighter-rouge">host-vak331</code>. The entity type is Oracle Database Instance, the associated agent is <code class="language-plaintext highlighter-rouge">odb-aws-host-vak331</code>, and the node-specific diagnostic properties are populated. The compartment identifier and entity OCID were replaced for publication.</em></p>

<h4 id="create-the-oradbrac2-oracle-database-instance-entity">Create the <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> Oracle Database Instance entity</h4>

<p>Repeat the entity creation for the second database instance, using the Management Agent and Oracle home on <code class="language-plaintext highlighter-rouge">host-vak332</code>:</p>

<table>
  <thead>
    <tr>
      <th>Entity setting</th>
      <th>Example value</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Name</td>
      <td><code class="language-plaintext highlighter-rouge">ORADBRAC2</code></td>
    </tr>
    <tr>
      <td>Entity Type</td>
      <td><code class="language-plaintext highlighter-rouge">Oracle Database Instance</code></td>
    </tr>
    <tr>
      <td>Management Agent</td>
      <td><code class="language-plaintext highlighter-rouge">odb-aws-host-vak332</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">DIAGNOSTIC_DEST</code></td>
      <td><code class="language-plaintext highlighter-rouge">/u02/app/oracle/diag</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">adr_home</code></td>
      <td><code class="language-plaintext highlighter-rouge">/u02/app/oracle/diag</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">host_name</code></td>
      <td><code class="language-plaintext highlighter-rouge">host-vak332</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">oracle_home</code></td>
      <td><code class="language-plaintext highlighter-rouge">/u02/app/oracle/product/19.0.0.0/dbhome_1</code></td>
    </tr>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">port</code></td>
      <td><code class="language-plaintext highlighter-rouge">1521</code></td>
    </tr>
  </tbody>
</table>

<p>Review the values against the paths discovered on <code class="language-plaintext highlighter-rouge">host-vak332</code>, then click <strong>Create Entity</strong>. After creation, reopen <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> and confirm that the selected agent and properties were saved before associating a source.</p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oradbrac2-oracle-database-instance-entity-redacted.png" alt="Public-safe OCI Log Analytics Create Entity view for the ORADBRAC2 Oracle Database Instance and its node-specific Management Agent properties." class="align-center" /></p>

<p><em>Figure 8. Creation of the <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> entity for alert-log collection on <code class="language-plaintext highlighter-rouge">host-vak332</code>. The entity uses <code class="language-plaintext highlighter-rouge">odb-aws-host-vak332</code>, the node’s <code class="language-plaintext highlighter-rouge">/u02</code> diagnostic paths, <code class="language-plaintext highlighter-rouge">dbhome_1</code>, and port <code class="language-plaintext highlighter-rouge">1521</code>. The compartment hierarchy and private DNS suffixes were replaced for publication.</em></p>

<h4 id="associate-the-database-instances-and-log-sources-with-add-data">Associate the database instances and log sources with Add Data</h4>

<p>Use the <strong>Add Data</strong> wizard to create the source-entity associations for both RAC instances in one workflow. Oracle documents this wizard as the continuous-collection path for selecting entities, selecting sources, assigning a log group, and validating the association. <a href="https://docs.oracle.com/en/cloud/paas/log-analytics/laagt/">Set up continuous log collection</a></p>

<ol>
  <li>Open <strong>Observability &amp; Management → Log Analytics → Administration → Overview</strong>, select the compartment that contains the database entities, and click <strong>Add Data</strong>.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/add-data-administration-overview-redacted.png" alt="Public-safe OCI Log Analytics Administration overview showing the Add Data entry point." class="align-center" /></p>

<p><em>Figure 9. Start the source-association workflow from Add Data. The compartment name and hierarchy were replaced for publication.</em></p>

<ol>
  <li>Expand <strong>Monitor with management agent</strong> and select <strong>Custom Selection</strong>.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/add-data-custom-selection.png" alt="OCI Log Analytics Add Data page with Custom Selection under Monitor with management agent." class="align-center" /></p>

<p><em>Figure 10. Custom Selection opens the Configure Agent-based Log Collection workflow for explicitly selected entities and sources.</em></p>

<ol>
  <li>On <strong>Select Entities</strong>, filter to <strong>Oracle Database Instance</strong> when the fleet contains many entity types. Select <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> and <code class="language-plaintext highlighter-rouge">ORADBRAC2</code>, confirm that each row resolves to its node-local Management Agent, and click <strong>Next</strong>.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/add-data-select-database-entities-redacted.png" alt="Public-safe Configure Agent-based Log Collection page with ORADBRAC1 and ORADBRAC2 selected." class="align-center" /></p>

<p><em>Figure 11. Both RAC instance entities are selected. Private DNS suffixes and Management Agent OCID fragments were replaced with example hostnames and the corresponding agent display names.</em></p>

<ol>
  <li>On <strong>Select Sources</strong>, select the Oracle-defined <strong>Database Alert Logs</strong> file source. That source is the baseline for this walkthrough. The captured environment also selected <strong>Database Attention Logs</strong> and <strong>Database Incident Dump Files</strong>; add those only when the operating requirement and expected ingestion volume justify them.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/add-data-select-log-sources.png" alt="Configure Agent-based Log Collection source selection showing Database Alert Logs and two optional diagnostic sources." class="align-center" /></p>

<p><em>Figure 12. <code class="language-plaintext highlighter-rouge">Database Alert Logs</code> is the required source for this walkthrough. <code class="language-plaintext highlighter-rouge">Database Attention Logs</code> and <code class="language-plaintext highlighter-rouge">Database Incident Dump Files</code> are optional selections visible in the captured configuration.</em></p>

<ol>
  <li>In <strong>Log Group Compartment</strong>, choose the intended destination compartment. Select an existing log group, or click <strong>Create New</strong>. This example creates <code class="language-plaintext highlighter-rouge">Multicloud_OracleDB_LogGroup</code> with the description <code class="language-plaintext highlighter-rouge">OracleDB@AWS</code>.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/add-data-create-log-group-redacted.png" alt="Public-safe Create Log Group dialog for the Oracle Database at AWS collection workflow." class="align-center" /></p>

<p><em>Figure 13. Creation of the <code class="language-plaintext highlighter-rouge">Multicloud_OracleDB_LogGroup</code> destination. The compartment identifier and hierarchy were replaced for publication.</em></p>

<ol>
  <li>Confirm that the new log group is selected, review the entity and source choices, and click <strong>Validate and configure log collection</strong>.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/add-data-validate-log-collection-redacted.png" alt="Public-safe Configure Agent-based Log Collection page ready to validate and configure the selected associations." class="align-center" /></p>

<p><em>Figure 14. Pre-submit configuration with the destination log group selected. This screen does not prove that validation or association creation completed.</em></p>

<ol>
  <li>Wait for the wizard to display its success confirmation. Open the activity status or source name and verify that the associations for both entities completed successfully. Then use <strong>Take me to Log Explorer</strong> or open Log Explorer separately. The supplied screenshot set stops at the pre-submit screen in Figure 14, so retain the actual confirmation or work-request result as deployment evidence before publication or rollout acceptance.</li>
</ol>

<p>If validation fails, do not repeatedly submit the same configuration. Inspect <strong>Agent Collection Warnings</strong>, verify that the entity properties resolve to the intended alert-log paths, test file access as <code class="language-plaintext highlighter-rouge">mgmt_agent</code>, confirm that the Log Analytics plug-in is running, and verify the dynamic group and IAM policy below.</p>

<h4 id="verify-the-management-agent-dynamic-group-and-upload-policy">Verify the Management Agent dynamic group and upload policy</h4>

<p>The <strong>Set Up Ingestion</strong> workflow can create some IAM resources automatically, but verify the result rather than assuming that it selected the intended scope. In <strong>Identity &amp; Security → Dynamic Groups</strong>, open <code class="language-plaintext highlighter-rouge">exadb-mgmtagent-dg</code> and confirm that its matching rule covers the Management Agent resources in the Management Agent compartment:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>ALL {resource.type='managementagent', resource.compartment.id='&lt;management-agent-compartment-OCID&gt;'}
</code></pre></div></div>

<p>Avoid the broader <code class="language-plaintext highlighter-rouge">ALL {resource.type='managementagent'}</code> rule unless every Management Agent in the tenancy is intentionally part of the collection identity. If the dynamic group belongs to an identity domain, include the domain name in policy subjects as Oracle documents. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/allow-continuous-log-collection-using-management-agents.html">Continuous collection IAM</a></p>

<p>Oracle’s <strong>Allow continuous log collection using management agent dynamic groups</strong> template contains the metrics and upload permissions. This article’s policy collection also includes tenancy-level <code class="language-plaintext highlighter-rouge">READ USERS</code>, which appears in Oracle’s automatic agent-ingestion policy example. Select the compartment that contains the target Log Analytics resources for the compartment-scoped grants:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>ALLOW DYNAMIC-GROUP &lt;identity-domain&gt;/exadb-mgmtagent-dg TO USE METRICS IN COMPARTMENT &lt;log-analytics-compartment&gt;
ALLOW DYNAMIC-GROUP &lt;identity-domain&gt;/exadb-mgmtagent-dg TO {LOG_ANALYTICS_LOG_GROUP_UPLOAD_LOGS} IN COMPARTMENT &lt;log-analytics-compartment&gt;
ALLOW DYNAMIC-GROUP &lt;identity-domain&gt;/exadb-mgmtagent-dg TO READ USERS IN TENANCY
</code></pre></div></div>

<p>Omit <code class="language-plaintext highlighter-rouge">&lt;identity-domain&gt;/</code> when the subject syntax for the tenancy does not require it. The captured environment uses the valid but broader <code class="language-plaintext highlighter-rouge">IN TENANCY</code> form shown in Figure 15. Prefer the narrowest compartment scope that covers the metrics and upload operations; <code class="language-plaintext highlighter-rouge">READ USERS</code> remains tenancy-scoped. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/oracle-defined-policy-templates-common-use-cases.html">Oracle-defined policy templates</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/security-monitoring-solution.html">automatic-ingestion policy example</a></p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/management-agent-dynamic-group-policy-redacted.png" alt="Public-safe OCI IAM policy editor showing only the Management Agent continuous log collection permissions." class="align-center" /></p>

<p><em>Figure 15. The captured tenancy-wide policy grants <code class="language-plaintext highlighter-rouge">exadb-mgmtagent-dg</code> permission to emit metrics and upload logs to Log Analytics log groups. The additional tenancy-scoped <code class="language-plaintext highlighter-rouge">READ USERS</code> statement is included in the policy collection shown in the text above. The tenancy OCID, cross-tenancy statements, and unrelated policy lines were removed from the publication copy.</em></p>

<p>Complete the association check in Log Analytics:</p>

<ol>
  <li>Reopen <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> and <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> under <strong>Administration → Entities</strong> and confirm that <strong>Database Alert Logs</strong> appears under <strong>Associated Sources</strong>.</li>
  <li>Inspect the source’s resolved include patterns and exclusions. Confirm that they resolve to the <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> alert-log location on <code class="language-plaintext highlighter-rouge">host-vak331</code> and the <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> alert-log location on <code class="language-plaintext highlighter-rouge">host-vak332</code>.</li>
  <li>Inspect <strong>Agent Collection Warnings</strong> and correct entity-property, file-matching, IAM, or <code class="language-plaintext highlighter-rouge">mgmt_agent</code> access problems before proceeding.</li>
  <li>Open <strong>Log Explorer</strong>, select <code class="language-plaintext highlighter-rouge">Multicloud_OracleDB_LogGroup</code> and <strong>Database Alert Logs</strong>, and verify a recent record from both <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> and <code class="language-plaintext highlighter-rouge">ORADBRAC2</code>, including each record’s timestamp, message, and extracted fields.</li>
</ol>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/log-explorer-oradbrac1-database-alert-logs.png" alt="OCI Log Analytics Log Explorer showing Database Alert Logs collected for the ORADBRAC1 Oracle Database Instance entity." class="align-center" /></p>

<p><em>Figure 16. Entity-scoped collection evidence for <code class="language-plaintext highlighter-rouge">ORADBRAC1</code>. Log Explorer shows 428 <code class="language-plaintext highlighter-rouge">Database Alert Logs</code> records in the selected 14-day window, including parsed entity, entity type, source, priority, and label context. This validates records for this entity and time range; repeat the check for <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> and after log rotation.</em></p>

<p>The <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/ingest-application-infrastructure-database-other-generic-logs.html">file collection workflow</a> explains source patterns and entity associations. Begin with one alert representation; collecting both text and XML copies can duplicate an event in downstream counts. Extend to traces or incident dumps when their diagnostic value justifies the volume.</p>

<p>For rollout acceptance, capture the expected VM/entity/source list alongside agent status, collection warnings, and a recent record from each enabled source. A source with no recent records may simply be quiet. Compare collection status and file activity before concluding that it is either healthy or broken.</p>

<h3 id="optional-extension-exawatcher-diagnostics">Optional extension: ExaWatcher diagnostics</h3>

<p>ExaWatcher can add guest operating-system context to a database investigation, but its collection and parsing workflow is outside this article’s database and GI focus. For a worked implementation, see Jerry Russell’s <a href="https://blogs.oracle.com/observability/advanced-log-parser-exawatcher-vmstat-output">Creating an Advanced Log Parser in Oracle Log Analytics for Exawatcher VMStat Output</a>. It demonstrates parser functions, source data filters, Management Agent association, on-demand testing, and visualizations for ExaWatcher VMStat records.</p>

<p>Before applying that pattern, validate the ExaWatcher file location, agent permissions, timestamp handling, rotation behavior, and VMStat semantics on the target guest image. Oracle’s <a href="https://docs.oracle.com/en/engineered-systems/exadata-database-machine/sagug/exawatcher.html">ExaWatcher documentation</a> provides the utility background and operational guidance.</p>

<h2 id="build-fleet-dashboards-and-investigation-queries">Build fleet dashboards and investigation queries</h2>

<p>Start with the <strong>Oracle Database Alert</strong> dashboard, which includes views of database alert trends and errors. Duplicate the Oracle-defined dashboard to customize it, then add your guest-host and GI views. Configure common time and scope filters so the panels describe the same incident window. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/oracle-database-alert.html">Database Alert dashboard</a>, <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/oracle-defined-dashboards-logging-analytics.html">Dashboard customization</a></p>

<h3 id="open-the-oracle-database-alert-dashboard">Open the Oracle Database Alert dashboard</h3>

<p>Open <strong>Log Analytics → Dashboards</strong>, select the intended compartment, and search for <code class="language-plaintext highlighter-rouge">oracle database</code>. The <strong>Created by</strong> column identifies the Oracle-defined dashboards. Open <strong>Oracle Database Alert</strong>.</p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/dashboards-oracle-database-list-redacted.png" alt="Public-safe OCI Log Analytics Dashboards listing filtered for Oracle Database dashboards." class="align-center" /></p>

<p><em>Figure 17. Oracle-defined database dashboards available in Log Analytics. The compartment name was replaced for publication.</em></p>

<p>Oracle-defined dashboards cannot be edited directly. Duplicate <strong>Oracle Database Alert</strong> before adding fleet-specific widgets, changing its filters, or replacing its saved searches. Apply the log-group compartment, region, entity compartment, database entities, and time range that belong to the ExaDB-D fleet.</p>

<h3 id="build-the-oracle-database-alert-error-summary-saved-search">Build the Oracle Database Alert Error Summary saved search</h3>

<p>Open the <strong>Error Summary</strong> widget in Log Explorer or create a saved search using this query:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>'Log Source' = 'Database Alert Logs'
| link 'Error ID', Entity
| lookup table = 'ORA Error Messages' select errmsg as 'Error Message'
  using 'Error ID' = errid
| stats unique('Problem Priority') as Severity
| eventstats ifnull(sum(Count), 0) as 'Total Errors',
  unique(Entity) as 'Database(s) with issues',
  ifnull(distinctcount(Entity), 0) as 'Number of database(s) with issues'
| fields target = ui -'Total Errors', -'Number of database(s) with issues'
</code></pre></div></div>

<p>The <code class="language-plaintext highlighter-rouge">link</code> command groups records by error ID and database entity. The lookup enriches matching error IDs with the <code class="language-plaintext highlighter-rouge">ORA Error Messages</code> table, while <code class="language-plaintext highlighter-rouge">eventstats</code> adds totals across the result. The final <code class="language-plaintext highlighter-rouge">fields target = ui</code> clause removes the two helper totals from the Link groups table without discarding the backend fields. If <strong>Error Message</strong> is blank, confirm that the lookup contains the parsed <code class="language-plaintext highlighter-rouge">errid</code>; keep the parsed Error ID and original records as the primary evidence.</p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oracle-database-alert-error-summary-query.png" alt="Oracle Database Alert Error Summary saved search showing an ORA-7445 group, two records, and one database with issues." class="align-center" /></p>

<p><em>Figure 18. The saved search groups two <code class="language-plaintext highlighter-rouge">ORA-7445</code> records for <code class="language-plaintext highlighter-rouge">oradbrac1</code>, marks the group High severity, and reports one database with issues in the selected 14-day window.</em></p>

<p>Save the search with a relative time range when the widget should stay current, and add it to the duplicated dashboard. A fixed time range preserves one investigation window instead. Oracle documents saved searches as reusable dashboard widgets and supports duplicating Oracle-defined searches before customization. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/save-share-log-searches.html">Save and share log searches</a></p>

<h3 id="drill-into-the-ora-7445-records">Drill into the ORA-7445 records</h3>

<p>In Figure 18, click the linked count <code class="language-plaintext highlighter-rouge">2</code> for the <code class="language-plaintext highlighter-rouge">ORA-7445</code> row. Log Analytics opens the two records in the Link collection and narrows the time range to their interval.</p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oracle-database-alert-ora-7445-drilldown-redacted.png" alt="Public-safe Log Explorer drilldown showing the two records linked to the ORA-7445 error-summary group." class="align-center" /></p>

<p><em>Figure 19. Record-level drilldown from the <code class="language-plaintext highlighter-rouge">ORA-7445</code> group. The Link collection identifier and patch inventory were replaced for publication; the entity, source, severity, label, timestamps, and two-record sequence remain visible.</em></p>

<p>Use this drilldown to inspect the alert entry, trace-file or incident references, surrounding database messages, and records from GI, ASM, and listener sources in the same window. The two linked records establish temporal context; they do not by themselves identify the ORA-7445 root cause. Preserve the original alert and trace evidence for the database diagnostic or Oracle Support workflow.</p>

<h3 id="add-ai-powered-assistance-with-loganai">Add AI-powered assistance with LoganAI</h3>

<p>LoganAI is the generative AI capability in Log Analytics. It can summarize individual records, groups, clusters, and charts; explain complex results; and propose context-aware follow-up questions within the Log Analytics workflow. It uses <a href="https://docs.oracle.com/en-us/iaas/Content/generative-ai/home.htm">OCI Generative AI</a> in the tenancy. Oracle cautions that AI-generated responses can be incomplete or inaccurate, so validate every explanation against the original records before making an operational decision. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/use-loganai.html">Use LoganAI</a></p>

<p>To enable it for a region, open <strong>Administration → Service Details → Configure LoganAI settings</strong>. Select the OCI Generative AI region and compartment, choose the model behavior, review and accept the required model licenses, select the user license-acceptance policy, and configure the displayed IAM permissions. Run <strong>Test</strong> under <strong>Validate settings</strong> before clicking <strong>Update LoganAI settings</strong>. LoganAI availability is regional, the selected OCI Generative AI service can add usage charges, and logs can be sent from the Log Analytics region to the selected Generative AI region. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/enable-loganai.html">Enable LoganAI</a></p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/loganai-settings-redacted.png" alt="Public-safe Configure LoganAI settings dialog showing regional, compartment, model, license, and IAM choices." class="align-center" /></p>

<p><em>Figure 20. Pre-update LoganAI configuration. The service namespace was replaced for publication. The background status remains <code class="language-plaintext highlighter-rouge">Disabled</code>; this screen documents the intended settings and does not prove that validation or activation succeeded.</em></p>

<p>After activation, use <strong>Explain</strong> on the selected ORA-7445 group or its surrounding chart to request a concise summary and investigation questions. Check every claim against the records, database trace files, and corroborating sources before adding it to the incident timeline or RCA.</p>

<h3 id="use-a-consolidated-database-alert-view">Use a consolidated database-alert view</h3>

<p>The Oracle-defined dashboard brings the alert summary, new issues and outliers, log trends, ORA and TNS distributions, corrupt-block results, database distribution, severity, and error trends into one view. Set the time and scope filters before interpreting its totals.</p>

<p><img src="/images/posts/2026-09-11-oci-log-analytics-oracle-database-at-aws/oracle-database-alert-dashboard.png" alt="Oracle Database Alert dashboard with error, issue, trend, ORA, TNS, database, and severity widgets." class="align-center" /></p>

<p><em>Figure 21. Oracle Database Alert dashboard populated in a sample environment. Use its widget layout as the starting point, then scope the duplicated dashboard to the ExaDB-D log group and database entities. The displayed sample counts and entity names are not results from the <code class="language-plaintext highlighter-rouge">ORADBRAC1</code> and <code class="language-plaintext highlighter-rouge">ORADBRAC2</code> walkthrough.</em></p>

<p>For the multicloud operations view, extend the duplicate with collection coverage, listener failures, and GI and ASM events. Keep the same time, log-group, and entity scope across widgets so operators can move from a fleet-level symptom to the contributing database and infrastructure records.</p>

<h3 id="turn-the-dashboard-into-an-operating-routine">Turn the dashboard into an operating routine</h3>

<p>For the connection-failure scenario, use the database and listener panels to identify affected instances, then inspect GI and ASM records in the same window. Ask LoganAI to summarize the selected evidence and suggest the next investigation step; verify its response against the original records before recording an RCA conclusion.</p>

<p>Save useful searches as dashboard widgets, validate that their filters apply to every intended source, and document what each count means. Once the query and threshold have been tested, selected searches can feed scheduled detection and alerting workflows. <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/create-schedule-run-saved-search.html">Scheduled searches</a></p>

<p>Track the collection pipeline as part of the same routine. Review agent health, warnings, new VM onboarding, and log volume. Retain frequently used diagnostics for the required investigation period, and add high-volume traces with a clear use case. These decisions keep the fleet dashboard useful as the environment changes.</p>

<h2 id="conclusion">Conclusion</h2>

<p>OCI Log Analytics gives Oracle Database@AWS ExaDB-D and ExaC@C operations a common way to work with distributed diagnostic evidence. Its value comes from connecting Oracle-aware source configuration with repeatable investigation: identify an affected instance, follow the related database and GI messages, inspect guest-host evidence, and share a query that another operator can reproduce.</p>

<p>Begin with one VM cluster. Validate the ZIP installation, environment-specific network path, source associations, file rotation, timestamps, and extracted fields, then expand the validated database and GI collection pattern across the Oracle Database@AWS or ExaC@C fleet.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://www.ateam-oracle.com/maximize-visibillity-collecting-and-analyzing-logs-for-multiple-oracle-databases-using-oci-logging-analytics">Maximizing Visibility: Collecting and Analyzing Logs from Oracle Databases using OCI Logging Analytics</a></li>
  <li><a href="https://blogs.oracle.com/observability/advanced-log-parser-exawatcher-vmstat-output">Creating an Advanced Log Parser in Oracle Log Analytics for Exawatcher VMStat Output</a></li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="OCI Log Analytics" /><category term="Oracle Database@AWS" /><category term="Exadata" /><category term="Exadata Cloud@Customer" /><category term="Multicloud" /><category term="Management Agent" /><category term="Observability and Monitoring" /><summary type="html"><![CDATA[Centralize database and Grid Infrastructure diagnostics from Oracle Database@AWS ExaDB-D and Exadata Database Service on Cloud@Customer with OCI Log Analytics.]]></summary></entry><entry><title type="html">OCI AI Ops framework for Cloud Operation Autonomous Resilience</title><link href="https://royce-fu.com/blog/oci-ai-ops-framework-for-cloud-operation-autonomous-resilience/" rel="alternate" type="text/html" title="OCI AI Ops framework for Cloud Operation Autonomous Resilience" /><published>2026-06-24T00:00:00+00:00</published><updated>2026-09-08T13:34:00+00:00</updated><id>https://royce-fu.com/blog/oci-ai-ops-framework-for-cloud-operation-autonomous-resilience</id><content type="html" xml:base="https://royce-fu.com/blog/oci-ai-ops-framework-for-cloud-operation-autonomous-resilience/"><![CDATA[<h1 id="oci-ai-ops-framework-for-cloud-operation-autonomous-resilience">OCI AI Ops framework for Cloud Operation Autonomous Resilience</h1>

<p>In the legacy operations model, a pager sounds, a human engineer joins a bridge, and the first critical minutes are spent collecting context. Which system changed? Which database slowed down? Which application tier is producing errors? Which metric crossed a threshold? Which log message matters? Which business process is impacted?
That model worked when environments were smaller, changes were slower, and operational knowledge could fit inside a few expert teams. It becomes fragile in a cloud operating model where applications are distributed, infrastructure is elastic, data platforms are mission critical, and signals arrive from many layers at the same time.</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/sVucbDzhrbg" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/oci-ai-ops-framework-for-cloud-operation-autonomous-resilience.png" alt="OCI AI Ops framework for Cloud Operation Autonomous Resilience — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>DevOps changed the industry by connecting development and operations: if you build it, you run it. But AI transformation is changing the operating model again. AI agents can now assist with code generation, application development, testing, and release engineering. The next logical step is AI Ops: using AI to operate the application, the infrastructure, the database estate, and the cloud platform itself.</p>

<p>The goal is not to remove people from operations. The goal is to move human experts out of repetitive correlation work and into architecture, governance, exception handling, and business decision-making. Autonomous resilience is the target state: systems that can sense, diagnose, plan, remediate, verify, and learn with appropriate human supervision.</p>

<h2 id="what-ai-ops-means">What AI Ops means</h2>

<p>AI Ops is the application of AI, automation, observability, and operational governance to run modern digital systems more intelligently. It is not just a chatbot attached to monitoring data. It is not a folder of scripts triggered by alerts. It is an architecture where telemetry, policies, agents, evaluators, workflows, and incident processes work together.</p>

<p>In a mature AI Ops model, the system can:</p>

<ul>
  <li>Detect a performance, availability, capacity, security, or data-platform anomaly.</li>
  <li>Correlate signals across metrics, logs, events, traces, SQL data, and configuration context.</li>
  <li>Determine whether the event is noise, a real incident, a capacity risk, or an emerging business-impacting condition.</li>
  <li>Generate a remediation plan that explains both the technical action and the expected outcome.</li>
  <li>Validate the plan before execution through an evaluator or policy guardrail.</li>
  <li>Execute the approved remediation through controlled OCI services and APIs.</li>
  <li>Verify the post-execution result against the desired state.</li>
  <li>Produce an incident summary, problem record, and root cause analysis for future learning.</li>
</ul>

<p>The key shift is that operations becomes an agentic loop, not a manual search exercise.</p>

<p><img src="/images/posts/2026-06-24-aiops-framework/oci-aiops-framework-autonomous-resilience.png" alt="OCI AI Ops Framework Architecture" />
<em>Figure 1: OCI AI Ops framework for autonomous resilience, from observability data foundation to agentic remediation and problem management.</em></p>

<h2 id="observability-is-the-data-foundation">Observability is the data foundation</h2>

<p>AI Ops begins with observability. An agent cannot diagnose what it cannot perceive. A framework that only sees CPU utilization cannot understand user experience. A framework that only sees logs cannot understand capacity. A framework that ignores database state cannot make reliable decisions for enterprise workloads.</p>

<p>The data foundation must include several classes of operational evidence:</p>

<ul>
  <li><strong>Metrics</strong>: numerical time-series data such as CPU, memory, storage, latency, queue depth, throughput, and error rate.</li>
  <li><strong>Logs</strong>: detailed records from applications, infrastructure, databases, middleware, security systems, and integration platforms.</li>
  <li><strong>Events</strong>: discrete changes in cloud resources, lifecycle state, configuration, alarms, and operational activity.</li>
  <li><strong>Traces</strong>: end-to-end transaction paths across applications, APIs, services, and dependencies.</li>
  <li><strong>SQL data</strong>: database-level state, workload, waits, sessions, execution patterns, backup posture, capacity, and performance signals.</li>
  <li><strong>Topology and resource context</strong>: relationships across applications, compute, databases, networks, storage, tags, compartments, and business services.</li>
</ul>

<p>For enterprise customers, this foundation is not only about troubleshooting. It is how the business understands operational risk, service performance, cost exposure, capacity pressure, and resilience posture.</p>

<h2 id="oci-observability-and-management-as-the-ai-ops-service-fabric">OCI Observability and Management as the AI Ops service fabric</h2>

<p>OCI provides a strong set of Observability and Management services that can become the service fabric for an AI Ops framework. Each service contributes a different kind of operational signal or control point.</p>

<table>
  <thead>
    <tr>
      <th>OCI capability</th>
      <th>Role in the AI Ops framework</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/Monitoring/home.htm">OCI Monitoring</a></strong></td>
      <td>Captures infrastructure and service metrics, evaluates alarms, and provides the primary threshold and anomaly signal for many operational workflows.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/Logging/home.htm">OCI Logging</a> and <a href="https://docs.oracle.com/en-us/iaas/log-analytics/home.htm">Oracle Log Analytics</a></strong></td>
      <td>Centralize logs, enrich and parse operational records, support pattern detection, and provide the evidence base for root cause analysis.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/application-performance-monitoring.html">OCI Application Performance Monitoring</a></strong></td>
      <td>Captures traces, spans, user experience, service dependencies, and application latency so the agent can reason about business transaction impact.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/database-management/home.htm">OCI Database Management</a></strong></td>
      <td>Provides database health, performance, fleet management, SQL diagnostics, sessions, wait events, and operational actions for database-centric workloads.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/operations-insights/doc/operations-insights.html">OCI Ops Insights</a></strong></td>
      <td>Supports capacity planning, resource utilization analysis, SQL insights, database performance trends, and long-horizon operational forecasting.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/resource-analytics/home.htm">OCI Resource Analytics</a></strong></td>
      <td>Maintains a near-real-time inventory of OCI resources, relationships, and configuration metadata. Its relational model, property graphs, and Graph Studio support topology analysis, dependency exploration, governance, and troubleshooting.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/Events/Concepts/eventsoverview.htm">OCI Events</a></strong></td>
      <td>Detects resource changes and state transitions, then routes event-driven workflows to downstream automation.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/Streaming/Concepts/streamingoverview.htm">OCI Streaming</a></strong></td>
      <td>Provides a scalable event and telemetry pipeline for decoupling producers, agent processors, and downstream consumers.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/Functions/home.htm">OCI Functions</a></strong></td>
      <td>Runs serverless detection, enrichment, planning, evaluation, remediation, and verification logic.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/APIGateway/">OCI API Gateway</a> and <a href="https://docs.oracle.com/en/cloud/paas/application-integration/integrations-user/integrations.html">Oracle Integration</a></strong></td>
      <td>Expose and orchestrate controlled workflow entry points, integrate with enterprise systems, and coordinate multi-step processes.</td>
    </tr>
  </tbody>
</table>

<p>When these services are connected into an architecture, they do more than generate dashboards. They create an operational decision fabric. Customers can use that fabric to understand which systems are at risk, which capacity trends require investment, which incidents have the highest business impact, and which remediations can be safely automated.</p>

<h2 id="the-database-native-ai-and-context-plane">The database-native AI and context plane</h2>

<p>Observability tells the agent what is happening. Autonomous operations also require a governed context plane that can explain what the signals mean, how resources are related, which prior knowledge applies, and what actions are available. This is where Oracle AI Database and its AI and machine-learning capabilities extend the OCI Observability and Management service fabric.</p>

<p>The design should not force every source artifact into one storage system. Large log archives, documents, images, video, runbooks, and incident attachments can remain in OCI Object Storage or an enterprise data lake. Oracle Autonomous AI Lakehouse can query data in object storage through external and hybrid-partitioned tables. Oracle AI Database can then hold the structured operational facts, document chunks, embeddings, source references, resource identities, and relationships required for governed retrieval and analysis.</p>

<table>
  <thead>
    <tr>
      <th>Oracle AI and data capability</th>
      <th>Role in the AI Ops framework</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en/solutions/data-platform-lakehouse/">OCI Object Storage and Oracle Autonomous AI Lakehouse</a></strong></td>
      <td>Provide the durable data-lake layer for unstructured evidence and historical operational data while enabling governed SQL access to data that remains in object storage.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/Content/generative-ai/overview.htm">OCI Generative AI</a></strong></td>
      <td>Provides OCI-managed foundation models and enterprise agent capabilities for chat, embeddings, rerank, OpenAI-compatible APIs, agent tools, vector stores, memory, and hosted agentic applications. In this framework, it is a governed model and agent-service option rather than the system of record for operational evidence.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en/database/oracle/oracle-database/26/vecse/overview-ai-vector-search.html">Oracle AI Vector Search</a></strong></td>
      <td>Stores vector embeddings alongside relational, JSON, spatial, graph, and operational metadata. Semantic and hybrid retrieval give RAG workflows access to relevant runbooks, incident records, change history, logs, and engineering knowledge.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en/database/oracle/oracle-database/26/prvai/oracle-private-ai-services-container.html">Oracle Private AI Services Container</a></strong></td>
      <td>Runs private embedding, reranking, text-classification, and LLM inference services in a customer-controlled environment. It can also offload vector-index creation to GPU infrastructure instead of consuming database compute.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/autonomous-database-serverless/doc/getting-started-select-ai-agent.html">Select AI Agent</a></strong></td>
      <td>Provides database-native agent capabilities for creating and coordinating tools, tasks, agents, and teams. Its built-in tools can support SQL, RAG, web search, and notifications, while <code class="language-plaintext highlighter-rouge">DBMS_CLOUD_AI_AGENT</code> provides the management and orchestration interface.</td>
    </tr>
    <tr>
      <td><strong><a href="https://www.oracle.com/database/agent-factory/">Oracle AI Database Private Agent Factory</a></strong></td>
      <td>Provides a deployable, governed environment for building, testing, and operating agents that use Oracle Database, enterprise content, APIs, Select AI Agent, approved model providers, and MCP tools.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en-us/iaas/autonomous-database-serverless/doc/mcp-server.html">Autonomous AI Database MCP Server</a></strong></td>
      <td>Provides a managed, per-database MCP endpoint that exposes approved Select AI Agent tools to MCP-compatible applications while retaining database authentication, authorization, auditing, and least-privilege controls.</td>
    </tr>
    <tr>
      <td><strong><a href="https://docs.oracle.com/en/database/oracle/machine-learning/data-science-agent/index.html">Oracle Machine Learning Data Science Agent</a></strong></td>
      <td>Adds conversational data profiling, data-quality and outlier analysis, statistical exploration, model training, evaluation, and inference through Oracle Machine Learning UI. It complements deterministic detection with human-supervised analytical investigation.</td>
    </tr>
  </tbody>
</table>

<p>These are not separate AI islands. Together they form a converged context and agent platform:</p>

<p><img src="/images/posts/2026-06-24-aiops-framework/oci-aiops-database-context-plane.png" alt="Oracle AI Database context plane and Private Agent Factory connecting operational telemetry, resource topology, and enterprise knowledge to evaluated operational action" class="align-center" />
<em>Figure 2: The Oracle AI Database context plane grounds Private Agent Factory workflows in operational evidence, enterprise knowledge, resource relationships, and governed retrieval.</em></p>

<p>The context plane grounds the workflow in governed operational evidence. Oracle AI Database Private Agent Factory operationalizes that context by providing the environment to build, test, govern, deploy, and operate Select AI Agent and approved analytical workflows.</p>

<h3 id="how-private-agent-factory-and-the-oracle-ai-services-fit-together">How Private Agent Factory and the Oracle AI services fit together</h3>

<p>The components in this architecture have distinct responsibilities:</p>

<ul>
  <li><strong>OCI Object Storage and Oracle Autonomous AI Lakehouse</strong> retain large source artifacts and historical operational data without forcing every document, log archive, image, or video into the database.</li>
  <li><strong>Oracle AI Database and AI Vector Search</strong> provide the governed operational context: structured facts, JSON, embeddings, resource identities, graph relationships, source references, and hybrid retrieval.</li>
  <li><strong>OCI Generative AI</strong> provides OCI-managed foundation-model inference and enterprise agent services, including chat, embeddings, rerank, OpenAI-compatible APIs, the OCI Responses API, agent tools, vector stores, memory, and hosted agentic applications. In this reference architecture, it is a candidate approved model provider or a separate OCI-managed agent runtime; the target integration must be validated and should cross explicit API or MCP boundaries.</li>
  <li><strong>Oracle Private AI Services Container</strong> provides private embedding, reranking, classification, and LLM inference services in a customer-controlled environment. Its Vector Index Service can use GPU infrastructure to accelerate index creation without turning the container into the system of record.</li>
  <li><strong>Oracle AI Database Private Agent Factory</strong> is the agent engineering and lifecycle-control environment. It brings together enterprise content, approved model providers, APIs, MCP tools, Select AI Agent, and analytical workflows for building, testing, governing, deploying, and operating agents.</li>
  <li><strong>Select AI Agent</strong> is the database-native agent runtime and orchestration capability. <code class="language-plaintext highlighter-rouge">DBMS_CLOUD_AI_AGENT</code> manages tools, tasks, agents, teams, and multi-step workflows that can use SQL, RAG, web search, and notification tools.</li>
  <li><strong>Autonomous AI Database MCP Server</strong> exposes approved Select AI Agent tools through a managed, per-database MCP endpoint while retaining database authentication, authorization, auditing, and least-privilege controls.</li>
  <li><strong>Oracle Machine Learning Data Science Agent</strong> complements the agent runtime with human-supervised data profiling, outlier analysis, statistical investigation, model training, evaluation, and inference.</li>
</ul>

<p>Private Agent Factory does not replace the context plane, the evaluator, or the controlled execution boundary. It operationalizes the agents that use the context. The evaluator remains an independent decision gate that checks evidence, policy, risk, confidence, approval requirements, and blast radius before any operational action is allowed to proceed.</p>

<p>The source evidence remains authoritative. Embeddings are derived retrieval structures, graph edges are relationship context, and model-generated conclusions remain hypotheses until the evaluator verifies them against fresh telemetry.</p>

<h2 id="nvidia-ai-blueprints-as-reference-accelerators">NVIDIA AI Blueprints as reference accelerators</h2>

<p>NVIDIA AI Blueprints provide useful implementation patterns for parts of this architecture. They should be treated as adaptable reference solutions rather than packaged integrations with Select AI Agent.</p>

<ul>
  <li>The <a href="https://github.com/NVIDIA-AI-Blueprints/rag">NVIDIA RAG Blueprint</a> demonstrates multimodal extraction, chunking, embeddings, hybrid retrieval, reranking, guardrails, evaluation, and agentic RAG. In an Oracle-centered implementation, these patterns can feed evidence and metadata into Oracle AI Vector Search, while Select AI Agent uses approved SQL and RAG tools to interact with the governed database context.</li>
  <li>The <a href="https://github.com/NVIDIA-AI-Blueprints/aiq">NVIDIA AI-Q Blueprint</a> demonstrates bounded research, planning, parallel investigation, source selection, citation-backed synthesis, and evaluation. Those patterns are useful for an AI Ops investigator that must assemble evidence before proposing remediation. Oracle database tools can be exposed to such workflows through governed MCP or API boundaries.</li>
  <li>The <a href="https://github.com/NVIDIA-AI-Blueprints/video-search-and-summarization">NVIDIA Video Search and Summarization Blueprint</a> demonstrates how video can become searchable operational evidence through vision models, embeddings, metadata streams, alert verification, and MCP-accessible tools. This is relevant to data centers, manufacturing, transportation, physical security, and other environments where an outage or anomaly may have visual evidence.</li>
</ul>

<p>The NVIDIA component name is <strong>cuVS</strong>, not an embedding model. Oracle Private AI Services Container provides embedding services; its Vector Index Service uses NVIDIA GPUs and <a href="https://blogs.oracle.com/database/introducing-the-vector-index-service">NVIDIA cuVS to accelerate vector-index construction</a>. Keeping this distinction clear separates model inference, embedding generation, vector storage, index construction, and retrieval into explicit architectural responsibilities.</p>

<h2 id="from-dashboards-to-decisions">From dashboards to decisions</h2>

<p>Traditional observability often stops at visibility. A dashboard shows that CPU is high, a database wait event is increasing, a transaction is slower than normal, or a log pattern is repeating. That visibility is useful, but it still leaves the human operator responsible for correlation, prioritization, and action.</p>

<p>AI Ops should move customers from dashboards to decisions.</p>

<p>For example:</p>

<ul>
  <li>OCI Monitoring identifies a compute CPU saturation pattern.</li>
  <li>APM shows that the affected compute instance is part of a customer-facing application path.</li>
  <li>Log Analytics detects a repeating application error after a deployment.</li>
  <li>Database Management shows increased database sessions and wait events.</li>
  <li>Ops Insights indicates the workload has been trending toward a capacity ceiling for several weeks.</li>
  <li>Resource Analytics identifies the affected resource, its OCI configuration, and its known relationships to dependent infrastructure.</li>
  <li>A metrics overlay binds CPU, memory, latency, error rate, and change events to the corresponding graph vertices and time window.</li>
  <li>A graph traversal follows the dependency path to estimate which hosts, databases, application services, and business processes may be inside the blast radius.</li>
  <li>Oracle AI Vector Search retrieves relevant runbooks, previous incidents, change records, and technical knowledge, while Select AI Agent uses approved SQL and RAG tools to investigate the structured and unstructured operational context.</li>
</ul>

<p>Individually, these are signals. Together, they tell a business story: which service is affected, why it matters, whether this is an incident or a capacity trend, what remediation is available, and which investment decision should be made next.</p>

<p>That is where AI Ops creates business value. It compresses the time between signal, understanding, action, and learning.</p>

<h2 id="oci-reference-architecture-for-autonomous-resilience">OCI reference architecture for autonomous resilience</h2>

<p>The OCI AI Ops framework can be organized into five architectural layers.</p>

<p><img src="/images/posts/2026-06-24-aiops-framework/oci-observability-signals-agent-workflow.final.png" alt="OCI Monitoring, Events, Log Analytics, APM, database, and audit signals flowing through event transport and OCI Functions into an agent workflow" class="align-center" />
<em>Figure 3: OCI observability signals move through event transport and processing services before invoking the governed agent workflow.</em></p>

<h2 id="1-telemetry-and-context-collection">1. Telemetry and context collection</h2>

<p>The collector layer gathers operational evidence from OCI Monitoring, Logging, Log Analytics, Application Performance Monitoring, Database Management, Ops Insights, Resource Analytics, Events, traces, SQL diagnostics, and resource metadata. It can also register unstructured evidence from Object Storage or an enterprise data lake and create embeddings for approved content through Oracle Private AI Services Container.</p>

<p>This layer should normalize identity and context as much as possible. Resource OCIDs, compartment names, tags, application names, database names, service tiers, environment labels, and business ownership all matter. Each chunk, embedding, metric, event, and graph vertex should retain a reference to its source and resource identity. Without this context, an agent may understand the symptom but miss the business priority or retrieve evidence for the wrong environment.</p>

<h2 id="2-detection-and-triggering">2. Detection and triggering</h2>

<p>The detector layer turns telemetry into operational signals. OCI Monitoring alarms, OCI Events rules, Log Analytics patterns, APM thresholds, database performance indicators, capacity forecasts, and security anomalies can all become triggers.</p>

<p>In a traditional model, the trigger may send an email or open a ticket. In an AI Ops model, the trigger should also route the payload to the agentic workflow. The alarm still keeps humans informed, but the architecture redirects machine-readable context toward the system that can analyze and act.</p>

<p>The preferred pattern is:</p>

<p><code class="language-plaintext highlighter-rouge">OCI Monitoring / Events / Log Analytics / APM / Database signals -&gt; OCI Streaming or Events -&gt; OCI Functions -&gt; Agent workflow</code></p>

<p>Slack, email, service desk, or collaboration notifications remain important, but they are supervisory channels. The operational payload should flow into the autonomous resilience framework.</p>

<h2 id="3-agent-intelligence-loop">3. Agent intelligence loop</h2>

<p>The agent intelligence loop is the core of the architecture. It turns an alarm into an operational decision.</p>

<p><img src="/images/posts/2026-06-24-aiops-framework/oci-aiops-framework-agent-loop.png" alt="OCI AI Ops agent intelligence loop reference architecture" class="align-center" />
<em>Figure 4: A bounded agent run observes, scopes, detects, plans, governs, simulates, verifies, and reports before accepting the next trusted signal.</em></p>

<p>The loop includes several roles:</p>

<ul>
  <li><strong>Collector</strong>: gathers and enriches evidence from multiple OCI services.</li>
  <li><strong>Detector</strong>: classifies the issue, such as performance degradation, outage, capacity pressure, database contention, security anomaly, or configuration drift.</li>
  <li><strong>Context retriever</strong>: uses Oracle AI Vector Search, Select AI Agent tools, and the Resource Analytics property graph to retrieve grounded knowledge, query operational state, and identify dependent resources.</li>
  <li><strong>Analytical investigator</strong>: uses deterministic queries and Oracle Machine Learning analysis to test hypotheses, identify outliers, and measure whether the condition is exceptional or part of a longer trend.</li>
  <li><strong>Planner</strong>: generates one or more remediation options and explains expected impact.</li>
  <li><strong>Evaluator</strong>: validates the plan before execution against policy, safety, risk, and confidence thresholds.</li>
  <li><strong>Tool broker and orchestrator</strong>: coordinates governed access through Autonomous AI Database MCP Server, OCI Functions, API Gateway, Oracle Integration, service APIs, and downstream enterprise systems. Private Agent Factory can provide the agent-building and lifecycle-governance environment around these workflows.</li>
</ul>

<p>The evaluator is the most important governance component. A good AI Ops system should not simply generate a plan and execute it. It should ask whether the plan is safe, whether the evidence supports the action, whether the blast radius is acceptable, whether a human approval is required, and whether the proposed change aligns with operational policy.</p>

<h2 id="4-controlled-execution-and-verification">4. Controlled execution and verification</h2>

<p>Once the evaluator approves a remediation plan, the execution layer performs the action through a controlled service boundary. In OCI, this may involve OCI Functions, Resource Manager, Database Management operations, Compute APIs, autoscaling actions, integration workflows, or runbook automation.</p>

<p>The framework should capture every action as evidence:</p>

<ul>
  <li>What plan was approved?</li>
  <li>Which policy or evaluator approved it?</li>
  <li>Which OCI identity executed the action?</li>
  <li>What resource changed?</li>
  <li>What was the expected outcome?</li>
  <li>What telemetry changed after execution?</li>
</ul>

<p>Post-execution verification is mandatory. The evaluator should review metrics, logs, traces, database state, and application behavior after the remediation. If the system is not back within the desired state, the loop can generate another plan, escalate to a human operator, or open a problem-management workflow.</p>

<h2 id="5-incident-problem-and-knowledge-management">5. Incident, problem, and knowledge management</h2>

<p>The agent’s responsibility does not end with remediation. The final layer turns an operational event into organizational learning.</p>

<p><img src="/images/posts/2026-06-24-aiops-framework/oci-aiops-incident-problem-knowledge-loop.png" alt="Incident, problem, and knowledge management operational learning loop" class="align-center" />
<em>Figure 5: Operational events become reusable knowledge that improves future agent decisions.</em></p>

<p>After an incident, the framework should generate:</p>

<ul>
  <li>An incident summary with timeline, affected systems, detected symptoms, and business impact.</li>
  <li>A root cause analysis that connects evidence from metrics, logs, traces, SQL data, and events.</li>
  <li>A remediation record describing what was proposed, what was approved, what was executed, and what changed.</li>
  <li>A problem-management recommendation if the issue reflects a recurring defect, capacity trend, design weakness, or process gap.</li>
  <li>A knowledge-base article or operational learning artifact that future agents and human operators can reuse.</li>
</ul>

<p>This is how AI Ops becomes more than automation. Every event improves the operational memory of the enterprise.</p>

<h2 id="example-compute-and-database-pressure">Example: compute and database pressure</h2>

<p>Consider a customer-facing application running on OCI Compute with an Oracle Database backend. OCI Monitoring detects that CPU utilization on the compute tier has crossed a threshold. Around the same time, Database Management shows increased sessions and wait events, APM shows higher transaction latency, and Log Analytics detects repeated timeout messages from the application.</p>

<p>In a traditional operations model, each signal may appear in a different console or dashboard. A human engineer has to assemble the timeline.</p>

<p>In the AI Ops framework, the alarm payload is routed to OCI Functions or OCI Streaming. The collector pulls related evidence from OCI Monitoring, APM, Log Analytics, Database Management, Ops Insights, and Resource Analytics. The Resource Analytics property graph identifies known dependencies around the saturated compute instance, and the metrics overlay shows which connected resources changed during the same time window. The agent can then estimate the blast radius instead of treating the CPU alarm as an isolated event.</p>

<p>Select AI Agent uses approved SQL and RAG tools to investigate structured database state and retrieve relevant runbooks, prior incidents, and change records through Oracle AI Vector Search. If the evidence includes documents, images, or video, an approved private or multimodal pipeline can extract and embed the content while preserving references to the source artifact. The detector classifies the condition as a possible application-saturation and database-response-time incident. The planner proposes remediation options such as scaling compute capacity, restarting a failed application component, tuning a database resource consumer group, or escalating because the confidence is too low for autonomous execution.</p>

<p>The evaluator checks the plan. If the action is low risk and policy-approved, the orchestrator executes it. If the action affects production capacity, database configuration, or business-critical workloads, the framework may require human approval through Slack, email, service desk, or an approval workflow.</p>

<p>After execution, the evaluator verifies whether CPU, latency, database waits, application errors, and transaction success rate returned to expected ranges. The framework then generates an incident summary and RCA, including the evidence chain that led to the remediation.</p>

<h2 id="human-in-the-loop-is-a-design-principle">Human in the loop is a design principle</h2>

<p>Autonomous resilience does not mean unsupervised change. The architecture should distinguish between informational actions, low-risk remediation, high-risk remediation, and business-impacting change.</p>

<p>Some actions can be fully autonomous, such as collecting additional diagnostics, enriching an incident, correlating logs, or creating an RCA draft. Some actions may be conditionally autonomous, such as restarting a stateless component or scaling a pool within an approved limit. Other actions should require explicit approval, such as changing database configuration, modifying network policy, altering security controls, or executing a remediation with uncertain blast radius.</p>

<p>The human-in-the-loop model should be built into the architecture from the beginning. Notifications are not only for awareness. They are a governance mechanism that keeps experts informed, captures approvals, and maintains trust.</p>

<h2 id="why-this-matters-for-customers">Why this matters for customers</h2>

<p>Customers do not adopt AI Ops because they want a new dashboard. They adopt it because cloud complexity is creating operational risk and slowing business decisions.</p>

<p>An OCI AI Ops framework can help customers answer higher-value questions:</p>

<ul>
  <li>Which systems are most likely to fail or breach performance targets?</li>
  <li>Which applications are consuming more capacity than their business value justifies?</li>
  <li>Which database workloads need tuning, scaling, or architectural change?</li>
  <li>Which incidents are recurring because the root problem was never removed?</li>
  <li>Which operational risks are isolated, and which indicate a systemic pattern?</li>
  <li>Which remediation actions are safe enough to automate, and which still need expert approval?</li>
  <li>Which infrastructure and application investments will improve resilience the most?</li>
</ul>

<p>This is where OCI Observability and Management services become strategic. OCI Monitoring, Log Analytics, Database Management, Ops Insights, APM, Resource Analytics, Events, Streaming, and Functions provide the operational evidence, topology, and workflow backbone. Oracle AI Database, AI Vector Search, Select AI Agent, Private AI Services Container, Private Agent Factory, Autonomous AI Database MCP Server, and Oracle Machine Learning Data Science Agent provide the governed context, retrieval, analytical, and agent-tooling plane. Evaluators provide safety. Human experts provide judgment and accountability.</p>

<h2 id="conclusion">Conclusion</h2>

<p>AI Ops is not a replacement for DevOps. It is the next evolution of cloud operations. DevOps connected builders and operators. AI Ops connects observability, automation, AI agents, governance, and business decision-making into one operating model.</p>

<p>For OCI customers, the opportunity is significant. The services already used for monitoring, logging, application performance, database management, capacity planning, event routing, and serverless automation can become the evidence and execution foundation of an autonomous resilience framework. Oracle AI Database then adds the converged context plane: relational state, vectors, graph relationships, machine learning, database-native agents, private inference, and governed tool access.</p>

<p>The future of cloud operations will not be defined by how many alerts a team can process. It will be defined by how quickly the organization can convert telemetry into understanding, understanding into safe action, and action into durable operational knowledge.</p>

<h2 id="authors">Authors</h2>

<ul>
  <li>Royce Fu is a Master Principal Cloud Architect at Oracle on the Observability and Management Specialist team. His work focuses on OCI observability, AIOps, Oracle Database, and enterprise-scale operational intelligence.</li>
  <li>Adrian Birzu is Observability and Security Domain Blackbelt at Oracle EMEA CTO Office. Adrian has around 18 years of work experience, and his focus is on OCI, Observability, Multicloud and Security and provide solutions to our customers challenges.</li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="AI Ops" /><category term="Oracle Cloud Infrastructure" /><category term="OCI Observability" /><category term="Autonomous Operations" /><category term="Cloud Operations" /><summary type="html"><![CDATA[OCI AI Ops framework for Cloud Operation Autonomous Resilience]]></summary></entry><entry><title type="html">AI Agent Observability: Understand How AI Agents Behave in Gen AI Applications and Ecosystems</title><link href="https://royce-fu.com/blog/understand-how-your-agents-behave-in-production/" rel="alternate" type="text/html" title="AI Agent Observability: Understand How AI Agents Behave in Gen AI Applications and Ecosystems" /><published>2026-05-23T00:00:00+00:00</published><updated>2026-06-25T17:33:49+00:00</updated><id>https://royce-fu.com/blog/understand-how-your-agents-behave-in-production</id><content type="html" xml:base="https://royce-fu.com/blog/understand-how-your-agents-behave-in-production/"><![CDATA[<h1 id="ai-agent-observability-understand-how-ai-agents-behave-in-gen-ai-applications-and-ecosystems">AI Agent Observability: Understand How AI Agents Behave in Gen AI Applications and Ecosystems</h1>

<h2 id="introduction">Introduction</h2>

<p>The hard part of deploying AI agents is not getting one impressive demo to work. The hard part is explaining what happened after the agent made a strange decision at 2:17 a.m., retried a tool five times, spent more tokens than expected, retrieved the wrong document, touched sensitive data, and still returned a confident answer.</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/qVEIR6JF0Ak" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/understand-how-your-agents-behave-in-production.png" alt="AI Agent Observability: Understand How AI Agents Behave in Gen AI Applications and Ecosystems — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>Traditional application monitoring tells you whether an API was slow, an endpoint failed, or a database query timed out. That still matters. But agentic systems add a new layer of behavior: prompts, retrieved context, model choices, tool calls, retries, guardrails, evaluator scores, feedback, cost, and data exposure. If you cannot reconstruct those steps, you are not operating an AI system. You are watching outputs arrive and hoping the process behind them made sense.</p>

<p>AI agent observability is the discipline of making that behavior traceable, measurable, governable, and improvable. It is not only about troubleshooting. It is also about quality, safety, cost control, release management, privacy, and trust.</p>

<h2 id="why-agent-observability-matters">Why Agent Observability Matters</h2>

<p>Agent observability matters because production teams need more than a final answer. They need enough evidence to understand what the agent saw, what it decided, what it did, what it cost, and whether it stayed inside the boundaries of policy and data protection.</p>

<p><img src="/images/posts/2026-05-23-agent-observability/why-ai-agent-observability-matters.png" alt="Why AI Agent Observability Matters: From Demos to Production — traditional monitoring versus AI agent observability across logic, data, and cost" class="align-center" /></p>

<ul>
  <li><strong>Debugging</strong>: Traces show causality across multi-step LLM workflows, so teams can identify the failing span and root-cause errors across prompts, retrieval, tools, guardrails, and orchestration.</li>
  <li><strong>Evaluation</strong>: Prompt and completion events capture non-deterministic model behavior. Those traces can feed automated evaluations for accuracy, groundedness, format compliance, safety, and other quality characteristics. User feedback tied to specific outputs adds another signal for understanding quality and engagement.</li>
  <li><strong>AI safety</strong>: GenAI telemetry, combined with specialized evaluators, helps detect unsafe outputs, bias, prompt injection, privacy violations, policy bypasses, and sensitive data exposure.</li>
  <li><strong>Cost tracking</strong>: Usage metrics and token counts reveal operational cost by model, workflow, tenant, feature, prompt version, tool path, or failure path.</li>
  <li><strong>Performance optimization</strong>: Latency, throughput, error rate, queue time, retry count, and tool dependency timing give agents the same production performance discipline expected from traditional applications.</li>
  <li><strong>Incident response automation</strong>: Observability data can trigger operational workflows such as opening an incident, attaching the trace, notifying the owner, scaling resources, throttling risky paths, or restarting failed components. High-risk actions still need policy, approval, and audit controls.</li>
  <li><strong>Version control and rollback</strong>: Tracking model versions, prompt versions, tool schema versions, retrieval indexes, and deployment versions makes it possible to see whether quality or reliability changed after a release and to roll back quickly when a new version degrades behavior.</li>
</ul>

<p>The business case is simple: an agent that cannot be explained cannot be trusted with important work, and an agent that cannot be measured cannot be optimized.</p>

<h2 id="from-final-answers-to-execution-traces">From Final Answers To Execution Traces</h2>

<p>For early chat applications, storing the final prompt and model response was often enough. For production agents, that view is too flat.</p>

<p>An agent request is a workflow. It may classify intent, rewrite the question, retrieve context, call a search index, call a business API, ask the model to choose the next step, validate the output, retry a failed tool, and finally compose the answer. The prompt is only one frame in that movie.</p>

<p>The useful debugging unit is the <strong>trace</strong>. A trace represents one user request or agent run from beginning to end. Inside the trace, each meaningful operation becomes a <strong>span</strong>: prompt assembly, model call, retrieval, embedding, tool call, evaluator, guardrail, retry, or handoff.</p>

<p>This is why LLM observability feels different from classic log search. You are not just asking, “What error did the system throw?” You are asking, “What did the agent believe, what evidence did it use, what actions did it take, and where did the behavior diverge from expectation?”</p>

<p>A useful production trace should capture:</p>

<ul>
  <li>Request ID, session ID, user or tenant context, and deployment version.</li>
  <li>Prompt template name, prompt version, variables, and model parameters.</li>
  <li>Model name, model version, response status, latency, token usage, cost estimate, and retry count.</li>
  <li>Retrieval query, document IDs, chunk IDs, scores, filters, and source system.</li>
  <li>Tool name, tool schema version, arguments summary, response summary, error, retry count, and side-effect status.</li>
  <li>Evaluator scores, guardrail results, masking decisions, safety decisions, and user feedback.</li>
  <li>Final answer, failure category, owner, and incident or ticket link.</li>
</ul>

<p>OpenTelemetry matters because AI systems do not live in isolation. An agent request may cross a web application, vector database, model gateway, tool service, workflow engine, identity provider, and enterprise system of record. OpenTelemetry GenAI semantic conventions and OpenInference point toward a more portable model for correlating AI behavior with infrastructure, application, audit, and security telemetry.</p>

<p>The practical rule is simple: if a human would need it during an incident review, capture it as structured trace data. If the field contains sensitive data, capture a masked or summarized version instead of pretending the field does not matter.</p>

<h2 id="cost-analysis-and-cost-control-for-ai-agents">Cost Analysis And Cost Control For AI Agents</h2>

<p>Cost control is one of the most important reasons to invest in agent observability. A model usage dashboard can tell you that token spend increased. It usually cannot tell you why.</p>

<p>AI agent cost is a workflow problem. A cost spike may come from prompt bloat, retrieval returning too many chunks, verbose tool responses, evaluator calls, repeated planning loops, retry storms, failed tool calls, oversized observations, or an expensive model being used for a step that a smaller model could handle.</p>

<p>The right unit of cost analysis is the trace. Then break the trace down by span:</p>

<ul>
  <li><strong>Planning cost</strong>: How many model calls are spent deciding what to do before any useful action happens?</li>
  <li><strong>Retrieval cost</strong>: How many chunks are retrieved, how large are they, and how much context is sent to the model?</li>
  <li><strong>Tool cost</strong>: Are tool responses too verbose, duplicated, or poorly shaped for the model?</li>
  <li><strong>Retry cost</strong>: How much spend comes from failed calls, timeouts, malformed JSON, or rejected tool arguments?</li>
  <li><strong>Evaluation cost</strong>: Which evaluator calls are required online, and which can run asynchronously or offline?</li>
  <li><strong>Guardrail cost</strong>: Which safety checks are necessary on every request, and which can be triggered by risk signals?</li>
  <li><strong>Failure cost</strong>: How much more expensive are failed requests than successful requests?</li>
</ul>

<p>Cost should also be attributed by business dimension: model, prompt version, retrieval index, tenant, user segment, workflow, product feature, environment, and successful outcome. A low-cost request that produces a wrong answer is not efficient. A high-cost request that avoids a costly human escalation may be justified. The useful metric is not only cost per request. It is cost per correct, safe, useful outcome.</p>

<p>Practical cost controls include:</p>

<ul>
  <li><strong>Prompt budgets</strong>: Set maximum prompt sizes and remove instructions that no longer change behavior.</li>
  <li><strong>Context budgets</strong>: Limit retrieval top-k, chunk size, and full-document stuffing. Prefer source references or summaries when the model does not need raw text.</li>
  <li><strong>Model routing</strong>: Use smaller or cheaper models for classification, routing, summarization, and formatting. Reserve expensive models for steps that need deeper reasoning.</li>
  <li><strong>Tool response shaping</strong>: Return only the fields the agent needs. Large JSON payloads often become hidden token waste.</li>
  <li><strong>Loop and retry limits</strong>: Set clear maximums for planning loops, tool retries, evaluator retries, and repair attempts.</li>
  <li><strong>Caching</strong>: Cache stable retrieval results, deterministic tool outputs, embeddings, and common classification results.</li>
  <li><strong>Evaluator placement</strong>: Run lightweight checks inline and heavier evaluations asynchronously when user experience allows it.</li>
  <li><strong>Budget alerts</strong>: Alert on cost per trace, cost per tenant, token growth by prompt version, retry spend, and sudden shifts in model mix.</li>
  <li><strong>Sampling and retention</strong>: Keep full traces for high-risk, failed, or expensive requests. Store summarized telemetry for low-risk paths when privacy and cost require it.</li>
</ul>

<p>The counter-intuitive lesson is that optimizing model cost usually starts outside the model. Better routing, cleaner prompts, smaller retrieval payloads, tool response shaping, masking of unnecessary sensitive fields, and loop controls often produce bigger savings than simply switching models.</p>

<h2 id="quality-safety-and-governance">Quality, Safety, And Governance</h2>

<p>If every bad outcome is labeled “LLM error,” the observability system is not helping. Production agents need a failure taxonomy that separates the failure modes teams can actually fix.</p>

<p>Useful categories include:</p>

<ul>
  <li><strong>Input failure</strong>: ambiguous user intent, unsupported request, prompt injection attempt, malformed input.</li>
  <li><strong>Prompt or version failure</strong>: wrong template, untested prompt change, missing system instruction, incompatible variables.</li>
  <li><strong>Retrieval failure</strong>: no relevant documents, stale content, weak ranking, excessive context, missing access control filter.</li>
  <li><strong>Model failure</strong>: hallucination, refusal, malformed JSON, unsupported tool choice, weak reasoning, unsafe output.</li>
  <li><strong>Tool failure</strong>: timeout, rate limit, authentication issue, schema drift, bad arguments, rejected side effect.</li>
  <li><strong>Orchestration failure</strong>: infinite loop, poor routing, bad handoff, retry storm, memory contamination.</li>
  <li><strong>Evaluation failure</strong>: evaluator drift, weak test set, missing golden examples, false positive safety block.</li>
  <li><strong>Security or privacy failure</strong>: prompt injection, sensitive data leakage, excessive privileges, unmasked trace payload, policy bypass.</li>
  <li><strong>Cost or latency failure</strong>: token explosion, slow dependency, oversized context, excessive retries.</li>
</ul>

<p>This taxonomy becomes the vocabulary for post-incident reviews, regression tests, release gates, model routing policies, security reviews, and rollback decisions.</p>

<p>Evals and observability are also converging. A bad production trace can become a regression test. A user thumbs-down can become a labeled example. A high-cost trace can become a prompt optimization candidate. A new model release can be evaluated against real historical failures before it reaches traffic.</p>

<p>The most mature teams will not ask only, “Did the agent fail?” They will ask, “Can we turn that failure into a reusable test so it does not come back?”</p>

<h2 id="data-masking-belongs-in-the-observability-design">Data Masking Belongs In The Observability Design</h2>

<p>Production traces can contain prompts, retrieved passages, tool arguments, model outputs, customer records, employee data, financial details, health information, credentials, and operational secrets. Observability data can become a second copy of sensitive business data if teams simply log everything.</p>

<p>That is why masking, redaction, tokenization, access control, retention, and sampling must be designed with the trace model. They are not cleanup tasks after the dashboard is built.</p>

<p>There are three practical masking points:</p>

<ul>
  <li><strong>Before the model call</strong>: Remove or tokenize sensitive values that the model does not need.</li>
  <li><strong>Before tool execution</strong>: Prevent sensitive or unauthorized fields from reaching tools that should not see them.</li>
  <li><strong>Before telemetry export</strong>: Mask prompt inputs, tool arguments, observations, retrieved chunks, model outputs, metadata, and evaluator payloads before they leave the application or database boundary.</li>
</ul>

<p>The tradeoff is real: the more you mask, the less raw detail you have for debugging and evaluation. The answer is not to choose visibility or privacy. The answer is to define safe observability contracts: capture enough structure to explain behavior, but avoid persisting raw sensitive content when a masked value, hash, label, row identifier, policy decision, or source reference will do.</p>

<h2 id="reference-architecture-production-agent-observability">Reference Architecture: Production Agent Observability</h2>

<p>A practical production architecture has five layers:</p>

<ol>
  <li><strong>Instrumentation layer</strong>: Capture traces and spans from the application, orchestration framework, model gateway, retrieval layer, tools, guardrails, evaluators, and feedback UI.</li>
  <li><strong>Data protection layer</strong>: Apply masking, redaction, access control, policy checks, retention rules, and sampling before telemetry becomes another sensitive data store.</li>
  <li><strong>Telemetry pipeline</strong>: Emit structured events through SDKs, OpenTelemetry, vendor APIs, or database-native history views. Preserve request IDs, user/session IDs, tenant IDs, prompt versions, model versions, and deployment versions.</li>
  <li><strong>Analysis layer</strong>: Use an LLM observability platform for trace inspection, prompt comparison, evals, datasets, feedback, cost analysis, and release regression checks.</li>
  <li><strong>Operations layer</strong>: Correlate agent telemetry with APM, logs, metrics, audit, SIEM, database telemetry, and incident management workflows.</li>
</ol>

<p>The architecture should answer five questions quickly:</p>

<ul>
  <li>What happened in this request?</li>
  <li>Which step caused the failure, latency, cost spike, or policy block?</li>
  <li>Did this behavior start after a prompt, model, data, tool, policy, or code change?</li>
  <li>Did sensitive data move farther than it needed to?</li>
  <li>Can this case become a test, alert, masking rule, rollback trigger, or remediation workflow?</li>
</ul>

<h2 id="tooling-landscape-where-each-option-fits">Tooling Landscape: Where Each Option Fits</h2>

<p>No single tool wins every scenario. The right choice depends on whether you prioritize deep eval workflows, open-source self-hosting, framework-native tracing, gateway-level observability, enterprise production support, data-residency controls, or OpenTelemetry portability.</p>

<table>
  <thead>
    <tr>
      <th>Tooling approach</th>
      <th>Tracing and eval fit</th>
      <th>Security and privacy posture</th>
      <th>Best fit</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><a href="https://www.braintrust.dev/docs">Braintrust</a></td>
      <td>Strong trace and span inspection for LLM apps, with experiments, logs, prompts, datasets, feedback, and eval workflows tied together.</td>
      <td>Supports global masking functions for sensitive input, output, expected, metadata, and context fields. Validate deployment and data-handling requirements for regulated workloads.</td>
      <td>Teams that want eval-driven release workflows and production feedback loops.</td>
    </tr>
    <tr>
      <td><a href="https://langfuse.com/docs">Langfuse</a></td>
      <td>Strong traces for LLM calls, chains, agents, tools, metadata, sessions, datasets, scores, experiments, prompt management, and user feedback.</td>
      <td>Strong for teams that want masking control: client-side masking can prevent sensitive data from leaving the app, and self-hosted enterprise ingestion masking can centralize policy enforcement.</td>
      <td>Teams that want open-source control plus broad LLM observability coverage.</td>
    </tr>
    <tr>
      <td><a href="https://docs.langchain.com/langsmith/home">LangSmith</a></td>
      <td>Very strong for LangChain and LangGraph applications, with detailed traces, threads, datasets, prompts, online evals, offline evals, and production monitoring.</td>
      <td>Supports hiding or masking inputs, outputs, and metadata, plus conditional tracing when some requests should not be traced at all.</td>
      <td>Teams already building with LangChain/LangGraph or needing tight framework integration.</td>
    </tr>
    <tr>
      <td><a href="https://docs.helicone.ai/">Helicone</a></td>
      <td>Strong gateway-centric request observability, cost, latency, caching, sessions, prompts, users, and properties.</td>
      <td>Good fit for centralized gateway controls and usage visibility. Confirm masking, retention, and self-hosted posture against your compliance requirements before sending raw prompts or tool payloads.</td>
      <td>Teams that want fast gateway deployment, usage visibility, and cost controls.</td>
    </tr>
    <tr>
      <td><a href="https://phoenix.arize.com/">Arize Phoenix</a> and Arize AX</td>
      <td>Strong open-source tracing for LLMs, retrieval, tools, agents, OpenTelemetry, OpenInference, datasets, experiments, and evaluators.</td>
      <td>OpenTelemetry-style control over spans and attributes; Arize documentation includes masking or redacting span attributes for sensitive data handling.</td>
      <td>Teams that want open-source AI observability with a path to enterprise AI monitoring.</td>
    </tr>
    <tr>
      <td><a href="https://docs.openlit.io/latest/overview">OpenLIT</a></td>
      <td>Strong OpenTelemetry-native tracing for LLMs, agents, vector databases, MCP, GPUs, prompts, metrics, logs, dashboards, and evaluations.</td>
      <td>Good for OpenTelemetry-first teams, but sensitive capture must be configured deliberately. OpenLIT warns that database parameter capture can expose passwords, API keys, or personal information.</td>
      <td>Teams that want an OpenTelemetry-first, self-hostable AI engineering platform with broad instrumentation coverage.</td>
    </tr>
    <tr>
      <td><a href="https://docs.oracle.com/en/cloud/paas/autonomous-database/serverless/adbsb/about-select-ai-agents.html">Oracle Autonomous AI Database Select AI Agent</a></td>
      <td>Database-resident agent framework with planning, tool use, reflection, conversation memory, tool history, and agent/team/task history views for transparency.</td>
      <td>Strong data-gravity pattern: agents run inside Autonomous AI Database, inherit database security controls and auditing, reduce data movement, and can use controls such as RBAC, CBAC, privileges, VPD, RAS, data masking, encryption, and Data Safe.</td>
      <td>Regulated or data-centric workflows where keeping tools, data, policy, and observability close to the database is more important than using a standalone agent framework.</td>
    </tr>
    <tr>
      <td><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/use-loganai.html">OCI Log Analytics with LoganAI</a></td>
      <td>Strong for enterprise log analytics, correlation, clustering, dashboards, and AI-assisted explanations of structured agent runtime logs. It is not a dedicated LLM span tracing product by itself.</td>
      <td>Strong for OCI-centric operations, audit, security correlation, and retention governance. Best fed with structured and masked agent telemetry rather than raw sensitive prompts.</td>
      <td>OCI-centric enterprises that need production operations, security, audit, and application telemetry in the same investigation workspace.</td>
    </tr>
    <tr>
      <td>OpenTelemetry-native</td>
      <td>Depends on your instrumentation and backend. Excellent portability across app, infra, security, database, and AI telemetry.</td>
      <td>Strong if your collectors, processors, exporters, and storage tiers enforce masking, filtering, retention, and access policies consistently.</td>
      <td>Platform teams that already run an enterprise telemetry stack and want portability.</td>
    </tr>
  </tbody>
</table>

<p>The most common pattern will be hybrid: use a specialized LLM observability tool for prompt, trace, eval, and feedback depth, while exporting or correlating key signals into the broader enterprise observability stack.</p>

<h2 id="balancing-efficiency-and-data-security">Balancing Efficiency And Data Security</h2>

<p>The efficiency question is not only “Which tool gives me the best dashboard?” It is also “Where should the data be observed, reduced, masked, and stored?”</p>

<p>For teams that need speed, an OpenAI-compatible gateway or open-source LLM observability tool can provide fast visibility into prompts, token usage, latency, sessions, tool calls, and evals. This is the path highlighted by many practical Langfuse-style implementations: start with trace visibility, add scoring, then turn production failures into datasets and tests.</p>

<p>For teams that need stronger data control, the architecture should shift left. Mask before telemetry export. Keep raw customer records in governed systems. Store references, policy decisions, hashes, row IDs, and summarized observations instead of full payloads when possible. Use self-hosted observability only when the operational team is ready to manage retention, patching, access control, backups, and audit.</p>

<p>This is where Autonomous AI Database Select AI Agent can be a strong enterprise pattern. If the agent’s primary job is to reason over database-resident data, execute database tools, or call governed business logic, running the agent framework inside Autonomous AI Database reduces data movement and lets the agent inherit database security and audit controls. The tradeoff is that you may still want a dedicated LLM observability or evaluation platform for richer prompt experiments, dataset management, human annotation, and cross-application trace analysis. In that case, export masked or summarized telemetry rather than raw sensitive records.</p>

<p>In other words, ADB Select AI Agent is not simply another dashboard option. It is a placement decision: put agent execution close to governed data, then publish safe operational signals outward.</p>

<h2 id="where-oci-log-analytics-and-loganai-fit">Where OCI Log Analytics And LoganAI Fit</h2>

<p>OCI Log Analytics is especially interesting for enterprise AI operations because agent behavior does not end at the LLM boundary. Agents touch identity systems, databases, integration services, ticketing platforms, cloud APIs, network paths, and business applications. Those systems already produce logs, events, and operational signals.</p>

<p>For OCI customers, the pragmatic pattern is to emit structured, masked agent runtime logs into OCI Log Analytics: trace ID, span ID, user or tenant context, prompt version, model name, retrieval source, tool name, latency, token usage, error class, guardrail result, masking policy result, and final failure taxonomy. Once those fields are indexed, teams can use Log Explorer, dashboards, clusters, link visualizations, and saved searches to correlate agent behavior with OCI Audit logs, application logs, infrastructure logs, database telemetry, and security events.</p>

<p>LoganAI adds an AI-assisted investigation layer on top of that telemetry. Oracle documents LoganAI as the AI capability in Oracle Log Analytics for analyzing logs and log-derived data, including AI-powered explanations for single logs, multiple logs, clusters, and charts. It can also fetch metrics from OCI Monitoring using MQL and mix them with logs for analysis.</p>

<p>That makes LoganAI a useful operational companion to LLM tracing platforms. A dedicated LLM observability tool may tell you that a retrieval step failed or a tool call retried. OCI Log Analytics can help answer the next enterprise question: what else was happening in the environment at that time, which tenant or compartment was affected, whether related audit events occurred, whether masking policies fired, and whether similar failures are clustering elsewhere.</p>

<h2 id="hands-on-example-trace-a-codex-agent-with-langfuse">Hands-On Example: Trace A Codex Agent With Langfuse</h2>

<p>Langfuse is a practical way to demonstrate LLM-focused observability because it gives teams traces, generations, tool calls, sessions, token usage, scores, datasets, and feedback workflows. For Codex specifically, the Langfuse Codex observability plugin traces agent turns, model calls, tool executions, token usage, and subagent threads to Langfuse.</p>

<p>Use this as a development or controlled-environment example first. The plugin can upload Codex transcript data, including prompts, assistant messages, reasoning summaries, tool-call inputs and outputs, model metadata, and token usage. Do not enable it for sessions that contain data you are not comfortable storing in Langfuse.</p>

<h3 id="1-create-a-langfuse-project">1. Create a Langfuse project</h3>

<p>Create a Langfuse Cloud project or use a self-hosted Langfuse instance. Generate a public key and secret key for the project.</p>

<p>Choose the correct base URL for your data region, for example:</p>

<ul>
  <li><code class="language-plaintext highlighter-rouge">https://cloud.langfuse.com</code></li>
  <li><code class="language-plaintext highlighter-rouge">https://us.cloud.langfuse.com</code></li>
  <li><code class="language-plaintext highlighter-rouge">https://jp.cloud.langfuse.com</code></li>
</ul>

<h3 id="2-optional-install-the-langfuse-skill-for-codex">2. Optional: install the Langfuse skill for Codex</h3>

<p>The Langfuse skill gives Codex Langfuse-specific guidance and documentation workflow support.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>python3 ~/.codex/skills/.system/skill-installer/scripts/install-skill-from-github.py <span class="se">\</span>
  <span class="nt">--repo</span> langfuse/skills <span class="se">\</span>
  <span class="nt">--path</span> skills/langfuse
</code></pre></div></div>

<p>Verify the skill:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">ls</span> <span class="nt">-la</span> ~/.codex/skills/langfuse
</code></pre></div></div>

<p>Expected files include:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>SKILL.md
references/
</code></pre></div></div>

<h3 id="3-add-the-langfuse-plugin-marketplace">3. Add the Langfuse plugin marketplace</h3>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>codex plugin marketplace add langfuse/codex-observability-plugin
</code></pre></div></div>

<h3 id="4-enable-the-tracing-plugin">4. Enable the tracing plugin</h3>

<p>Depending on your Codex build, you may install the marketplace plugin explicitly:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>codex plugin add tracing@codex-observability-plugin
</code></pre></div></div>

<p>Then verify:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>codex plugin list
</code></pre></div></div>

<p>Expected entry:</p>

<div class="language-text highlighter-rouge"><div class="highlight"><pre class="highlight"><code>tracing@codex-observability-plugin  installed, enabled
</code></pre></div></div>

<h3 id="5-enable-plugin-hooks">5. Enable plugin hooks</h3>

<p>Edit <code class="language-plaintext highlighter-rouge">~/.codex/config.toml</code>, or use <code class="language-plaintext highlighter-rouge">&lt;project&gt;/.codex/config.toml</code> for project-specific tracing.</p>

<p>Put <code class="language-plaintext highlighter-rouge">plugin_hooks = true</code> under the <code class="language-plaintext highlighter-rouge">[features]</code> block:</p>

<div class="language-toml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nn">[features]</span>
<span class="py">plugin_hooks</span> <span class="p">=</span> <span class="kc">true</span>
</code></pre></div></div>

<p>Enable the plugin:</p>

<div class="language-toml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nn">[plugins."tracing@codex-observability-plugin"]</span>
<span class="py">enabled</span> <span class="p">=</span> <span class="kc">true</span>
</code></pre></div></div>

<h3 id="6-configure-langfuse-credentials">6. Configure Langfuse credentials</h3>

<p>Environment variables are usually the cleanest option for public examples and automation:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">export </span><span class="nv">TRACE_TO_LANGFUSE</span><span class="o">=</span><span class="s2">"true"</span>
<span class="nb">export </span><span class="nv">LANGFUSE_PUBLIC_KEY</span><span class="o">=</span><span class="s2">"pk-lf-..."</span>
<span class="nb">export </span><span class="nv">LANGFUSE_SECRET_KEY</span><span class="o">=</span><span class="s2">"sk-lf-..."</span>
<span class="nb">export </span><span class="nv">LANGFUSE_BASE_URL</span><span class="o">=</span><span class="s2">"https://us.cloud.langfuse.com"</span>
</code></pre></div></div>

<p>You can also use <code class="language-plaintext highlighter-rouge">LANGFUSE_CODEX_PUBLIC_KEY</code>, <code class="language-plaintext highlighter-rouge">LANGFUSE_CODEX_SECRET_KEY</code>, and <code class="language-plaintext highlighter-rouge">LANGFUSE_CODEX_BASE_URL</code> if you want Codex-specific settings that do not affect other Langfuse tools.</p>

<p>For a JSON config file, create <code class="language-plaintext highlighter-rouge">~/.codex/langfuse.json</code> or <code class="language-plaintext highlighter-rouge">&lt;project&gt;/.codex/langfuse.json</code>:</p>

<div class="language-json highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="p">{</span><span class="w">
  </span><span class="nl">"enabled"</span><span class="p">:</span><span class="w"> </span><span class="kc">true</span><span class="p">,</span><span class="w">
  </span><span class="nl">"public_key"</span><span class="p">:</span><span class="w"> </span><span class="s2">"pk-lf-..."</span><span class="p">,</span><span class="w">
  </span><span class="nl">"secret_key"</span><span class="p">:</span><span class="w"> </span><span class="s2">"sk-lf-..."</span><span class="p">,</span><span class="w">
  </span><span class="nl">"base_url"</span><span class="p">:</span><span class="w"> </span><span class="s2">"https://us.cloud.langfuse.com"</span><span class="w">
</span><span class="p">}</span><span class="w">
</span></code></pre></div></div>

<p>Lock down the file:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">chmod </span>600 ~/.codex/langfuse.json
</code></pre></div></div>

<h3 id="7-restart-codex">7. Restart Codex</h3>

<p>Restart Codex after changing plugin or hook settings. Hook configuration is loaded when Codex starts.</p>

<h3 id="8-run-a-test-turn-and-verify-traces">8. Run a test turn and verify traces</h3>

<p>Run a simple Codex task that does not contain sensitive data. Then open the Langfuse project and look for a new trace.</p>

<p>The Langfuse <strong>Home</strong> view gives a project-level overview of total traces, model cost, observations over time, and scores, so you can confirm telemetry is flowing before drilling into individual runs.</p>

<p><img src="/images/posts/2026-05-23-agent-observability/langfuse-home-page.png" alt="Langfuse Home dashboard showing total traces, model costs, observations by time, and model usage for a Codex project" class="align-center" /></p>

<p>The <strong>Tracing</strong> view lists every agent run with its timestamp, name, input, output, latency, cost, and token usage, so you can scan for slow, expensive, or failed traces at a glance.</p>

<p><img src="/images/posts/2026-05-23-agent-observability/langfuse-tracing-page.png" alt="Langfuse Tracing list view showing Codex agent runs with latency, cost, and token usage columns" class="align-center" /></p>

<p>Inspect:</p>

<ul>
  <li>Overall trace duration.</li>
  <li>Model name and token usage.</li>
  <li>Tool calls and errors.</li>
  <li>Failed commands or retries.</li>
  <li>Cost by model call or generation.</li>
  <li>Long prompts, large outputs, or oversized tool responses.</li>
</ul>

<p>Opening a single <strong>Codex Turn</strong> trace shows the span tree for that run — the model call, <code class="language-plaintext highlighter-rouge">exec_command</code>, <code class="language-plaintext highlighter-rouge">apply_patch</code>, and any subagent threads — alongside the prompt, output, and per-span metadata. This is the unit where you root-cause behavior: which step ran, what it produced, and where the run diverged from expectation.</p>

<p>The same detail view exposes the full output and structured metadata for each span — model name, token usage, service attributes, and version tags — which is exactly the evidence you need during an incident review.</p>

<p><img src="/images/posts/2026-05-23-agent-observability/langfuse-trace-details.png" alt="Langfuse trace detail showing a Codex Turn output and structured span metadata such as model, tokens, and version tags" class="align-center" /></p>

<p>You can also run with debug and stricter failure reporting during testing:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">export </span><span class="nv">LANGFUSE_CODEX_DEBUG</span><span class="o">=</span><span class="s2">"true"</span>
<span class="nb">export </span><span class="nv">LANGFUSE_CODEX_FAIL_ON_ERROR</span><span class="o">=</span><span class="s2">"true"</span>
</code></pre></div></div>

<p>Turn those off for normal interactive use unless you want tracing upload errors to interrupt your workflow.</p>

<h3 id="9-use-the-data-to-control-behavior-and-cost">9. Use the data to control behavior and cost</h3>

<p>Once traces are flowing, start with four dashboards or saved views:</p>

<ul>
  <li><strong>Cost by model and prompt version</strong>: Find expensive prompts, model upgrades, and regressions.</li>
  <li><strong>Cost by trace outcome</strong>: Compare successful, failed, retried, and user-rejected requests.</li>
  <li><strong>Tool and retrieval overhead</strong>: Identify tools returning too much data or retrieval steps stuffing too much context.</li>
  <li><strong>Quality and safety signals</strong>: Correlate evaluator scores, user feedback, guardrail blocks, and sensitive-data masking decisions.</li>
</ul>

<p>A cost dashboard turns those views into one place to watch spend: total cost across all traces, cost by model name and environment, and the top users, traces, and observations by cost — so a spike points you straight at the workflow that caused it.</p>

<p>The goal is not simply to store agent traces. The goal is to create a feedback loop: observe behavior, identify waste or risk, change prompts/tools/routing/retrieval, evaluate again, and keep the traces that prove the improvement.</p>

<h2 id="conclusion">Conclusion</h2>

<p>The next phase of AI operations will not be won by teams with the prettiest dashboards. It will be won by teams that can reconstruct the full story of an agent’s behavior: what it saw, what it decided, what it did, what it cost, why it failed, what data it exposed, and how that failure becomes a better system tomorrow.</p>

<p>As agents move from demos into enterprise workflows, observability becomes more than troubleshooting. It becomes the control plane for trust, quality, safety, and cost.</p>

<p>The question is not whether your agent can answer. The question is whether you can explain how it answered when production asks for proof, whether you can afford the workflow at scale, and whether you can prove that the explanation did not create a new privacy problem.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://github.com/langfuse/codex-observability-plugin">Langfuse Codex observability plugin</a></li>
  <li><a href="https://github.com/langfuse/skills/tree/main/skills/langfuse">Langfuse skill for Codex</a></li>
  <li><a href="https://luigi-saetta.medium.com/observability-for-enterprise-ai-agents-an-open-source-solution-bb90eb42a086">Observability for Enterprise AI Agents: An Open Source Solution</a></li>
  <li><a href="https://opentelemetry.io/docs/specs/semconv/gen-ai/">OpenTelemetry GenAI semantic conventions</a></li>
  <li><a href="https://arize-ai.github.io/openinference/spec/">OpenInference specification</a></li>
  <li><a href="https://www.braintrust.dev/docs">Braintrust documentation</a></li>
  <li><a href="https://www.braintrust.dev/docs/instrument/advanced-tracing">Braintrust advanced tracing: Mask sensitive data</a></li>
  <li><a href="https://langfuse.com/docs">Langfuse documentation</a></li>
  <li><a href="https://langfuse.com/docs/observability/features/masking">Langfuse masking of sensitive LLM data</a></li>
  <li><a href="https://langfuse.com/self-hosting/security/data-masking">Langfuse self-hosted data masking</a></li>
  <li><a href="https://docs.langchain.com/langsmith/home">LangSmith documentation</a></li>
  <li><a href="https://docs.langchain.com/langsmith/mask-inputs-outputs">LangSmith: Prevent logging of sensitive data in traces</a></li>
  <li><a href="https://docs.helicone.ai/">Helicone documentation</a></li>
  <li><a href="https://phoenix.arize.com/">Arize Phoenix</a></li>
  <li><a href="https://arize.com/docs/ax/observe/tracing/configure">Arize tracing configuration: Sensitive data handling</a></li>
  <li><a href="https://docs.openlit.io/latest/overview">OpenLIT documentation</a></li>
  <li><a href="https://docs.openlit.io/latest/sdk/configuration">OpenLIT SDK configuration</a></li>
  <li><a href="https://www.oracle.com/autonomous-database/select-ai/">Oracle Autonomous AI Database Select AI</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/paas/autonomous-database/serverless/adbsb/about-select-ai-agents.html">Oracle Autonomous AI Database: About Select AI Agent</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/paas/autonomous-database/serverless/adbsb/select-ai-agents-concepts.html">Oracle Autonomous AI Database: Select AI Agent Concepts</a></li>
  <li><a href="https://blogs.oracle.com/machinelearning/build-your-agentic-solution-using-oracle-adb-select-ai-agent">Build Your Agentic Solution using Oracle Autonomous AI Database Select AI Agent</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/data-safe/doc/oracle-data-safe-overview.html">Oracle Data Safe overview</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/use-loganai.html">OCI Log Analytics: Use LoganAI</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/prerequisites-using-loganai.html">OCI Log Analytics: Prerequisites for LoganAI</a></li>
  <li><a href="https://owasp.org/www-project-top-10-for-large-language-model-applications/">OWASP Top 10 for Large Language Model Applications</a></li>
</ul>

<h2 id="authors">Authors</h2>

<ul>
  <li>Royce Fu is a Master Principal Cloud Architect at Oracle on the Observability and Management Specialist team. His work focuses on OCI observability, AIOps, Oracle Database, and enterprise-scale operational intelligence.</li>
  <li>Adrian Birzu is Observability and Security Domain Blackbelt at Oracle EMEA CTO Office. Adrian has around 18 years of work experience, and his focus is on OCI, Observability, Multicloud and Security and provide solutions to our customers challenges.</li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="AI Observability" /><category term="Agentic AI" /><category term="LLMOps" /><category term="OpenTelemetry" /><category term="AI Architecture" /><category term="Data Security" /><summary type="html"><![CDATA[AI Agent Observability: Understand How AI Agents Behave in Gen AI Applications and Ecosystems]]></summary></entry><entry><title type="html">AI Architect Series: How to Build an Efficient AI Ecosystem</title><link href="https://royce-fu.com/blog/AI-Architect-how-to-build-an-efficient-AI-ecosystem/" rel="alternate" type="text/html" title="AI Architect Series: How to Build an Efficient AI Ecosystem" /><published>2026-03-09T00:00:00+00:00</published><updated>2026-03-09T14:00:00+00:00</updated><id>https://royce-fu.com/blog/AI-Architect-how-to-build-an-efficient-AI-ecosystem</id><content type="html" xml:base="https://royce-fu.com/blog/AI-Architect-how-to-build-an-efficient-AI-ecosystem/"><![CDATA[<h1 id="ai-architect-series-how-to-build-an-efficient-ai-ecosystem">AI Architect Series: How to Build an Efficient AI Ecosystem</h1>

<h2 id="introduction-the-transformation-has-already-begun">Introduction: The Transformation Has Already Begun</h2>

<p>If you are a DBA, Cloud Architect, or IT operations professional, you have likely noticed a seismic shift in how technology teams operate. The runbooks you maintained, the monitoring dashboards you built, the incident response playbooks you refined over years—all of these are being reimagined through the lens of AI.</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/JoM6Q7rLdeE" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/AI-Architect-how-to-build-an-efficient-AI-ecosystem.png" alt="AI Architect Series: How to Build an Efficient AI Ecosystem — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>This is not about replacing your expertise. It is about <strong>amplifying</strong> it.</p>

<p>The emergence of AI coding assistants and agentic AI systems has created a new discipline: <strong>AI Architecture</strong>—the practice of designing, orchestrating, and governing an ecosystem of AI tools that work together to enhance your operational capabilities. Just as Cloud Architecture transformed how we think about infrastructure, AI Architecture is transforming how we think about <strong>knowledge work itself</strong>.</p>

<p>This post—the first in the <strong>AI Architect</strong> series—draws insights from Anthropic’s <a href="https://resources.anthropic.com/hubfs/The-Complete-Guide-to-Building-Skill-for-Claude.pdf"><em>The Complete Guide to Building Skills for Claude</em></a> and maps those concepts to the realities of enterprise IT. Whether you manage Oracle databases, orchestrate cloud infrastructure, or run an operations center, this guide will help you understand how to build a personal AI ecosystem that makes you dramatically more effective.</p>

<h2 id="from-prompt-engineering-to-execution-design">From Prompt Engineering to Execution Design</h2>

<h3 id="the-old-way-prompt-engineering">The Old Way: Prompt Engineering</h3>

<p>Most IT professionals start their AI journey the same way: typing ad-hoc questions into ChatGPT or Claude. <em>“How do I tune a PGA in Oracle 19c?”</em> or <em>“Write me a Terraform module for an OCI VCN.”</em> This is <strong>prompt engineering</strong>—crafting one-off requests and hoping for a useful response.</p>

<p>It works. But it does not scale.</p>

<p>Every time you start a new conversation, you lose context. You re-explain your environment, your naming conventions, your compliance requirements. You copy-paste responses and manually verify them. This is the equivalent of SSH-ing into a server to run ad-hoc commands—functional, but not operational.</p>

<h3 id="the-new-way-execution-design">The New Way: Execution Design</h3>

<p>Anthropic’s skills guide introduces a paradigm shift: moving from <strong>prompt engineering</strong> to <strong>execution design</strong>. Instead of asking an AI to do something, you design a <strong>system</strong> that enables the AI to do it consistently, correctly, and autonomously.</p>

<p>The core insight is this:</p>

<blockquote>
  <p><strong>MCP (Model Context Protocol) gives the AI the kitchen. Skills give it the recipe.</strong></p>
</blockquote>

<p>In IT terms: MCP is like giving your AI access to APIs, CLIs, and databases. Skills are like giving it your runbooks, SOPs, and tribal knowledge—packaged in a way the AI can actually use.</p>

<p>This distinction is critical for IT professionals. You already have the recipes. Your runbooks, your monitoring strategies, your incident response procedures—these are the institutional knowledge that makes your team effective. The question is: <strong>how do you encode that knowledge so an AI agent can leverage it?</strong></p>

<h2 id="understanding-the-ai-skills-framework">Understanding the AI Skills Framework</h2>

<p>Anthropic’s guide defines a <strong>skill</strong> as a structured set of instructions, packaged in a folder, that teaches an AI how to perform specific tasks consistently. Think of it as an <strong>Infrastructure-as-Code template, but for AI behavior</strong>.</p>

<h3 id="skill-anatomy-a-skillmd-file">Skill Anatomy: A SKILL.md File</h3>

<p>At the heart of every skill is a <code class="language-plaintext highlighter-rouge">SKILL.md</code> file—a Markdown document with YAML frontmatter that tells the AI:</p>
<ul>
  <li><strong>When</strong> to activate (what triggers this skill?)</li>
  <li><strong>How</strong> to execute (what are the step-by-step instructions?)</li>
  <li><strong>What</strong> to reference (what scripts, templates, or documentation should it consult?)</li>
</ul>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nn">---</span>
<span class="na">name</span><span class="pi">:</span> <span class="s">oracle-awr-analysis</span>
<span class="na">description</span><span class="pi">:</span> <span class="s">Analyze Oracle AWR reports to identify performance bottlenecks</span>
  <span class="s">and generate recommendations for database tuning.</span>
<span class="nn">---</span>
</code></pre></div></div>

<div class="language-markdown highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="gu">## Instructions</span>
<span class="p">
1.</span> Read the uploaded AWR report (HTML or text format)
<span class="p">2.</span> Identify the Top 5 Wait Events by DB Time percentage
<span class="p">3.</span> Cross-reference with the SQL Statistics section
<span class="p">4.</span> Check the Instance Efficiency Percentages
<span class="p">5.</span> Generate a summary with:
<span class="p">   -</span> Root cause analysis for each major wait event
<span class="p">   -</span> Specific init.ora parameter recommendations
<span class="p">   -</span> SQL tuning recommendations with evidence
<span class="p">6.</span> Format output as a structured report with severity levels
</code></pre></div></div>

<p>For someone who has spent years writing runbooks, this format should feel natural. The difference is that this runbook is not for a junior DBA to follow—it is for an <strong>AI agent</strong> to execute autonomously.</p>

<h3 id="progressive-disclosure-loading-context-on-demand">Progressive Disclosure: Loading Context On Demand</h3>

<p>One of the most important concepts from the guide is <strong>progressive disclosure</strong>—a three-level system for loading information efficiently:</p>

<table>
  <thead>
    <tr>
      <th>Level</th>
      <th>What Loads</th>
      <th>When It Loads</th>
      <th>IT Analogy</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><strong>Level 1</strong></td>
      <td>YAML frontmatter (name + description)</td>
      <td>Always loaded in the system prompt</td>
      <td>Service discovery — the AI knows what skills exist</td>
    </tr>
    <tr>
      <td><strong>Level 2</strong></td>
      <td>Full SKILL.md body with instructions</td>
      <td>Only when the AI determines the skill is relevant</td>
      <td>On-demand documentation lookup</td>
    </tr>
    <tr>
      <td><strong>Level 3</strong></td>
      <td>Reference files, scripts, templates</td>
      <td>Only when explicitly needed during execution</td>
      <td>Lazy loading of dependencies</td>
    </tr>
  </tbody>
</table>

<p>Why does this matter? Because <strong>context windows are like memory</strong>. Every token loaded into the context window is working memory consumed. If you dump 50 runbooks into a prompt, the AI’s performance degrades—just like an application with memory pressure.</p>

<p>Progressive disclosure is the AI equivalent of <strong>just-in-time resource allocation</strong>. Load what you need, when you need it.</p>

<p>For those managing large environments, this is analogous to how you architect monitoring solutions: you do not push every metric to every dashboard. You define tiers—high-level health checks always visible, detailed diagnostics available on drill-down, and raw telemetry accessible only when investigating specific incidents.</p>

<h2 id="building-your-ai-ecosystem-a-practical-architecture">Building Your AI Ecosystem: A Practical Architecture</h2>

<p>Now let us translate these concepts into a practical architecture that IT professionals can implement today.</p>

<h3 id="layer-1-the-foundation--ai-coding-assistants">Layer 1: The Foundation — AI Coding Assistants</h3>

<p>Your AI ecosystem starts with a capable AI assistant. Today, the leading options include:</p>

<ul>
  <li><strong>Claude</strong> (Anthropic) — via Claude.ai, Claude Code CLI, or API</li>
  <li><strong>Gemini</strong> (Google) — via Gemini CLI, Gemini Canvas, or API</li>
  <li><strong>ChatGPT</strong> (OpenAI) — via ChatGPT, Codex CLI, or API</li>
  <li><strong>GitHub Copilot</strong> — integrated IDE experience</li>
</ul>

<p>These are your <strong>compute engines</strong>. Just as you would not run production workloads on a single VM, you should not rely on a single AI tool. Each has strengths:</p>

<table>
  <thead>
    <tr>
      <th>Capability</th>
      <th>Best Suited For</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Deep reasoning and analysis</td>
      <td>Complex architecture reviews, root cause analysis</td>
    </tr>
    <tr>
      <td>Code generation</td>
      <td>Terraform/Ansible modules, shell scripts, SQL queries</td>
    </tr>
    <tr>
      <td>Document synthesis</td>
      <td>Runbook creation, incident post-mortems, design docs</td>
    </tr>
    <tr>
      <td>Multi-turn conversation</td>
      <td>Iterative debugging, exploratory analysis</td>
    </tr>
  </tbody>
</table>

<h3 id="layer-2-the-connective-tissue--model-context-protocol-mcp">Layer 2: The Connective Tissue — Model Context Protocol (MCP)</h3>

<p>MCP is an open protocol that gives AI assistants access to external tools and data sources. Think of it as <strong>an API gateway for AI agents</strong>.</p>

<p>For IT professionals, MCP servers can connect your AI to:</p>

<ul>
  <li><strong>Database systems</strong> — query execution, schema exploration, performance metrics</li>
  <li><strong>Cloud APIs</strong> — OCI, AWS, Azure, GCP resource management</li>
  <li><strong>Monitoring platforms</strong> — metrics queries, log analysis, alert management</li>
  <li><strong>Version control</strong> — Git operations, code review, change tracking</li>
  <li><strong>Ticketing systems</strong> — Jira, ServiceNow ticket creation and updates</li>
</ul>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>┌─────────────────────────────────────┐
│         AI Assistant (Claude)       │
│                                     │
│  ┌──────────┐  ┌──────────────┐     │
│  │  Skills   │  │   Memory     │     │
│  │ (Recipes) │  │  (Context)   │     │
│  └──────────┘  └──────────────┘     │
│                                     │
└─────────────┬───────────────────────┘
              │ MCP Protocol
    ┌─────────┼──────────┐
    │         │          │
    ▼         ▼          ▼
┌────────┐ ┌────────┐ ┌────────┐
│Database│ │ Cloud  │ │Monitor │
│ Server │ │  API   │ │  API   │
│(Oracle,│ │(OCI,   │ │(APM,   │
│ MySQL) │ │ AWS)   │ │ LA)    │
└────────┘ └────────┘ └────────┘
</code></pre></div></div>

<p>The power of MCP is that it transforms your AI from a <strong>conversational chatbot</strong> into an <strong>operational agent</strong> that can actually query your systems, analyze real data, and take actions.</p>

<h3 id="layer-3-the-intelligence--skills-library">Layer 3: The Intelligence — Skills Library</h3>

<p>This is where your institutional knowledge lives. Your skills library is a collection of <code class="language-plaintext highlighter-rouge">SKILL.md</code> files organized by domain:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>.agents/
├── skills/
│   ├── database/
│   │   ├── awr-analysis/
│   │   │   ├── SKILL.md
│   │   │   └── scripts/
│   │   │       └── parse_awr.py
│   │   ├── capacity-planning/
│   │   │   ├── SKILL.md
│   │   │   └── references/
│   │   │       └── sizing_guidelines.md
│   │   └── incident-response/
│   │       ├── SKILL.md
│   │       └── templates/
│   │           └── incident_report.md
│   ├── cloud/
│   │   ├── oci-deployment/
│   │   │   └── SKILL.md
│   │   └── cost-optimization/
│   │       └── SKILL.md
│   └── monitoring/
│       ├── log-analysis/
│       │   └── SKILL.md
│       └── alert-triage/
│           └── SKILL.md
└── workflows/
    ├── weekly-health-check.md
    └── incident-response.md
</code></pre></div></div>

<p>Each skill encodes a specific capability:</p>

<p><strong>Example: Database Incident Response Skill</strong></p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nn">---</span>
<span class="na">name</span><span class="pi">:</span> <span class="s">db-incident-response</span>
<span class="na">description</span><span class="pi">:</span> <span class="s">Triage and diagnose Oracle database performance incidents</span>
  <span class="s">using AWR, ASH, and system metrics. Generate structured incident reports.</span>
<span class="nn">---</span>
</code></pre></div></div>

<div class="language-markdown highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="gu">## Trigger Conditions</span>
Activate when the user reports:
<span class="p">-</span> Database performance degradation
<span class="p">-</span> Application timeout errors
<span class="p">-</span> High wait event alerts
<span class="p">-</span> ORA- errors in production

<span class="gu">## Workflow</span>

<span class="gu">### Phase 1: Triage (&lt; 5 minutes)</span>
<span class="p">1.</span> Query current active sessions: <span class="sb">`SELECT * FROM V$SESSION WHERE STATUS='ACTIVE'`</span>
<span class="p">2.</span> Check for blocking sessions: <span class="sb">`SELECT * FROM V$LOCK WHERE BLOCK &gt; 0`</span>
<span class="p">3.</span> Review latest AWR snapshot for Top Wait Events
<span class="p">4.</span> Classify severity: P1 (outage), P2 (degraded), P3 (warning)

<span class="gu">### Phase 2: Diagnosis (&lt; 15 minutes)</span>
<span class="p">1.</span> Generate ASH report for the incident window
<span class="p">2.</span> Identify top SQL by elapsed time
<span class="p">3.</span> Check for plan changes via DBA_HIST_SQL_PLAN
<span class="p">4.</span> Review system statistics (CPU, I/O, memory)

<span class="gu">### Phase 3: Report Generation</span>
Use the template in templates/incident_report.md to generate:
<span class="p">-</span> Timeline of events
<span class="p">-</span> Root cause analysis
<span class="p">-</span> Immediate actions taken
<span class="p">-</span> Long-term recommendations
</code></pre></div></div>

<p>This is your runbook, but supercharged. The AI does not just read it—it <strong>executes</strong> it, querying your actual database through MCP, analyzing real metrics, and generating a report you can hand to management.</p>

<h3 id="layer-4-the-memory--persistent-context">Layer 4: The Memory — Persistent Context</h3>

<p>One of the most transformative capabilities in modern AI systems is <strong>persistent memory</strong>—the ability for an AI to remember context across conversations.</p>

<p>For IT professionals, this means:</p>

<ul>
  <li><strong>Environment knowledge</strong>: The AI remembers your database versions, patch levels, cluster topology, and naming conventions</li>
  <li><strong>Historical context</strong>: Past incidents, performance baselines, and known issues</li>
  <li><strong>Team preferences</strong>: Your coding standards, documentation templates, and approval workflows</li>
  <li><strong>Project state</strong>: Where you left off on a migration, what has been tested, what remains</li>
</ul>

<p>This is the equivalent of having a team member who <strong>never forgets</strong> the institutional knowledge that typically lives in someone’s head or scattered across wikis.</p>

<p><strong>Practical implementation</strong>: AI tools like Claude support memory through knowledge items and conversation history. You can accelerate this by creating a structured context file:</p>

<div class="language-markdown highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="gh"># Environment Context</span>

<span class="gu">## Database Infrastructure</span>
<span class="p">-</span> Production: Oracle 19c RAC (2-node) on OCI BM.Standard.E4
<span class="p">-</span> Standby: Active Data Guard in different region
<span class="p">-</span> PDB architecture: 1 CDB, 4 PDBs (HR, FIN, SCM, CX)

<span class="gu">## Cloud Infrastructure  </span>
<span class="p">-</span> Primary region: us-ashburn-1
<span class="p">-</span> DR region: us-phoenix-1
<span class="p">-</span> Compartment structure: prod/nonprod/shared-services

<span class="gu">## Monitoring Stack</span>
<span class="p">-</span> OCI Logging Analytics for log consolidation
<span class="p">-</span> OCI APM for application monitoring
<span class="p">-</span> Custom metrics via OCI Monitoring API
<span class="p">-</span> Alerting via OCI Notifications + PagerDuty

<span class="gu">## Standards</span>
<span class="p">-</span> Terraform for all infrastructure provisioning
<span class="p">-</span> Ansible for database patching
<span class="p">-</span> Git branching: main → staging → feature/<span class="err">*</span>
<span class="p">-</span> Change management: ServiceNow tickets required for prod changes
</code></pre></div></div>

<h2 id="the-aiops-transformation-from-reactive-to-predictive">The AIOps Transformation: From Reactive to Predictive</h2>

<p>For IT operations teams, this AI ecosystem enables a fundamental shift in how you work:</p>

<h3 id="traditional-it-operations">Traditional IT Operations</h3>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Alert fires → Engineer investigates → Manual diagnosis → Fix applied
              (15-30 min)              (30-60 min)       (variable)
</code></pre></div></div>

<p>Each step requires context loading: <em>What environment is this? What changed recently? Has this happened before? What is the standard fix?</em></p>

<h3 id="ai-augmented-operations-aiops">AI-Augmented Operations (AIOps)</h3>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>Alert fires → AI agent triages with full context → Diagnosis + recommendations ready
              (&lt; 2 min)                             (&lt; 5 min)
</code></pre></div></div>

<p>The AI agent already knows your environment, has access to your monitoring data via MCP, and follows your incident response skill. Your role shifts from <strong>executor</strong> to <strong>reviewer and decision-maker</strong>.</p>

<h3 id="what-this-looks-like-in-practice">What This Looks Like in Practice</h3>

<p><strong>Scenario</strong>: A P2 database performance alert fires at 2 AM.</p>

<p><strong>Without AI ecosystem:</strong></p>
<ol>
  <li>On-call DBA receives page</li>
  <li>VPNs into the environment</li>
  <li>Tries to remember which database, which application</li>
  <li>Runs ad-hoc diagnostic queries</li>
  <li>Googles error codes</li>
  <li>Eventually identifies the issue</li>
  <li>Manually writes the incident report next morning</li>
</ol>

<p><strong>With AI ecosystem:</strong></p>
<ol>
  <li>On-call DBA receives page with AI-generated triage summary</li>
  <li>Summary includes: affected database, top wait events, suspect SQLs, comparison to historical baseline, and recommended actions</li>
  <li>DBA reviews the analysis, confirms the diagnosis</li>
  <li>AI generates the incident report with full evidence</li>
  <li>Total time: 15 minutes instead of 2 hours</li>
</ol>

<h2 id="getting-started-your-first-30-days">Getting Started: Your First 30 Days</h2>

<p>Here is a practical roadmap for building your AI ecosystem:</p>

<h3 id="week-1-foundation">Week 1: Foundation</h3>
<ul class="task-list">
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Set up Claude (or your preferred AI) with a professional plan</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Create your environment context file (see template above)</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Start a <code class="language-plaintext highlighter-rouge">.agents/</code> directory in your team’s Git repository</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Write your first <code class="language-plaintext highlighter-rouge">SKILL.md</code> for a task you do frequently</li>
</ul>

<h3 id="week-2-skills-development">Week 2: Skills Development</h3>
<ul class="task-list">
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Convert your top 3 most-used runbooks into skills</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Add reference files (scripts, templates, documentation)</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Test each skill by running through it with your AI assistant</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Iterate based on what the AI gets right and wrong</li>
</ul>

<h3 id="week-3-mcp-integration">Week 3: MCP Integration</h3>
<ul class="task-list">
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Explore available MCP servers for your technology stack</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Set up at least one MCP connection (database, cloud API, or monitoring)</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Create a skill that leverages MCP for real data analysis</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Document the integration for your team</li>
</ul>

<h3 id="week-4-team-adoption">Week 4: Team Adoption</h3>
<ul class="task-list">
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Share your skills library with your team</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Run a workshop demonstrating the AI ecosystem</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Collect feedback and prioritize the next set of skills to build</li>
  <li class="task-list-item"><input type="checkbox" class="task-list-item-checkbox" disabled="disabled" />Establish governance: who reviews and approves skills?</li>
</ul>

<h2 id="testing-and-quality-the-verification-loop">Testing and Quality: The Verification Loop</h2>

<p>Anthropic’s guide emphasizes that skills should be <strong>tested</strong> just like code. This resonates deeply with IT professionals who understand the importance of validation.</p>

<p>The guide recommends three levels of testing:</p>

<ol>
  <li>
    <p><strong>Manual Testing</strong>: Run through the skill interactively and verify the output matches expectations. This is your smoke test.</p>
  </li>
  <li>
    <p><strong>Scripted Testing</strong>: Create test scenarios with known inputs and expected outputs. For a database analysis skill, this might mean feeding it a sample AWR report and verifying it identifies the correct bottlenecks.</p>
  </li>
  <li>
    <p><strong>Metrics Monitoring</strong>: Track how often skills are triggered correctly, how many tool calls they make, and their failure rates. This is your SLA monitoring for AI operations.</p>
  </li>
</ol>

<p>The key metrics to watch:</p>

<table>
  <thead>
    <tr>
      <th>Metric</th>
      <th>Target</th>
      <th>Why It Matters</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Trigger accuracy</td>
      <td>&gt; 95%</td>
      <td>Does the right skill activate for the right task?</td>
    </tr>
    <tr>
      <td>Completion rate</td>
      <td>&gt; 90%</td>
      <td>Does the skill complete without errors?</td>
    </tr>
    <tr>
      <td>Tool call efficiency</td>
      <td>Minimize unnecessary calls</td>
      <td>Fewer calls = faster execution + lower cost</td>
    </tr>
    <tr>
      <td>Output quality</td>
      <td>Consistent with templates</td>
      <td>Does the output match your standards?</td>
    </tr>
  </tbody>
</table>

<h2 id="security-and-governance-operating-ai-in-enterprise-environments">Security and Governance: Operating AI in Enterprise Environments</h2>

<p>For IT professionals working in regulated environments, governance is non-negotiable. Here are the key considerations:</p>

<h3 id="data-classification">Data Classification</h3>
<ul>
  <li><strong>Never</strong> encode credentials, tokens, or secrets in skill files</li>
  <li>Use environment variables or secret management tools for sensitive configuration</li>
  <li>Classify your skills by the data sensitivity they handle</li>
</ul>

<h3 id="access-control">Access Control</h3>
<ul>
  <li>Store skills in version-controlled repositories with appropriate access controls</li>
  <li>Use code review processes for skill changes, just like infrastructure code</li>
  <li>Implement approval workflows for skills that interact with production systems</li>
</ul>

<h3 id="audit-and-compliance">Audit and Compliance</h3>
<ul>
  <li>Log all AI agent actions, especially those involving production systems</li>
  <li>Maintain an audit trail of skill executions and their outcomes</li>
  <li>Regularly review and update skills to reflect policy changes</li>
</ul>

<h3 id="responsible-use">Responsible Use</h3>
<ul>
  <li>Always have a human review AI-generated recommendations before applying to production</li>
  <li>Define clear escalation paths for when AI diagnosis is uncertain</li>
  <li>Establish boundaries: what can the AI do autonomously vs. what requires human approval?</li>
</ul>

<h2 id="the-bigger-picture-skills-as-a-cross-platform-standard">The Bigger Picture: Skills as a Cross-Platform Standard</h2>

<p>One of the most compelling aspects of the skills framework is that <code class="language-plaintext highlighter-rouge">SKILL.md</code> is an <strong>open standard</strong>. It works across:</p>

<ul>
  <li><strong>Claude Code</strong> (Anthropic)</li>
  <li><strong>Gemini CLI</strong> (Google)</li>
  <li><strong>OpenAI Codex</strong> (OpenAI)</li>
  <li><strong>Any AI assistant</strong> that can read Markdown files</li>
</ul>

<p>This means your investment in building skills is <strong>portable</strong>. If you switch AI providers—or use multiple providers for different tasks—your skills library moves with you. This is analogous to how Terraform provides cloud-agnostic infrastructure definitions: write once, execute anywhere.</p>

<p>For IT organizations evaluating AI tools, this portability significantly de-risks adoption. You are not locked into a vendor; you are building a <strong>knowledge asset</strong> that appreciates over time.</p>

<h2 id="conclusion-the-ai-architect-mindset">Conclusion: The AI Architect Mindset</h2>

<p>The transition from traditional IT operations to AI-augmented operations is not about learning a new tool. It is about adopting a new <strong>architecture mindset</strong>:</p>

<ol>
  <li>
    <p><strong>Think in systems, not prompts</strong>: Design your AI ecosystem as an architecture with layers, interfaces, and governance—not as a collection of chat conversations.</p>
  </li>
  <li>
    <p><strong>Encode knowledge, not just commands</strong>: Your institutional knowledge—runbooks, best practices, lessons learned—is your most valuable asset. Package it as skills so it can be leveraged consistently.</p>
  </li>
  <li>
    <p><strong>Design for progressive disclosure</strong>: Load context efficiently. Not everything needs to be in the prompt. Structure your knowledge so the AI can find what it needs, when it needs it.</p>
  </li>
  <li>
    <p><strong>Verify and iterate</strong>: Test your skills like you test your infrastructure. Monitor their effectiveness. Continuously improve them based on real-world usage.</p>
  </li>
  <li>
    <p><strong>Govern like production</strong>: Apply the same discipline to your AI ecosystem that you apply to your production environments—access control, change management, audit trails, and security reviews.</p>
  </li>
</ol>

<p>The AI Architect does not just use AI tools. They <strong>design the system</strong> in which AI tools operate most effectively—bringing together the right models, the right context, the right skills, and the right governance to create an ecosystem that amplifies the entire team’s capabilities.</p>

<p>In the next installments of this series, we will dive deeper into practical implementations: building MCP integrations for Oracle databases, creating monitoring skills for OCI, and designing AI-powered incident response workflows.</p>

<p>The future of IT operations is not AI replacing DBAs and Cloud Architects. It is AI <strong>making every DBA and Cloud Architect ten times more effective</strong>.</p>

<hr />

<h2 id="references">References</h2>

<ul>
  <li><a href="https://resources.anthropic.com/hubfs/The-Complete-Guide-to-Building-Skill-for-Claude.pdf">The Complete Guide to Building Skills for Claude (PDF)</a> — Anthropic</li>
  <li><a href="https://modelcontextprotocol.io/">Model Context Protocol (MCP) Documentation</a> — Anthropic</li>
  <li><a href="https://www.anthropic.com/engineering/building-effective-agents">Building Effective Agents</a> — Anthropic Engineering</li>
  <li><a href="https://docs.anthropic.com/en/docs/claude-code/overview">Claude Code Documentation</a> — Anthropic</li>
  <li><a href="https://docs.oracle.com/en-us/iaas/Content/Monitoring/home.htm">OCI Observability and Management</a> — Oracle Cloud Infrastructure</li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="AI Architecture" /><category term="AI Ecosystem" /><category term="AI Skills" /><category term="AI Coding Assistants" /><summary type="html"><![CDATA[AI Architect Series: How to Build an Efficient AI Ecosystem]]></summary></entry><entry><title type="html">Real User Monitoring for Oracle Fusion SaaS Cloud Apps with OCI APM Browser Agent</title><link href="https://royce-fu.com/blog/enabling-real-user-monitoring-for-oracle-fusion-saas-cloud-apps-with-oci-apm-browser-agent/" rel="alternate" type="text/html" title="Real User Monitoring for Oracle Fusion SaaS Cloud Apps with OCI APM Browser Agent" /><published>2026-03-06T00:00:00+00:00</published><updated>2026-09-15T16:23:30+00:00</updated><id>https://royce-fu.com/blog/enabling-real-user-monitoring-for-oracle-fusion-saas-cloud-apps-with-oci-apm-browser-agent</id><content type="html" xml:base="https://royce-fu.com/blog/enabling-real-user-monitoring-for-oracle-fusion-saas-cloud-apps-with-oci-apm-browser-agent/"><![CDATA[<h1 id="real-user-monitoring-for-oracle-fusion-saas-cloud-apps-with-oci-apm-browser-agent">Real User Monitoring for Oracle Fusion SaaS Cloud Apps with OCI APM Browser Agent</h1>

<p><strong>Authors:</strong> Royce Fu and Robert Brouwer, Software Development, OCI Application Performance Monitoring</p>

<h2 id="introduction">Introduction</h2>

<p>Oracle Fusion Applications represent one of the most comprehensive enterprise SaaS solutions, supporting critical business functions across Human Capital Management (HCM), Enterprise Resource Planning (ERP), Supply Chain Management (SCM), and Customer Experience (CX). As organizations increasingly rely on Fusion Cloud Apps for mission-critical operations, understanding the real user experience becomes paramount for ensuring optimal performance, identifying bottlenecks, and maintaining user satisfaction.</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/vmqymMFgmz0" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/enabling-real-user-monitoring-for-oracle-fusion-saas-cloud-apps-with-oci-apm-browser-agent.png" alt="Real User Monitoring for Oracle Fusion SaaS Cloud Apps with OCI APM Browser Agent — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>Oracle Cloud Infrastructure (OCI) Application Performance Monitoring (APM) Real User Monitoring (RUM) Browser Agent provides a powerful solution for gaining deep visibility into how users interact with Fusion Cloud Applications. By deploying the APM Browser Agent, organizations can monitor real user sessions, track page performance, analyze user behavior patterns, and correlate performance metrics with business outcomes—all from the browser perspective.</p>

<p>This blog post provides a comprehensive guide to implementing OCI APM RUM Browser Agent for Oracle Fusion SaaS Cloud Apps, covering both ADF (Application Development Framework) and Redwood page implementations, and exploring key use cases that enable data-driven performance optimization.</p>

<h2 id="reference-architecture-oci-apm-real-user-monitoring-for-oracle-fusion-saas-cloud-apps">Reference Architecture: OCI APM Real User Monitoring for Oracle Fusion SaaS Cloud Apps</h2>

<p>OCI APM Real User Monitoring captures user interaction data directly from the browser, providing comprehensive insights into the actual user experience. The APM Browser Agent records:</p>

<ul>
  <li><strong>Page Load Performance</strong>: Complete page load times, resource loading, and rendering metrics</li>
  <li><strong>User Interactions</strong>: Clicks, navigation patterns, and user session flows</li>
  <li><strong>AJAX Calls</strong>: API call performance and error rates</li>
  <li><strong>JavaScript Errors</strong>: Client-side errors that impact user experience</li>
  <li><strong>Geographic Data</strong>: User location-based performance analysis</li>
  <li><strong>Device Information</strong>: Browser, device type, and connection characteristics</li>
  <li><strong>Application Performance Index (Apdex)</strong>: Standardized performance scoring</li>
</ul>

<p>The APM Browser Agent sends browser spans and RUM metrics to OCI APM, where they can be visualized in <strong>Trace Explorer</strong> and <strong>Metrics Explorer</strong>, enabling comprehensive analysis of user experience across Fusion Cloud Applications. Beyond deep-dive analysis, this telemetry allows you to utilize out-of-the-box <strong>RUM Dashboards</strong> and define <strong>Custom Metrics</strong> to detect and alert on Fusion environment performance issues proactively.</p>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_ref_architecture.png" alt="Fusion Monitoring APM Reference Architecture" />
<em>Figure 1: OCI APM Real User Monitoring for Oracle Fusion SaaS Cloud Apps</em></p>

<h2 id="prerequisites">Prerequisites</h2>

<p>Before implementing APM RUM for Fusion Cloud Apps, ensure you have:</p>

<ol>
  <li><strong>OCI APM Domain</strong>: An active APM domain in your OCI tenancy
    <ul>
      <li>Follow these quick steps to create a domain:
        <ul>
          <li>Sign in to the Oracle Cloud Infrastructure console.</li>
          <li>Open the navigation menu, click <strong>Observability &amp; Management</strong>, and under Application Performance Monitoring, click <strong>Administration</strong>.</li>
          <li>Select your target compartment, click <strong>Create APM Domain</strong>, and fill in the required details (Name, Compartment, Description, etc.).</li>
          <li>Click <strong>Create APM domain</strong> and wait for the domain to be provisioned.</li>
        </ul>
      </li>
      <li>For full setup details, see <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/create-apm-domain.html">Create an APM Domain</a>.</li>
    </ul>
  </li>
  <li><strong>APM Data Key</strong>: The public data key from your APM domain
    <ul>
      <li>Navigate to APM Domain &gt; Resources &gt; Data Keys</li>
      <li>Copy the Public Data Key</li>
    </ul>
  </li>
  <li><strong>Data Upload Endpoint</strong>: The OCI data upload endpoint URL for your APM domain
    <ul>
      <li>Format: <code class="language-plaintext highlighter-rouge">https://&lt;domain-id&gt;.apm-agt.&lt;region&gt;.oci.oraclecloud.com</code></li>
      <li>Found in APM Domain &gt; Administration &gt; Data Upload Endpoint</li>
      <li>Copy the Data Upload Endpoint</li>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_data_key.png" alt="Fusion Monitoring APM Data Key and Data Upload Endpoint" /> <em>Figure 2: OCI APM Data Key and Data Upload Endpoint</em></li>
    </ul>
  </li>
  <li>
    <p><strong>ADF Sandbox Access</strong>: Ability to create and publish sandboxes in Fusion Applications</p>
  </li>
  <li><strong>Redwood Visual Builder Studio project access</strong>: Ability to export, import, preview, and publish an application-extension workspace for Fusion Redwood pages.
    <ul>
      <li><strong>Note</strong>: The Fusion role alone does not grant access to VB Studio — the user also needs a VB Studio role in the Identity Domain.</li>
      <li>If role synchronization is enabled (the common case), assign one of:
        <ul>
          <li><code class="language-plaintext highlighter-rouge">ORA_SYNC_ENABLED_ADMINISTRATOR_ABSTRACT</code> — maps to VB Studio Administrator</li>
          <li><code class="language-plaintext highlighter-rouge">ORA_SYNC_ENABLED_DEVELOPER_ABSTRACT</code> — maps to VB Studio Developer
<em>(These are assigned in the Fusion Security Console and auto-sync to the Identity Domain.)</em></li>
        </ul>
      </li>
      <li>If role synchronization is disabled, you must manually assign in the Identity Domain console:
        <ul>
          <li><code class="language-plaintext highlighter-rouge">DEVELOPER_ADMINISTRATOR</code> — VB Studio admin access (create projects, manage settings)</li>
          <li><code class="language-plaintext highlighter-rouge">DEVELOPER_USER</code> — VB Studio developer access (create/develop projects).</li>
        </ul>
      </li>
    </ul>
  </li>
</ol>

<h2 id="implementation-deploying-apm-browser-agent">Implementation: Deploying APM Browser Agent</h2>

<p>Oracle Fusion Applications consist of two distinct page architectures, each requiring a specific implementation approach:</p>

<ul>
  <li><strong>ADF Pages</strong>: Legacy pages identified by <code class="language-plaintext highlighter-rouge">/faces/</code> in the URL</li>
  <li><strong>Redwood Pages</strong>: Modern pages identified by <code class="language-plaintext highlighter-rouge">/redwood/</code> in the URL</li>
</ul>

<p>For complete coverage, you must implement the APM Browser Agent for both page types.</p>

<h3 id="part-1-adding-rum-agent-to-fusion-adf-pages">Part 1: Adding RUM Agent to Fusion ADF Pages</h3>

<p>ADF pages use a global page template that can be customized to include the APM Browser Agent across all ADF pages in your Fusion instance.</p>

<h4 id="step-1-access-global-page-template-editor">Step 1: Access Global Page Template Editor</h4>

<ol>
  <li>Log in to your Fusion Cloud Application</li>
  <li>Navigate to <strong>Settings</strong> &gt; <strong>Actions</strong> &gt; <strong>Edit Global Page Template</strong>
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_edit_global_page_template.png" alt="Fusion Monitoring APM Edit Global Page Template" /> <em>Figure 3: Edit Global Page Template</em></li>
    </ul>
  </li>
  <li>Create or activate a sandbox:
    <ul>
      <li>Click <strong>Activate a Sandbox</strong></li>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_activate_sandbox.png" alt="Fusion Monitoring APM Activate Sandbox" /> <em>Figure 4: Activate a Sandbox</em></li>
      <li>Select <strong>Page Template Composer</strong> option</li>
      <li>Click <strong>Create and Enter</strong></li>
      <li>Enter the sandbox by clicking on its name</li>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_create_sandbox.png" alt="Fusion Monitoring APM Create Sandbox" /> <em>Figure 5: Create Sandbox</em></li>
    </ul>
  </li>
</ol>

<h4 id="step-2-edit-the-template">Step 2: Edit the Template</h4>

<ol>
  <li>Click <strong>Edit Global Page Template</strong> from the menu (now that you’re in a sandbox)
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_edit_global_page_template_sandbox.png" alt="Fusion Monitoring APM Edit Global Page Template" /> <em>Figure 6: Edit Global Page Template</em></li>
    </ul>
  </li>
  <li>Ensure the page is in <strong>Design</strong> mode
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td>When active, you’ll see a bar with ‘Add content’</td>
              <td>‘Select’</td>
              <td>‘Structure’</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_design_mode.png" alt="Fusion Monitoring APM Design Mode" /> <em>Figure 7: Design Mode</em></li>
    </ul>
  </li>
  <li>Select <strong>Structure</strong> from that bar</li>
  <li>Click the <strong>”+”</strong> symbol at the bottom to add a new HTML markup component
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_add_component.png" alt="Fusion Monitoring APM Add Component" /> <em>Figure 8: Add Component</em></li>
    </ul>
  </li>
  <li>Select <strong>Component</strong> and click <strong>Add</strong> to add the HTML Markup, then <strong>Close</strong> the popup
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_add_component_2.png" alt="Fusion Monitoring APM Add Component" /> <em>Figure 9: Add Component</em></li>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_add_component_3.png" alt="Fusion Monitoring APM Add Component" /> <em>Figure 10: Add Component</em></li>
    </ul>
  </li>
  <li>Switch to <strong>Add Content</strong> tab and click the <strong>gear setting button</strong> of the <strong>HTML Markup</strong> component</li>
  <li>Open the Expression by clicking the settings icon
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_open_expression.png" alt="Fusion Monitoring APM Open Expression" /> <em>Figure 11: Open Expression</em></li>
    </ul>
  </li>
  <li>Click <strong>Expression Builder</strong>
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_expression_builder.png" alt="Fusion Monitoring APM Expression Builder" /> <em>Figure 12: Expression Builder</em></li>
    </ul>
  </li>
</ol>

<h4 id="step-3-add-apm-browser-agent-script">Step 3: Add APM Browser Agent Script</h4>

<p>In the Expression Builder, add the following HTML markup:</p>

<div class="language-html highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c">&lt;!-- APM RUM Library --&gt;</span>
<span class="c">&lt;!-- Note: static.oracle.com requires maintenance to update the version --&gt;</span>
<span class="c">&lt;!-- Alternative: Use region-specific script if needed --&gt;</span>
<span class="nt">&lt;script </span><span class="na">type=</span><span class="s">"text/javascript"</span> <span class="na">crossorigin=</span><span class="s">"anonymous"</span> <span class="na">src=</span><span class="s">"https://static.oracle.com/cdn/apm/oci/1.1/1.1-1xx/1.1-148/apmrum.fus.base.combi.min.js"</span><span class="nt">&gt;&lt;/script&gt;</span>

<span class="nt">&lt;script </span><span class="na">type=</span><span class="s">"text/javascript"</span><span class="nt">&gt;</span>
<span class="kd">function</span> <span class="nx">initializeAPMRumConf</span><span class="p">()</span> <span class="p">{</span>
  <span class="kd">const</span> <span class="nx">apmRumConfig</span> <span class="o">=</span> <span class="nb">document</span><span class="p">.</span><span class="nx">apmrum</span> <span class="o">||</span> <span class="nb">window</span><span class="p">.</span><span class="nx">apmrum</span> <span class="o">||</span> <span class="p">(</span><span class="nb">document</span><span class="p">.</span><span class="nx">apmrum</span> <span class="o">=</span> <span class="p">{});</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">custEP</span> <span class="o">=</span> <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">custEP</span> <span class="o">||</span> <span class="p">{};</span>
  
  <span class="cm">/* CUSTOMER SPECIFIC VALUES */</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">custEP</span><span class="p">.</span><span class="nx">OracleAPMPublicDataKey</span> <span class="o">=</span> <span class="dl">'</span><span class="s1">YOUR_PUBLIC_DATA_KEY</span><span class="dl">'</span><span class="p">;</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">custEP</span><span class="p">.</span><span class="nx">ociDataUploadEndpoint</span> <span class="o">=</span> <span class="dl">'</span><span class="s1">https://YOUR_DOMAIN_ID.apm-agt.us-phoenix-1.oci.oraclecloud.com</span><span class="dl">'</span><span class="p">;</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">custEP</span><span class="p">.</span><span class="nx">serviceName</span> <span class="o">=</span> <span class="dl">'</span><span class="s1">Fusion</span><span class="dl">'</span><span class="p">;</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">custEP</span><span class="p">.</span><span class="nx">webApplication</span> <span class="o">=</span> <span class="dl">'</span><span class="s1">ADF-Page</span><span class="dl">'</span><span class="p">;</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">traceSupportingEndpoints</span> <span class="o">=</span> <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">traceSupportingEndpoints</span> <span class="o">||</span> <span class="p">[</span>
    <span class="p">{</span> <span class="na">headers</span><span class="p">:</span> <span class="p">[],</span> <span class="na">hostPattern</span><span class="p">:</span> <span class="dl">'</span><span class="s1">.*</span><span class="dl">'</span> <span class="p">}</span>
  <span class="p">];</span>
  
  <span class="cm">/* Uncomment the lines below only after the required privacy review. */</span>
  <span class="c1">// apmRumConfig.custEP.trackPlainUserId = true;</span>
  <span class="c1">// apmRumConfig.trackPlainUserId = true;</span>
  <span class="c1">// apmRumConfig.trackScreenText = true;</span>
  
  <span class="cm">/* END OF CUSTOMER SPECIFIC SETTINGS */</span>
  <span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">confInst</span> <span class="o">=</span> <span class="p">(</span><span class="nx">apmRumConfig</span><span class="p">.</span><span class="nx">confInst</span> <span class="o">||</span> <span class="k">new</span> <span class="nb">Set</span><span class="p">()).</span><span class="nx">add</span><span class="p">(</span><span class="dl">'</span><span class="s1">custEP</span><span class="dl">'</span><span class="p">);</span>
<span class="p">}</span>
<span class="nx">initializeAPMRumConf</span><span class="p">();</span>
<span class="nt">&lt;/script&gt;</span>
</code></pre></div></div>

<p><strong>Configuration Notes:</strong></p>
<ul>
  <li>Replace <code class="language-plaintext highlighter-rouge">YOUR_PUBLIC_DATA_KEY</code> with your APM domain’s public data key</li>
  <li>Replace <code class="language-plaintext highlighter-rouge">YOUR_DOMAIN_ID.apm-agt.us-phoenix-1.oci.oraclecloud.com</code> with your actual data upload endpoint</li>
  <li>Adjust the region in the endpoint URL to match your APM domain region</li>
  <li>The <code class="language-plaintext highlighter-rouge">webApplication</code> value is set to <code class="language-plaintext highlighter-rouge">'ADF-Page'</code> to identify ADF pages in APM</li>
  <li>Screen-text collection and plain user-name reporting remain disabled unless you explicitly enable them after the required privacy and security review</li>
</ul>

<p><strong>User ID Hashing</strong>:</p>
<ul>
  <li>By default, APM hashes user IDs to protect privacy</li>
  <li>To track plain text user IDs (for debugging), uncomment: <code class="language-plaintext highlighter-rouge">apmRumConfig.custEP.trackPlainUserId = true;</code></li>
  <li><strong>Warning</strong>: Only enable plain text user IDs if required for troubleshooting and ensure compliance with privacy regulations</li>
</ul>

<p><strong>Personally Identifiable Information (PII)</strong>:</p>
<ul>
  <li>Review APM documentation on <a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/hide-personally-identifiable-information-pii.html">Hiding Personally Identifiable Information</a></li>
  <li>Configure PII masking if your application contains sensitive user data</li>
  <li>Ensure compliance with GDPR, CCPA, and other privacy regulations</li>
</ul>

<h4 id="set-the-content-security-policy-header">Set the Content-Security-Policy Header</h4>

<p>The browser must be permitted to load the APM RUM library from the location used in the script. Add either <code class="language-plaintext highlighter-rouge">static.oracle.com</code> or your region-specific <code class="language-plaintext highlighter-rouge">ingest-rum.apm-agt.&lt;region&gt;.oci.oraclecloud.com</code> host to the applicable ADF Content-Security-Policy <code class="language-plaintext highlighter-rouge">ALLOWED_ORIGINS</code> configuration. Preserve any origins that are already configured. The APM data upload endpoint must also be permitted for outbound browser connections. See <a href="https://docs.oracle.com/en/middleware/developer-tools/adf/12.2.1.4/develop-faces/adf-faces-configuration.html">ADF Faces Configuration</a> and <a href="https://docs.oracle.com/en/education/customer-success/guided-learning/ogl-faq/content-security-policy-csp-error-correction.html">Content Security Policy Error Correction</a>.</p>

<h4 id="step-4-publish-the-changes">Step 4: Publish the Changes</h4>

<ol>
  <li>Click <strong>Apply</strong> or <strong>Save</strong> to close the popup</li>
  <li>Click <strong>Publish</strong></li>
  <li>Click <strong>Yes</strong> in the confirmation dialog
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_publish.png" alt="Fusion Monitoring APM Publish" /> <em>Figure 13: Publish</em></li>
    </ul>
  </li>
</ol>

<p>The APM Browser Agent is now deployed to all ADF pages in your Fusion instance.</p>

<h3 id="part-2-adding-rum-agent-to-fusion-redwood-pages">Part 2: Adding RUM Agent to Fusion Redwood Pages</h3>

<p>Starting from Oracle Fusion Release 26C, the earlier approach of adding JavaScript to the <strong>Unified Module</strong> in <strong>Advanced</strong> mode is no longer used. Instead, the Fusion APM RUM Assistant transforms a current Visual Builder workspace export into an importable ZIP, embeds the browser agent and shared APM configuration, and activates the module in the eligible Redwood App UI overrides selected for that extension. The administrator does not need to edit JavaScript or JSON.</p>

<blockquote>
  <p><strong>Access:</strong> To request access to the Fusion APM RUM Assistant, contact your Oracle account team so they can engage the development team, or open a My Oracle Support service request for additional support.</p>
</blockquote>

<blockquote>
  <p><strong>Deployment boundary:</strong> Generate and review the ZIP locally, then import it into a non-production Visual Builder workspace first. Treat Preview, RUM upload verification, and publication as separate administrator approval gates. Keep the original workspace export as the rollback artifact.</p>
</blockquote>

<h4 id="step-1-open-the-current-workspace-from-a-redwood-page">Step 1: Open the Current Workspace from a Redwood Page</h4>

<ol>
  <li>
    <p>Navigate to any Redwood page in your Fusion application. For example, navigate to <strong>Me</strong> &gt; <strong>Journeys</strong>, or another Redwood page you know.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_redwood_page.png" alt="Fusion Redwood page" /> <em>Figure 14: Redwood page</em></p>
  </li>
  <li>Click the <strong>Profile</strong> icon in the upper-right corner.</li>
  <li>
    <p>Select <strong>Edit the Page in Visual Builder Studio</strong>.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_edit_page_in_visual_builder_studio.png" alt="Edit the page in Visual Builder Studio" /> <em>Figure 15: Edit the page in Visual Builder Studio</em></p>

    <p>The first time you access this option, Fusion automatically creates a Git repository for your Oracle Application or App Extension project. This is a one-time activity.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_git_repository.png" alt="Visual Builder Studio Git repository" /> <em>Figure 16: Git repository</em></p>
  </li>
</ol>

<h4 id="step-2-export-the-current-workspace">Step 2: Export the Current Workspace</h4>

<ol>
  <li>
    <p>The project Git repository opens and displays the page template.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_page_template.png" alt="Visual Builder Studio page template" /> <em>Figure 17: Page template</em></p>
  </li>
  <li>
    <p>From the menu in the upper-right corner, select <strong>Export</strong>. The downloaded archive contains the current files from the workspace branch.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_visual_builder_import_export_menu.png" alt="Visual Builder menu with Export highlighted" /> <em>Figure 18: Export and Import are available from the Visual Builder workspace menu</em></p>
  </li>
  <li>
    <p>Keep this original ZIP unchanged as the rollback copy. Run the assistant against a copy of this current export, not against an older generated APM ZIP.</p>
  </li>
</ol>

<p>For more information, see <a href="https://docs.oracle.com/en/cloud/paas/visual-builder/visualbuilder-building-appui/export-your-workspace-archive.html">Export Your Workspace as an Archive</a>.</p>

<h4 id="step-3-prepare-and-start-the-assistant">Step 3: Prepare and Start the Assistant</h4>

<ol>
  <li>Extract <code class="language-plaintext highlighter-rouge">fusion-apm-rum-assistant.zip</code> into a private working folder.</li>
  <li>Copy the Fusion workspace export into the assistant’s <code class="language-plaintext highlighter-rouge">downloads</code> folder.</li>
  <li>Start the assistant:
    <ul>
      <li><strong>macOS:</strong> Double-click <strong>Fusion APM RUM Assistant.command</strong>.</li>
      <li><strong>Windows:</strong> Double-click <strong>Fusion APM RUM Assistant.bat</strong>.</li>
    </ul>
  </li>
  <li>If prompted that Python 3 is unavailable, ask your local IT team to install Python 3 and then start the assistant again.</li>
</ol>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_assistant_folder.png" alt="Fusion APM RUM Assistant folder showing the launchers, downloads folder, and output folder" /> <em>Figure 19: Fusion APM RUM Assistant working folder on macOS; environment-specific archive names are redacted</em></p>

<p>On the first run, enter the following values from the target OCI APM domain:</p>

<ul>
  <li><strong>OCI region:</strong> The region containing the APM domain. The assistant uses this region to obtain the browser agent while generating the ZIP.</li>
  <li><strong>APM public data key:</strong> Found under <strong>APM domain details</strong> &gt; <strong>Data Keys</strong> &gt; <strong>Public Data Key</strong>.</li>
  <li><strong>APM data upload endpoint:</strong> Shown in the APM domain details. Copy it directly and confirm that it is the HTTPS <code class="language-plaintext highlighter-rouge">apm-agt</code> endpoint for the intended APM domain and OCI realm; do not substitute a general-purpose HTTPS URL. This assistant version checks the URL format but does not prove that the host belongs to the intended APM domain, so this manual comparison is required.</li>
</ul>

<p>The local configuration is stored in the extracted assistant folder for reuse. The generated ZIP also contains deployment-specific APM settings, so keep both the working folder and generated ZIP within the approved deployment process. The assistant writes <code class="language-plaintext highlighter-rouge">trackScreenText: false</code> and <code class="language-plaintext highlighter-rouge">trackPlainUserId: false</code> in its customer configuration. Static inspection of this package also found that the embedded Fusion base library initializes a separate <code class="language-plaintext highlighter-rouge">fusBaseConfig.trackPlainUserId</code> value to <code class="language-plaintext highlighter-rouge">true</code>. Treat the effective user-name behavior as unresolved until the target APM data confirms that identity is hashed or omitted, and do not publish if plain identifiers appear.</p>

<h4 id="step-4-select-the-fusion-app-ui-scope">Step 4: Select the Fusion App UI Scope</h4>

<p>The assistant asks two scope questions. Both default to <strong>No</strong>:</p>

<ol>
  <li><strong>Refresh the stored App UI catalog from Fusion?</strong>
    <ul>
      <li>Choose <strong>No</strong> to use the saved catalog, or when you only want to instrument App UIs already represented in the exported workspace.</li>
      <li>Choose <strong>Yes</strong> for first-time pillar expansion or after Fusion changes. Enter the Fusion pod host name when prompted. The assistant downloads the pod’s current <code class="language-plaintext highlighter-rouge">app-ui-info</code> catalog and saves it beside the local APM configuration.</li>
      <li>If the pod returns an interactive sign-in page instead of the catalog, download the catalog URL through an authenticated Fusion browser session, save it as <code class="language-plaintext highlighter-rouge">config/app-ui-info.json</code>, and run the assistant again without refreshing it.</li>
    </ul>
  </li>
  <li><strong>Add all eligible App UIs in one Fusion pillar?</strong>
    <ul>
      <li>Choose <strong>No</strong> to use only the App UIs already present in the export.</li>
      <li>Choose <strong>Yes</strong>, then enter exactly one pillar: <code class="language-plaintext highlighter-rouge">hcm</code>, <code class="language-plaintext highlighter-rouge">cx</code>, <code class="language-plaintext highlighter-rouge">erp</code>, or <code class="language-plaintext highlighter-rouge">scm</code>. A comma-separated list is not accepted.</li>
    </ul>
  </li>
</ol>

<p>Each generated ZIP covers one selected pillar. To instrument another pillar, start from that pillar’s corresponding extension/workspace export and create a separate output; rerunning against the same original export does not combine pillars.</p>

<p>Pillar expansion includes only applications that the catalog explicitly identifies as extensible. In this mode, the assistant deliberately excludes <code class="language-plaintext highlighter-rouge">unified-module</code>, creates the selected App UI override directories, merges the required provider dependencies, and applies the shared APM RUM module import. When you choose <strong>No</strong> for pillar expansion, the assistant applies the import to every App UI directory already present in the export. Because this package version does not remove an existing <code class="language-plaintext highlighter-rouge">unified-module</code> directory in that mode, confirm that the source workspace does not contain a <code class="language-plaintext highlighter-rouge">unified-module</code> App UI override before proceeding.</p>

<p>If the <code class="language-plaintext highlighter-rouge">downloads</code> folder contains several Fusion export ZIPs, select the intended archive from the numbered list.</p>

<h5 id="review-the-generation-summary">Review the Generation Summary</h5>

<p>Do not import the generated ZIP until the summary matches the intended scope. Review these lines in particular:</p>

<ul>
  <li><strong>Extension</strong> and <strong>Manifest:</strong> Confirm the expected application extension and export format.</li>
  <li><strong>Expansion pillar:</strong> Confirm the one intended business pillar.</li>
  <li><strong>Catalog applications selected:</strong> Confirm that eligible App UIs were found.</li>
  <li><strong>Applications created</strong> and <strong>Applications updated:</strong> At least one of these values must be greater than zero. If both are zero, the ZIP contains APM resources but does not activate RUM in any App UI; correct the export or select the confirmed pillar and rerun the assistant.</li>
  <li><strong>Created:</strong> Record the exact output ZIP that will be imported.</li>
</ul>

<p>In one validated HCM packaging run, the current pod catalog contained 199 HCM applications: 174 were marked extensible and added, 25 were skipped, 93 provider dependencies were added, and <code class="language-plaintext highlighter-rouge">unified-module</code> was excluded. These counts describe that pod and release only; expect them to change across Fusion environments and updates.</p>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_assistant_generation_summary.png" alt="Fusion APM RUM Assistant terminal summary showing a successful HCM pillar-expansion packaging run" /> <em>Figure 20: Successful HCM pillar-expansion packaging summary; environment-specific identifiers and local paths are redacted</em></p>

<blockquote>
  <p><strong>Validation scope:</strong> This result validates local macOS packaging and the structure of that generated HCM ZIP. It does not by itself validate Windows execution, Visual Builder import or build, live RUM delivery, privacy behavior, or CSP. Complete the non-production checks in Step 5 before publishing. The displayed <strong>Agent source</strong> is the packaging-time download source; the generated extension embeds that library for runtime use.</p>
</blockquote>

<h4 id="step-5-import-preview-verify-and-publish">Step 5: Import, Preview, Verify, and Publish</h4>

<ol>
  <li>Return to the same Visual Builder workspace used for the export.</li>
  <li>Confirm that no one has changed the workspace since the source export was created. If it has changed, export a fresh rollback ZIP, rerun the assistant against that archive, and review the new output before importing.</li>
  <li>From the upper-right menu, select <strong>Import</strong> and choose the <code class="language-plaintext highlighter-rouge">*-with-apm-rum.zip</code> file from the assistant’s <code class="language-plaintext highlighter-rouge">output</code> folder.</li>
  <li>
    <p>When replacing the workspace from this complete generated export, select <strong>Delete existing files and resources</strong> to prevent duplication, then click <strong>Import</strong>. See <a href="https://docs.oracle.com/en/cloud/paas/visual-builder/visualbuilder-building-appui/import-resources-your-workspace.html">Import Resources to Your Workspace</a>.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_redwood_import.png" alt="Import the generated APM RUM ZIP into the Visual Builder workspace" /> <em>Figure 21: Import the generated APM RUM ZIP</em></p>
  </li>
  <li>Review the import result and build messages. A large pillar-wide extension can require additional processing time; the published Fusion runtime remains unchanged until you select <strong>Publish</strong>.</li>
  <li>
    <p>Preview representative Redwood user workflows in the selected App UIs to generate RUM activity. Do not publish yet.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_preview_run.png" alt="Preview a representative Redwood user workflow" /> <em>Figure 22: Preview a representative Redwood user workflow before publishing</em></p>
  </li>
  <li>
    <p>Wait 5–10 minutes, then open the browser Developer Tools <strong>Network</strong> tab. Filter for <code class="language-plaintext highlighter-rouge">apm</code>, or more narrowly for <code class="language-plaintext highlighter-rouge">observations/public-span</code>, and confirm that the APM data upload endpoint returns HTTP <code class="language-plaintext highlighter-rouge">200</code> or <code class="language-plaintext highlighter-rouge">204</code>.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_preview_network_inspector.png" alt="Verify the APM upload response in the browser Network tab" /> <em>Figure 23: Verify the APM upload response in the browser Network tab</em></p>
  </li>
  <li>In the intended APM domain, confirm the new activity in <strong>Trace Explorer</strong> or the <strong>Real User Monitoring</strong> dashboard. Verify the expected <code class="language-plaintext highlighter-rouge">ServiceName</code> and <code class="language-plaintext highlighter-rouge">WebApplication</code>, and confirm that privacy-sensitive values are not reported.</li>
  <li>Click <strong>Publish</strong> only after the preview and APM checks succeed. This deploys the changes to the eligible Redwood App UIs included in the imported extension.</li>
</ol>

<p>The generated extension embeds the browser-agent library in its APM module. At runtime, the App UI should therefore not fetch the library from <code class="language-plaintext highlighter-rouge">static.oracle.com</code> or an <code class="language-plaintext highlighter-rouge">ingest-rum</code> host. The browser still uploads RUM observations to the configured APM data upload endpoint, which must be allowed by the application’s Content-Security-Policy <code class="language-plaintext highlighter-rouge">connect-src</code> rules. A CSP error in the browser console or a missing <code class="language-plaintext highlighter-rouge">200</code>/<code class="language-plaintext highlighter-rouge">204</code> upload response indicates that the connection policy or network path still needs attention.</p>

<p>If validation fails, do not publish. Retain the assistant configuration, catalog, source export, generated ZIP, and validation result as the deployment record; use the untouched source export to restore the workspace if rollback is required.</p>

<h3 id="part-3-configure-apm-domain-enrichment-rules">Part 3: Configure APM Domain Enrichment Rules</h3>

<p>For complete Fusion coverage, enable the Oracle-provided Fusion (FUS) span rule to add Fusion-specific attributes and dimensions to your traces.</p>

<h4 id="enable-fusion-enrichment-rule">Enable Fusion Enrichment Rule</h4>

<ol>
  <li>Navigate to your OCI APM Domain</li>
  <li>Go to <strong>Administration</strong> &gt; <strong>Span Rules</strong></li>
  <li>Click <strong>Create Span Enrichment</strong>
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_create_span_enrichment.png" alt="Fusion Monitoring APM Create Span Enrichment" /> <em>Figure 24: Create Span Enrichment</em></li>
    </ul>
  </li>
  <li>Select <strong>Oracle Provided</strong> span rules</li>
  <li>Find and add the <strong>“FUS”</strong> rule
    <ul>
      <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_add_span_enrichment_rule.png" alt="Fusion Monitoring APM Add Span Enrichment Rule" /> <em>Figure 25: Add Span Enrichment Rule</em></li>
    </ul>
  </li>
</ol>

<p>This enrichment rule creates the following Fusion-specific attributes:</p>

<ul>
  <li><strong>RwApplication</strong>: Identifies the Redwood application</li>
  <li><strong>RwPath</strong>: Captures the Redwood page path</li>
  <li><strong>RwContainer</strong>: Identifies the Redwood container</li>
  <li><strong>FusFamily</strong>: Describes the Fusion area where activity occurred (e.g., HCM, ERP, SCM, CX)</li>
</ul>

<p>These attributes enable powerful filtering and analysis capabilities in APM Trace Explorer and Metrics Explorer.</p>

<h3 id="part-4-verify-application-performance-monitoring-browser-agent-deployment">Part 4: Verify Application Performance Monitoring Browser Agent Deployment</h3>

<p>To generate some monitoring data and verify the setup, use the application you are configuring:</p>

<ul>
  <li><strong>Generate Data:</strong> Use the application you are setting up the monitoring for to generate initial monitoring data.</li>
  <li><strong>View in APM:</strong> Go to the APM Trace explorer page to see the data loaded. For example, see APM screenshots below.</li>
  <li><strong>Check privacy settings:</strong> For ADF, leave the plain-user-name and screen-text lines commented unless their use has completed privacy and security review. For Redwood, do not infer the effective setting from the generated customer configuration alone because the embedded Fusion base library has its own user-name setting. Confirm that the resulting APM data does not expose plain user names or screen text before publishing.</li>
</ul>

<p>If needed, verify that the APM data upload url (<code class="language-plaintext highlighter-rouge">window.apmrum.ociDataUploadEndpoint</code>) is reachable by doing the following:</p>

<ul>
  <li>Go to your application and use the Developer Tools in your browser to go to the Developer console. In most browsers, you can start the Developer Console by pressing the F12 key.</li>
  <li>Select the Network tab and filter the URL list by <code class="language-plaintext highlighter-rouge">observations/public-span</code>, if required.</li>
  <li>
    <p>The Collector URL should be displayed with the 200 or 204 HTTP response code. If you do not see a 200 or 204 HTTP response code, then the browser is not able to access the Collector URL.</p>
  </li>
  <li><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_network_tab.png" alt="Fusion Monitoring APM Network Tab" /> <em>Figure 26: Network Tab</em></li>
</ul>

<h2 id="utilize-the-apm-real-user-monitoring-dashboard-to-monitor-user-behavior-and-application-performance">Utilize the APM Real User Monitoring Dashboard to monitor user behavior and application performance</h2>

<p>OCI Application Performance Monitoring provides an out-of-the-box <strong>Real User Monitoring (RUM) Dashboard</strong> that offers immediate, high-level visibility into your Fusion Cloud Apps performance without requiring any custom queries.</p>

<p>To access the RUM Dashboard:</p>
<ol>
  <li>Navigate to <strong>Observability &amp; Management</strong> in the Oracle Cloud Console.</li>
  <li>Navigate to <strong>Application Performance Monitoring</strong>, and click <strong>Real User Monitoring</strong>.</li>
  <li>Use the global filters at the top to select your compartment, APM domain, Web Application and the desired time frame.</li>
</ol>

<p>The RUM Dashboard visualizes critical performance metrics across several key dimensions automatically:</p>
<ul>
  <li><strong>Apdex Score</strong>: Monitor the overall satisfaction of your users in a single aggregate performance score.</li>
  <li><strong>Page Performance</strong>: Track the exact, real-world time it takes for your Redwood and ADF pages to render for users.</li>
  <li><strong>Page Views &amp; Sessions</strong>: View user engagement trends and active sessions over time to understand peak traffic periods.</li>
  <li><strong>Geographic Breakdown</strong>: Visually analyze which regions and countries your users are connecting from, and identify location-specific performance latency.</li>
  <li><strong>Client &amp; Browser Breakdown</strong>: Understand the device types, operating systems, and browsers your users depend on to access Fusion.</li>
  <li><strong>Top Slowest Pages</strong>: Instantly pinpoint the specific Fusion pages currently exhibiting the poorest performance to prioritize code and network optimizations.</li>
</ul>

<p>This built-in dashboard serves as an excellent starting point for everyday monitoring, performance reporting, and quickly diagnosing macro-level user experience issues without ever looking at the raw telemetry data.</p>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_dashboard.png" alt="Fusion Monitoring APM RUM Dashboard" /> <em>Figure 27: RUM Dashboard</em></p>

<h2 id="gain-additional-insights-from-rum-data">Gain additional insights from RUM Data</h2>

<p>Once the APM Browser Agent is deployed and the Fusion span enrichment rules are configured, you can leverage the newly populated attributes (such as <code class="language-plaintext highlighter-rouge">RwApplication</code>, <code class="language-plaintext highlighter-rouge">RwContainer</code>, <code class="language-plaintext highlighter-rouge">RwPath</code>, <code class="language-plaintext highlighter-rouge">FusFamily</code>, <code class="language-plaintext highlighter-rouge">FusProductCode</code>, <code class="language-plaintext highlighter-rouge">FusComponentType</code>, etc.) to gain deeper, custom insights from your RUM data across various use cases:</p>

<h3 id="use-case-1-fusion-cloud-apps-pages-clicks-by-user">Use Case 1: Fusion Cloud Apps Pages Clicks by User</h3>

<p>Understand which Fusion pages users access most frequently and identify user navigation patterns.</p>

<p><em>For Redwood Pages:</em></p>
<div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="k">show</span> <span class="n">spans</span> <span class="o">*</span>  <span class="k">group</span> <span class="k">by</span> <span class="n">RwApplication</span><span class="p">,</span><span class="n">RwContainer</span><span class="p">,</span><span class="n">RwPath</span>
</code></pre></div></div>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_redwood_pages_analysis.png" alt="Fusion Monitoring APM RUM Redwood Pages Analysis" /> <em>Figure 28: Redwood Pages Analysis</em></p>

<p><em>For ADF Pages:</em></p>
<div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="k">show</span> <span class="n">spans</span> <span class="o">*</span>  <span class="k">group</span> <span class="k">by</span> <span class="n">FusFamily</span><span class="p">,</span><span class="n">FusProductCode</span><span class="p">,</span><span class="n">FusComponentType</span><span class="p">,</span><span class="n">FusContextRoot</span><span class="p">,</span><span class="n">FusRegionId</span>
</code></pre></div></div>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_adf_pages_analysis.png" alt="Fusion Monitoring APM RUM ADF Pages Analysis" /> <em>Figure 29: ADF Pages Analysis</em></p>

<h3 id="use-case-2-user-session-performance-profiling">Use Case 2: User Session Performance Profiling</h3>

<p>Analyze the sequence of events and performance bottlenecks within individual user sessions.</p>

<div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="k">show</span> <span class="p">(</span><span class="n">traces</span><span class="p">)</span> <span class="o">*</span> <span class="k">where</span> <span class="n">SessionId</span><span class="o">=</span><span class="s1">'&lt;your_session_id&gt;'</span> <span class="k">order</span> <span class="k">by</span> <span class="n">TraceRootSpanStartTime</span> <span class="k">asc</span>
</code></pre></div></div>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_user_session_analysis.png" alt="Fusion Monitoring APM RUM User Session Analysis" /> <em>Figure 30: User Session Analysis</em></p>

<h3 id="use-case-3-comprehensive-application-usage-and-engagement">Use Case 3: Comprehensive Application Usage and Engagement</h3>

<p>Analyze user engagement across both ADF modules and Redwood pages by aggregating the number of unique sessions, users, and total pageviews for each application area, ordered by highest session volume.</p>

<div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="k">SHOW</span> <span class="n">traces</span>  <span class="n">FusFamily</span> <span class="o">||</span><span class="s1">'-'</span><span class="o">||</span> <span class="n">FusProduct</span> <span class="k">as</span> <span class="nv">"baseDetails"</span><span class="p">,</span><span class="n">RwApplication</span> <span class="o">||</span><span class="s1">'-'</span><span class="o">||</span> <span class="n">RwContainer</span> <span class="o">||</span><span class="s1">'-'</span><span class="o">||</span><span class="n">RwPath</span> <span class="k">as</span> <span class="n">RedwoodDetails</span><span class="p">,</span> <span class="n">count_distinct</span><span class="p">(</span><span class="n">sessionId</span><span class="p">)</span> <span class="k">as</span> <span class="n">sessions</span><span class="p">,</span> <span class="n">count_distinct</span><span class="p">(</span><span class="n">username</span><span class="p">)</span> <span class="k">as</span> <span class="n">users</span><span class="p">,</span> <span class="k">sum</span><span class="p">(</span><span class="n">pageviews</span><span class="p">)</span> <span class="k">as</span> <span class="n">activities</span>
   <span class="k">where</span> <span class="n">RwApplication</span> <span class="k">is</span> <span class="k">not</span> <span class="n">omitted</span> <span class="k">or</span> <span class="n">FusFamily</span> <span class="k">is</span> <span class="k">not</span> <span class="n">omitted</span>
   <span class="k">group</span> <span class="k">by</span> <span class="n">FusFamily</span> <span class="o">||</span><span class="s1">'-'</span><span class="o">||</span> <span class="n">FusProduct</span><span class="p">,</span><span class="n">RwApplication</span> <span class="o">||</span><span class="s1">'-'</span><span class="o">||</span> <span class="n">RwContainer</span> <span class="o">||</span><span class="s1">'-'</span><span class="o">||</span><span class="n">RwPath</span>
<span class="k">order</span> <span class="k">by</span> <span class="n">count_distinct</span><span class="p">(</span><span class="n">sessionId</span><span class="p">)</span> <span class="k">desc</span>
</code></pre></div></div>

<p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_application_usage_analysis.png" alt="Fusion Monitoring APM RUM Application Usage Analysis" /> <em>Figure 31: Application Usage Analysis</em></p>

<h2 id="apm-custom-metrics-and-alarms">APM Custom Metrics and Alarms</h2>

<p>Beyond passively monitoring dashboards, you can configure OCI APM to proactively alert you when Fusion web pages exceed acceptable performance thresholds. This involves creating a <strong>Custom Metric</strong> to aggregate performance data based on specific criteria, and then configuring <strong>OCI Alarms</strong>.</p>

<h3 id="step-1-create-a-custom-metric">Step 1: Create a Custom Metric</h3>
<p>First, define a custom metric to continuously capture specific performance behavior, such as slow page loads.</p>
<ol>
  <li>Navigate to your APM Domain &gt; <strong>Resources</strong> &gt; <strong>Custom metrics</strong>.</li>
  <li>Click <strong>Create custom metric</strong>.</li>
  <li>Enter a <strong>Metric name</strong> (e.g., <code class="language-plaintext highlighter-rouge">SlowFusionRedwoodPages</code>).</li>
  <li>In the <strong>Span filter</strong> box, configure the query to isolate the targeted behavior. For example:
    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="n">ServiceName</span> <span class="o">=</span> <span class="s1">'Fusion'</span> <span class="k">and</span> <span class="n">WebApplication</span> <span class="o">=</span> <span class="s1">'RedwoodPage'</span>
</code></pre></div>    </div>
  </li>
  <li>
    <p>From the <strong>Metric value source</strong> dropdown list, select the numeric metric to capture (e.g., <code class="language-plaintext highlighter-rouge">SpanDuration</code>).</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_custom_metric_value_source.png" alt="Fusion Monitoring APM RUM Custom Metric Value Source" /> <em>Figure 32: Custom Metric Value Source</em></p>
  </li>
  <li>
    <p><em>(Optional)</em> Select one or multiple <strong>Dimensions</strong> for fine-grained grouping (e.g., <code class="language-plaintext highlighter-rouge">RwContainer</code>, <code class="language-plaintext highlighter-rouge">RwApplication</code>, <code class="language-plaintext highlighter-rouge">FusFamily</code>).</p>

    <p><strong>Note: if you choose too many dimensions, the custom metric will be aggregated for each combination of dimensions, which may result in high cardinality which could potentially overload monitoring service. Please reduce the number of dimensions to avoid this issue.</strong>
 <img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_custom_metric_large_volume_warning.png" alt="Fusion Monitoring APM RUM Custom Metric Large Volume Warning" /> <em>Figure 33: Custom Metric Large Volume Warning</em></p>
  </li>
  <li>Click <strong>Next</strong> to choose metric storage options.</li>
  <li>Choose your target <strong>Compartment</strong> and <strong>Namespace</strong>. The default namespace is <code class="language-plaintext highlighter-rouge">oracle_apm_custom</code> (note: using a non-default custom namespace requires configuring OCI identity policies).</li>
  <li>
    <p>Click <strong>Create</strong>. APM will now periodically aggregate and push this custom metric to the OCI Monitoring service.</p>

    <p><img src="/images/posts/2026-03-06-apm-fusion-blogs/blog_fusion_apm_rum_custom_metric.png" alt="Fusion Monitoring APM RUM Custom Metric" /> <em>Figure 34: Custom Metric</em></p>
  </li>
</ol>

<h3 id="step-2-configure-an-oci-alarm">Step 2: Configure an OCI Alarm</h3>
<p>Finally, set up an alarm to notify your team when the custom metric breaches a threshold.</p>
<ol>
  <li>In the Oracle Cloud Console, navigate to <strong>Observability &amp; Management</strong> &gt; <strong>Monitoring</strong> &gt; <strong>Metrics Explorer</strong>.</li>
  <li>Select the compartment, metric namespace (<code class="language-plaintext highlighter-rouge">oracle_apm_custom</code>) and the custom metric name (e.g., <code class="language-plaintext highlighter-rouge">SlowFusionRedwoodPages</code>).</li>
  <li>Click <strong>Create Alarm</strong>.</li>
  <li>Provide Alarm Name, Alarm Summary, Metric Namespace(e.g., <code class="language-plaintext highlighter-rouge">oracle_apm_custom</code>), Metric Name(e.g., <code class="language-plaintext highlighter-rouge">SlowFusionRedwoodPages</code>), Interval(1 minute), Statistic(Mean).</li>
  <li>Define the <strong>Trigger Rule</strong> (e.g., trigger when the count &gt; 1000 within a 1-minute interval).</li>
  <li>Under <strong>Destinations</strong>, select or create an <strong>OCI Notification Topic</strong> (e.g., Email, Slack/PagerDuty integration) to route the alert to your support team.</li>
  <li>Click <strong>Save Alarm</strong>.</li>
</ol>

<p>Your team will now receive automated alerts whenever Fusion page performance degrades beyond your specified thresholds!</p>

<h2 id="conclusion">Conclusion</h2>

<p>Implementing OCI APM Real User Monitoring for Oracle Fusion SaaS Cloud Apps provides organizations with comprehensive visibility into real user experience, enabling data-driven performance optimization and improved user satisfaction. By deploying the APM Browser Agent for both ADF and Redwood pages, organizations can:</p>

<ul>
  <li><strong>Track User Behavior</strong>: Understand which pages users access and how they navigate through Fusion Apps</li>
  <li><strong>Profile Performance</strong>: Analyze individual user sessions to identify performance bottlenecks</li>
  <li><strong>Geographic Analysis</strong>: Understand how user location impacts application performance</li>
  <li><strong>Standardized Metrics</strong>: Use Apdex scores to measure and track overall application performance</li>
  <li><strong>Trend Analysis</strong>: Monitor performance over time to detect degradation and measure improvements</li>
  <li><strong>Device Profiling</strong>: Optimize application performance for different devices, browsers, and connection types</li>
</ul>

<p>The implementation uses an ADF page-template configuration for ADF pages and an assistant-generated Visual Builder workspace import for eligible Redwood App UIs. After the Fusion enrichment rule is enabled and the deployment is validated, the APM Browser Agent collects RUM data without requiring additional server-side agents.</p>

<p>By leveraging the insights provided by APM RUM, organizations can proactively identify and resolve performance issues, optimize user experience, and ensure that Fusion Cloud Apps deliver the performance and reliability that users expect.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://www.ateam-oracle.com/real-user-monitoring-for-oracle-fusion-saas-cloud-apps-using-oci-apm-browser-agent">Real User Monitoring for Oracle Fusion SaaS Cloud Apps using OCI APM Browser Agent</a></li>
  <li><a href="https://docs.oracle.com/en/learn/ofaob/index.html#introduction">Observability and Management Solution: Oracle Fusion Applications and OCI Observability Services</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/configure-browser-agent-real-user-monitoring.html">Configure APM Browser Agent for Real User Monitoring</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/deploy-browser-agent-your-application.html">Deploy the APM Browser Agent With Your Application</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/configure-attributes-real-user-monitoring.html">Configure Attributes for Real User Monitoring</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/configure-session-tracking-rum.html">Configure Session Tracking</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/configure-automatic-end-end-tracing-same-domain.html">Configure Ajax Calls Instrumentation</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/configure-span-rules.html">Configure Span Rules</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/hide-personally-identifiable-information-pii.html">Hide Personally Identifiable Information</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/application-performance-monitoring/doc/verify-browser-agent-deployment.html">Verify APM Browser Agent Deployment</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/paas/visual-builder/visualbuilder-building-appui/export-your-workspace-archive.html">Export Your Workspace as an Archive</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/paas/visual-builder/visualbuilder-building-appui/import-resources-your-workspace.html">Import Resources to Your Workspace</a></li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="Observability and Monitoring" /><category term="Oracle Fusion SaaS Cloud Apps" /><category term="Oracle Cloud Infrastructure" /><category term="Performance Monitoring" /><summary type="html"><![CDATA[Real User Monitoring for Oracle Fusion SaaS Cloud Apps with OCI APM Browser Agent]]></summary></entry><entry><title type="html">Monitoring OKE Cluster Processes with nmon: Capturing Granular Performance Data</title><link href="https://royce-fu.com/blog/monitoring-oke-cluster-processes-with-nmon-capturing-granular-performance-data/" rel="alternate" type="text/html" title="Monitoring OKE Cluster Processes with nmon: Capturing Granular Performance Data" /><published>2026-02-08T00:00:00+00:00</published><updated>2026-02-08T14:00:00+00:00</updated><id>https://royce-fu.com/blog/monitoring-oke-cluster-processes-with-nmon-capturing-granular-performance-data</id><content type="html" xml:base="https://royce-fu.com/blog/monitoring-oke-cluster-processes-with-nmon-capturing-granular-performance-data/"><![CDATA[<h1 id="monitoring-oke-cluster-processes-with-nmon-capturing-granular-performance-data">Monitoring OKE Cluster Processes with nmon: Capturing Granular Performance Data</h1>

<h2 id="introduction">Introduction</h2>

<p>When running workloads in Oracle Kubernetes Engine (OKE) clusters, having detailed visibility into system performance is crucial for troubleshooting issues, optimizing resources, and ensuring application reliability. While Kubernetes provides basic monitoring capabilities, capturing granular process-level metrics often requires specialized tools.</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/qUtwcWJZ5Q8" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/monitoring-oke-cluster-processes-with-nmon-capturing-granular-performance-data.png" alt="Monitoring OKE Cluster Processes with nmon: Capturing Granular Performance Data — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>In this blog post, we’ll explore how to use nmon (Nigel’s Monitor) to capture detailed process information in OKE clusters. We’ll cover both production monitoring configurations (30-second intervals) and high-resolution troubleshooting setups (1-second intervals) for capturing granular metrics when investigating performance issues.</p>

<h2 id="what-is-nmon">What is nmon?</h2>

<p>nmon is a powerful system performance monitoring tool originally developed by IBM for AIX and later ported to Linux. It provides comprehensive insights into various system aspects:</p>

<ul>
  <li>CPU utilization by core</li>
  <li>Memory usage</li>
  <li>Disk I/O activity</li>
  <li>Network throughput</li>
  <li>Top processes by resource usage</li>
  <li>File system statistics</li>
  <li>Kernel statistics</li>
</ul>

<p>What makes nmon particularly valuable is its ability to monitor multiple system resources simultaneously, providing a consolidated view that helps identify correlations between different performance aspects. For example, you might notice that high CPU usage coincides with specific disk I/O patterns, pointing to potential bottlenecks.</p>

<h2 id="why-use-nmon-in-oke-clusters">Why Use nmon in OKE Clusters?</h2>

<p>Kubernetes environments add layers of abstraction that can make performance troubleshooting challenging. Standard monitoring solutions often aggregate metrics over longer intervals (typically 15-60 seconds), which can mask short-duration spikes that impact application performance.</p>

<p>Key benefits of using nmon in OKE clusters include:</p>

<ol>
  <li><strong>Flexible monitoring resolution</strong>: Capture metrics at configurable intervals (30-60 seconds for production, 1 second for troubleshooting)</li>
  <li><strong>Process-level visibility</strong>: Track specific processes and their resource consumption with the <code class="language-plaintext highlighter-rouge">-t</code> flag</li>
  <li><strong>Low overhead</strong>: nmon is designed to be lightweight and consume minimal resources, especially at longer intervals</li>
  <li><strong>Data persistence</strong>: Record performance data for offline analysis and historical comparison</li>
  <li><strong>Visualization capabilities</strong>: Generate charts for easier interpretation of complex performance patterns</li>
  <li><strong>Dynamic configuration</strong>: Switch between production and troubleshooting modes based on operational needs</li>
</ol>

<h2 id="deployment-options-for-nmon-in-oke">Deployment Options for nmon in OKE</h2>

<p>There are several approaches to deploying nmon in an OKE cluster. We’ll explore two primary methods:</p>

<ol>
  <li>Standalone installation on individual nodes</li>
  <li>Containerized deployment using DaemonSets</li>
</ol>

<h3 id="option-1-standalone-installation">Option 1: Standalone Installation</h3>

<p>For direct installation on OKE nodes, you can use the following commands:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Download nmon and nmonchart</span>
curl <span class="nt">-LO</span> http://sourceforge.net/projects/nmon/files/nmonchart40.tar

<span class="c"># Create directory and extract</span>
<span class="nb">mkdir </span>nmonchart
<span class="nb">tar </span>xvf nmonchart40.tar <span class="nt">-C</span> nmonchart

<span class="c"># Install ksh (required for nmonchart)</span>
dnf <span class="nb">install </span>ksh

<span class="c"># Run nmon with 1-second interval</span>
nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 3600  <span class="c"># Captures data for 1 hour with 1-second intervals</span>
</code></pre></div></div>

<h3 id="option-2-containerized-deployment-recommended">Option 2: Containerized Deployment (Recommended)</h3>

<p>For Kubernetes environments, a containerized approach using DaemonSets provides better manageability and integration with the cluster. This ensures nmon runs on every node without manual installation.</p>

<h4 id="step-1-create-a-dockerfile-for-nmon">Step 1: Create a Dockerfile for nmon</h4>

<div class="language-dockerfile highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Dockerfile</span>
<span class="k">FROM</span><span class="s"> oraclelinux:8</span>

<span class="c"># Install EPEL</span>
<span class="k">RUN </span>yum <span class="nb">install</span> <span class="nt">-y</span> oracle-epel-release-el8.x86_64 <span class="o">&amp;&amp;</span> <span class="se">\
</span>    yum <span class="nb">install</span> <span class="nt">-y</span> yum-utils <span class="o">&amp;&amp;</span> <span class="se">\
</span>    yum-config-manager <span class="nt">--enable</span> ol8_baseos_latest ol8_appstream ol8_addons ol8_developer_EPEL

<span class="c"># Install nmon</span>
<span class="k">RUN </span>yum <span class="nb">install</span> <span class="nt">-y</span> nmon <span class="o">&amp;&amp;</span> <span class="se">\
</span>    yum clean all

<span class="c"># Create a directory for nmon logs</span>
<span class="k">RUN </span><span class="nb">mkdir</span> <span class="nt">-p</span> /var/log/nmon
<span class="k">RUN </span><span class="nb">mkdir</span> <span class="nt">-p</span> /opt/nmon/output

<span class="c"># Default command with 30-second interval for production monitoring</span>
<span class="c"># Override with command in DaemonSet YAML for troubleshooting scenarios</span>
<span class="k">ENTRYPOINT</span><span class="s"> ["nmon", "-f", "-t", "-s", "30", "-c", "2880"]</span>
</code></pre></div></div>

<h4 id="step-2-build-and-push-the-docker-image">Step 2: Build and Push the Docker Image</h4>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Build the image</span>
docker build <span class="nt">-t</span> nmon:oraclelinux8 <span class="nb">.</span>

<span class="c"># Tag the image for your registry</span>
docker tag nmon:oraclelinux8 &lt;your-registry&gt;/nmon-repo:v1

<span class="c"># Log in to your registry</span>
docker login <span class="nt">-u</span> <span class="s1">'&lt;username&gt;'</span> &lt;your-registry&gt;

<span class="c"># Push the image</span>
docker push &lt;your-registry&gt;/nmon-repo:v1
</code></pre></div></div>

<p>Replace <code class="language-plaintext highlighter-rouge">&lt;your-registry&gt;</code>, <code class="language-plaintext highlighter-rouge">&lt;username&gt;</code> with your specific Oracle Cloud Infrastructure Registry details.</p>

<h4 id="step-3-deploy-nmon-as-a-daemonset">Step 3: Deploy nmon as a DaemonSet</h4>

<p>Create a YAML file named <code class="language-plaintext highlighter-rouge">nmon-daemonset.yaml</code>:</p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="na">apiVersion</span><span class="pi">:</span> <span class="s">apps/v1</span>
<span class="na">kind</span><span class="pi">:</span> <span class="s">DaemonSet</span>
<span class="na">metadata</span><span class="pi">:</span>
  <span class="na">name</span><span class="pi">:</span> <span class="s">nmon-daemonset</span>
  <span class="na">namespace</span><span class="pi">:</span> <span class="s">monitoring</span>  <span class="c1"># Adjust as needed</span>
  <span class="na">labels</span><span class="pi">:</span>
    <span class="na">k8s-app</span><span class="pi">:</span> <span class="s">nmon</span>
<span class="na">spec</span><span class="pi">:</span>
  <span class="na">selector</span><span class="pi">:</span>
    <span class="na">matchLabels</span><span class="pi">:</span>
      <span class="na">name</span><span class="pi">:</span> <span class="s">nmon</span>
  <span class="na">template</span><span class="pi">:</span>
    <span class="na">metadata</span><span class="pi">:</span>
      <span class="na">labels</span><span class="pi">:</span>
        <span class="na">name</span><span class="pi">:</span> <span class="s">nmon</span>
    <span class="na">spec</span><span class="pi">:</span>
      <span class="c1"># Tolerations to allow running on control-plane nodes if desired</span>
      <span class="na">tolerations</span><span class="pi">:</span>
      <span class="pi">-</span> <span class="na">key</span><span class="pi">:</span> <span class="s">node-role.kubernetes.io/control-plane</span>
        <span class="na">operator</span><span class="pi">:</span> <span class="s">Exists</span>
        <span class="na">effect</span><span class="pi">:</span> <span class="s">NoSchedule</span>
      <span class="pi">-</span> <span class="na">key</span><span class="pi">:</span> <span class="s">node-role.kubernetes.io/master</span>
        <span class="na">operator</span><span class="pi">:</span> <span class="s">Exists</span>
        <span class="na">effect</span><span class="pi">:</span> <span class="s">NoSchedule</span>

      <span class="c1"># Enable to see host processes</span>
      <span class="na">hostPID</span><span class="pi">:</span> <span class="no">true</span>
      <span class="na">containers</span><span class="pi">:</span>
      <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">nmon</span>
        <span class="na">image</span><span class="pi">:</span> <span class="s">&lt;your-registry&gt;/nmon-repo:v1</span>
        <span class="na">resources</span><span class="pi">:</span>
          <span class="na">limits</span><span class="pi">:</span>
            <span class="na">memory</span><span class="pi">:</span> <span class="s">200Mi</span>
          <span class="na">requests</span><span class="pi">:</span>
            <span class="na">cpu</span><span class="pi">:</span> <span class="s">100m</span>
            <span class="na">memory</span><span class="pi">:</span> <span class="s">200Mi</span>
        <span class="na">volumeMounts</span><span class="pi">:</span>
        <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">nmon-output</span>
          <span class="na">mountPath</span><span class="pi">:</span> <span class="s">/opt/nmon/output</span>
        <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">varlog</span>
          <span class="na">mountPath</span><span class="pi">:</span> <span class="s">/var/log</span>
        <span class="na">securityContext</span><span class="pi">:</span>
          <span class="na">privileged</span><span class="pi">:</span> <span class="no">true</span>  <span class="c1"># Required to access host metrics</span>
      <span class="na">terminationGracePeriodSeconds</span><span class="pi">:</span> <span class="m">30</span>
      <span class="na">volumes</span><span class="pi">:</span>
      <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">nmon-output</span>
        <span class="na">hostPath</span><span class="pi">:</span>
          <span class="na">path</span><span class="pi">:</span> <span class="s">/var/log/nmon</span>
      <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">varlog</span>
        <span class="na">hostPath</span><span class="pi">:</span>
          <span class="na">path</span><span class="pi">:</span> <span class="s">/var/log</span>
</code></pre></div></div>

<p>Apply the DaemonSet configuration:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>kubectl apply <span class="nt">-f</span> nmon-daemonset.yaml
</code></pre></div></div>

<p>Verify that the DaemonSet pods are running:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>kubectl get pods <span class="nt">-n</span> monitoring
</code></pre></div></div>

<h2 id="configuring-nmon-for-high-resolution-metrics-when-needed">Configuring nmon for High-Resolution Metrics When Needed</h2>

<p>nmon provides flexible configuration options that allow you to balance monitoring overhead with the level of detail needed for troubleshooting. The key to effective monitoring is understanding when to use different sampling intervals and which flags to enable.</p>

<h3 id="understanding-nmon-command-line-options">Understanding nmon Command-Line Options</h3>

<p>The core nmon parameters for data collection are:</p>

<ul>
  <li><code class="language-plaintext highlighter-rouge">-f</code>: Write to a file instead of displaying interactively</li>
  <li><code class="language-plaintext highlighter-rouge">-t</code>: <strong>Critical flag</strong> - Include top processes in the output (required for process-level troubleshooting)</li>
  <li><code class="language-plaintext highlighter-rouge">-s &lt;seconds&gt;</code>: Sampling interval (how often to collect data)</li>
  <li><code class="language-plaintext highlighter-rouge">-c &lt;count&gt;</code>: Number of samples to collect</li>
  <li><code class="language-plaintext highlighter-rouge">-p</code>: Add extra process details including command arguments</li>
  <li><code class="language-plaintext highlighter-rouge">-T</code>: Include top threads (helps identify specific threads causing high CPU usage)</li>
</ul>

<h3 id="production-monitoring-vs-high-resolution-troubleshooting">Production Monitoring vs. High-Resolution Troubleshooting</h3>

<p><strong>For Production Monitoring (Continuous Operation):</strong></p>

<p>Use longer intervals to minimize overhead while maintaining visibility:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># 30-second intervals for production monitoring (recommended)</span>
nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 30 <span class="nt">-c</span> 2880  <span class="c"># Captures 24 hours of data at 30-second intervals</span>

<span class="c"># Alternative: 60-second intervals for lower overhead</span>
nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 60 <span class="nt">-c</span> 1440  <span class="c"># Captures 24 hours of data at 60-second intervals</span>
</code></pre></div></div>

<p><strong>For High-Resolution Troubleshooting (When Issues Occur):</strong></p>

<p>When investigating performance issues, switch to high-resolution monitoring to capture granular details:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># 1-second intervals for detailed troubleshooting</span>
nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 3600  <span class="c"># Captures 1 hour of data at 1-second intervals</span>

<span class="c"># For very short incidents (5-10 minutes)</span>
nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 600   <span class="c"># Captures 10 minutes of data at 1-second intervals</span>
</code></pre></div></div>

<h3 id="critical-configuration-the--t-flag">Critical Configuration: The <code class="language-plaintext highlighter-rouge">-t</code> Flag</h3>

<p><strong>Always include the <code class="language-plaintext highlighter-rouge">-t</code> flag</strong> when deploying nmon for troubleshooting. This flag is essential for capturing top processes, which is critical for identifying which processes are consuming resources during performance incidents.</p>

<p>Without <code class="language-plaintext highlighter-rouge">-t</code>, you’ll only get system-level metrics (CPU, memory, disk) but won’t be able to identify the specific processes causing issues. This is a common oversight that can significantly limit troubleshooting effectiveness.</p>

<h4 id="process-level-visualizations-requires--t-flag">Process-Level Visualizations (Requires <code class="language-plaintext highlighter-rouge">-t</code> Flag)</h4>

<p>When you use the <code class="language-plaintext highlighter-rouge">-t</code> flag, nmonchart generates process-level visualizations that are essential for troubleshooting:</p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_top_processes_cpu_chart.png" alt="Top Process Commands by CPU" /></p>

<p><em>Figure 6: Top Process Commands by CPU percentage - <strong>critical for identifying which processes consume CPU resources</strong>. This chart clearly shows processes like <code class="language-plaintext highlighter-rouge">setroubleshootd</code>, <code class="language-plaintext highlighter-rouge">prometheus</code>, and <code class="language-plaintext highlighter-rouge">ruby</code> consuming CPU at specific times. <strong>This visualization is only available when using the <code class="language-plaintext highlighter-rouge">-t</code> flag</strong> - without it, you cannot identify which processes are causing performance issues.</em></p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_top_commands_bubble_chart.png" alt="Top Commands Bubble Chart" /></p>

<p><em>Figure 7: Top 20 processes correlation chart showing relationships between CPU seconds, Character I/O, and Memory Size. Bubble size represents memory consumption. This helps identify processes with high resource usage across multiple dimensions. Also requires the <code class="language-plaintext highlighter-rouge">-t</code> flag.</em></p>

<p><strong>Critical Note</strong>: Without the <code class="language-plaintext highlighter-rouge">-t</code> flag, Figures 6 and 7 would not be available, making it impossible to identify which specific processes are causing performance issues. Always include <code class="language-plaintext highlighter-rouge">-t</code> when deploying nmon for troubleshooting.</p>

<h3 id="enhanced-troubleshooting-configuration">Enhanced Troubleshooting Configuration</h3>

<p>For comprehensive troubleshooting during critical incidents, use additional flags to capture maximum detail:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Maximum detail configuration for troubleshooting</span>
nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-p</span> <span class="nt">-T</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 1800  <span class="c"># 30 minutes of 1-second data with process and thread details</span>

<span class="c"># Parameters explained:</span>
<span class="c"># -f: File output</span>
<span class="c"># -t: Top processes (REQUIRED for process identification)</span>
<span class="c"># -p: Extra process details including command arguments</span>
<span class="c"># -T: Top threads (identify specific threads causing high CPU)</span>
<span class="c"># -s 1: 1-second sampling interval</span>
<span class="c"># -c 1800: 1800 samples (30 minutes)</span>
</code></pre></div></div>

<h3 id="dynamic-configuration-switching">Dynamic Configuration Switching</h3>

<p>In production environments, you can run nmon with normal intervals and dynamically switch to high-resolution mode when issues are detected:</p>

<p><strong>Scenario: Intermittent CPU Spikes</strong></p>

<ol>
  <li><strong>Normal Operation</strong>: Run nmon with 30-second intervals
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 30 <span class="nt">-c</span> 2880 <span class="nt">-F</span> /var/log/nmon/production_<span class="si">$(</span><span class="nb">date</span> +%y%m%d_%H%M%S<span class="si">)</span>.nmon
</code></pre></div>    </div>
  </li>
  <li><strong>When Alert Detected</strong>: Immediately start high-resolution capture
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Execute in the nmon container/pod</span>
kubectl <span class="nb">exec</span> <span class="nt">-n</span> monitoring &lt;nmon-pod-name&gt; <span class="nt">--</span> nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-p</span> <span class="nt">-T</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 300 <span class="nt">-F</span> /var/log/nmon/incident_<span class="si">$(</span><span class="nb">date</span> +%y%m%d_%H%M%S<span class="si">)</span>.nmon
</code></pre></div>    </div>
  </li>
  <li><strong>Post-Incident Analysis</strong>: Collect both normal and high-resolution data files for comparison</li>
</ol>

<h3 id="containerized-deployment-configuration">Containerized Deployment Configuration</h3>

<p>When deploying nmon as a DaemonSet, you can configure different behaviors for production vs. troubleshooting:</p>

<p><strong>Production DaemonSet Configuration:</strong></p>

<div class="language-dockerfile highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Default command for production monitoring (30-second intervals)</span>
<span class="k">ENTRYPOINT</span><span class="s"> ["nmon", "-f", "-t", "-s", "30", "-c", "2880"]</span>
</code></pre></div></div>

<p><strong>Troubleshooting DaemonSet Configuration:</strong></p>

<p>Create a separate DaemonSet or modify the existing one for incident response:</p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c1"># In your DaemonSet YAML, you can override the command for troubleshooting</span>
<span class="na">containers</span><span class="pi">:</span>
<span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">nmon</span>
  <span class="na">image</span><span class="pi">:</span> <span class="s">&lt;your-registry&gt;/nmon-repo:v1</span>
  <span class="na">command</span><span class="pi">:</span> <span class="pi">[</span><span class="s2">"</span><span class="s">nmon"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-f"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-t"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-p"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-T"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-s"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">1"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-c"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">1800"</span><span class="pi">]</span>
  <span class="c1"># ... rest of configuration</span>
</code></pre></div></div>

<p>Or use environment variables for flexible configuration:</p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="na">containers</span><span class="pi">:</span>
<span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">nmon</span>
  <span class="na">image</span><span class="pi">:</span> <span class="s">&lt;your-registry&gt;/nmon-repo:v1</span>
  <span class="na">env</span><span class="pi">:</span>
  <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">NMON_INTERVAL</span>
    <span class="na">value</span><span class="pi">:</span> <span class="s2">"</span><span class="s">1"</span>  <span class="c1"># Change to 30 for production</span>
  <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">NMON_COUNT</span>
    <span class="na">value</span><span class="pi">:</span> <span class="s2">"</span><span class="s">1800"</span>  <span class="c1"># Adjust based on monitoring duration needed</span>
  <span class="pi">-</span> <span class="na">name</span><span class="pi">:</span> <span class="s">NMON_FLAGS</span>
    <span class="na">value</span><span class="pi">:</span> <span class="s2">"</span><span class="s">-t</span><span class="nv"> </span><span class="s">-p</span><span class="nv"> </span><span class="s">-T"</span>  <span class="c1"># Include top processes, process details, and threads</span>
  <span class="na">command</span><span class="pi">:</span> <span class="pi">[</span><span class="s2">"</span><span class="s">/bin/sh"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">-c"</span><span class="pi">,</span> <span class="s2">"</span><span class="s">nmon</span><span class="nv"> </span><span class="s">-f</span><span class="nv"> </span><span class="s">$NMON_FLAGS</span><span class="nv"> </span><span class="s">-s</span><span class="nv"> </span><span class="s">$NMON_INTERVAL</span><span class="nv"> </span><span class="s">-c</span><span class="nv"> </span><span class="s">$NMON_COUNT"</span><span class="pi">]</span>
</code></pre></div></div>

<h3 id="real-world-example-capturing-process-information-during-cpu-spikes">Real-World Example: Capturing Process Information During CPU Spikes</h3>

<p>Based on production experience with OKE clusters experiencing intermittent CPU spikes:</p>

<p><strong>Problem</strong>: CPU spikes lasting less than a minute causing hundreds of alerts, but standard monitoring couldn’t identify the root cause.</p>

<p><strong>Solution</strong>: Deploy nmon with proper configuration:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Deploy nmon DaemonSet with 30-second intervals for continuous monitoring</span>
kubectl apply <span class="nt">-f</span> nmon-daemonset-production.yaml

<span class="c"># When CPU spike is detected, immediately capture high-resolution data</span>
kubectl <span class="nb">exec</span> <span class="nt">-n</span> monitoring &lt;nmon-pod-name&gt; <span class="nt">--</span> nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-p</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 300 <span class="nt">-F</span> /opt/nmon/output/spike_<span class="si">$(</span><span class="nb">date</span> +%y%m%d_%H%M%S<span class="si">)</span>.nmon
</code></pre></div></div>

<p><strong>Key Learning</strong>: The <code class="language-plaintext highlighter-rouge">-t</code> flag is essential. Without it, you’ll capture system metrics but won’t be able to identify which processes are consuming CPU during the spike.</p>

<h3 id="configuration-best-practices">Configuration Best Practices</h3>

<ol>
  <li>
    <p><strong>Always use <code class="language-plaintext highlighter-rouge">-t</code> flag</strong>: This is non-negotiable for troubleshooting. It enables process-level visibility.</p>
  </li>
  <li><strong>Match interval to problem duration</strong>:
    <ul>
      <li>For issues lasting seconds: Use 1-second intervals</li>
      <li>For issues lasting minutes: 5-10 second intervals may suffice</li>
      <li>For continuous monitoring: 30-60 second intervals</li>
    </ul>
  </li>
  <li>
    <p><strong>Balance data volume with detail</strong>: Higher resolution generates more data. Plan storage accordingly.</p>
  </li>
  <li>
    <p><strong>Use <code class="language-plaintext highlighter-rouge">-p</code> and <code class="language-plaintext highlighter-rouge">-T</code> selectively</strong>: These flags add overhead. Use them during active troubleshooting, not for continuous monitoring.</p>
  </li>
  <li><strong>File naming convention</strong>: Use descriptive names with timestamps for easy identification:
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 600 <span class="nt">-F</span> /var/log/nmon/cpu_spike_<span class="si">$(</span><span class="nb">date</span> +%y%m%d_%H%M%S<span class="si">)</span>.nmon
</code></pre></div>    </div>
  </li>
</ol>

<h2 id="analyzing-nmon-data">Analyzing nmon Data</h2>

<p>nmon generates files with the <code class="language-plaintext highlighter-rouge">.nmon</code> extension, which contain all the collected metrics in a CSV-like format. There are several ways to analyze this data:</p>

<h3 id="option-1-using-nmonchart-recommended-for-visual-analysis">Option 1: Using nmonchart (Recommended for Visual Analysis)</h3>

<p>The simplest and most effective approach is to use the included <code class="language-plaintext highlighter-rouge">nmonchart</code> tool to generate interactive HTML-based charts:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>./nmonchart/nmonchart hostname_date_time.nmon
<span class="c"># Creates: hostname_date_time.html</span>
</code></pre></div></div>

<p>This generates an interactive HTML file with comprehensive performance visualizations. The following sections show examples of the key charts available:</p>

<h4 id="cpu-utilization-chart">CPU Utilization Chart</h4>

<p>The CPU utilization chart shows how CPU resources are distributed across different categories:</p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_cpu_utilization_chart.png" alt="CPU Utilization Chart" /></p>

<p><em>Figure 1: CPU Utilization Chart showing User%, System%, Wait%, Idle%, and Steal% over time. High Wait% (orange area) indicates I/O bottlenecks. This example shows data collected at 10-second intervals - use 1-second intervals for troubleshooting incidents.</em></p>

<h4 id="memory-usage-chart">Memory Usage Chart</h4>

<p>The memory chart displays RAM utilization breakdown:</p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_memory_chart.png" alt="Memory Usage Chart" /></p>

<p><em>Figure 2: Real Memory (RAM) breakdown showing total, free, cached, active, buffers, and inactive memory over time. Helps identify memory pressure that might correlate with performance issues.</em></p>

<h4 id="disk-io-charts">Disk I/O Charts</h4>

<p>Disk charts help identify I/O bottlenecks:</p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_disk_busy_chart.png" alt="Disk Busy Chart" /></p>

<p><em>Figure 3: Disk Busy Percentage (stacked) showing activity across multiple disk devices. High values indicate disk I/O bottlenecks.</em></p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_top_disk_chart.png" alt="Top Disk Chart" /></p>

<p><em>Figure 4: Top 15 disks by Busy% - identifies which specific disks are experiencing the highest utilization.</em></p>

<h4 id="run-queue-chart">Run Queue Chart</h4>

<p>The run queue chart shows process scheduling activity:</p>

<p><img src="/images/posts/2026-02-nmon-blogs/nmon_run_queue_chart.png" alt="Run Queue Chart" /></p>

<p><em>Figure 5: Run Queue showing Runnable (blue) and Blocked (red) processes. High runnable counts indicate CPU contention where many processes are competing for CPU time.</em></p>

<p><strong>Key Features of nmonchart Visualizations:</strong></p>

<ul>
  <li><strong>Time-series Analysis</strong>: All charts are time-aligned, making it easy to correlate events across different metrics</li>
  <li><strong>Interactive Navigation</strong>: Scroll through the HTML to view different time periods and metrics</li>
  <li><strong>Configuration Summary</strong>: The HTML includes system configuration details (CPU count, memory, disk layout) captured at collection time</li>
</ul>

<h3 id="option-2-custom-analysis-with-nmon2csv">Option 2: Custom Analysis with nmon2csv</h3>

<p>For more advanced analysis, you can convert nmon data to CSV format and process it with tools like Python, R, or Excel:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Install nmon2csv (if not already available)</span>
pip <span class="nb">install </span>nmon2csv

<span class="c"># Convert nmon data to CSV</span>
nmon2csv hostname_date_time.nmon
</code></pre></div></div>

<h3 id="option-3-integration-with-monitoring-platforms">Option 3: Integration with Monitoring Platforms</h3>

<p>For persistent monitoring, you can integrate nmon data with platforms like Prometheus and Grafana:</p>

<ol>
  <li>Use a sidecar container to process nmon output</li>
  <li>Expose metrics in Prometheus format</li>
  <li>Create Grafana dashboards for visualization</li>
</ol>

<h2 id="use-case-identifying-cpu-intensive-processes-during-intermittent-spikes">Use Case: Identifying CPU-Intensive Processes During Intermittent Spikes</h2>

<p>Let’s walk through a real-world use case: identifying CPU spikes in an OKE cluster that last less than a minute.</p>

<h3 id="scenario-setup">Scenario Setup</h3>

<p><strong>Initial State</strong>: nmon DaemonSet running with 30-second intervals for continuous production monitoring.</p>

<p><strong>Incident</strong>: Intermittent CPU spikes detected, causing hundreds of alerts but standard monitoring cannot identify root cause.</p>

<h3 id="investigation-steps">Investigation Steps</h3>

<ol>
  <li><strong>Deploy nmon for Production Monitoring</strong> (if not already running)
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Deploy with 30-second intervals for continuous monitoring</span>
kubectl apply <span class="nt">-f</span> nmon-daemonset.yaml
</code></pre></div>    </div>
  </li>
  <li><strong>When CPU Spike is Detected</strong>: Immediately switch to high-resolution capture
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Execute high-resolution capture in the running nmon pod</span>
kubectl <span class="nb">exec</span> <span class="nt">-n</span> monitoring &lt;nmon-pod-name&gt; <span class="nt">--</span> nmon <span class="nt">-f</span> <span class="nt">-t</span> <span class="nt">-p</span> <span class="nt">-s</span> 1 <span class="nt">-c</span> 300 <span class="nt">-F</span> /opt/nmon/output/spike_<span class="si">$(</span><span class="nb">date</span> +%y%m%d_%H%M%S<span class="si">)</span>.nmon
</code></pre></div>    </div>

    <p><strong>Critical</strong>: Ensure the <code class="language-plaintext highlighter-rouge">-t</code> flag is included to capture top processes. Without this flag, you’ll only see system-level metrics and won’t be able to identify the problematic processes.</p>
  </li>
  <li><strong>Collect nmon Files</strong> after the incident
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Copy nmon files from the pod</span>
kubectl <span class="nb">cp </span>monitoring/&lt;nmon-pod-name&gt;:/opt/nmon/output/spike_<span class="k">*</span>.nmon ./incident_data.nmon
</code></pre></div>    </div>
  </li>
  <li><strong>Generate Visualizations</strong> using nmonchart
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>./nmonchart/nmonchart incident_data.nmon
<span class="c"># Opens incident_data.html in your browser</span>
</code></pre></div>    </div>
  </li>
  <li><strong>Analyze Visualizations</strong>: Review the HTML charts to identify the issue
    <ul>
      <li><strong>CPU Chart</strong> (Figure 1): Locate the spike time window and check Wait% for I/O bottlenecks</li>
      <li><strong>Run Queue Chart</strong> (Figure 5): Check for high runnable processes indicating CPU contention</li>
      <li><strong>Top Processes Section</strong> (Figure 6): Identify which processes consumed CPU during the spike - <strong>requires <code class="language-plaintext highlighter-rouge">-t</code> flag</strong></li>
      <li><strong>Memory Chart</strong> (Figure 2): Check if memory pressure coincided with CPU spike</li>
      <li><strong>Disk I/O Charts</strong> (Figures 3-4): Determine if disk I/O was a contributing factor</li>
      <li><strong>Process Correlation</strong> (Figure 7): Review bubble chart for multi-dimensional resource analysis</li>
    </ul>
  </li>
  <li><strong>Extract Process Details</strong> from raw nmon data (if needed for further analysis)
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Extract top processes during the spike period</span>
<span class="nb">grep</span> <span class="s2">"^TOP"</span> incident_data.nmon | <span class="nb">tail</span> <span class="nt">-50</span>
   
<span class="c"># Look for processes with high CPU usage</span>
<span class="nb">grep</span> <span class="s2">"^TOP"</span> incident_data.nmon | <span class="nb">grep</span> <span class="nt">-E</span> <span class="s2">"CPU.*[5-9][0-9]|CPU.*100"</span>
</code></pre></div>    </div>
  </li>
  <li><strong>Identify Root Cause</strong>: Correlate findings from visualizations (Figures 1-7) with application logs and system events</li>
</ol>

<h3 id="key-success-factors">Key Success Factors</h3>

<ul>
  <li><strong>The <code class="language-plaintext highlighter-rouge">-t</code> flag is essential</strong>: Without it, process identification is impossible</li>
  <li><strong>High-resolution timing</strong>: 1-second intervals capture short-lived spikes that 30-second intervals miss</li>
  <li><strong>Immediate response</strong>: Start high-resolution capture as soon as the issue is detected</li>
  <li><strong>Process details</strong>: The <code class="language-plaintext highlighter-rouge">-p</code> flag provides command arguments that help identify specific application components</li>
</ul>

<h3 id="example-output-analysis">Example Output Analysis</h3>

<p>When analyzing nmon data, look for patterns like:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>TOP,CPU%,Mem%,Pid,Command
TOP,45.2,2.1,12345,/usr/bin/java -Xmx2g MyApplication
TOP,32.1,1.5,12346,/usr/bin/kubelet --config=/etc/kubernetes/kubelet.conf
</code></pre></div></div>

<p>This shows that a Java application process (PID 12345) is consuming 45.2% CPU during the spike, which would be missed with standard monitoring intervals.</p>

<p>When visualized using nmonchart (see Figure 6), you can see this process activity clearly in the Top Process Commands chart. The 1-second granularity allows you to catch short-lived spikes that might be missed with standard monitoring intervals, while the <code class="language-plaintext highlighter-rouge">-t</code> flag ensures you can identify exactly which processes are responsible.</p>

<p><strong>Correlating Charts for Root Cause Analysis:</strong></p>

<p>When analyzing performance incidents, correlate findings across multiple charts:</p>

<ul>
  <li><strong>High CPU Wait%</strong> (Figure 1) + <strong>High Disk Busy%</strong> (Figures 3-4) = I/O bottleneck</li>
  <li><strong>High Runnable processes</strong> (Figure 5) + <strong>High CPU User%</strong> (Figure 1) = CPU contention</li>
  <li><strong>Specific process CPU spikes</strong> (Figure 6) + <strong>Memory pressure</strong> (Figure 2) = Process-specific resource issue</li>
  <li><strong>Process correlation</strong> (Figure 7) helps identify processes with high resource usage across multiple dimensions</li>
</ul>

<h2 id="best-practices-for-nmon-in-oke">Best Practices for nmon in OKE</h2>

<ol>
  <li><strong>Configuration Strategy</strong>:
    <ul>
      <li>Use 30-second intervals for continuous production monitoring to balance detail with overhead</li>
      <li>Switch to 1-second intervals only when troubleshooting active incidents</li>
      <li>Always include the <code class="language-plaintext highlighter-rouge">-t</code> flag to capture top processes (critical for troubleshooting)</li>
    </ul>
  </li>
  <li><strong>Resource considerations</strong>:
    <ul>
      <li>While nmon is lightweight, 1-second intervals generate significantly more data than 30-second intervals</li>
      <li>Monitor the resource usage of nmon itself, especially during high-resolution captures</li>
      <li>Plan storage capacity based on your monitoring intervals and retention requirements</li>
    </ul>
  </li>
  <li><strong>Data retention</strong>:
    <ul>
      <li>Implement a rotation policy for nmon files to prevent disk space issues</li>
      <li>Archive high-resolution troubleshooting captures separately from routine monitoring data</li>
      <li>Consider compressing older nmon files to save space</li>
    </ul>
  </li>
  <li><strong>Security context</strong>:
    <ul>
      <li>The nmon container requires privileged access to gather all metrics</li>
      <li>Consider your security requirements and use least-privilege principles where possible</li>
      <li>Review and restrict access to nmon output files containing system information</li>
    </ul>
  </li>
  <li><strong>Selective deployment</strong>:
    <ul>
      <li>You may not need nmon on every node</li>
      <li>Consider using node selectors to deploy only to nodes of interest</li>
      <li>For troubleshooting, you can deploy to specific nodes experiencing issues</li>
    </ul>
  </li>
  <li><strong>Process visibility</strong>:
    <ul>
      <li><strong>Always use <code class="language-plaintext highlighter-rouge">-t</code> flag</strong>: This is the most critical flag for troubleshooting. Without it, you cannot identify which processes are consuming resources</li>
      <li>Use <code class="language-plaintext highlighter-rouge">-p</code> flag during active troubleshooting to get command arguments for better process identification</li>
      <li>Use <code class="language-plaintext highlighter-rouge">-T</code> flag when investigating thread-level issues</li>
    </ul>
  </li>
  <li><strong>Integration with alerting</strong>:
    <ul>
      <li>Automate the analysis of nmon data to trigger alerts on abnormal patterns</li>
      <li>Set up automated high-resolution capture when critical alerts are triggered</li>
      <li>Correlate nmon data with application and infrastructure logs for comprehensive analysis</li>
    </ul>
  </li>
  <li><strong>Troubleshooting Workflow</strong>:
    <ul>
      <li>Establish baseline metrics with normal interval monitoring</li>
      <li>When issues occur, immediately switch to high-resolution capture</li>
      <li>Document the configuration used during each troubleshooting session</li>
      <li>Review and refine your monitoring strategy based on incident patterns</li>
    </ul>
  </li>
</ol>

<h2 id="conclusion">Conclusion</h2>

<p>nmon provides a powerful and flexible way to capture performance data in OKE clusters, helping identify and troubleshoot issues that might be missed with standard monitoring solutions. By deploying nmon as a DaemonSet with appropriate configuration for your use case, you gain detailed visibility into process behavior across your cluster.</p>

<p><strong>Key Takeaways:</strong></p>

<ul>
  <li><strong>Use appropriate intervals</strong>: 30-second intervals for production monitoring, 1-second intervals for active troubleshooting</li>
  <li><strong>Always include the <code class="language-plaintext highlighter-rouge">-t</code> flag</strong>: This is critical for capturing top processes and identifying resource-consuming applications</li>
  <li><strong>Dynamic configuration</strong>: Switch to high-resolution mode when investigating incidents, then return to normal monitoring</li>
  <li><strong>Process identification</strong>: The combination of <code class="language-plaintext highlighter-rouge">-t</code>, <code class="language-plaintext highlighter-rouge">-p</code>, and <code class="language-plaintext highlighter-rouge">-T</code> flags provides comprehensive process and thread-level visibility</li>
</ul>

<p>This approach complements existing monitoring solutions, providing the flexibility to capture high-resolution data when needed while maintaining efficient continuous monitoring during normal operations. The ability to dynamically adjust monitoring resolution based on operational needs makes nmon an invaluable tool for troubleshooting complex performance issues in OKE environments.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://www.redhat.com/en/blog/monitor-linux-performance-nmon">Monitor Linux performance with nmon</a></li>
  <li><a href="https://www.dbi-services.com/blog/monitoring-linux-with-nmon/">Monitoring Linux with nmon</a></li>
  <li><a href="https://nmon.sourceforge.io/pmwiki.php?n=Site.Documentation">nmon Documentation</a></li>
  <li><a href="https://nmon.sourceforge.io/pmwiki.php?n=Site.Nmonchart">nmonchart Documentation</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/Content/ContEng/Concepts/contengoverview.htm">Oracle Kubernetes Engine Documentation</a></li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="Observability and Monitoring" /><category term="OKE" /><category term="Kubernetes" /><category term="Performance Monitoring" /><summary type="html"><![CDATA[Monitoring OKE Cluster Processes with nmon: Capturing Granular Performance Data]]></summary></entry><entry><title type="html">Gaining Insights from Fusion ESS, Audit and Security Dashboards with AI Augmentation Using LoganAI - Part 3</title><link href="https://royce-fu.com/blog/gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai-part-3/" rel="alternate" type="text/html" title="Gaining Insights from Fusion ESS, Audit and Security Dashboards with AI Augmentation Using LoganAI - Part 3" /><published>2026-01-30T00:00:00+00:00</published><updated>2026-01-30T14:00:00+00:00</updated><id>https://royce-fu.com/blog/gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai-part-3</id><content type="html" xml:base="https://royce-fu.com/blog/gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai-part-3/"><![CDATA[<h1 id="gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai---part-3">Gaining Insights from Fusion ESS, Audit and Security Dashboards with AI Augmentation Using LoganAI - Part 3</h1>

<p><strong>Description: After setting up Fusion Applications audit logs ingestion in OCI Log Analytics (Parts 1 and 2), organizations need to transform raw log data into actionable insights. This blog post demonstrates how to leverage OCI Log Analytics dashboards and LoganAI to gain comprehensive visibility into Fusion Applications ESS jobs, security events, and audit activities. We’ll explore dashboard visualizations, compare Fusion native interfaces with OCI Log Analytics capabilities, and showcase AI-powered analysis for proactive monitoring and threat detection.</strong></p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/0tmoj8r3rL0" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/gaining-insights-from-fusion-ess-audit-and-security-dashboards-with-ai-augmentation-using-loganai-part-3.png" alt="Gaining Insights from Fusion ESS, Audit and Security Dashboards with AI Augmentation Using LoganAI - Part 3 — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<h2 id="introduction">Introduction</h2>

<p>Welcome to Part 3 of our blog series, where we move beyond simply collecting Fusion Applications audit logs and start putting them to use for practical, real-world monitoring of your organization’s Fusion security and operational health.</p>

<p>Fusion Audit Log Key Use Cases Overview:
<img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_key_use_cases.png" alt="Fusion Applications Audit Logs Key Use Cases" /></p>

<p><em>Figure 1: Key Fusion Audit Logs Use Cases for OCI Log Analytics</em></p>

<p>In Parts 1 and 2, you learned how to configure permissions and set up OCI Log Analytics to ingest audit logs from Oracle Fusion Applications. Now that your data is flowing in, the main challenge is turning raw log data into insights that improve your security posture and operations—especially for Fusion ESS (Enterprise Scheduler Service) and Security and Audit use cases.</p>

<p>While Oracle Fusion offers basic native tools for tracking scheduled jobs and audit events, those interfaces are often limited: you might find it hard to review historical trends, correlate security activities across modules, or customize dashboards for stakeholders. Most importantly, as your monitoring needs evolve, you will need deeper analytics and a more proactive approach.</p>

<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_native_scheduled_processes.png" alt="Fusion Applications Native Scheduled Processes Work Area" />
<em>Figure 2: Fusion Applications Native Scheduled Processes Work Area - Typical user interface for ESS job tracking</em></p>

<p>Historically, to answer critical questions like below, organizations have developed a set of dashboards and reports, set up rule-based alerts, and sifted through log records to identify patterns.</p>
<ul>
  <li>What patterns do you see in off-hours logins?</li>
  <li>Which countries and cities have the highest number of failed login attempts?</li>
  <li>Which users have logged in from geographically distant locations in the past 24 hours?</li>
  <li>Show me users with unusual login patterns that might indicate compromised accounts</li>
  <li>Identify any brute-force attack patterns in failed login attempts</li>
  <li>Are there trends in failed logins or system access?</li>
  <li>Are there patterns in job delays or recurring errors across modules?</li>
  <li>What ESS jobs are failing most frequently, and why?</li>
  <li>Show me ESS jobs that are taking longer than usual to execute compared to last month</li>
  <li>Identify any unusual patterns in ESS job execution that might indicate performance degradation</li>
  <li>Which ESS jobs are at risk of failure based on recent trends?</li>
  <li>What is causing ESS job performance degradation in the CRM module?</li>
</ul>

<p>At Oracle, we have collective knowledge domain expertise in Fusion Applications and OCI Log Analytics, and we have developed a set of dashboards and reports that provide a comprehensive view of Fusion Applications audit logs and security events. We have published these dashboards as out-of-the-box in the Log Analytics Dashboards section, or you can find more technical content in the <a href="https://github.com/oracle-quickstart/oci-o11y-solutions/tree/main/knowledge-content/fa-ess-scheduler/dashboards">Oracle o11y solutions GitHub repository</a>.</p>

<ul>
  <li><strong>Oracle Fusion Apps_ESS Analysis</strong>: Provides a comprehensive view of Enterprise Scheduler Service (ESS) job execution status, including total jobs run, success and failure rates, historical trends, and quick identification of failed or delayed jobs.</li>
  <li><strong>Oracle Fusion Apps_User Access Analysis</strong>: Offers in-depth insight into Fusion user access events, including login/logout activity, unique user counts, client locations, failed login attempts, and suspicious sign-in/out patterns across modules.</li>
  <li><strong>Oracle Fusion Apps_OPSS Audit Analysis</strong>: Focuses on OPSS (Oracle Platform Security Services) audit events, surfacing privileged account use, policy changes, and security-related configuration activity for compliance and incident investigation.</li>
  <li><strong>Oracle Fusion Apps_SOA</strong>: Tracks key SOA (Service-Oriented Architecture) process activity, identifying integration errors, process execution status, and bottlenecks in connected systems.</li>
  <li><strong>Oracle Fusion Apps_Data Service (MDS) Unified</strong>: Unifies visibility into Fusion Metadata Services (MDS) activities, surfacing configuration changes and important metadata management events across modules.</li>
  <li><strong>Oracle Human Capital Management_Business Objects</strong>: Monitors critical transactions and access patterns related to HCM business objects, including changes, workflows, and sensitive personnel data activity.</li>
  <li><strong>Oracle Fusion Apps_OIC Process Monitoring</strong>: Monitors Oracle Integration Cloud (OIC) process executions, integration flows, and failures relevant to Fusion Apps, providing operational assurance for cloud-based integrations.</li>
</ul>

<h3 id="understanding-the-oracle-fusion-apps-enterprise-scheduler-service-ess-analysis-dashboard">Understanding the Oracle Fusion Apps Enterprise Scheduler Service (ESS) Analysis Dashboard</h3>

<p>The ESS Analysis Dashboard is a comprehensive view of ESS job execution status that provides proactive monitoring and rapid troubleshooting capabilities. It aggregates ESS audit log data ingested via the Management Agent REST API source (configured in Part 2) and presents it through multiple visualization widgets. The following screenshot shows the ESS Analysis Dashboard:</p>
<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_ess_analysis_dashboard.png" alt="ESS Analysis Dashboard" />
<em>Figure 3: ESS Analysis Dashboard - Comprehensive view of ESS job execution status</em></p>

<p>Each widget serves a specific monitoring purpose:</p>
<ul>
  <li><strong>Real-time Job Status Monitoring</strong>: Instantly see the overall health of ESS jobs, including total jobs, success rates, and failures, without digging into each job.</li>
  <li><strong>Historical Trend Analysis</strong>: View long-term trends and patterns in job performance to spot slowdowns or recurring issues over time.</li>
  <li><strong>Cross-Module Job Correlation</strong>: See ESS job data from all Fusion modules together, making it easy to identify problems that span multiple modules.</li>
  <li><strong>Performance Degradation Detection</strong>: Quickly find jobs that are running slower than usual so you can fix problems before failures occur.</li>
  <li><strong>Schedule Optimization Insights</strong>: Use heatmaps to spot busy periods and scheduling conflicts, so you can better plan and spread out job workloads.</li>
</ul>

<p>The ESS Analysis Dashboard provides several key advantages for day-to-day operations:</p>

<ul>
  <li>
    <p><strong>At-a-Glance Health Monitoring</strong>: Administrators can quickly assess overall ESS job health for a period of time without navigating through multiple Fusion screens or manually aggregating data. The dashboard’s summary widgets (counters, donut charts, status distributions) provide immediate visibility into job execution status.</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Oracle Fusion Apps: Enterprise Scheduler Service'</span> <span class="o">|</span> <span class="n">stats</span> <span class="n">distinctcount</span><span class="p">(</span><span class="s1">'Request ID'</span><span class="p">)</span> <span class="k">as</span> <span class="n">Requests</span> <span class="k">by</span> <span class="s1">'State Description'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>

    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_ess_job_status_distribution.png" alt="ESS Job Status Distribution" />
 <em>Figure 4: ESS Job Status Distribution</em></p>
  </li>
  <li>
    <p><strong>Rapid Failure Identification</strong>: By clicking the number of failed jobs, the log explorer will open another tab with the failed jobs details and the corresponding query. The query is as follows:</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Oracle Fusion Apps: Enterprise Scheduler Service'</span> <span class="k">and</span> <span class="s1">'State Description'</span> <span class="o">=</span> <span class="n">error</span> <span class="o">|</span> <span class="n">timestats</span> <span class="n">distinctcount</span><span class="p">(</span><span class="s1">'Request ID'</span><span class="p">)</span> <span class="k">as</span> <span class="n">Requests</span> <span class="k">by</span> <span class="s1">'State Description'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>

    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_failed_jobs_details.png" alt="Failed Jobs Details" />
 <em>Figure 5: Failed Jobs Details</em></p>
  </li>
  <li>
    <p><strong>Schedule Conflict Prevention</strong>: The ESS Job Schedule Heatmap (Widget 5) visualizes execution patterns across time periods, helping administrators identify and resolve scheduling conflicts before they impact job execution.</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Oracle Fusion Apps: Enterprise Scheduler Service'</span> <span class="o">|</span> <span class="n">stats</span> <span class="n">distinctcount</span><span class="p">(</span><span class="s1">'Request ID'</span><span class="p">)</span> <span class="k">as</span> <span class="n">Requests</span> <span class="k">by</span> <span class="n">hour</span><span class="p">(</span><span class="s1">'Start Time'</span><span class="p">)</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>

    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_ess_job_schedule_heatmap.png" alt="ESS Job Schedule Heatmap" />
<em>Figure 6: ESS Job Schedule Heatmap</em></p>
  </li>
  <li>
    <p><strong>Performance Trend Awareness</strong>: Historical trend analysis helps administrators identify jobs that are gradually slowing down, allowing proactive optimization before failures occur. Widgets like “ESS Job Execution Duration Analysis” (Widget 4) and “Jobs with Execution Time Degradation” (Widget 7) surface these trends automatically.</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Oracle Fusion Apps: Enterprise Scheduler Service'</span> <span class="o">|</span> <span class="n">timestats</span> <span class="k">avg</span><span class="p">(</span><span class="n">ElapsedTime</span><span class="p">)</span> <span class="k">as</span> <span class="s1">'Avg Duration'</span><span class="p">,</span> <span class="k">max</span><span class="p">(</span><span class="n">ElapsedTime</span><span class="p">)</span> <span class="k">as</span> <span class="s1">'Max Duration'</span> <span class="k">by</span> <span class="s1">'Job Display Name'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_ess_job_execution_duration_analysis.png" alt="ESS Job Execution Duration Analysis" />
 <em>Figure 7: ESS Job Execution Duration Analysis</em></p>
  </li>
  <li>
    <p><strong>Cross-Module Impact Assessment</strong>: When investigating job failures or performance issues, administrators can quickly see which Fusion modules are affected and correlate issues across different application areas. This unified view is essential for understanding the broader impact of ESS job problems.</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Oracle Fusion Apps: Enterprise Scheduler Service'</span> <span class="o">|</span> <span class="n">stats</span> <span class="n">distinctcount</span><span class="p">(</span><span class="s1">'Request ID'</span><span class="p">)</span> <span class="k">as</span> <span class="n">Requests</span><span class="p">,</span> <span class="k">avg</span><span class="p">(</span><span class="n">ElapsedTime</span><span class="p">)</span> <span class="k">as</span> <span class="s1">'Avg Duration'</span> <span class="k">by</span> <span class="s1">'Product Family'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_ess_module_performance_impact.png" alt="ESS Job Module Performance Impact" />
 <em>Figure 8: ESS Job Module Performance Impact</em></p>
  </li>
</ul>

<h3 id="understanding-the-oracle-fusion-apps-user-access-analysis-dashboard">Understanding the Oracle Fusion Apps User Access Analysis Dashboard</h3>

<p>The User Access Analysis Dashboard is a comprehensive view of Fusion user access events that provides proactive monitoring and rapid troubleshooting capabilities. It aggregates Fusion user access audit log data ingested via the Management Agent REST API source (configured in Part 2) and presents it through multiple visualization widgets. The following screenshot shows the User Access Analysis Dashboard:</p>
<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_user_access_analysis_dashboard.png" alt="User Access Analysis Dashboard" />
<em>Figure 9: User Access Analysis Dashboard - Comprehensive view of Fusion user access events</em></p>

<p>Each widget serves a specific monitoring purpose:</p>
<ul>
  <li><strong>Real-time Login Activity Monitoring</strong>: Instantly see the overall health of Fusion user access, including total login events, success and failure rates, without digging into each login event.</li>
  <li><strong>Historical Trend Analysis</strong>: View long-term trends and patterns in login activity to spot slowdowns or recurring issues over time.</li>
  <li><strong>Cross-Module Login Correlation</strong>: See Fusion user access data from all Fusion modules together, making it easy to identify problems that span multiple modules.</li>
  <li><strong>Geographic Anomaly Detection</strong>: Identify unusual geographic access patterns that may indicate account compromise or unauthorized access.</li>
  <li>
    <p><strong>Failed Login Analysis</strong>: Track and analyze failed login attempts to identify potential security threats and brute-force attacks.</p>
  </li>
  <li>
    <p><strong>Fusion User Access Login Events Analysis</strong>: This widget displays login event counts by status (Success, Failed), providing an overview of authentication activity and helping identify authentication failures that may indicate security threats.</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Fusion Apps: Sign In - Sign Out Activity Logs'</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">rats_monitor</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">fusion_apps_osn_integ_appid</span> <span class="o">|</span> <span class="n">stats</span> <span class="k">count</span> <span class="k">as</span> <span class="s1">'Login Events '</span> <span class="k">by</span> <span class="n">Status</span> <span class="o">|</span> <span class="n">sort</span> <span class="o">-</span><span class="n">Status</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_user_access_login_events_analysis.png" alt="Fusion User Access Login Events Analysis" />
 <em>Figure 10: Fusion User Access Login Events Analysis</em></p>
  </li>
  <li>
    <p><strong>Fusion User Access Unique Users Analysis</strong>: This widget tracks the number of unique users accessing Fusion Applications over time, enabling administrators to monitor user activity trends and detect unusual spikes or drops in user engagement.</p>

    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Fusion Apps: Sign In - Sign Out Activity Logs'</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">rats_monitor</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">fusion_apps_osn_integ_appid</span> <span class="o">|</span> <span class="n">stats</span> <span class="n">distinctcount</span><span class="p">(</span><span class="s1">'User ID'</span><span class="p">)</span> <span class="k">as</span> <span class="s1">'Unique Users'</span><span class="p">,</span> <span class="n">trend</span><span class="p">(</span><span class="n">distinctcount</span><span class="p">(</span><span class="s1">'User ID'</span><span class="p">))</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_user_access_unique_users_analysis.png" alt="Fusion User Access Unique Users Analysis" />
 <em>Figure 11: Fusion User Access Unique Users Analysis</em></p>
  </li>
  <li><strong>Fusion User Access Geographic Client Locations Analysis</strong>: This widget visualizes user access by geographic location on a world map, helping identify impossible travel scenarios and unusual geographic access patterns that may indicate account compromise or unauthorized access.
    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Fusion Apps: Sign In - Sign Out Activity Logs'</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">rats_monitor</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">fusion_apps_osn_integ_appid</span> <span class="o">|</span> <span class="n">stats</span> <span class="n">distinctcount</span><span class="p">(</span><span class="s1">'User ID'</span><span class="p">)</span> <span class="k">as</span> <span class="s1">'Unique Users'</span> <span class="k">by</span> <span class="s1">'Client Host Country'</span><span class="p">,</span> <span class="s1">'Client Host City'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_user_access_geographic_client_locations_analysis.png" alt="Fusion User Access Geographic Client Locations Analysis" />
 <em>Figure 12: Fusion User Access Geographic Client Locations Analysis</em></p>
  </li>
  <li><strong>Fusion Apps: Failed Login User by City</strong>: This widget shows failed login attempts grouped by city, helping identify geographic hotspots for authentication failures that may indicate brute-force attacks or compromised credentials.
    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Fusion Apps: Sign In - Sign Out Activity Logs'</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">rats_monitor</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">fusion_apps_osn_integ_appid</span> <span class="k">and</span> <span class="s1">'Status'</span> <span class="o">=</span> <span class="s1">'Failed'</span> <span class="o">|</span> <span class="n">stats</span> <span class="k">count</span> <span class="k">as</span> <span class="n">FailedLoginCount</span> <span class="k">by</span> <span class="s1">'Client Host City'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_failed_login_user_by_city.png" alt="Fusion Apps: Failed Login User by City" />
 <em>Figure 13: Fusion Apps: Failed Login User by City</em></p>
  </li>
  <li><strong>Fusion Apps: Failed Login Top Users</strong>: This widget identifies users with the highest number of failed login attempts, helping prioritize investigation of potentially compromised accounts or brute-force attack targets.
    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Fusion Apps: Sign In - Sign Out Activity Logs'</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">rats_monitor</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">fusion_apps_osn_integ_appid</span> <span class="k">and</span> <span class="s1">'Status'</span> <span class="o">=</span> <span class="s1">'Failed'</span> <span class="o">|</span> <span class="n">stats</span> <span class="k">count</span> <span class="k">as</span> <span class="n">FailedLoginCount</span> <span class="k">by</span> <span class="s1">'User Name'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_failed_login_top_users.png" alt="Fusion Apps: Failed Login Top Users" />
 <em>Figure 14: Fusion Apps: Failed Login Top Users</em></p>
  </li>
  <li><strong>Fusion Apps: Failed Login multi-dimensional Analysis</strong>: This widget provides a multi-dimensional view of failed logins by country and city, enabling correlation analysis to identify coordinated attacks across geographic regions.
    <div class="language-sql highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="o">&lt;</span><span class="k">copy</span><span class="o">&gt;</span>
 <span class="s1">'Log Source'</span> <span class="o">=</span> <span class="s1">'Fusion Apps: Sign In - Sign Out Activity Logs'</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">rats_monitor</span> <span class="k">and</span> <span class="s1">'User ID'</span> <span class="o">!=</span> <span class="n">fusion_apps_osn_integ_appid</span> <span class="k">and</span> <span class="s1">'Status'</span> <span class="o">=</span> <span class="s1">'Failed'</span> <span class="o">|</span> <span class="n">stats</span> <span class="k">count</span> <span class="k">as</span> <span class="n">FailedLoginCount</span> <span class="k">by</span> <span class="s1">'Client Host Country'</span><span class="p">,</span> <span class="s1">'Client Host City'</span>
 <span class="o">&lt;/</span><span class="k">copy</span><span class="o">&gt;</span>
</code></pre></div>    </div>
    <p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_failed_login_multi_dimensional.png" alt="Fusion Apps: Failed Login multi-dimensional Analysis" />
 <em>Figure 15: Fusion Apps: Failed Login multi-dimensional Analysis</em></p>
  </li>
</ul>

<h3 id="ai-augmentation-enriching-fusion-log-analytics-with-genai-powered-insights">AI Augmentation: Enriching Fusion Log Analytics with GenAI-Powered Insights</h3>

<p>With the introduction of the GenAI-powered LoganAI feature in Log Analytics, this process is dramatically enhanced. Now, administrators and security teams can simply ask their questions in plain language—LoganAI automatically leverages the underlying log data as context for the large language model (LLM). This means you can get clear, actionable answers to complex operational and security queries in real time, without manually writing queries or manually preparing the data.</p>

<p>Key benefits of integrating LoganAI with Fusion log monitoring include:</p>

<ul>
  <li><strong>Natural Language Insights:</strong> Ask LoganAI direct questions like “Show the top failed login users this month” or “Summarize the recent security exceptions,” and receive tailored analytics and context from your logs, instantly.</li>
  <li><strong>Contextual, Explainable Summaries:</strong> LoganAI processes large volumes of log data—clustering, detecting patterns, and providing summarized explanations of job executions, user activities, or anomalies, turning raw logs into operational intelligence.</li>
  <li><strong>Proactive Threat Detection:</strong> By connecting the dots across audit and application logs, LoganAI can uncover rare risks or unusual activity patterns—empowering you to detect threats before they escalate.</li>
  <li><strong>AI-Augmented Dashboards:</strong> Your existing widgets and dashboards are automatically enriched with AI-powered explanations, making log data comprehensible and actionable for users of all backgrounds, not just data experts.</li>
</ul>

<p>By leveraging LoganAI’s GenAI capabilities, you move from static metrics to dynamic, AI-driven observability—enabling faster, deeper insights into both ESS job processing and Fusion user access, all by simply providing your logs as context to the LLM.</p>

<p>This section showcases how LoganAI elevates Fusion operational and security monitoring with GenAI-powered, context-aware intelligence and a conversational approach, making advanced log analytics accessible and actionable for everyone.</p>

<h2 id="prerequisite-enabling-loganai-for-ai-powered-analysis">Prerequisite: Enabling LoganAI for AI-Powered Analysis</h2>

<p>LoganAI is a generative AI-powered feature in Log Analytics that enables advanced natural language understanding, summarization, in-context assistance, and intelligent insights across various Log Analytics workflows. It leverages the OCI Generative AI service in your tenancy.
Enabling LoganAI may incur additional charges depending on usage. Please refer to OCI Generative AI Pricing for more details.
As a tenancy administrator, you can enable or disable LoganAI features in specific OCI regions and configure how Generative AI services will be used within Log Analytics.</p>

<p>That’s where OCI Log Analytics and AI-based augmentation (with LoganAI) make a significant difference. With these tools, you can:</p>
<ul>
  <li>Visualize and monitor ESS job health, failures, and performance in dynamic dashboards.</li>
  <li>Detect security threats as they emerge, leveraging both built-in analytics and customizable real-time alerts.</li>
  <li>Unlock long-term and cross-module visibility for audit logs and security events—far beyond the short history available in native Fusion screens.</li>
  <li>Take advantage of AI-powered features such as natural language queries and anomaly detection to find patterns or issues you might otherwise miss.</li>
</ul>

<h3 id="step-1-enable-loganai">Step 1: Enable LoganAI</h3>

<ul>
  <li><strong>Navigate to Log Analytics Administration</strong>:
    <ul>
      <li>Go to OCI Console &gt; Observability &amp; Management &gt; Log Analytics</li>
      <li>Click <strong>Administration</strong> in the left navigation menu</li>
      <li>Click <strong>Service Details</strong> in the left navigation menu</li>
      <li>Click <strong>Configure LoganAI Settings</strong> in Logan AI section</li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-loganai_configure_settings.png" alt="Configure LoganAI Settings" /></li>
      <li><em>Figure 16: Configure LoganAI Settings</em></li>
      <li>Update the **Preference settings for current region <region-name>**</region-name></li>
      <li>Confirm the setting to <strong>Enable LoganAI for the tenancy</strong></li>
      <li>Confirm the Oracle LLM license details</li>
      <li>Select License acceptance requirements for users</li>
      <li>Add the required policies in IAM Policies section</li>
      <li>
        <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code> allow group Log-Analytics-Users to use generative-ai-chat <span class="k">in </span>compartment <span class="nb">id </span>ocid1.compartment.oc1..aaaaaaaawaaaaaaaaaaazma
 allow group Log-Analytics-Users to <span class="nb">read </span>generative-ai-model <span class="k">in </span>compartment <span class="nb">id </span>ocid1.compartment.oc1..aaaaaaaawaaaaaaaaaaazma
 allow group Log-Analytics-Users to <span class="nb">read </span>generative-ai-endpoint <span class="k">in </span>compartment <span class="nb">id </span>ocid1.compartment.oc1..aaaaaaaawaaaaaaaaaaazma
</code></pre></div>        </div>
      </li>
      <li>Click <strong>Update LoganAI Settings</strong> to save the changes</li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-loganai_settings_updated.png" alt="LoganAI Settings Updated" /></li>
      <li><em>Figure 17: LoganAI Settings Updated</em></li>
    </ul>
  </li>
</ul>

<h3 id="step-2-using-loganai-in-log-explorer">Step 2: Using LoganAI in Log Explorer</h3>

<p>Once enabled, LoganAI is available throughout Log Explorer. The Explain feature uses artificial intelligence to summarize log messages and charts, transforming complex log data into actionable insights.
To access LoganAI Explain, click the AI icon <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_ai_icon.png" alt="AI Icon" /> wherever it appears throughout Log Explorer. The AI icon is available in various visualizations that present log records. LoganAI Explain can be utilized in the following ways:</p>

<h4 id="loganai-explain-use-cases">LoganAI Explain Use Cases</h4>

<p><strong>Single Log Explain</strong>: Click the AI icon next to any log record to instantly receive a concise summary of that entry. Ask follow-up questions or review conversation history for deeper insights—ideal for quickly understanding errors or suspicious events.</p>

<p><strong>Multi-log Explain</strong>: Summarize and analyze multiple log entries at once by clicking the AI icon above the log records. LoganAI automatically highlights key patterns and anomalies across your selection, helping you spot trends or root causes without manual review.</p>

<p><strong>Cluster Explain</strong>: Use Cluster Explain to review large volumes of similar logs. With one click, AI summarizes patterns, outliers, and potential issues within log clusters—supporting rapid identification of systemic problems or anomalies in operational data.</p>

<p><strong>Chart Explain</strong>: In Link chart visualizations, click the AI icon below the chart to get an AI-generated summary of key patterns, trends, and anomalies. You can target specific data subsets by selecting chart bubbles for focused analysis.</p>

<p>For more details, visit the <a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/how-use-loganai-explain-feature.html">Oracle Log Analytics documentation</a>.</p>

<p>Let’s see the LoganAI Explain in action with sample queries:</p>

<ul>
  <li><strong>LoganAI Cluster Explain Insights</strong>: What patterns do you see in off-hours (8am-8pm EST) logins?
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Fusion Apps: Sign In - Sign Out Activity Logs’ and ‘User ID’ not like in (rats_monitor, ‘Fusion_app%’) and ‘User ID’ != fusion_apps_osn_integ_appid</td>
              <td>timestats distinctcount(‘User ID’) as logrecords by ‘Log Source’</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Records with Histogram</li>
          <li><strong>Time Range</strong>: Last 14 days</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_pattern.png" alt="LoganAI Explain pattern" /></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>LoganAI Chart Explain Insights</strong>: Show me users with unusual login patterns that might indicate compromised accounts
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Fusion Apps: Sign In - Sign Out Activity Logs’ and ‘User ID’ != rats_monitor and Status = fail and ‘User ID’ != fusion_apps_osn_integ_appid</td>
              <td>link ‘User ID’</td>
              <td>stats unique(‘Client Host Country’) as Country</td>
              <td>eval ‘Time Window’ = ‘End Time’ - ‘Start Time’</td>
              <td>rename ‘End Time’ as ‘Last failed login’</td>
              <td>rename Count as ‘Failed Logins’</td>
              <td>rename ‘Start Time’ as ‘First failed login’</td>
              <td>classify correlate = -*, Country ‘First failed login’, ‘Failed Logins’, ‘Time Window’, ‘User ID’ as ‘Failed Logins Analysis’</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Link</li>
          <li><strong>Time Range</strong>: Last 7 days</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_chart_pattern.png" alt="LoganAI Explain Chart Pattern" /></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>LoganAI Chart Explain Insights</strong>: Which countries and cities have the highest number of failed login attempts?
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Fusion Apps: Sign In - Sign Out Activity Logs’ and ‘User ID’ != rats_monitor and ‘User ID’ != fusion_apps_osn_integ_appid</td>
              <td>link Status, ‘Client Host Country’</td>
              <td>stats unique(‘Client Host City’) as ‘Client Host City’, unique(‘Client Host Region’) as ‘Client Host Region’</td>
              <td>classify topcount = 300 correlate = -*, ‘Client Host Country’, Status ‘Start Time’, ‘Client Host City’, Count as ‘Start Time, Client Host City, Client Host Country’</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Link</li>
          <li><strong>Time Range</strong>: Last 7 days</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_chart_country_pattern.png" alt="LoganAI Explain Chart Country Pattern" /></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>LoganAI Single Log Explain Insights</strong>: What is the ESS job about?
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Oracle Fusion Apps: Enterprise Scheduler Service’</td>
              <td>timestats distinctcount(‘Request ID’) as Jobs</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Records with Histogram</li>
          <li><strong>Time Range</strong>: Last 7 days</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_single_log_job_request_details.png" alt="LoganAI Explain Single Log Job Request details" /></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>LoganAI Multiple Log Explain Insights</strong>: Which job has the longest elapsed time?
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Oracle Fusion Apps: Enterprise Scheduler Service’</td>
              <td>timestats count as logrecords by ‘Log Source’</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Records with Histogram</li>
          <li><strong>Time Range</strong>: Last 8 hours</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_multiple_log_job_request_overview.png" alt="LoganAI Explain Multiple Log Job Requests overview" /></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>LoganAI Chart Explain Insights</strong>: What ESS jobs are failing most frequently, and what are the primary reasons for the failure?
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Oracle Fusion Apps: Enterprise Scheduler Service’</td>
              <td>link ‘Request ID’</td>
              <td>stats unique(Application) as Application, avg(ElapsedTime) as E, unique(‘Instance Parent Id’) as ‘Parent ID’, unique(‘Job Display Name’) as Job, unique(‘Parent Request ID’) as ‘Parent Req ID’, unique(‘Product Name’) as Product, unique(‘Product Family’) as ‘Product Family’, latest(‘State Description’) as Status, unique(Submitter) as Submitter</td>
              <td>eval ‘Time Taken’ = unit(E, ms)</td>
              <td>eval U = url(‘https://oracle.com’, View)</td>
              <td>eventstats distinctcount(‘Request ID’) as Requests, avg(E) as AE, latest(U) as Details by Product, Job, Status</td>
              <td>eval ‘Average Time Taken’ = unit(AE, ms)</td>
              <td>createtable name = ‘Job Summary’ select Product, ‘Product Family’, Job, Status, Requests, ‘Average Time Taken’, Details</td>
              <td>classify ‘Start Time’, Job, ‘Time Taken’, Product, ‘Product Family’, Status as ‘ESS Jobs Analysis’</td>
              <td>fields -E, -AE</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Link</li>
          <li><strong>Time Range</strong>: Last 7 days</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_chart_cluster_pattern.png" alt="LoganAI Explain Chart Cluster Pattern" /></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>LoganAI Chart Explain Insights</strong>: What is causing ESS job performance degradation in the CRM module?
    <ul>
      <li>
        <table>
          <tbody>
            <tr>
              <td><strong>Query</strong>: ‘Log Source’ = ‘Oracle Fusion Apps: Enterprise Scheduler Service’</td>
              <td>cluster</td>
            </tr>
          </tbody>
        </table>
      </li>
      <li><strong>LoganAI explain</strong>:
        <ul>
          <li><strong>Visualization</strong>: Cluster</li>
          <li><strong>Time Range</strong>: Last 7 days</li>
          <li><strong>Screenshot</strong>: <img src="/images/posts/2026-01-fusion-blogs/blog-loganai_explain_cluster_analysis.png" alt="LoganAI Explain Cluster Analysis" /></li>
        </ul>
      </li>
    </ul>
  </li>
</ul>

<h4 id="best-practices-for-maximizing-loganai-explain">Best Practices for Maximizing LoganAI Explain</h4>

<p>To fully leverage LoganAI’s advanced AI-driven analysis capabilities within OCI Log Analytics, adopt these best practices:</p>

<ol>
  <li>
    <p><strong>Use ‘Log Source’ or ‘Entity’ Filtering with Cluster Visualization</strong><br />
Always apply appropriate ‘Log Source’ or ‘Entity’ filters before using Cluster visualization. This ensures that the AI summary is both relevant and focused, and enables context-rich follow-up queries for deeper insight. Precise filtering reduces noise and guides LoganAI to more actionable conclusions.</p>
  </li>
  <li>
    <p><strong>Select the Proper Time Range for the Right Level of Analysis</strong><br />
For a high-level overview or trend discovery, set broader time ranges when clustering data. For detailed, tactical analysis—such as troubleshooting or anomaly investigation—narrow the time window and use Records with Histogram visualization. Matching your time range to your investigation depth yields optimal insights and avoids information overload.</p>
  </li>
  <li>
    <p><strong>Be Aware of Cluster Group Context Window Limit (500 Items)</strong><br />
LoganAI Cluster analysis works best with smaller, well-scoped data sets. The maximum context window for a cluster group is 500 records; if your data approaches or exceeds this, the AI may hallucinate or miss important context details. For accurate root cause analysis and precise recommendations, focus on filtering to smaller, meaningful log groups.</p>
  </li>
  <li>
    <p><strong>Leverage Link Visualization and Charts for AI-Augmented Context</strong><br />
Use Link visualization and custom charts to enrich your analysis. By combining AI-derived insights with visual context, you gain a clearer picture of relationships (e.g., between users, locations, and event statuses) and subtle patterns not easily detected by raw log inspection alone.</p>
  </li>
  <li>
    <p><strong>Utilize the Custom Action Menu to Add and Augment Datasets</strong><br />
Take advantage of LoganAI in the custom action menu to bring additional datasets into your investigation. This multi-source context augments the analysis, uncovering trends or anomalies that might span modules or log types, and yielding holistic, cross-source insights.</p>
  </li>
  <li>
    <p><strong>Monitor and Manage Generative AI Usage and Cost</strong><br />
Each LoganAI Explain action consumes resources from OCI Generative AI Services, and costs are based on how often you use Explain, the size and complexity of the data, and the number of follow-up analyses. These charges are separate from standard OCI Log Analytics costs. Review the OCI Pricing guide under Generative AI Services, and plan your usage accordingly to balance insights value and budget considerations.</p>
  </li>
</ol>

<p>By following these best practices, you can maximize both the technical and business value of LoganAI in your security, compliance, and operational monitoring workflows—gaining sharper insights, accelerating investigations, and optimizing your OCI resource usage.</p>

<h3 id="conclusion">Conclusion</h3>

<p>Robust log collection, when combined with AI-driven analytics, unlocks transformative security monitoring, observability, and compliance for Oracle Fusion Applications customers. With the right permissions and access in place, organizations can efficiently ingest and analyze log data using Log Analytics and advanced tooling like LoganAI. This enables deep visibility into operations, rapid threat detection, and identification of anomalous behaviors and attack patterns—all from within unified dashboards and automated workflows.</p>

<p>LoganAI is more than a feature—it’s a leap forward in log intelligence. It makes troubleshooting faster, insights clearer, and log analytics more accessible. Whether you’re an engineer, analyst, or business stakeholder, LoganAI transforms how you understand and act on your log data.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/enable-loganai">Enable LoganAI</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/create-dashboards.html">Create Dashboards</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/query-language.html">Log Explorer Query Language</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/create-schedule-run-saved-search.html">Create Detection Rules</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/log-analytics/doc/create-alerts-detected-events.html">Create Alerts for Detected Events</a></li>
  <li><a href="https://www.ateam-oracle.com/aidriven-iam-audit-analysis-for-oracle-saas-from-raw-logs-to-actionable-security-insights-with-oci-log-analytics">AI-Driven IAM Audit Analysis for Oracle SaaS</a></li>
  <li><a href="https://www.ateam-oracle.com/beyond-monitoring-ai-driven-fusion-ess-job-health-risk-observatory-operational-intelligence-for-ess-jobs-with-oci-log-analytics">Beyond Monitoring: AI-Driven Fusion ESS Job Health Risk Observatory</a></li>
  <li><a href="https://www.ateam-oracle.com/fusion-apps-observability-by-collecting-ess-logs-using-oci-logging-analytics-rest-api-ingestion">Fusion Applications Observability: Collecting ESS Logs</a></li>
  <li><a href="https://github.com/oracle-quickstart/oci-o11y-solutions/tree/main/knowledge-content/fa-ess-scheduler/dashboards">Oracle o11y Solutions GitHub Repository</a></li>
  <li><a href="https://www.ateam-oracle.com/post/methods-and-ways-to-extract-session-information-using-oci-audit-and-integrate-into-external-systems">Methods and Ways to Extract Session Information Using OCI Audit</a></li>
  <li><a href="https://www.ateam-oracle.com/configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-1">Configure Fusion Applications Audit and Security Logs Ingestion - Part 1</a></li>
  <li><a href="https://www.ateam-oracle.com/configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-2">Configure Fusion Applications Audit and Security Logs Ingestion - Part 2</a></li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="Observability and Monitoring" /><category term="Fusion Applications" /><category term="OCI Log Analytics" /><category term="AI" /><category term="Security" /><summary type="html"><![CDATA[Gaining Insights from Fusion ESS, Audit and Security Dashboards with AI Augmentation Using LoganAI - Part 3]]></summary></entry><entry><title type="html">Configure Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics</title><link href="https://royce-fu.com/blog/configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-2/" rel="alternate" type="text/html" title="Configure Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics" /><published>2025-12-18T00:00:00+00:00</published><updated>2025-12-18T14:00:00+00:00</updated><id>https://royce-fu.com/blog/configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-2</id><content type="html" xml:base="https://royce-fu.com/blog/configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-2/"><![CDATA[<h1 id="configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics">Configure Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics</h1>

<h2 id="introduction">Introduction</h2>

<p>Oracle Fusion Applications generate extensive audit logs that capture every significant security and business event across your SaaS environment. These logs include user authentication events, authorization decisions, administrative changes, transaction-level activities, and platform-level operations. For organizations running Fusion Applications across multiple modules (ERP, HCM, SCM, CX, EPM), centralizing these audit logs in OCI Log Analytics enables:</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/kzUxTtl2MEk" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/configure-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-2.png" alt="Configure Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>OCI Log Analytics provides the ideal destination for Fusion Applications audit data, offering powerful exploration capabilities, correlation with other log sources, detection rules, and AI-powered analysis through LoganAI. By leveraging the REST API-based log collection method with OCI Management Agents, organizations can establish continuous, automated ingestion of Fusion audit logs without complex middleware or custom integrations.</p>

<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_key_use_cases.png" alt="Fusion Application Audit Logs Key Use Cases" /></p>

<p><em>Figure 1: Fusion Application Audit Logs Key Use Cases</em></p>

<p><strong>Note:</strong> If you want to monitor the ESS jobs performance and status, I have published a blog post on the Fusion Enterprise Scheduler Service (ESS) job request logs collection using OCI Management Agent and REST API log collection,  you can find it <a href="https://www.ateam-oracle.com/post/fusion-applications-observability-collecting-fusion-audit-logs-into-oci-log-analytics-using-rest-api-ingestion">here</a>.</p>

<p>However, accessing and collecting Fusion Application audit logs requires understanding the complex permission model and configuring the appropriate integration mechanisms. This blog post addresses two critical aspects:</p>

<ol>
  <li><strong>Part 1: Understanding Required Permissions</strong>: What privileges and roles are needed to access Fusion audit log data</li>
  <li><strong>Part 2: Setting Up Log Ingestion</strong>: Step-by-step configuration for Fusion Apps Audit Logs using OCI Management Agent and REST API log collection</li>
</ol>

<blockquote>
  <p><strong>Note:</strong> This guide focuses on Fusion Applications transaction and business object audit logs accessed via the Fusion Audit REST API. For IAM Identity Domain audit events (sign-in attempts, MFA challenges, session activity), these flow through OCI Audit and can be ingested via Service Connector - see <a href="https://www.ateam-oracle.com/post/methods-and-ways-to-extract-session-information-using-oci-audit-and-integrate-into-external-systems">Methods and Ways to Extract Session Information Using OCI Audit</a> for that complementary approach.</p>
</blockquote>

<h2 id="solution-design">Solution Design</h2>

<p>Oracle Log Analytics enables continuous collection of Fusion Application audit logs through REST API-based log sources. The Management Agent acts as the collector, periodically invoking Fusion Applications REST APIs to fetch audit log data and forwarding it to Log Analytics for parsing, indexing, and analysis.</p>

<p><strong>Reference Architecture:</strong></p>

<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_ref_architecture.png" alt="Fusion Application Audit Logs Reference Architecture" /></p>

<p><em>Figure 2: Fusion Application Audit Logs Reference Architecture</em></p>

<h3 id="prerequisites">Prerequisites</h3>

<p>Before proceeding with the implementation, ensure you have:</p>

<ul>
  <li>An active OCI tenancy with appropriate IAM permissions</li>
  <li>Access to Oracle Fusion Applications with administrative privileges</li>
  <li>An OCI Compute instance (Oracle Linux) where the Management Agent will be installed</li>
  <li>Network connectivity between the Management Agent host and your Fusion Applications instance</li>
  <li>Understanding of your Fusion Applications POD URL and LOGIN URL (refer to Doc ID 2661308.1 in Oracle My Support)</li>
  <li>Create a service account in Fusion Applications for the Management Agent to use</li>
</ul>

<h2 id="part-2-step-by-step-setup-for-ingesting-fusion-application-audit-logs">Part 2: Step-by-Step Setup for Ingesting Fusion Application Audit Logs</h2>

<p>This section provides detailed step-by-step instructions for setting up Fusion Application audit log collection using the Management Agent and REST API log ingestion method.</p>

<p>Note: OCI Log Analytics provides pre-defined log sources and parsers for Fusion Applications audit logs.</p>

<ul>
  <li><strong>Fusion Apps: SOA Audit Logs</strong></li>
  <li><strong>Fusion Apps: Sign In - Sign Out Activity Logs</strong></li>
  <li><strong>Fusion Apps: OPSS Audit Logs</strong></li>
  <li><strong>Fusion Apps: ODI Audit Logs</strong></li>
  <li><strong>Fusion Apps: OBIEE Audit Logs</strong></li>
  <li><strong>Fusion Apps: MDS Audit Logs</strong></li>
  <li><strong>Fusion Apps: HCM People Audit Logs</strong></li>
  <li><strong>Fusion Apps: HCM Payroll Audit Logs</strong></li>
</ul>

<h3 id="prerequisites-1">Prerequisites</h3>

<p>Before you set up log ingestion for Fusion Application Audit logs, ensure the following prerequisites are met:</p>

<ul>
  <li>
    <p>Review the <a href="https://docs.oracle.com/en/cloud/saas/applications-common/24b/faaps/">Fusion Applications REST API documentation</a> to understand how to use the Audit Logs APIs, available endpoints, supported log types, and query mechanisms.</p>
  </li>
  <li>
    <p>Ensure you have valid Fusion Applications credentials (username and password) with sufficient privileges to access the Audit Logs REST API. Privileges are typically assigned via appropriate Fusion Applications roles.</p>
  </li>
  <li>Identify and note the required endpoints for your Fusion application instance:
    <ul>
      <li><strong>login_url</strong>: The login URL for Fusion Applications (e.g., <code class="language-plaintext highlighter-rouge">https://&lt;identity-domain&gt;.fa.&lt;region&gt;.oraclecloud.com</code>)</li>
      <li><strong>pod_url</strong>: The base URL for your Fusion Applications pod (e.g., <code class="language-plaintext highlighter-rouge">https://&lt;identity-domain&gt;.fa.&lt;region&gt;.oraclecloud.com</code>)</li>
      <li><strong>proxy_url</strong> (Optional): If your environment requires access through a proxy, provide the proxy server URL (<code class="language-plaintext highlighter-rouge">http(s)://&lt;proxy-host&gt;:&lt;proxy-port&gt;</code>).</li>
      <li>For more information on constructing and locating Fusion Application instance URLs, refer to <a href="https://support.oracle.com/epmos/faces/DocumentDisplay?id=2661308.1">Oracle My Support Doc ID 2661308.1</a>.</li>
    </ul>

    <blockquote>
      <p><strong>Note:</strong> Sign-in Sign-out REST API is deprecated and no longer available after Fusion Identity Upgrade, starting Oracle Fusion 25B or higher. You will have to use the OCI Audit feature as per KB181606</p>
    </blockquote>
  </li>
  <li>Ensure Fusion Applications REST API access is enabled for your environment:
    <ul>
      <li>Confirm that users or application clients have the necessary REST API security privileges and duty roles to access audit logs endpoints.</li>
      <li>This includes role assignments such as <code class="language-plaintext highlighter-rouge">FND_VIEW_AUDIT_HISTORY_PRIV</code> and other relevant product/duty roles depending on the audit log type.</li>
      <li>REST API access is typically controlled by user provisioning or within the Fusion Applications Security Console.</li>
      <li>See <a href="https://docs.oracle.com/en/cloud/saas/applications-common/24b/faaps/">Fusion Apps REST API Security Overview</a> for details on configuring user access.</li>
    </ul>
  </li>
  <li>(Optional) If outbound network traffic from the Management Agent host to Fusion Applications must traverse a proxy, ensure the proxy URL and credentials are available. Verify network routing allows connections from your OCI environment to the Fusion Applications REST endpoints.</li>
</ul>

<h3 id="step-1-install-and-configure-management-agent">Step 1: Install and Configure Management Agent</h3>

<ul>
  <li><strong>Provision OCI Compute Instance</strong>:
    <ul>
      <li>Provision an OCI Compute instance with Oracle Linux image</li>
      <li>Ensure the instance has HTTP/HTTPS access to your Fusion Applications POD URL</li>
      <li>Note the instance name (e.g., <code class="language-plaintext highlighter-rouge">mgmtagent-vm</code>)</li>
    </ul>
  </li>
  <li><strong>Enable Management Agent Plugin</strong>:
    <ul>
      <li>Navigate to OCI Console &gt; Compute &gt; Instances</li>
      <li>Select your compute instance</li>
      <li>Go to the <strong>Oracle Cloud Agent</strong> tab</li>
      <li>Enable the <strong>Management Agent</strong> plugin</li>
      <li>Ensure the <strong>Logging Analytics</strong> plugin is deployed during installation</li>
      <li>Reference: <a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/set-continuous-log-collection-form-your-hosts.html">Set Up Continuous Log Collection From Your Hosts</a></li>
    </ul>
  </li>
  <li><strong>Fusion Applications Entity Creation</strong>:
    <ul>
      <li>An entity of type “Host (Linux)” will be automatically created in Log Analytics</li>
      <li>Navigate to OCI Console &gt; Observability &amp; Management &gt; Log Analytics &gt; Administration &gt; Entities</li>
      <li>Verify the entity exists in the same compartment as your compute instance</li>
      <li>Note the entity name (should match your instance name, e.g., <code class="language-plaintext highlighter-rouge">mgmtagent-vm</code>)</li>
      <li>Create a new entity with the following details:
        <ul>
          <li><strong>Name</strong>: <code class="language-plaintext highlighter-rouge">fusion-apps-mgmtagent-vm</code></li>
          <li><strong>Entity Type</strong>: <code class="language-plaintext highlighter-rouge">Oracle Fusion Applications</code></li>
          <li><strong>Management Agent Compartment</strong>: <code class="language-plaintext highlighter-rouge">your_mgmtagent_compartment_name</code></li>
          <li><strong>Management Agent</strong>: <code class="language-plaintext highlighter-rouge">Agent(mgmtagent-vm)</code></li>
          <li><strong>Properties</strong>:
            <ul>
              <li><strong>Property Name</strong>: <code class="language-plaintext highlighter-rouge">login_url</code></li>
              <li><strong>Property Value</strong>: The base URL of your Fusion Applications instance (e.g., <code class="language-plaintext highlighter-rouge">https://&lt;yourpod&gt;.login.fa.us1.oraclecloud.com</code>)</li>
              <li><strong>Property Name</strong>: <code class="language-plaintext highlighter-rouge">pod_url</code></li>
              <li><strong>Property Value</strong>: The base URL of your Fusion Applications instance (e.g., <code class="language-plaintext highlighter-rouge">https://&lt;yourpod&gt;.fa.us1.oraclecloud.com</code>)</li>
              <li><strong>Property Name</strong>: <code class="language-plaintext highlighter-rouge">proxy_url</code></li>
              <li><strong>Property Value</strong>: (Optional) The URL that sends a request to your proxy server</li>
            </ul>
          </li>
          <li><strong>Agent Collection Properties</strong>:
            <ul>
              <li><strong>Source Type</strong>: <code class="language-plaintext highlighter-rouge">REST API</code></li>
              <li><strong>Historical Data</strong>: <code class="language-plaintext highlighter-rouge">30D</code> (or your desired historical data fetching period)</li>
              <li><strong>Enable Filter Duplicate Records</strong>: <code class="language-plaintext highlighter-rouge">true</code></li>
              <li><strong>Customized Schedule</strong>: <code class="language-plaintext highlighter-rouge">FREQ=MINUTELY;INTERVAL=5</code> (5 mins or your desired schedule interval)</li>
            </ul>
          </li>
          <li>Click <strong>Create</strong></li>
          <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_entity_creation.png" alt="Fusion Applications Entity Creation" /></li>
          <li><em>Figure 3: Fusion Applications Entity Creation</em></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>Configure IAM Policies</strong>:
    <ul>
      <li>Ensure policies are in place to allow Management Agent to send logs</li>
      <li>Reference: <a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/allow-continuous-log-collection-using-management-agents.html">Allow Continuous Log Collection Using Management Agents</a></li>
    </ul>
  </li>
</ul>

<h3 id="step-2-configure-management-agent-credentials">Step 2: Configure Management Agent Credentials</h3>

<ul>
  <li><strong>SSH to the Compute Instance</strong>:
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code> ssh opc@&lt;your-mgmtagent-vm-compute-instance-ip&gt;
</code></pre></div>    </div>
  </li>
  <li><strong>Switch to Root User</strong> (if needed):
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="nb">sudo </span>su -
</code></pre></div>    </div>
  </li>
  <li><strong>Navigate to Management Agent Bin Directory</strong>:
    <ul>
      <li>For Management Agents running via Oracle Cloud Agent plugin:
        <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cd</span> /var/lib/oracle-cloud-agent/plugins/oci-managementagent/polaris/agent_inst/bin
</code></pre></div>        </div>
      </li>
      <li>For manually installed Management Agents:
        <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cd</span> /opt/oracle/mgmt_agent/agent_inst/bin
</code></pre></div>        </div>
      </li>
    </ul>
  </li>
  <li><strong>Create Credential JSON File</strong>:
 Navigate to the appropriate /bin directory for your setup to create the credential JSON file. The following example shows the values provided in the <code class="language-plaintext highlighter-rouge">fapps.json</code> file:
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="nb">cat</span> <span class="o">&gt;</span> /tmp/FA-CREDS.json <span class="o">&lt;&lt;</span> <span class="no">EOF</span><span class="sh">
 {
       "source": "lacollector.la_rest_api",
       "name": "FA-CREDS",
       "type": "HTTPSBasicAuthCreds",
       "description": "These are HTTPS (BasicAuth) credentials.",
       "properties": [
          {
             "name": "HTTPSUserName",
             "value": "USER"
          },
          {
             "name": "HTTPSPassword",
             "value": "PASS"
          }
       ]
 }
</span><span class="no"> EOF
</span></code></pre></div>    </div>

    <p>Replace <code class="language-plaintext highlighter-rouge">your_service_account_username</code> and <code class="language-plaintext highlighter-rouge">your_service_account_password</code> with your Fusion Applications service account credentials.</p>
  </li>
  <li><strong>Insert Credentials into Agent Credential Store</strong>:
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code> <span class="nb">cat </span>fapps.json | ./credential_mgmt.sh <span class="nt">-s</span> logan <span class="nt">-o</span> upsertCredentials
</code></pre></div>    </div>
  </li>
  <li><strong>Verify Credential Storage</strong>:
    <div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code> ./credential_mgmt.sh <span class="nt">-o</span> listCredentials <span class="nt">-s</span> logan | <span class="nb">grep </span>FA-CREDS
</code></pre></div>    </div>

    <p>Reference: <a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/rest-api-log-collection.html#LOGAN-GUID-17E91D5F-5EE3-42EB-8214-1D4597432D6C">Management Agent Source Credentials</a></p>
  </li>
</ul>

<h3 id="step-3-associate-source-with-entity-and-start-collection">Step 3: Associate Source with Entity and Start Collection</h3>

<ul>
  <li><strong>Validate the Log Source Endpoint Configuration</strong>:
    <ul>
      <li>Navigate to OCI Console &gt; Observability &amp; Management &gt; Log Analytics &gt; Administration &gt; Sources</li>
      <li>Click on the log source (e.g., <code class="language-plaintext highlighter-rouge">Fusion Apps: Sign In - Sign Out Activity Logs</code>)</li>
      <li>Click <strong>Customize</strong></li>
      <li>Click the endpoint … &gt; View to inspect the endpoint configuration</li>
    </ul>
  </li>
  <li><strong>Navigate to Entity Details</strong>:
    <ul>
      <li>Go to OCI Console &gt; Observability &amp; Management &gt; Log Analytics &gt; Administration &gt; Entities</li>
      <li>Click on your entity (e.g., <code class="language-plaintext highlighter-rouge">fusion-apps-mgmtagent-vm</code>)</li>
    </ul>
  </li>
  <li><strong>Add Data Source</strong>:
    <ul>
      <li>Click <strong>Add Data</strong></li>
      <li>Select the entity (e.g., <code class="language-plaintext highlighter-rouge">fusion-apps-mgmtagent-vm</code>)</li>
      <li>Click <strong>Next</strong></li>
    </ul>
  </li>
  <li><strong>Select Log Sources</strong>:
    <ul>
      <li>Search for <strong>Fusion Apps:</strong> to filter Fusion Applications sources</li>
      <li>Select the log sources you want to collect (e.g., <code class="language-plaintext highlighter-rouge">Fusion Apps: Sign In - Sign Out Activity Logs, Fusion Apps: OPSS Audit Logs, Fusion Apps: ESS Audit Logs</code>)</li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_select_log_sources.png" alt="Select Log Sources" /></li>
      <li><em>Figure 4: Log Analytics Fusion Apps Audit Select Log Sources</em></li>
      <li>Verify the Agent Collection Properties are correctly configured</li>
      <li>Select the correct log group to store log data for new association</li>
      <li>Click <strong>Validate and configure log collection</strong></li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_validate_and_configure_log_collection.png" alt="Validate and configure log collection" /></li>
      <li><em>Figure 5: Log Analytics Fusion Apps Audit Validate and Configure Log Collection</em></li>
    </ul>
  </li>
  <li><strong>Start Collection</strong>:
    <ul>
      <li>Once configured, click <strong>Take me to Log Explorer</strong> to verify log ingestion</li>
    </ul>
  </li>
</ul>

<h3 id="step-4-verify-log-ingestion">Step 4: Verify Log Ingestion</h3>

<ul>
  <li><strong>Navigate to Log Explorer</strong>:
    <ul>
      <li>Go to OCI Console &gt; Observability &amp; Management &gt; Log Analytics &gt; Log Explorer</li>
      <li>Or use the link provided after configuration</li>
    </ul>
  </li>
  <li><strong>Query Audit Logs</strong>:
    <ul>
      <li>In the search bar, enter a query to find Fusion Applications Sign-in/Sign-out activity logs:
        <div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>'Log Source' in ('Fusion Apps: ESS Audit Logs', 'Oracle Fusion Apps: OPSS Audit Logs', 'Fusion Apps: OPSS Audit Logs', 'Fusion Apps: MDS Audit Logs') | stats count as logrecords by 'Log Source' | sort -logrecords
</code></pre></div>        </div>
      </li>
      <li>To verify sign-in/sign-out activity (if enabled):
        <div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>'Log Source' = 'Fusion Apps: Sign In - Sign Out Activity Logs' | stats count as logrecords by 'Log Source' | sort -logrecords
</code></pre></div>        </div>
      </li>
      <li>Adjust the time range to see recent logs</li>
      <li>Click <strong>Run Query</strong></li>
    </ul>
  </li>
</ul>

<h3 id="step-5-import-dashboards">Step 5: Import Dashboards</h3>

<ul>
  <li><strong>Locate Dashboards on GitHub</strong>:
    <ul>
      <li>Find the pre-built Log Analytics dashboard JSON files for Fusion Apps audit logs on the <a href="https://github.com/oracle-quickstart/oci-o11y-solutions/tree/main/knowledge-content/fa-ess-scheduler/dashboards">Oracle o11y solutions GitHub repository</a>.</li>
      <li>Common dashboard files:
        <ul>
          <li><code class="language-plaintext highlighter-rouge">Oracle Fusion User Access.json</code></li>
          <li><code class="language-plaintext highlighter-rouge">Oracle Fusion Apps_OPSS Audit Analysis.json</code></li>
          <li><code class="language-plaintext highlighter-rouge">Oracle Fusion Apps_SOA.json</code></li>
          <li><code class="language-plaintext highlighter-rouge">Oracle Fusion Apps_Data Service (MDS) Unified.json</code></li>
          <li><code class="language-plaintext highlighter-rouge">Oracle Human Capital Management_Business Objects.json</code></li>
          <li><code class="language-plaintext highlighter-rouge">Fusion OIC Process Monitoring.json</code></li>
        </ul>
      </li>
    </ul>
  </li>
  <li><strong>Import the Dashboard in OCI Log Analytics</strong>:
    <ul>
      <li>Go to <strong>OCI Console → Observability &amp; Management → Log Analytics → Dashboards</strong>.</li>
      <li>Click on <strong>Import dashboards</strong>.</li>
      <li>Browse to the downloaded dashboard <code class="language-plaintext highlighter-rouge">.json</code> file and select it.</li>
    </ul>
  </li>
</ul>

<h2 id="conclusion">Conclusion</h2>

<p>By following the process outlined in this guide, you can establish a robust and streamlined approach to collecting, monitoring, and analyzing audit logs from Oracle Fusion Applications within OCI Log Analytics. Automating audit log ingestion via REST APIs and the OCI Management Agent empowers your organization to consolidate critical audit and user activity data in one place—enabling you to:</p>

<ul>
  <li><strong>Increase Visibility and Control</strong>: Monitor user interactions and system events across Fusion Applications to strengthen governance and transparency.</li>
  <li><strong>Simplify Compliance Reporting</strong>: Generate comprehensive audit trails that support both external regulatory requirements and internal policies.</li>
  <li><strong>Drive Operational Insight</strong>: Leverage centralized log data to uncover usage trends, improve business processes, and support data-driven decision making.</li>
  <li><strong>Accelerate Threat Detection</strong>: Quickly identify anomalies and act on potential threats using advanced analytics and visualization capabilities.</li>
</ul>

<p>Integrating your Fusion Applications audit logs with OCI Log Analytics not only simplifies adherence to audit and compliance obligations, but also transforms raw log data into actionable intelligence. This approach enhances your organization’s ability to safeguard data, comply with regulations, and maximize the value derived from your Oracle Cloud investments.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/faucf/assign-roles-for-access-to-manage-scheduled-processes.html">ESS Roles Documentation</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/ochus/enable-audit-for-oracle-platform-security-services.html">Enable Audit for Oracle Platform Security Services</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/rest-api-log-collection.html">Set Up REST API Log Collection</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/rest-api-log-collection.html#LOGAN-GUID-17E91D5F-5EE3-42EB-8214-1D4597432D6C">Ingest Fusion Applications Audit Logs</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/applications-common/25d/facia/audit-policies.html">Fusion Applications Audit Policies</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/applications-common/25d/farca/api-audit-report.html">Fusion Applications Audit Report API</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/farws/Authorize.html">HCM REST API Authorization</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/ochus/get-user-sign-in-sign-out-information.html">How to Get User Sign-in Sign-out Information?</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/fusion-service/faiec/create-a-fusion-service-integration-user-account-for-other.html">Create a Fusion Service Integration User Account</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/applications-common/24c/farca/Quick_Start.html">REST API Quick Start</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/set-continuous-log-collection-form-your-hosts.html">Set Up Continuous Log Collection From Your Hosts</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/allow-continuous-log-collection-using-management-agents.html">Allow Continuous Log Collection Using Management Agents</a></li>
  <li><a href="https://docs.oracle.com/en-us/iaas/logging-analytics/doc/rest-api-log-collection.html#LOGAN-GUID-17E91D5F-5EE3-42EB-8214-1D4597432D6C">Management Agent Source Credentials</a></li>
  <li>Doc ID 2661308.1 - Fusion Applications URLs and Configuration</li>
  <li>Doc ID 2059102.1 - How To Configure And Use Audit In BI Publisher For Fusion SaaS Cloud Customers</li>
  <li>Doc ID 2731495.1 - Fusion Applications OTBI: How To Configure And Use Audit For Usage and Performance In OTBI For Fusion SaaS Cloud Customers</li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="Observability and Monitoring" /><category term="Fusion Applications" /><category term="OCI Log Analytics" /><category term="Security" /><summary type="html"><![CDATA[Configure Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics]]></summary></entry><entry><title type="html">Understand Required Permissions for Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics - Part 1</title><link href="https://royce-fu.com/blog/understand-required-permissions-for-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-1/" rel="alternate" type="text/html" title="Understand Required Permissions for Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics - Part 1" /><published>2025-12-17T00:00:00+00:00</published><updated>2025-12-17T14:00:00+00:00</updated><id>https://royce-fu.com/blog/understand-required-permissions-for-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-1</id><content type="html" xml:base="https://royce-fu.com/blog/understand-required-permissions-for-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-1/"><![CDATA[<h1 id="understand-required-permissions-for-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics---part-1">Understand Required Permissions for Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics - Part 1</h1>

<h2 id="introduction">Introduction</h2>

<p>Oracle Fusion Applications generate extensive audit logs that capture every significant security and business event across your SaaS environment. These logs include user authentication events, authorization decisions, administrative changes, transaction-level activities, and platform-level operations. For organizations running Fusion Applications across multiple modules (ERP, HCM, SCM, CX, EPM), centralizing these audit logs in OCI Log Analytics enables:</p>

<!-- nblm-media-start -->

<!-- Courtesy of embedresponsively.com -->

<div class="responsive-video-container">
    <iframe src="https://www.youtube-nocookie.com/embed/wNdZPctrHF0" frameborder="0" webkitallowfullscreen="" mozallowfullscreen="" allowfullscreen=""></iframe>
  </div>

<p><img src="/images/posts/notebooklm/understand-required-permissions-for-fusion-applications-audit-and-security-logs-ingestion-in-oci-log-analytics-part-1.png" alt="Understand Required Permissions for Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics - Part 1 — infographic overview" class="align-center" />
<!-- nblm-media-end --></p>

<p>OCI Log Analytics provides the ideal destination for Fusion Applications audit data, offering powerful exploration capabilities, correlation with other log sources, detection rules, and AI-powered analysis through LoganAI. By leveraging the REST API-based log collection method with OCI Management Agents, organizations can establish continuous, automated ingestion of Fusion audit logs without complex middleware or custom integrations.</p>

<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_key_use_cases.png" alt="Fusion Application Audit Logs Key Use Cases" /></p>

<p><em>Figure 1: Fusion Application Audit Logs Key Use Cases</em></p>

<p><strong>Note:</strong> If you want to monitor the ESS jobs performance and status, I have published a blog post on the Fusion Enterprise Scheduler Service (ESS) job request logs collection using OCI Management Agent and REST API log collection,  you can find it <a href="https://www.ateam-oracle.com/post/fusion-applications-observability-collecting-fusion-audit-logs-into-oci-log-analytics-using-rest-api-ingestion">here</a>.</p>

<p>However, accessing and collecting Fusion Application audit logs requires understanding the complex permission model and configuring the appropriate integration mechanisms. This blog post addresses two critical aspects:</p>

<ol>
  <li><strong>Part 1: Understanding Required Permissions</strong>: What privileges and roles are needed to access Fusion audit log data</li>
  <li><strong>Part 2: Setting Up Log Ingestion</strong>: Step-by-step configuration for Fusion Apps Audit Logs using OCI Management Agent and REST API log collection</li>
</ol>

<blockquote>
  <p><strong>Note:</strong> This guide focuses on Fusion Applications transaction and business object audit logs accessed via the Fusion Audit REST API. For IAM Identity Domain audit events (sign-in attempts, MFA challenges, session activity), these flow through OCI Audit and can be ingested via Service Connector - see <a href="https://www.ateam-oracle.com/post/methods-and-ways-to-extract-session-information-using-oci-audit-and-integrate-into-external-systems">Methods and Ways to Extract Session Information Using OCI Audit</a> for that complementary approach.</p>
</blockquote>

<h2 id="solution-design">Solution Design</h2>

<p>Oracle Log Analytics enables continuous collection of Fusion Application audit logs through REST API-based log sources. The Management Agent acts as the collector, periodically invoking Fusion Applications REST APIs to fetch audit log data and forwarding it to Log Analytics for parsing, indexing, and analysis.</p>

<p><strong>Reference Architecture:</strong></p>

<p><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_ref_architecture.png" alt="Fusion Application Audit Logs Reference Architecture" /></p>

<p><em>Figure 2: Fusion Application Audit Logs Reference Architecture</em></p>

<h3 id="prerequisites">Prerequisites</h3>

<p>Before proceeding with the implementation, ensure you have:</p>

<ul>
  <li>An active OCI tenancy with appropriate IAM permissions</li>
  <li>Access to Oracle Fusion Applications with administrative privileges</li>
  <li>An OCI Compute instance (Oracle Linux) where the Management Agent will be installed</li>
  <li>Network connectivity between the Management Agent host and your Fusion Applications instance</li>
  <li>Understanding of your Fusion Applications POD URL and LOGIN URL (refer to Doc ID 2661308.1 in Oracle My Support)</li>
  <li>Create a service account in Fusion Applications for the Management Agent to use</li>
</ul>

<h2 id="part-1-understanding-required-fusion-applications-audit-and-security-logs-permissions">Part 1: Understanding Required Fusion Applications Audit and Security Logs Permissions</h2>

<p>Accessing Fusion Application audit logs requires a combination of Fusion Applications privileges. This section provides a comprehensive overview of the permission requirements.</p>

<h3 id="service-account-setup">Service Account Setup</h3>

<p>For REST API access, you need to create a service account (integration user) in Fusion Applications:</p>

<ul>
  <li><strong>Sign in</strong> to Oracle Fusion Applications using administrator privileges.</li>
  <li><strong>Navigate</strong> to:
    <ul>
      <li><strong>Tools</strong> &gt; <strong>Security Console</strong> &gt; <strong>Users</strong></li>
    </ul>
  </li>
  <li><strong>Create a service account (integration user)</strong> with the following details:
    <ul>
      <li><strong>Last Name</strong>: <code class="language-plaintext highlighter-rouge">SERVICE_APP_ICS_ID</code></li>
      <li><strong>Email</strong>: <em>Valid email address</em></li>
      <li><strong>User Name</strong>: <code class="language-plaintext highlighter-rouge">SERVICE_APP_ICS_ID</code></li>
      <li><strong>Person Type</strong>: None</li>
    </ul>
  </li>
</ul>

<h3 id="recommended-core-audit-and-security-logs-privileges">Recommended Core Audit and Security Logs Privileges</h3>

<h4 id="sign-in---sign-out-activity-logs">Sign In - Sign Out Activity Logs</h4>

<p>You can get the last seven days of user sign-in sign-out information using a setting available on the Add User Account page in Security Console. To view the setting, you must enable a profile option.</p>

<p>Note: Update the configuration of the <strong>Sign-In/Sign-Out</strong> audit data requires Fusion Apps Administrator or Security Administrator privilege, or make sure the admin account user has FND_MANAGE_AUDIT_POLICIES_PRIV.</p>

<ul>
  <li>The <strong>Sign-In/Sign-Out</strong> audit data requires an additional Fusion Applications enablement step that is <strong>separate from role/privilege assignment</strong>.</li>
  <li><strong>Data availability limitation</strong>: <strong>Sign-In/Sign-Out</strong> audit data is available for <strong>the last seven days</strong> only.</li>
  <li><strong>Enable the profile option</strong>:
    <ul>
      <li>In <strong>Setup and Maintenance</strong></li>
      <li>Open the side bar to search task</li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_search_task.png" alt="Search task" /></li>
      <li><em>Figure 3: Fusion Applications Audit LogsSearch task</em></li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_search_task_manage_admin_profile_values.png" alt="Search task" /></li>
      <li><em>Figure 4: Fusion Applications Audit Logs Search task Manage Administrator Profile Values</em></li>
      <li>Open the task <strong>Manage Administrator Profile Values</strong></li>
      <li>Search for <strong>Profile Option Code</strong>: <code class="language-plaintext highlighter-rouge">ASE_ADVANCED_USER_MANAGEMENT_SETTING</code></li>
      <li>Set the profile option value <strong>Site</strong> to <strong>Yes</strong></li>
      <li>Click <strong>Save and Close</strong></li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_manage_admin_profile_values.png" alt="Manage Administrator Profile Values" /></li>
      <li><em>Figure 5: Fusion Applications Audit Logs Manage Administrator Profile Values</em></li>
    </ul>
  </li>
  <li><strong>Enable administration access for the integration user</strong>:
    <ul>
      <li>In <strong>Security Console</strong>, go to <strong>Users</strong></li>
      <li>Open the integration user (or when creating it via <strong>Add User Account</strong>)</li>
      <li>In <strong>Advanced Information</strong>, enable <strong>Enable Administration Access for Sign In-Sign Out Audit REST API</strong></li>
    </ul>
  </li>
  <li>Reference: <a href="https://docs.oracle.com/en/cloud/saas/human-resources/ochus/get-user-sign-in-sign-out-information.html">How to Get User Sign-in Sign-out Information?</a></li>
</ul>

<h4 id="fusion-erp-hcm-scm-cx-audit-logs">Fusion ERP, HCM, SCM, CX Audit Logs</h4>

<table>
  <thead>
    <tr>
      <th>Role/Privilege</th>
      <th>Provides</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td><code class="language-plaintext highlighter-rouge">ASE_REST_SERVICE_ACCESS_IDENTITY_INTEGRATION_PRIV</code></td>
      <td>Access to Fusion REST API endpoints: fscmRestApi, fndAuditRESTService, audittrail, getaudithistory</td>
    </tr>
  </tbody>
</table>

<ul>
  <li><strong>Sign in</strong> to Oracle Fusion Applications using administrator privileges.</li>
  <li><strong>Navigate</strong> to:
    <ul>
      <li><strong>Tools</strong> &gt; <strong>Security Console</strong> &gt; <strong>Roles</strong></li>
    </ul>
  </li>
  <li><strong>Create a service account custom role</strong> with the following details:
    <ul>
      <li><strong>Role Name</strong>: <code class="language-plaintext highlighter-rouge">SERVICE_APP_ICS_ID_ROLE</code></li>
      <li><strong>Role Code</strong>: <code class="language-plaintext highlighter-rouge">SERVICE_APP_ICS_ID_ROLE</code></li>
      <li><strong>Role Category</strong>: <code class="language-plaintext highlighter-rouge">Common - Job Roles</code></li>
      <li><strong>Role Privilege</strong>:
        <ul>
          <li>Add the following Function Security Policy <code class="language-plaintext highlighter-rouge">ASE_REST_SERVICE_ACCESS_IDENTITY_INTEGRATION_PRIV</code></li>
          <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_add_function_security_policy.png" alt="Add Function Security Policy" /></li>
          <li><em>Figure 6: Fusion Applications Audit Logs Add Function Security Policy</em></li>
          <li>Click <strong>Next</strong></li>
        </ul>
      </li>
      <li>Add User <code class="language-plaintext highlighter-rouge">SERVICE_APP_ICS_ID</code> to the custom role <code class="language-plaintext highlighter-rouge">SERVICE_APP_ICS_ID_ROLE</code></li>
      <li>Click <strong>Save and Close</strong></li>
    </ul>
  </li>
</ul>

<h4 id="oracle-platform-security-services-opss-audit-logs">Oracle Platform Security Services (OPSS) Audit Logs</h4>

<p>Oracle Platform Security Services (OPSS) audit enables auditing of security-related events, such as authentication and authorization, across Oracle Fusion Applications. To enable OPSS audit logging, follow these steps:</p>

<p>By default, auditing is disabled for all Oracle Fusion Applications, including Oracle Platform Security Services (OPSS). To enable or disable auditing for OPSS, follow these steps:</p>

<ul>
  <li><strong>Access Manage Audit Policies:</strong>
    <ul>
      <li>In the <strong>Setup and Maintenance</strong> work area, search for and select the <strong>Manage Audit Policies</strong> task.</li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_search_task_manage_audit_policies.png" alt="Search task" /></li>
      <li><em>Figure 7: Fusion Applications Audit Logs Search task Manage Audit Policies</em></li>
    </ul>
  </li>
  <li><strong>Set Audit Level for OPSS:</strong>
    <ul>
      <li>On the <strong>Manage Audit Policies</strong> page, locate <strong>Oracle Platform Security Services</strong> in the list.</li>
      <li>To enable auditing, set the <strong>Audit Level</strong> to <code class="language-plaintext highlighter-rouge">Low - Critical Events Only</code>.</li>
      <li>To disable auditing, set the <strong>Audit Level</strong> to <code class="language-plaintext highlighter-rouge">None</code>.</li>
      <li>Click <strong>Save and Close</strong> to confirm and apply your changes.</li>
    </ul>
  </li>
</ul>

<blockquote>
  <p><strong>Note:</strong></p>
  <ul>
    <li>To manage audit policies, you must have the <strong>Manage Audit Policies</strong> (<code class="language-plaintext highlighter-rouge">FND_MANAGE_AUDIT_POLICIES_PRIV</code>) function security privilege. The predefined <strong>Application Implementation Consultant</strong> job role includes this privilege. If you want to want to use the <strong>Security - Audit Real Time</strong> subject area in Oracle Transactional Business Intelligence (OTBI) to access OPSS audit data. Access to this OTBI subject area requires the <code class="language-plaintext highlighter-rouge">FBI_SECURITY_TRANSACTION_ANALYSIS_DUTY</code> duty role. The predefined <strong>IT Security Manager</strong> job role contains this duty role.</li>
  </ul>
</blockquote>

<h4 id="enterprise-scheduler-service-ess-job-request-logs">Enterprise Scheduler Service (ESS) Job Request Logs</h4>

<p>Users can view and manage the scheduled processes that they submit, for example, to cancel the process or see the output. However, to perform these actions for scheduled processes submitted by other users, specific roles are required.</p>

<p><strong>ESS Monitor Role</strong> is sufficient for viewing the scheduled process history.</p>

<p>The privilege required to access for all Scheduled Process is <code class="language-plaintext highlighter-rouge">ESS_REQUEST_HISTORY</code>.</p>

<ul>
  <li>Open <strong>Security Console</strong> and go to the <strong>Roles</strong> page. Click <strong>Create Role</strong>.</li>
  <li><em>(Optional)</em> On the <strong>Data Security Policies</strong> page:
    <ul>
      <li>Add a policy with:
        <ul>
          <li><strong>Data Resource:</strong> <code class="language-plaintext highlighter-rouge">ESS_REQUEST_HISTORY</code></li>
          <li><strong>Data Set:</strong> <em>All Values</em></li>
          <li><strong>Actions:</strong> Select desired tasks (e.g., View, Update, Cancel).</li>
        </ul>
      </li>
    </ul>
  </li>
  <li>On the <strong>Role Hierarchy</strong> page, add any needed roles.</li>
  <li>On the <strong>Users</strong> page, assign the users who need this custom role.</li>
</ul>

<h4 id="enterprise-scheduler-service-ess-audit-logs">Enterprise Scheduler Service (ESS) Audit Logs</h4>

<p>You can also update the Audit Level for Oracle Enterprise Scheduling Service (ESS) for  ESS metadata changes, ESS request operations, Administrative operations to ESS request processor and dispatcher.</p>

<ul>
  <li><strong>Access Manage Audit Policies:</strong>
    <ul>
      <li>In the <strong>Setup and Maintenance</strong> work area, search for and select the <strong>Manage Audit Policies</strong> task.</li>
    </ul>
  </li>
  <li><strong>Set Audit Level for ESS:</strong>
    <ul>
      <li>On the <strong>Manage Audit Policies</strong> page, locate <strong>Enterprise Scheduler Service</strong> in the list.</li>
      <li>To enable auditing, set the <strong>Audit Level</strong> to <code class="language-plaintext highlighter-rouge">Medium - Some Events</code>.</li>
      <li>Click <strong>Save and Close</strong> to confirm and apply your changes.</li>
    </ul>
  </li>
</ul>

<h4 id="oracle-metadata-services-mds-audit-logs">Oracle Metadata Services (MDS) Audit Logs</h4>

<p>Customization of the Fusion web application developed with Oracle ADF is supported by Oracle Metadata Services (MDS), which is a framework that integrates with JDeveloper tools and also manages the customization of ADF features by end users at runtime. The Oracle Metadata Services (MDS) framework allows you to create applications that your customers can further customize for their users or customers and which the end users can also customize.</p>

<p>MDS can be applied to the range of other components in the ADF technology stack, such as ADF Faces, ADF Controller, ADF Model, and ADF Business Components. Oracle Metadata Services (MDS) audit enables auditing of metadata changes in Oracle Fusion Applications. To enable MDS audit logging, follow these steps:</p>

<ul>
  <li><strong>Access Manage Audit Policies:</strong>
    <ul>
      <li>In the <strong>Setup and Maintenance</strong> work area, search for and select the <strong>Manage Audit Policies</strong> task.</li>
    </ul>
  </li>
  <li><strong>Set Audit Level for MDS:</strong>
    <ul>
      <li>On the <strong>Manage Audit Policies</strong> page, locate <strong>Oracle Metadata Services</strong> in the list.</li>
      <li>To enable auditing, set the <strong>Audit Level</strong> to <code class="language-plaintext highlighter-rouge">Medium - Some Events</code>.</li>
      <li>Click <strong>Save and Close</strong> to confirm and apply your changes.</li>
    </ul>
  </li>
</ul>

<h4 id="oracle-soa-suite-audit-logs">Oracle SOA Suite Audit Logs</h4>

<p>The Oracle SOA Suite audit enables auditing of SOA Suite events in Oracle Fusion Applications. To enable SOA Suite audit logging, follow these steps:</p>

<ul>
  <li><strong>Access Manage Audit Policies:</strong>
    <ul>
      <li>In the <strong>Setup and Maintenance</strong> work area, search for and select the <strong>Manage Audit Policies</strong> task.</li>
    </ul>
  </li>
  <li><strong>Set Audit Level for SOA Suite:</strong>
    <ul>
      <li>On the <strong>Manage Audit Policies</strong> page, locate <strong>Oracle SOA Suite</strong> in the list.</li>
      <li>To enable auditing, set the <strong>Audit Level</strong> to <code class="language-plaintext highlighter-rouge">Medium - Some Events</code>.</li>
      <li>Click <strong>Save and Close</strong> to confirm and apply your changes.</li>
    </ul>
  </li>
</ul>

<h4 id="oracle-fusion-applications-business-object-audit-logs">Oracle Fusion Applications Business Object Audit Logs</h4>

<p>To configure which attributes appear in the audit report for Oracle Fusion Applications business objects, follow these steps (adapted from <a href="https://docs.oracle.com/en/cloud/saas/supply-chain-and-manufacturing/25d/fauqm/manage-audit-policies.html">Oracle documentation</a>):</p>

<ul>
  <li><strong>Access Manage Audit Policies:</strong>
    <ul>
      <li>In the <strong>Setup and Maintenance</strong> work area, search for and select the <strong>Manage Audit Policies</strong> task.</li>
    </ul>
  </li>
  <li>
    <p>Under Fusion Applications Business Objects section, set Audit Level to <strong>Auditing</strong></p>
  </li>
  <li>
    <p>Under Fusion Applications Business Objects section, click <strong>Configure Business Object Attributes:</strong></p>
  </li>
  <li><strong>Select Product and Object:</strong>
    <ul>
      <li>From the <strong>Product</strong> list, select the relevant product. For example:
        <ul>
          <li><strong>Global Human Resources</strong> for Log Analytics <strong>Fusion Apps: HCM People Audit Logs</strong> Log Source</li>
          <li><strong>Global Payroll</strong> for Log Analytics <strong>Fusion Apps: HCM Payroll Audit Logs</strong> Log Source</li>
        </ul>
      </li>
      <li>Check the Audit checkbox for the relevant business object.</li>
      <li><img src="/images/posts/2026-01-fusion-blogs/blog-fusion_apps_audit_logs_configure_business_object_audit_hcm_people.png" alt="Configure Business Object Audit" /></li>
      <li><em>Figure 8: Fusion Applications Audit Logs Configure Business Object Audit HCM People</em></li>
      <li>Click <strong>Save and Close</strong> to confirm and apply your changes.</li>
    </ul>
  </li>
</ul>

<h3 id="conclusion">Conclusion</h3>

<p>In Part 1, we explored how to enable and configure audit logging across key Oracle Fusion Applications components, including ESS, MDS, SOA Suite, and Business Objects. By following the steps outlined, you ensure critical business transactions and workflow activities are recorded, supporting your compliance and security monitoring objectives. Properly configured audit policies allow for effective tracking of user and system activity, forming the foundation for robust audit log collection and analysis in OCI Log Analytics.</p>

<p>In the next part, we will cover step-by-step guidance on ingesting these audit logs into Oracle Cloud Infrastructure, so you can gain actionable insights and streamline your audit compliance processes.</p>

<h2 id="references">References</h2>

<ul>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/faucf/assign-roles-for-access-to-manage-scheduled-processes.html">ESS Roles Documentation</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/ochus/enable-audit-for-oracle-platform-security-services.html">Enable Audit for Oracle Platform Security Services</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/applications-common/25d/facia/audit-policies.html">Fusion Applications Audit Policies</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/applications-common/25d/farca/api-audit-report.html">Fusion Applications Audit Report API</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/farws/Authorize.html">HCM REST API Authorization</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/human-resources/ochus/get-user-sign-in-sign-out-information.html">How to Get User Sign-in Sign-out Information?</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/fusion-service/faiec/create-a-fusion-service-integration-user-account-for-other.html">Create a Fusion Service Integration User Account</a></li>
  <li><a href="https://docs.oracle.com/en/cloud/saas/applications-common/24c/farca/Quick_Start.html">REST API Quick Start</a></li>
  <li>Doc ID 2661308.1 - Fusion Applications URLs and Configuration</li>
  <li>Doc ID 2059102.1 - How To Configure And Use Audit In BI Publisher For Fusion SaaS Cloud Customers</li>
  <li>Doc ID 2731495.1 - Fusion Applications OTBI: How To Configure And Use Audit For Usage and Performance In OTBI For Fusion SaaS Cloud Customers</li>
</ul>]]></content><author><name>Royce Fu</name></author><category term="Blog" /><category term="Observability and Monitoring" /><category term="Fusion Applications" /><category term="OCI Log Analytics" /><category term="Security" /><summary type="html"><![CDATA[Understand Required Permissions for Fusion Applications Audit and Security Logs Ingestion in OCI Log Analytics - Part 1]]></summary></entry></feed>